❌

Reading view

Pokémon Center Breach Shows Why Your Delivery Data Matters: This Week in Scams

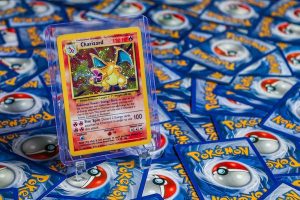
A pile of Pokemon cards, with Charizard visible.

A data breach doesn’t have to hit the company you shopped with directly to put your information at risk. 

That’s the lesson from this week’s Pokémon Center breach. Customers in the United Kingdom and Germany are being notified that personal and order information was exposed after attackers compromised CEVA Logistics, the third-party company used to fulfill and ship Pokémon Center orders. 

The good news: Pokémon Center says CEVA did not have access to customers’ payment-card information.  

The bigger concern is what criminals could potentially do with the information that was exposed, particularly when it can make a phishing message look unusually convincing. 

What Happened in the Pokémon Center Data Breach? 

According to breach notifications reviewed by BleepingComputer, attackers may have obtained Pokémon Center customers’ full names, mailing addresses, phone numbers, email addresses, and information about the products they ordered. The affected customers were in the UK and Germany. 

The intrusion occurred at CEVA Logistics rather than Pokémon Center itself. Reporting indicates attackers accessed CEVA systems between late July and August 1, disrupting operations at eight European warehouses and affecting multiple retailers. Valve previously notified European Steam hardware customers that their information had also been exposed through the CEVA incident. 

Why Does Shipping Data Matter to Scammers? 

A name and email address may not seem as sensitive as a credit-card number. But when criminals also know your address, phone number, and what you recently bought, they have something valuable: context. 

Context helps scammers make phishing messages believable. 

Phishing is when a criminal pretends to be a trusted company or person to persuade you to click a malicious link, hand over a password, share personal information, or send money. 

After a breach like this, criminals could potentially impersonate Pokémon Center, a delivery company, or another retailer and reference details that make their message feel legitimate. 

They might claim an order needs to be rescheduled, a delivery fee must be paid, or a refund is waiting. Knowing that you really placed an order can make the bait much harder to spot. 

Importantly, there is currently no evidence that the stolen Pokémon Center information is being used in such a campaign. But personalized phishing is a common reason breached contact and transaction information deserves attention. 

Key Takeaways 

➡ Pokémon Center says the breach occurred at its logistics provider, CEVA, not its own shopping platform. 

➡  Names, addresses, phone numbers, email addresses, and order details may have been exposed. 

➡  Pokémon Center says payment-card information was not available to CEVA. 

➡  Real order details could make future phishing or delivery scams appear more credible. 

➡  Customers should independently verify unexpected messages about refunds, cancellations, or deliveries. 

3 Easy Safety Actions to Take If Your Information Is Exposed in a Data Breach 

Getting a breach notification doesn’t necessarily mean someone has already misused your information. It does mean you should take a few steps to make that information harder to use against you. 

1) Find out exactly what was exposed. Read the company’s breach notice carefully. An exposed email address calls for different precautions than a stolen password, Social Security number, financial information, or medical record.

2) Secure the accounts that could be at risk. Change any exposed or reused passwords, use a unique password for every account, and turn on multi-factor authentication where it’s available. If sensitive financial or identity information was stolen, consider a credit freeze or fraud alert as well.

3) Be extra skeptical of messages that know something about you. Breached information can help scammers create convincing emails, texts, and calls. A message that knows your name, address, recent purchase, or other real details isn’t necessarily legitimate. Go directly to the company’s website or app to verify unexpected requests rather than clicking a link or calling a number in the message.  

How McAfee Protects Against Breaches 

Before a breach  

Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.  

Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.  

During a breach  

Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.   

Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.  

After a breach  

Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even more of your information. 

Other Scam and Security News This Week 

FBI warns about callers impersonating federal agents. The FBI’s Boston Division is warning about scammers who spoof its real phone number, pretend victims are connected to crimes, and then try to move conversations onto encrypted messaging apps. The key reminder: caller ID can be faked, and the FBI says it will not call private citizens to demand payment, threaten arrest, or request sensitive information. 

(Source: FBI Boston) 

CareCloud breach grows to more than 3.75 million patients. Healthcare technology company CareCloud has confirmed with federal regulators that hackers stole personal and medical information belonging to more than 3.75 million people, including Social Security numbers, health information, government-issued ID numbers, and some financial data. Because medical and identity information cannot simply be replaced like a password, affected people should take breach notifications particularly seriously. 

(Source: TechCrunch) 

Hacker claims millions of corporate directory records were stolen. A cybercriminal known as “TheHatman” is offering databases allegedly taken from the Microsoft Azure and Entra environments of several major companies, although some named organizations dispute that their current systems were breached and say portions of the information appear old. Even older employee information can still be useful for impersonation and targeted phishing, so the claims are worth watching without treating every advertised dataset as independently confirmed. 

(Source: TechRadar) 

This Week’s Safety Tips 

✓ Treat unexpected delivery messages with caution. Open the retailer or carrier’s official app or website instead of following a link in a text or email. 

✓ Don’t trust caller ID alone. Scammers can spoof a legitimate organization’s real phone number. 

✓ Use unique passwords and multi-factor authentication. Stolen personal information becomes more dangerous when criminals can also get into your accounts. 

✓ Pay attention to breach notices. Knowing exactly what information was exposed helps you recognize the scams criminals may try next. 

And we’ll be back next week with more cybersecurity news and scam alerts. 

The post Pokémon Center Breach Shows Why Your Delivery Data Matters: This Week in Scams appeared first on McAfee Blog.
  •  

AWS Security makes an inscrutable choice

One of the best ways to lower your AWS bill by 99 percent or more is by not checking your keys into public GitHub repositories. Many of us have done this inadvertently over the years, and the defenses against it have improved dramatically (my personal favorite being "using non-ephemeral credentials derived from OIDC or SSO is an anti-pattern"), but it still happens. On Friday, BleepingComputer reported on a Truffle Security finding that hundreds of leaked AWS keys are root keys and are somehow still active and valid. AWS Security is full of very smart people who care deeply about a number of things, including "not abetting crime." If they detect (usually via automated means) that a credential has been leaked, they're quick to apply a Quarantine Policy to it. Trouble is, that policy enumerates a bunch of bad behaviors in an ever-expanding graph of principals and associated behaviors. AWS' considered position on this is that they don't want to break customer environments: "The policy aims to limit the potential damage that may be caused by fraud-related activity leading to unauthorized charges, while not impacting the existing resources." AWS' considered position on this is wrong. If I get access to your credentials (much less a root credential, good god), deactivating them may very well break your workload because anything that relies on those credentials will start failing. Until you rotate them, those workloads will continue to fail. That's not good! But I promise you, as a bad actor, I can do far worse to you. Hold my tea Go ahead and apply a quarantine policy to a credential set and toss it my way. I won't be able to buy savings plans, read your S3 data, modify Lambda functions, and do a host of other things. But here's what I can do. Anything I damn well feel like on RDS. You don't have anything important in databases, right? ssm:SendCommand / ssm:StartSession are permitted, which means I can run commands as root on EC2 instances, which will in turn invoke with that instance role’s permissions. sts:AssumeRole means that I can assume any other role in the account and get its permissions, rendering the entire restriction list potentially moot. I can use autoscaling:CreateAutoScalingGroup / UpdateAutoScalingGroup to launch instances via the Auto Scaling service-linked role, so the ec2:RunInstances deny never applies. cloudtrail:LookupEvents gets denied (that'll stop you from... reading the audit log), but I can call both cloudtrail:StopLogging and DeleteTrail which do exactly what you expect; you don't have an audit log anymore. SES denies ses:GetSendQuota / ListIdentities actions, but y'know what's missing? SendEmail, so I can blast my spam out to your entire list. sns:GetSMSAttributes means I can't get your SMS configuration, but I can absolutely sns:Publish to send fraudulent text messages wherever I'd like. s3:DeleteObject gets denied, but s3:PutObject is allowed. I can't delete your data, but I can fill a bucket to petabytes. Next, they fail to block s3:PutBucketVersioning, s3:PutObjectLockConfiguration, s3:PutObjectRetention, and s3:PutObjectLegalHold. So on any existing bucket, like that one I just stuffed petabytes into, I can enable versioning, turn on Object Lock, and set a bucket-default COMPLIANCE-mode retention out to 2126, or alternatively slap it on per object. COMPLIANCE retention can't be shortened or removed by anyone, including the account root and AWS Support. The only way to remove it is to delete the entire AWS account. secretsmanager:GetSecretValue, ssm:GetParameter* (WithDecryption), and kms:Decrypt are all unencumbered, so your secrets are now my secrets. Sharing is good! Backups are important, so it's a shame you don't have any. Well, not after I kick off backup:DeleteRecoveryPoint / DeleteBackupVault, and rds:DeleteDBSnapshot. If you're using CloudFormation, and for some things you almost certainly are, cloudformation:DeleteStack going unmentioned means you're not using it anymore and all of your stacks are gone. I would make different choices This isn't a comprehensive list - just a few things that occurred to me over the course of about an hour. I'm not a bad actor; I'm almost positive that I'm missing a whole bunch. AWS is almost certainly going to change this. My question for them is simply, "how big of a customer incident needs to happen before you do?" ®

  •  

Homeland security cybercops say patch TrueConf (Russia's Zoom) if you're using it

CISA has ordered US federal agencies to patch two exploited flaws in TrueConf, a Russian-built video conferencing platform, after compromised servers were caught handing malware to unsuspecting meeting participants. The US cybersecurity agency on Thursday added CVE-2026-72529 and CVE-2026-72530 to its Known Exploited Vulnerabilities catalog, saying both have been used in real-world attacks. What CISA doesn't say is who is being attacked, or where. The only publicly documented attacks exploiting these two bugs so far come from Kaspersky, which linked them to Head Mare, a pro-Ukrainian hacktivist group that has repeatedly gone after Russian organizations. Its latest campaign targeted Russian companies across industries including transport, energy, electronics, IT, and software development. CISA doesn't say whether it added the flaws to KEV because of those attacks or because it has evidence of exploitation elsewhere, potentially including against organizations in the US. That question is particularly interesting given what TrueConf is and who uses it. TrueConf is a Moscow-based maker of video conferencing software that offers an on-premises alternative to cloud services such as Zoom and Microsoft Teams. Organizations can run TrueConf Server on their own infrastructure, including in private networks, giving them control over where their calls and associated data go. While the company's roots and much of its customer base are Russian, TrueConf has users worldwide. It says it has users in its portfolio that include Switzerland’s Department of Justice and Home Affairs, Istanbul Airport, and a news org, which The Reg has contacted to confirm. Most of the customer success stories are dated before 2022. Used together, the two bugs flagged by CISA can give an attacker control of the underlying server. According to Kaspersky, an unauthenticated attacker with network access to TCP port 4307, which TrueConf documentation says is open by default, can exploit the first flaw to run a malicious script. The second flaw lets the attacker break out of the isolated environment where the script runs and execute arbitrary code on the underlying server. Kaspersky says Head Mare used that access to plant a web shell, move through victims' infrastructure, and gain privileged access to the TrueConf database. From there, the attackers replaced the legitimate TrueConf Windows client installer on compromised servers with a trojanized version carrying the PhantomCore backdoor. Kaspersky warns that this creates a risk beyond organizations actually running vulnerable TrueConf servers. Employees joining conferences hosted by suppliers or other third parties could potentially download a compromised client from someone else's hacked infrastructure. The researcher says the flaws affect TrueConf Server releases going back to 2022. TrueConf shipped fixes in versions 5.3.9, 5.4.9 and 5.5.5 on June 18, warning customers that skipping the update could leave their conferencing systems exposed to attacks over the public internet. That doesn't mean every TrueConf box is sitting on the internet waiting to be popped. Exploitation requires network access to the vulnerable service, so a server confined to an internal network would not be directly reachable from outside unless an attacker had another route in. Federal agencies have until September 10 to patch the flaws. Other TrueConf admins can take their time, as long as they're comfortable with a conferencing server potentially moonlighting as a malware distribution point. ®

  •  

Hackers poison popular Rust crates to steal developers' credentials

Hackers slipped malware into several popular Rust packages this week, turning routine software builds into a route onto developers' machines. The Rust Security Response Team disclosed the supply chain attack on Thursday after receiving a tip about a crate called proc-macro1. An investigation found that its build script fetched malware from a remote server. The attack extended beyond a single dodgy crate. Someone had published a new version of arrayref, a legitimate and widely used Rust package, with proc-macro1 added as a dependency. The attacker had also yanked recent legitimate releases of arrayref, helping steer users toward the poisoned release. The Rust team does not believe arrayref's maintainer was responsible. It suspects the developer's computer or credentials were compromised and locked the account while attempting to contact them. The attacker also published malicious versions of two other crates maintained by the same developer, internment and append-only-vec. The poisoned releases weren't around for long. Arrayref 0.3.10 was available on crates.io for 86 minutes, internment 0.8.7 for 90 minutes, and append-only-vec 0.1.9 for 107 minutes before they were removed. That's a narrow window, but arrayref is hardly some forgotten package gathering dust in the registry. Security firm Aikido, which separately analyzed the attack, puts arrayref at roughly 245 million lifetime downloads and append-only-vec at more than 4 million. However, those figures don't tell us how many developers pulled the malicious versions during the brief period they were live. Aikido found that the attacker largely left the legitimate source code untouched, adding only a dependency on proc-macro1, a typosquat of the legitimate proc-macro2 package. The malicious code was tucked inside proc-macro1's build.rs file. Cargo, Rust's package manager, runs build scripts during compilation. This allowed proc-macro1 to identify the operating system and processor architecture of the developer or build machine, download a matching payload, and execute it. Aikido found malware built for Linux, Windows, Intel Macs, and Apple Silicon Macs. The second-stage payload was more than a simple downloader. Aikido found code targeting Chromium-based browser data, including profiles for Google Chrome, Brave, and Microsoft Edge, as well as browser extension storage used by cryptocurrency wallets. It also found functionality to establish persistence and receive commands from the attacker's server. The Rust team also deleted proc-macro-en, aovine, arone, aronenao, and tinymember, warning that every version of those crates should be considered malicious. Developers have been urged to check their Cargo lockfiles and local registry caches for the affected packages. Rust credits Nextron Systems' research team with initially discovering and reporting the attack. It has not said how the legitimate maintainer was compromised, how many developers downloaded the poisoned releases, or how many systems ultimately executed the payload. The malicious packages may have lasted less than two hours on crates.io, but whoever was behind them chose a well-traveled route into developers' machines. ®

  •  

Cisco bug severity warning reads like Olympic gymnastics scores: 10, 10, 9.9, 9.6, and 7.5.

Cisco has revealed its Secure Workload Software, a micro-segmentation tool formerly known as Tetration that is supposed to stop attackers moving laterally across a network, has four critical flaws plus another high-severity bug. CVE-2026-20315 and CVE-2026-20317 are the two perfect-ten-rated bugs. Both relate to improper access control. Cisco has not offered much detail about either, saying only that 20315 “covers authorization, authentication, privileges, and bypasses” and that 20317 has to do with “missing authentication, authentication bypass, and reliance on untrusted inputs.” The 9.9-rated flaw is CVE-2026-20231, which describes issues related to “Improper neutralization of special elements (covers command, OS, argument injection).” CVE-2026-20318 is the 9.6-er and is an improper input validation problem. Coming in last, at 7.5, is CVE-2026-20319, a problem related to “Improper restriction of operations within the bounds of a memory buffer” including overflows and out-of-bounds writes. Cisco offers Secure Workload Software as a SaaS-y service and for on-prem deployment. The company has fixed the flaws with its SaaS, but users still need to upgrade the Agent and Connector tools needed to use the cloudy software. On-prem users who have deployed version 3.10 or earlier need to get to version 3.10.9.1. Users of version 4.0 or later need to adopt 4.0.4.16 sooner rather than later. Cisco revealed the flaws on Thursday and says it discovered them after “a comprehensive internal security review” that involved “existing testing processes as well as frontier AI models.” Cisco is a known participant in Project Glasswing, which grants access to Anthropic’s too-powerful-for-public-release Mythos bug-finding model. So maybe that’s the frontier model involved in this research. Thankfully, Cisco says it has detected no malicious use of the vulnerabilities. ®

  •  

Russian snoops add OAuth abuse to targeted phishing campaigns

Google is tracking three distinct suspected Russian cyber-spy groups that are targeting individuals in academia, aerospace, defense, government agencies, and think tanks across Europe and the US. The UNC (unclassified) groups, as Google calls them, have been orchestrating these highly targeted campaigns since at least last year, and they remain ongoing. Some of the phishing and OAuth-abuse operations used in the attack took place this month. Each campaign had fewer than 100 targets, and under 10 victims, the threat-intel team told The Register. Despite the small numbers, if you work in government, NGOs, academia, or aerospace, you may be a target, and over the past few months the Russian snoops have adapted their attacks to abuse legitimate authentication flows. This makes these types of social engineering tactics appear more legitimate – and allows the cyber operatives to compromise personal accounts across multiple platforms, Google warns. It also means that potential victims may not recognize these as phishing attempts. Google says it wants to raise awareness about these campaigns “so that targets can more readily recognize malicious outreach.” In other words: don’t blindly trust that calendar invite that purports to come from the US State Department. UNC6293 The security analysts have been tracking one of the three, UNC6293, for almost two years. UNC6293 is a suspected APT29 (aka Cozy Bear, which Google now tracks as Ice Relic – insert eyeroll) phishing squad that poses as US State Department employees to lure victims into giving the snoops long-term access to their email correspondence. APT29 is probably best known for the 2020 SolarWinds hack, and infosec analysts from the UK and US governments, and the private sector, often link it to Russia's Foreign Intelligence Service (SVR). On Thursday, Google’s Threat Intelligence Group (GTIG) said it's now tracking two other suspected Russian groups, UNC7005 and UNC5976, which also conduct phishing, abuse OAuth flows, and/or deploy malware to these same types of targeted individuals. Last summer, GTIG documented UNC6293 phishing for app passwords belonging to people who are critical of Russia. In this campaign, they impersonated State Department personnel, and they’ve continued using that lure while also adding OAuth phishing into their toolkit. “In June 2026, GTIG observed OAuth phishing where UNC6293 requested targets share either the full URL or ‘verification code’ after performing a legitimate login to an external provider,” Google threat analysts Gabby Roncone and Wesley Shields said in the Thursday report. “By providing the requested verification code the target would grant UNC6293 access to the account.” UNC7005 GTIG also asserts, with “moderate confidence,” that UNC7005 is another initial access group connected to APT29/Cozy Bear/Ice Relic – and the SVR. This crew, first identified in February, usually targets academia, diplomatic, and nonprofit personnel across Ukraine, Western Europe, and the US. While it shares similarities with UNC6293, Google tracks it separately “due to its lower sophistication and poor operational security, infrastructure with divergent characteristics, and incorporation of malware.” Reliaquest and Microsoft first sounded the alarm on this group - Redmond tracks UNC6293 as Storm-2945 - after spotting a campaign compromising captive portal networks to deliver infostealers, keyloggers, and other malware. The Russian intelligence operatives targeted users of public Wi-Fi networks at places like hotels, conference centers, and other shared venues in the hospitality sector in an AI-assisted operation that began in February. UNC7005 also enjoys device-code phishing for both Microsoft and WhatsApp accounts. Most recently, the phishing lures look like invitations to diplomatic events and conferences delivered via email with links to attacker-controlled websites. The crew also tends to reuse website templates. They did this in May, we’re told, re-using the website template from an operation that used the theme of an "embassy invite." The later campaign spoofed the real GLOBSEC forum - a geopolitical gabfest that focuses on Eastern Europe. Once victims visit the attacker-controlled website, the snoops fingerprint the victim’s system and prompt them to confirm their attendance at a conference. “The registration process is thorough, and notably contains an epicurean wine selection, which was a theme in multiple previous ICE RELIC-linked phishing campaigns,” the Googlers wrote. In May and June, UNC7005 carried out social engineering attacks spoofing WhatsApp and prompting the victim to either join a voice call, encrypted chat, or download a file. Joining the voice call triggers a malicious JavaScript that records audio and video of the target, which the malware uploads to the attacker’s command-and-control server. While Google doesn’t say how the Russians use the stolen images and audio, attackers can use both to help carry out convincing social engineering campaigns. Also in May, the goons conducted “a much broader phishing wave than any we had previously observed,” Roncone and Shields wrote. This one targeted prominent, mostly US-based academics, diplomats, and researchers whose work focused on Russia and former Soviet states. The miscreants’ website was more “elaborately built to social engineer the target,” with specific information about a resolution supporting Ukraine, plus contact details for general questions or tech support. Those contacts were a hotline to the attackers, not a helpdesk. When users click the button that, they believe, will download a “Summit Companion App” to read the full resolution, they inadvertently put infostealers on their own Mac OS and Windows devices. Since August, the same crew also started both Google and Microsoft account OAuth phishing operations using cloud infrastructure. UNC5976 Finally, UNC5976 is yet another suspected Russian cyberespionage group and again likes to steal OAuth tokens. GTIG began tracking OAuth-related activity from this crew in March 2026. In these campaigns, UNC5976 buys up several domains with names related to file sharing and then creates a cloud project related to the domain. The domains host a fake file sharing page that prompts users to “Continue with Google” via a popup link. The links takes them to a legitimate Google OAuth login page, asks them to sign in, and after authenticating the credentials redirects the victim to a Google Cloud project URL that saves the authentication token for the attacker. GTIG calls UNC5976 “distinct” from the other two initial access groups, and notes that this may indicate “differing strategic mandates and potential alignment with alternative Russian intelligence services.” It also uses dedicated infrastructure for post-compromise activity instead of residential proxies, plus more malware and tooling in its OAuth operations. ®

  •  
❌